
CVE-2026-89282
 dorkerdevil/cve-2026-89282
Proof-of-concept for CVE-2026-89282: proxy DLL search-order hijack in Apache Lounge Windows installs that yields SYSTEM privilege escalation on…
binary-exploitationexploitationpayload-development+4
dorkerdevil/cve-2026-89282Proof-of-concept for CVE-2026-89282: proxy DLL search-order hijack in Apache Lounge Windows installs that yields SYSTEM privilege escalation on…
 ivancabrera02/whfb-pincapture
Captures Windows Hello PINs at entry by injecting a DLL into LogonUI.exe that sets a CPU hardware breakpoint on NgcSerializeConvenienceCredential,…
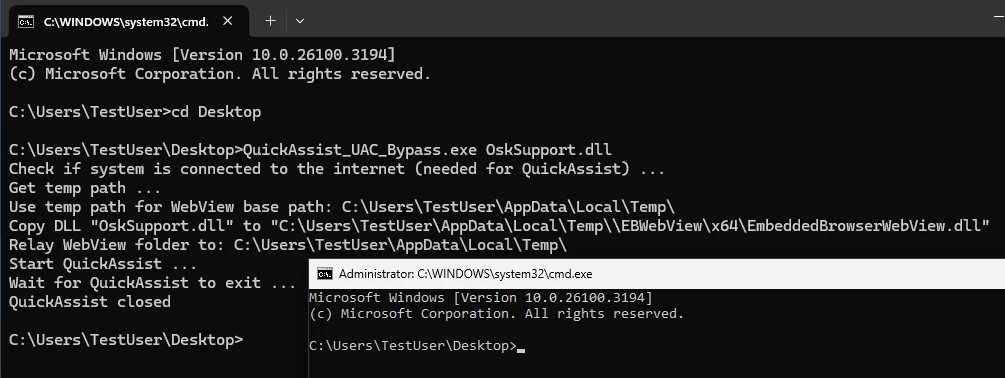 r41n3rzuf477/quickassist_uac_bypass
UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…
 andrewtrube/cve-2021-1675
Local privilege escalation exploit for CVE-2021-1675 (PrintNightmare) that installs a malicious DLL to gain SYSTEM access on vulnerable Windows…
 0xc4r/cve-2026-21508_poc
Proof-of-concept for CVE-2026-21508, demonstrating a DLL hijacking attack on Windows 11 that escalates privileges by loading a crafted DLL into…
 s3c/globalprotect-ca-cert-ipc
Proof-of-concept exploit for CVE-2025-0117 in GlobalProtect, achieving privilege escalation to SYSTEM via a backdoored installer and DLL injection.
 cypherhippie/cve-2026-66804
Local Windows privilege escalation PoC for CVE-2026-66804: plants a COM DLL in a missing path to abuse Camera FrameServer and impersonate SYSTEM.
 duyduongduyduong/cve-2021-36934-dll-hijacking-dfir-investigation
DFIR investigation resources for CVE-2021-36934, covering DLL hijacking, privilege-escalation detection, and forensic analysis of affected Windows…
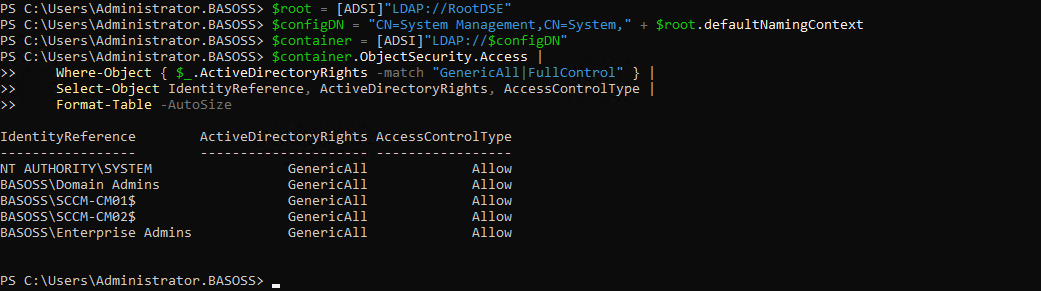 omribaso/sccm-cve-2026-47301-remote-code-execution-exploit
Proof-of-concept exploit chain (CVE-2026-47301) for Microsoft Configuration Manager (SCCM), combining a broken access, CAB arbitrary-write path…
 davidcarliez/cve-2026-66804-crossdevice-lpe
Local privilege escalation PoC for Windows CVE-2026-66804 using CrossDevice DLL planting and SigmaPotato token impersonation to spawn a SYSTEM…
 phackt/wptsextensions.dll
WptsExtensions.dll for exploiting DLL hijacking of the task scheduler.
 sailay1996/cdpsvclpe
Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
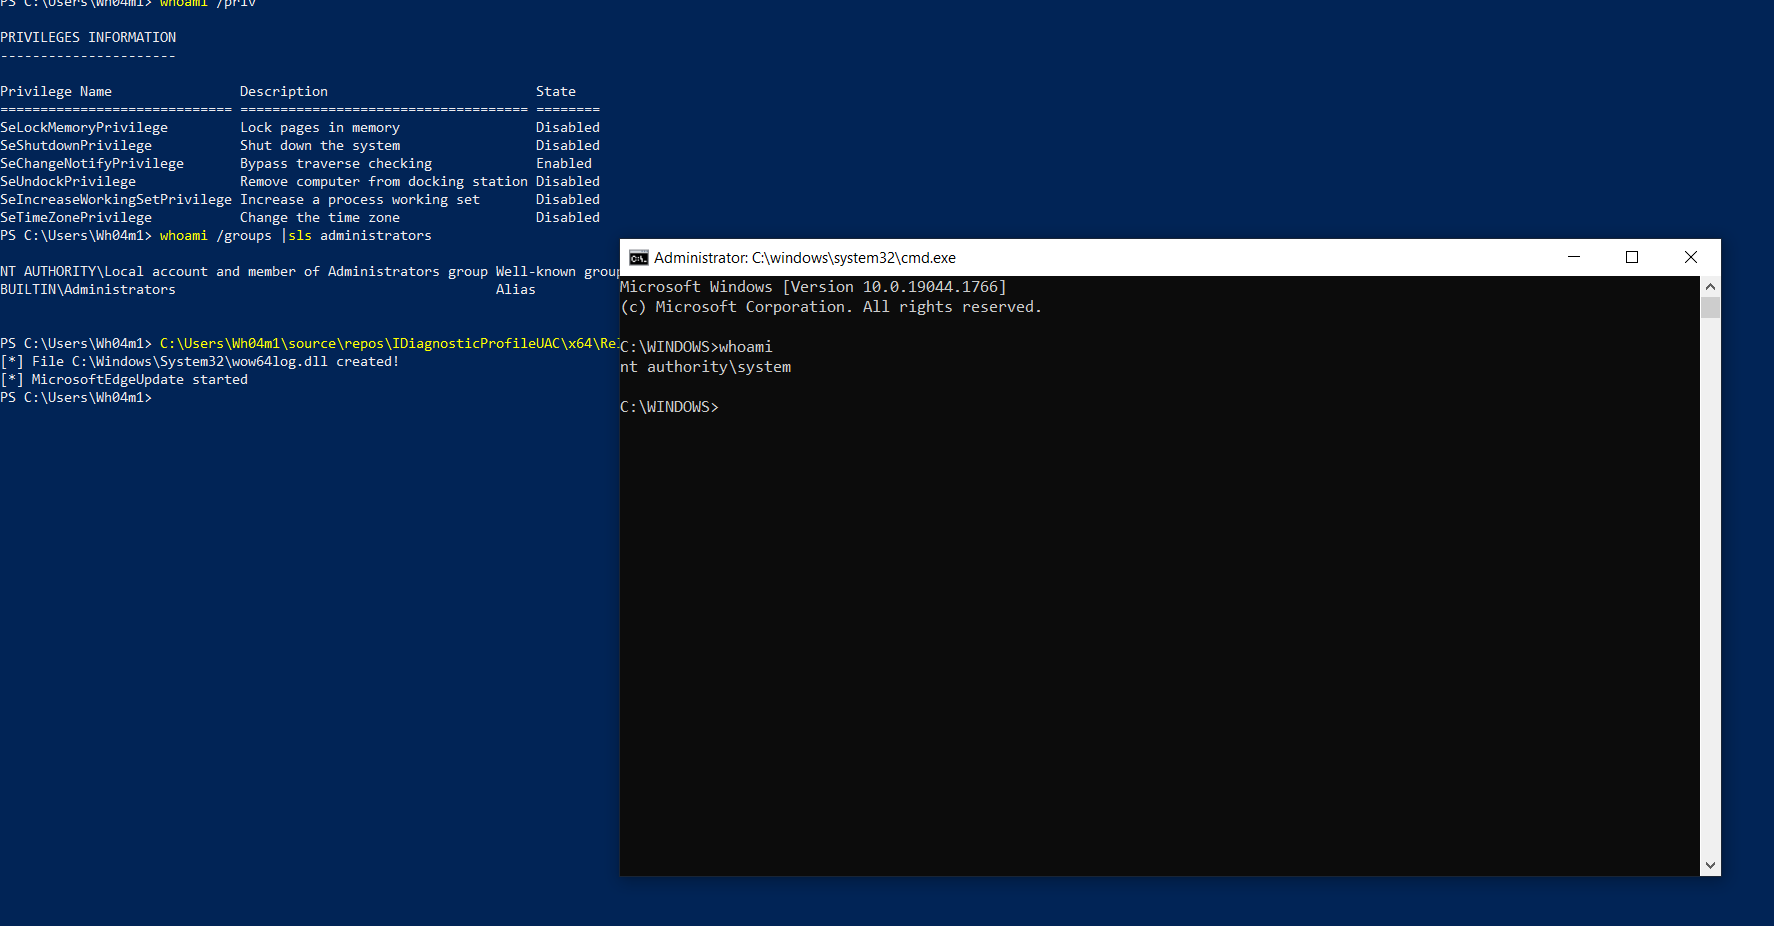 wh04m1001/idiagnosticprofileuac
Proof-of-concept UAC bypass abusing auto-elevated COM objects to copy a user-specified DLL into System32 and trigger a SYSTEM service load for…
 hackerhouse-opensource/iscsicpl_bypassuac
UAC bypass for x64 Windows 7 - 11
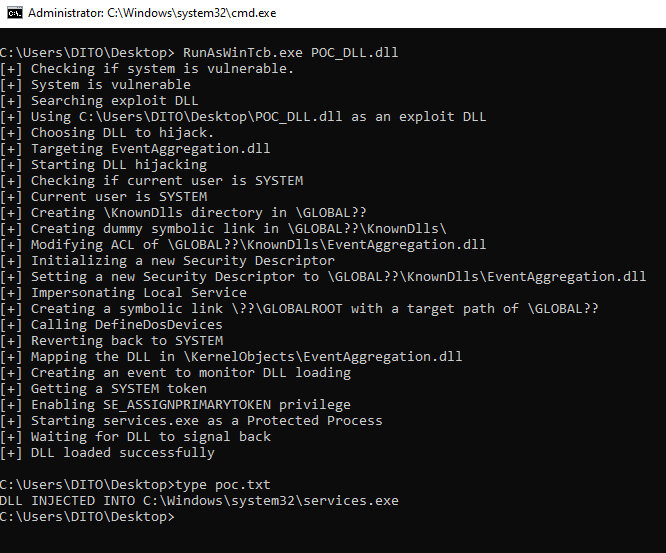 tastypepperoni/runaswintcb
Proof-of-concept C exploit that runs a DLL with WinTcb-Light protection from userland, demonstrating a Windows privilege-escalation primitive and…
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 hackerhouse-opensource/nofaxgiven
Code Execution & Persistence in NETWORK SERVICE FAX Service
 hackerhouse-opensource/compmgmtlauncher_dll_uacbypass
CompMgmtLauncher & Sharepoint DLL Search Order hijacking UAC/persist via OneDrive