

HorusEye
 omar-tamerr/horuseye
AI-Powered Active Directory Attack Platform
defensive-toolsinformation-gatheringlateral-movement+6
omar-tamerr/horuseyeAI-Powered Active Directory Attack Platform
 abraxas/ats-jsonrpc-unrestricted
Apache Traffic Server 10.2.0 - High - Local - Privilege leftover - JSON-RPC unix socket unrestricted mode 0777
 blendin/3snake
Tool for extracting information from newly spawned processes
 abraxas/pfsense-api-unix-sock-noauth
pfSense Plus MIM API toolkit b4acd7ca - High - Local - Privilege leftover - unix sock enroll no JWT
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.
 poxsky/cve-2026-24516-digitalocean-rce.
Technical analysis and PoC for CVE-2026-24516: Unauthenticated Root Remote Code Execution in DigitalOcean Droplet Agent (CVSS 10.0).
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 murrez/cve-2026-13355
Python PoC scanner and exploit for CVE-2026-13355, an unauthenticated admin privilege escalation in Meta Box AIO WordPress plugins, with FOFA mass…
 murrez/cve-2026-12793
Python PoC scanner and exploit for CVE-2026-12793, an unauthenticated privilege escalation in JetFormBuilder <=3.6.2 that creates WordPress admin…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 princeaikinsbaidoo/cve-2022-24637
Defensive notes on CVE-2022-24637 in Open Web Analytics before 1.7.4, covering unauthenticated information disclosure, privilege escalation impact,…
 ridpath/terrminus-cve-2026-2406
AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…
 ghostpels/cve-2026-18366
Unauthenticated privilege-escalation PoC for WordPress Events Manager < 7.4.1; discovers colliding post/user IDs and escalates targets to…
 specterops/sharphound
Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…
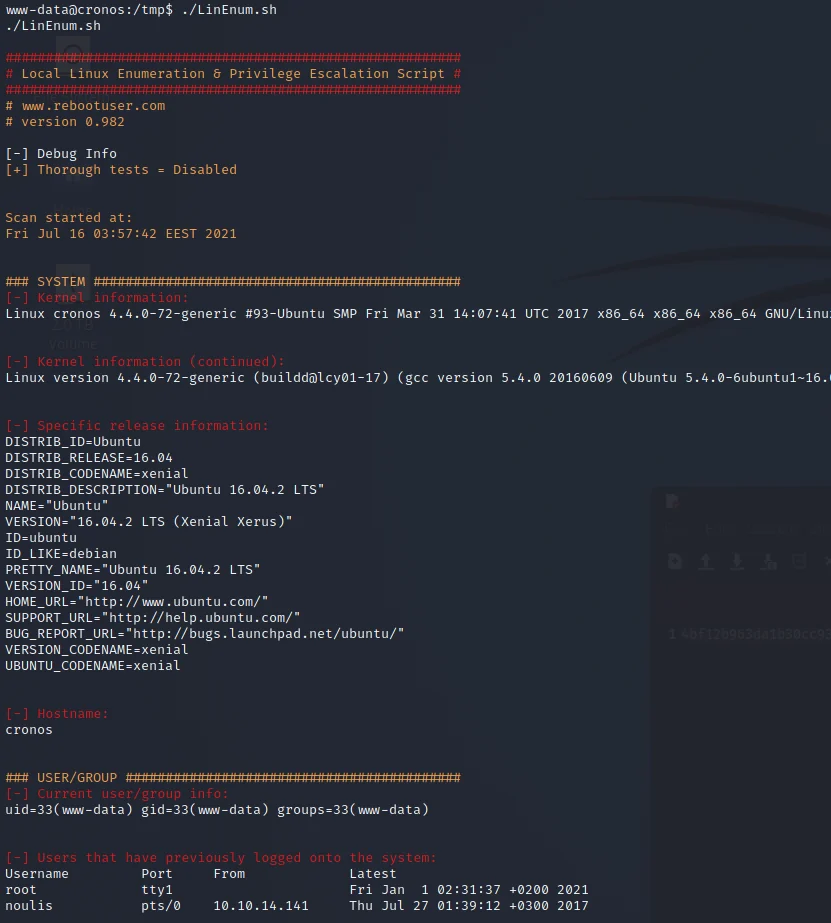 h3x0v3rl0rd/lin_enum
Shell script for automated enumeration of Linux systems to identify privilege escalation vectors and configuration weaknesses.
 h3x0v3rl0rd/linenum
Linux enumeration script for automated system information gathering to identify potential privilege escalation vectors during penetration testing.
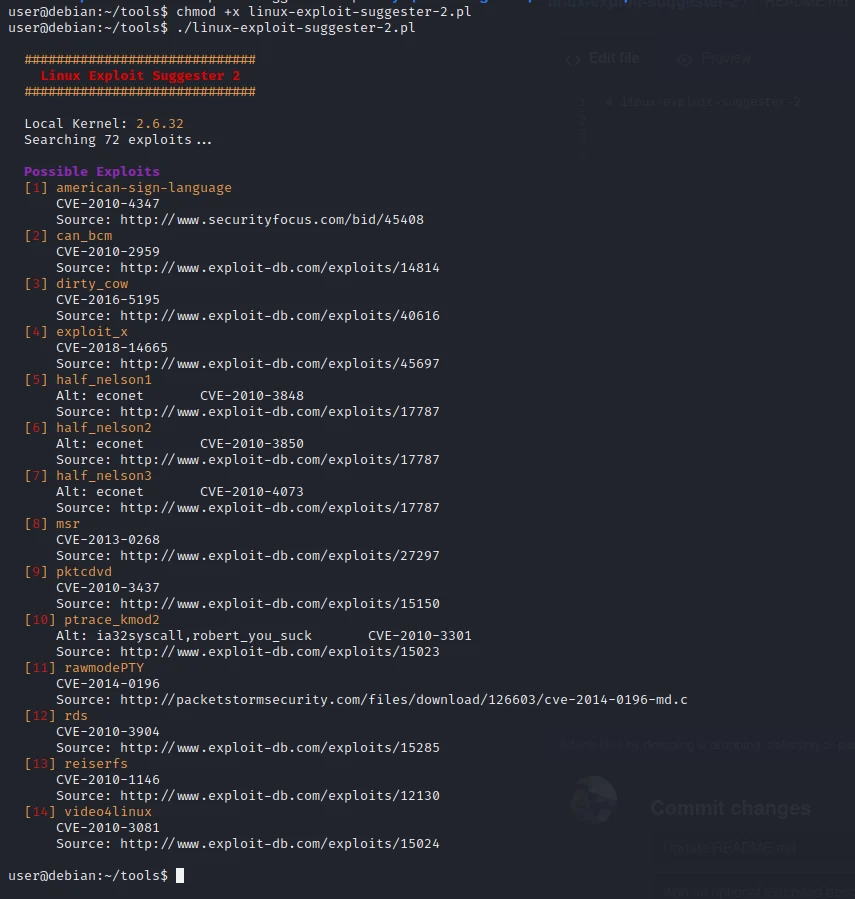 h3x0v3rl0rd/linux-exploit-suggester-2
Post-exploitation utility that scans kernel/OS version and configuration to suggest applicable local privilege escalation exploits.
 nxploited/cve-2026-18366
Events Manager < 7.4.1 - Unauthenticated Privilege Escalation to Administrator