
bpfjailer
 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer
authentication-authorizationconfiguration-auditingcontainer-security+3
36
facebookincubator/bpfjailereBPF LSM based Mandatory Access Control and jailer
 abraxas/veneficus-implant-public
Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
 langz337/cve-2026-14281
Mass scanner and single-target exploit for CVE-2026-14281, an unauthenticated privilege escalation in the WordPress Automation Web Platform plugin…
 mythicagents/xenon
A Mythic agent for Windows written in C
 hasanuyarrr/cve-2026-18782-trex-mes-uygulamalarinda-sql-zafiyeti
Advisory and technical write-up for CVE-2026-18782, a critical SQL injection in TREX MES web API endpoints enabling auth bypass, data theft, and RCE…
 fabianch20/soc335---cve-2024-49138-exploitation-detected
SOC335 incident response walkthrough for CVE-2024-49138 CLFS privilege escalation, covering alert triage, threat intel enrichment, process tree…
 pyyyc/honor-6.12.38-43499-research
Research repository documenting exploitation attempts of CVE-2026-43499 futex UAF on Honor YLP-W00 kernel 6.12.38, including PoC sources, kernel…
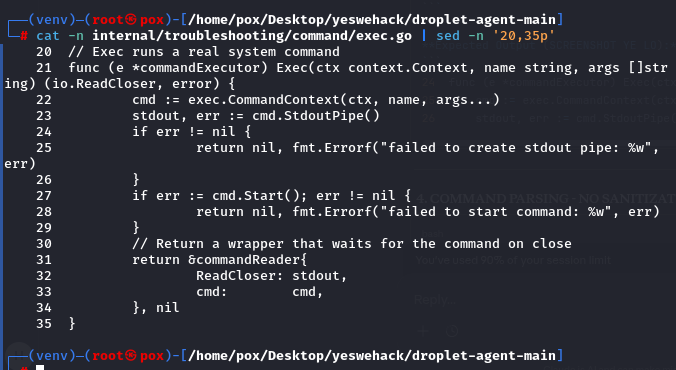 poxsky/cve-2026-24516-digitalocean-rce.
Technical analysis and PoC for CVE-2026-24516: Unauthenticated Root Remote Code Execution in DigitalOcean Droplet Agent (CVSS 10.0).
 imeiplus/cve-2026-23111-poc
Working local privilege escalation exploit for CVE-2026-23111, a use-after-free in the Linux kernel nf_tables subsystem, with KASLR bypass and ROP…
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 mein-0/gvcidrv64
Proof-of-concept exploit for Gigabyte's GVCIDrv64.sys kernel driver, achieving local privilege escalation via arbitrary physical memory and I/O port…
 hackspeak/cve-2026-67279
Python proof-of-concept scripts for the MikroTrick MikroTik RouterOS SSH takeover chain (CVE-2026-67279, CVE-2026-86060, CVE-2026-67276) for…
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
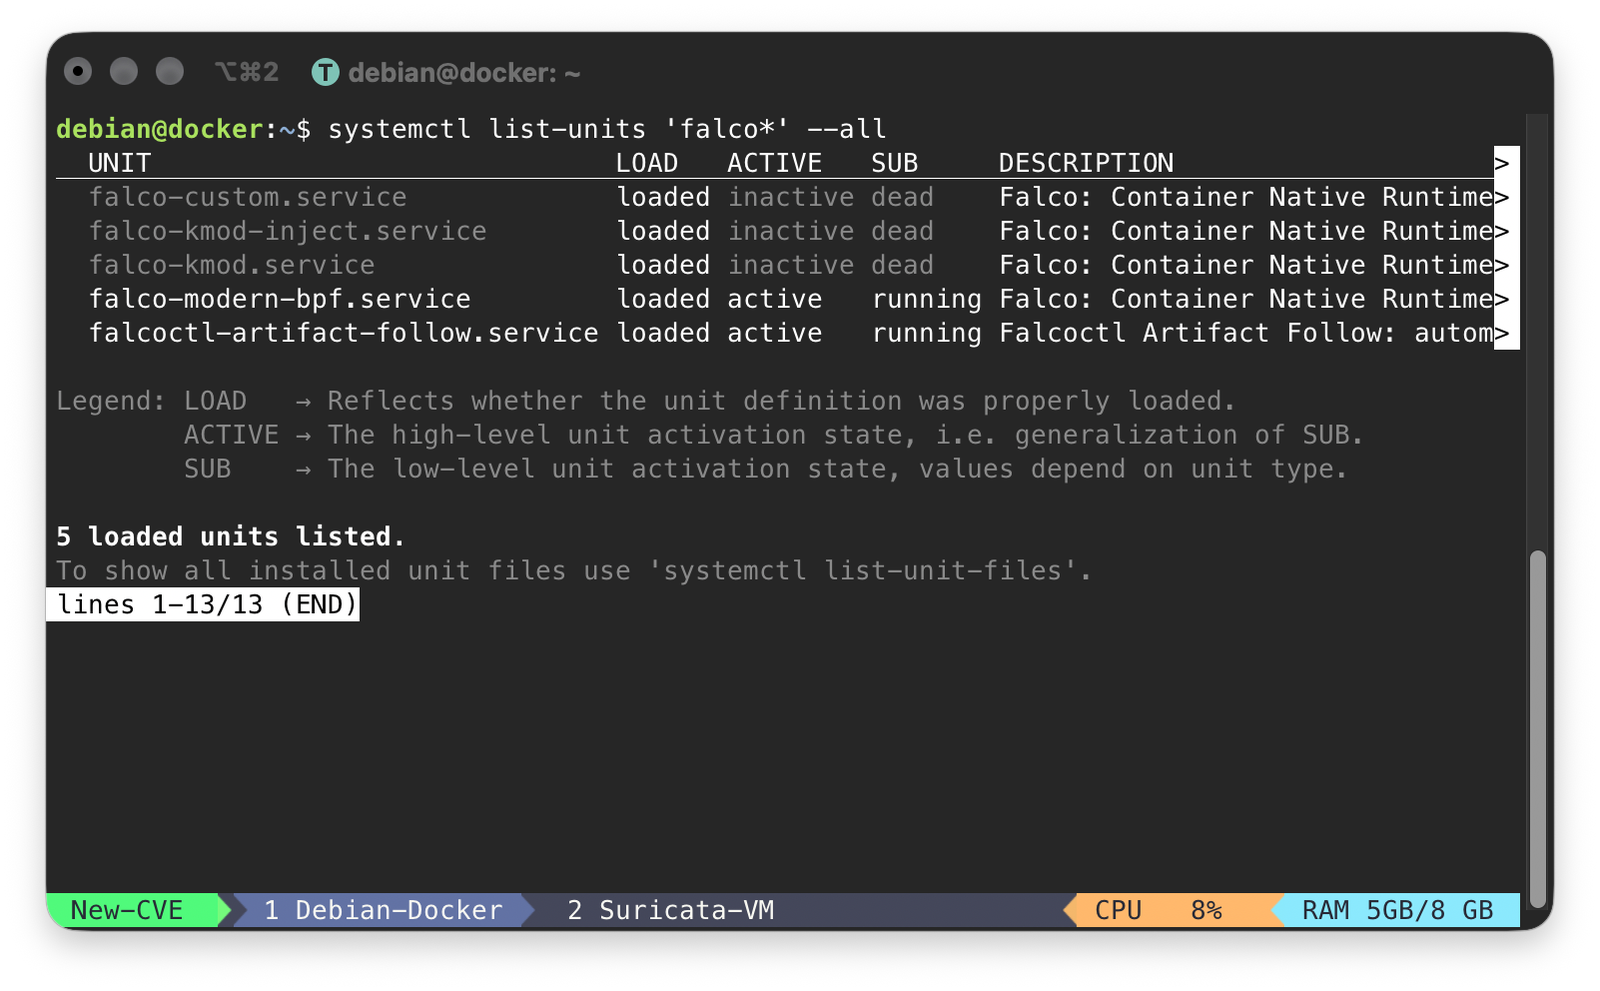 atlasvector/kestra-cve-2026-53576
End-to-end reproduction and cross-layer detection of CVE-2026-53576, the unauthenticated RCE in Kestra — taken past the base PoC to show how a common…
 hitechcloud-vietnam/cve-2026-41940-poc
Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.