Internal-Network-Penetration-testing

Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…

Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…

An AD CS toolkit for AD Admins, Defensive Security Professionals, and Filthy Red Teamers

GhostLock One-Tap Execution App (CVE-2026-43499)

Exploit and analyze CVE-2026-42978 with a Windows Push Notifications module for AI security, multi-protocol terminal, and autonomous agent suite.

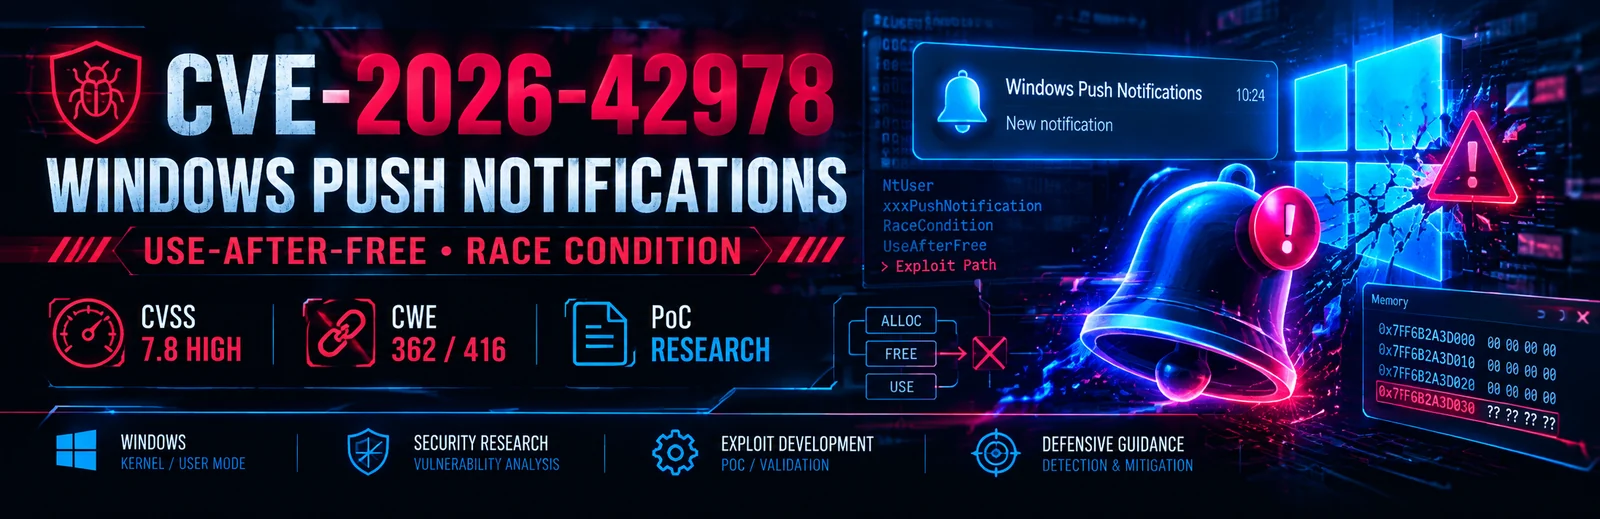
CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…

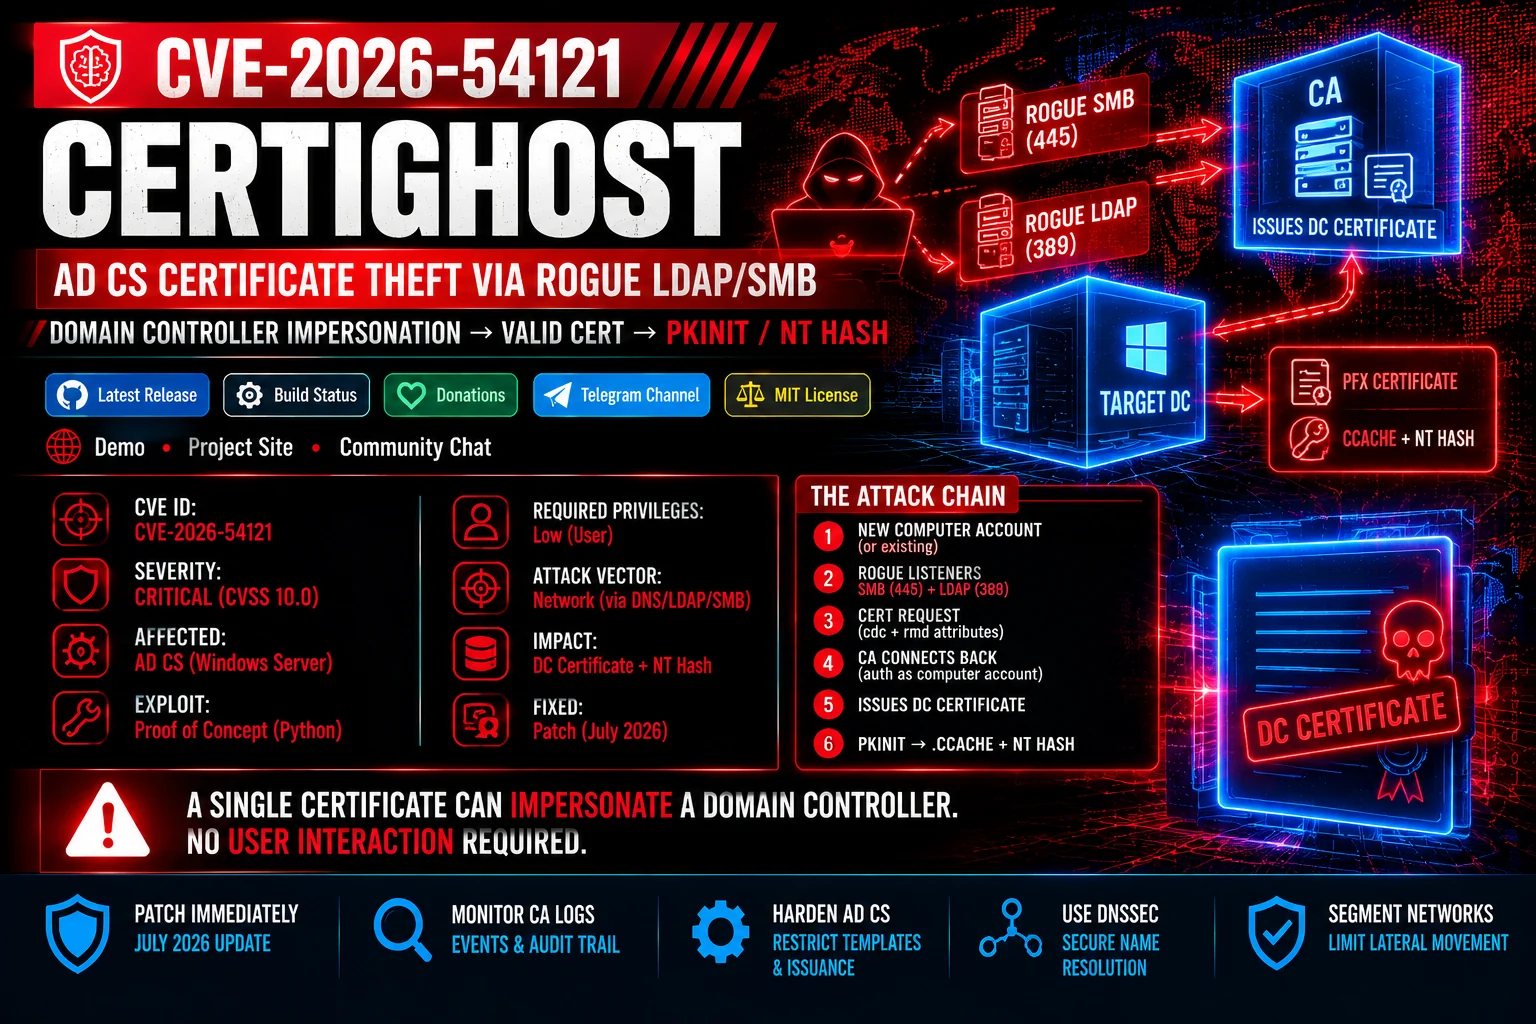
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…

Unauthenticated SQL injection to RCE exploit for FreePBX 16 Endpoint Manager (CVE-2025-57819). Demonstrates stacked queries to write a webshell via…

Linux kernel module that grants root privileges, hides processes/files, and protects itself from unloading, designed for educational purposes on…

Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…

Research and detection toolkit for Linux kernel LPE CVE-2026-31431, including exploit analysis, YARA rules, auditd/Falco detection, patching guide,…

Comprehensive analysis of CVE-2026-31431, a Linux kernel LPE, including exploit methodology, detection scripts, YARA rules, auditd and Falco…

Copy Fail (CVE-2026-31431) is a logic flaw in the Linux kernel's algif_aead module — part of the AF_ALG userspace crypto API. It was disclosed on…

Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation vulnerability in the algif_aead module, enabling unprivileged…

Lab testing documentation for CVE-2026-31431 (Copy Fail) Linux kernel LPE

Tests for CVE-2026-31431 kernel vulnerability, checks if vulnerable, and provides a fix by disabling the algif_aead module.

Kernel module exploiting CVE-2026-31431 to bypass system stop mechanisms, with configurable fake implementation for testing on non-stoppable machines.

Technical analysis of CVE-2026-31431, a Linux kernel local privilege escalation in the algif_aead module, including root cause, affected versions,…

pwncat module that automatically exploits CVE-2021-4034 (pwnkit)