

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
122 results
Overthrone preview

Overthrone

GitHubkarmanya03/overthrone

All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
command-and-controlexploit-frameworksinformation-gathering+8
31
6 days ago
gopacket preview

gopacket

GitHubmandiant/gopacket

A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
command-and-controlexploit-frameworkslateral-movement+7
7233 months ago
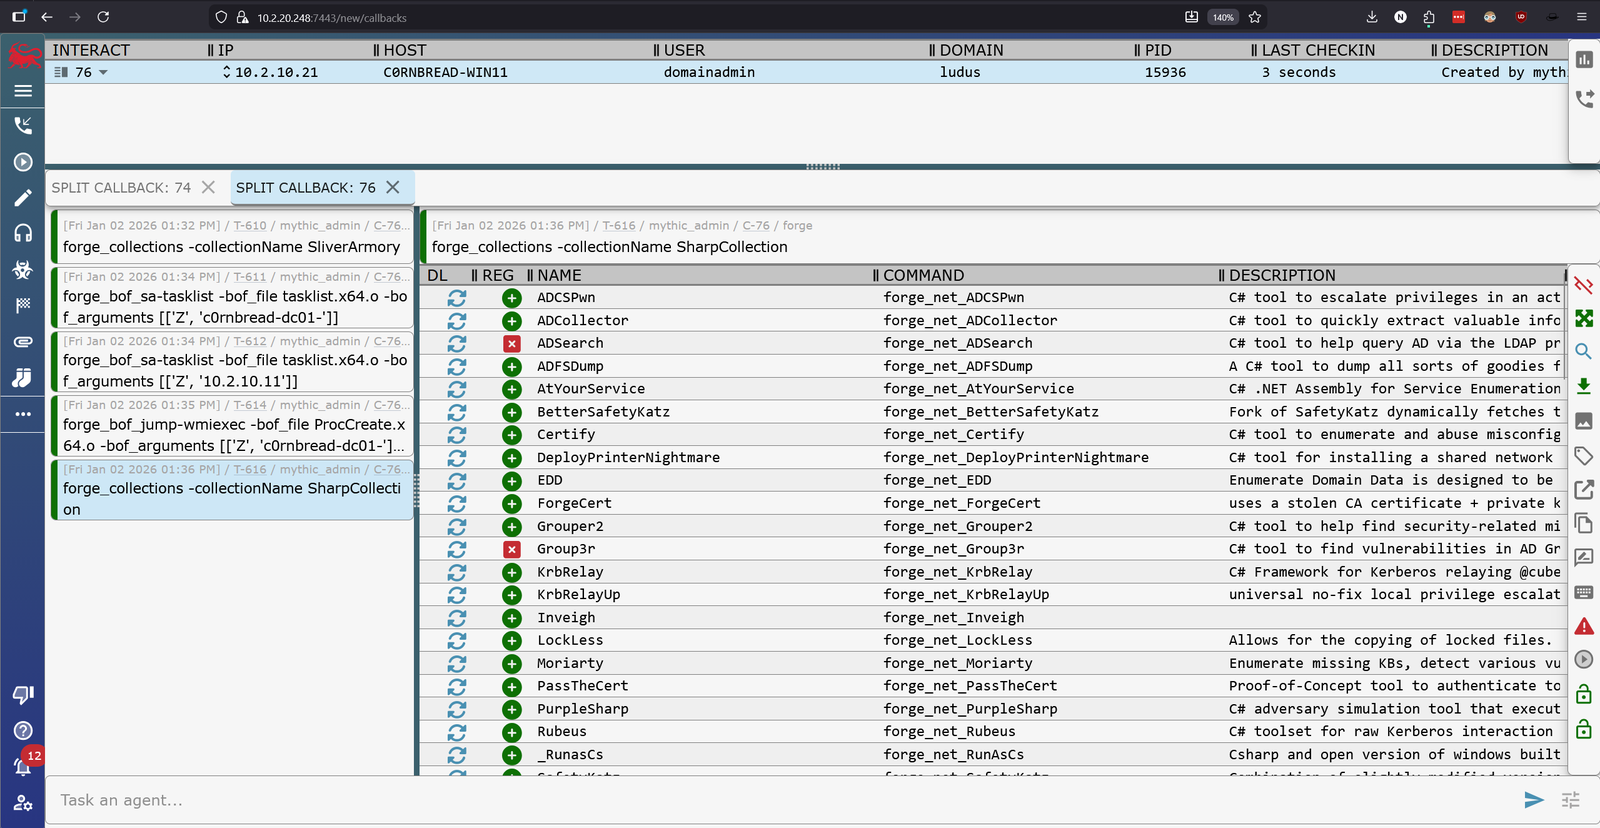
Xenon preview

Xenon

GitHubmythicagents/xenon

A Mythic agent for Windows written in C

command-and-controldata-exfiltrationdefensive-tools+9
1872 months ago
hoaxshell preview

hoaxshell

GitHubt3l3machus/hoaxshell

A Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.

command-and-controlexploitationpayload-generation+5
3.5k1 year ago
phpsploit preview

phpsploit

GitHubnil0x42/phpsploit

Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
command-and-controlexploit-frameworkspayload-development+6
2.5k2 years ago
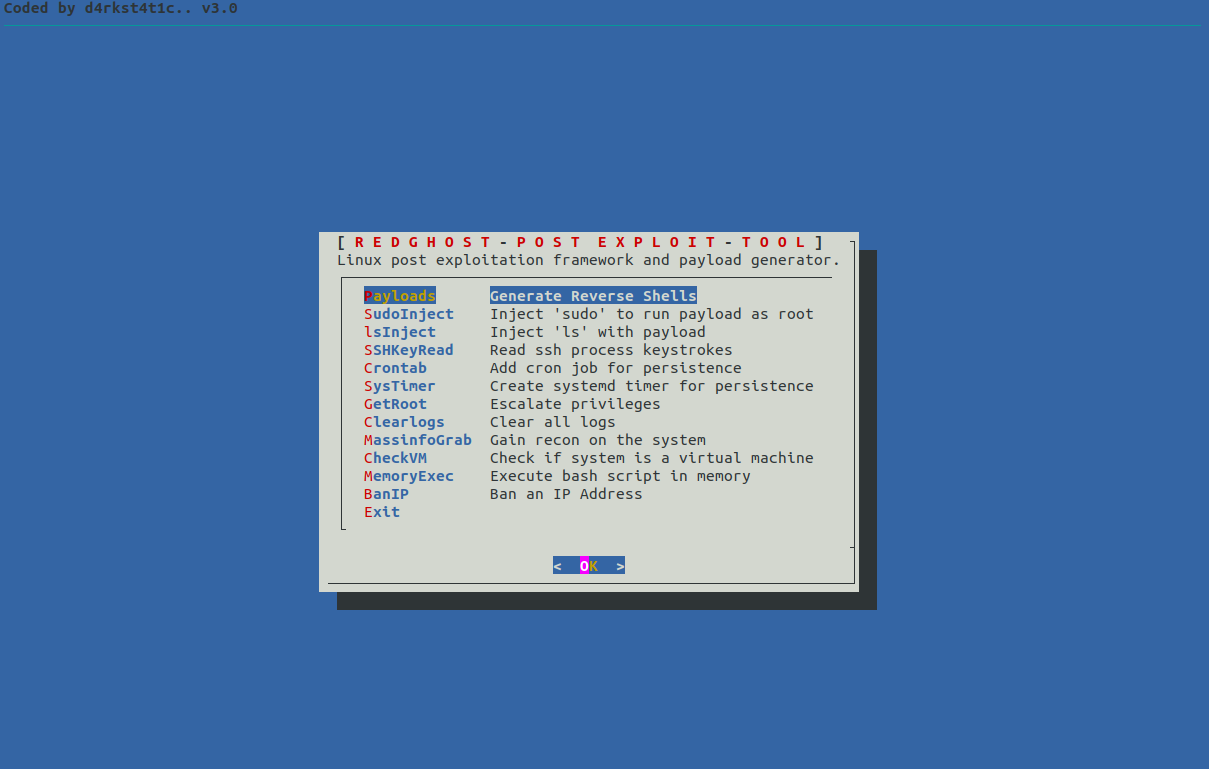
RedGhost preview

RedGhost

GitHubd4rk007/redghost

Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…

command-and-controllateral-movementpayload-generation+5
5415 years ago
NetExec preview

NetExec

GitHubpennyw0rth/netexec

Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
command-and-controldatabase-securityexploitation+14
6.0k10h 8m ago
Stracciatella preview

Stracciatella

GitHubmgeeky/stracciatella

OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup

command-and-controlexploit-frameworksids-ips-evasion+7
5434 years ago
wasmforge preview

wasmforge

GitHubpraetorian-inc/wasmforge

WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.

binary-analysiscommand-and-controlexploit-frameworks+9
1344 months ago
Medusa preview

Medusa

GitHubmythicagents/medusa

Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
command-and-controlexploit-frameworkslateral-movement+8
2127 days ago
LOLSpoof preview

LOLSpoof

GitHubitaymigdal/lolspoof

An interactive shell to spoof some LOLBins command line
command-and-controldefensive-toolspenetration-testing+3
1882 years ago
SharpHide preview

SharpHide

GitHuboutflanknl/sharphide

Tool to create hidden registry keys.
persistence-mechanismspost-exploitationprivilege-escalation+1
4887 years ago
Suborner preview

Suborner

GitHubr4wd3r/suborner

Creates invisible Windows accounts with administrative privileges via direct SAM manipulation and RID hijacking, bypassing standard user management…
persistence-mechanismspost-exploitationprivilege-escalation+1
4691 year ago
MiniPlasma-Runner preview

MiniPlasma-Runner

GitHubalexlinov/miniplasma-runner

CVE-2020-17103 adapted for C2 with split-binary SYSTEM callback
command-and-controlexploitationexploit-frameworks+5
465 months ago
SockTail preview

SockTail

GitHubyeeb1/socktail

Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…
command-and-controllateral-movementnetwork-security+4
5741 year ago
ImpulsiveDLLHijack preview

ImpulsiveDLLHijack

GitHubknight0x07/impulsivedllhijack

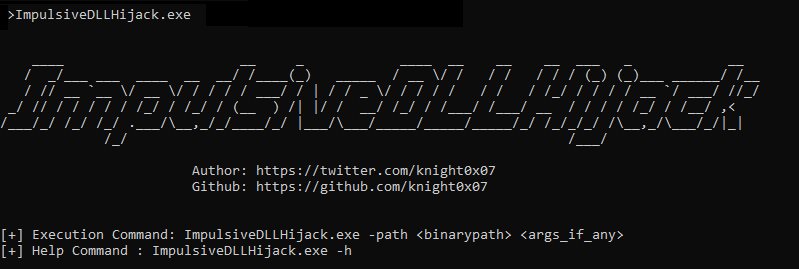
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…
binary-exploitationexploitationpersistence-mechanisms+2
5575 years ago
Nimbo-C2 preview

Nimbo-C2

GitHubitaymigdal/nimbo-c2

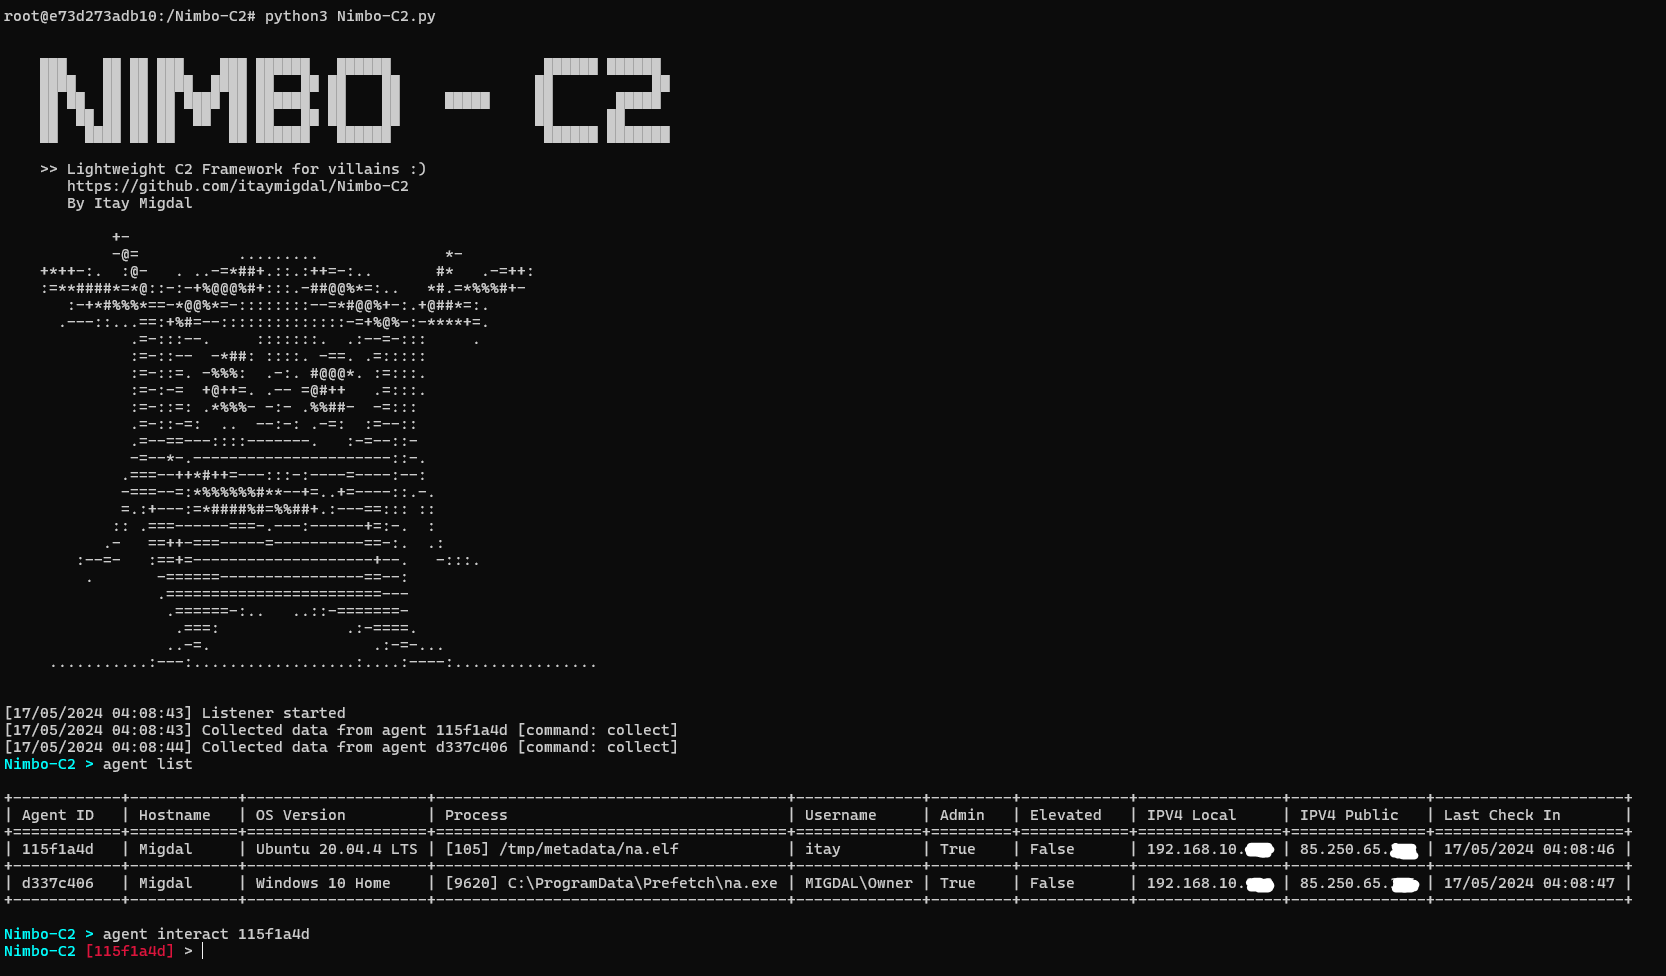
Nimbo-C2 is yet another (simple and lightweight) C2 framework
command-and-controlexploit-frameworkspayload-generation+5
4499 months ago
sliver-gui preview

sliver-gui

GitHubmr-in4inci3le/sliver-gui

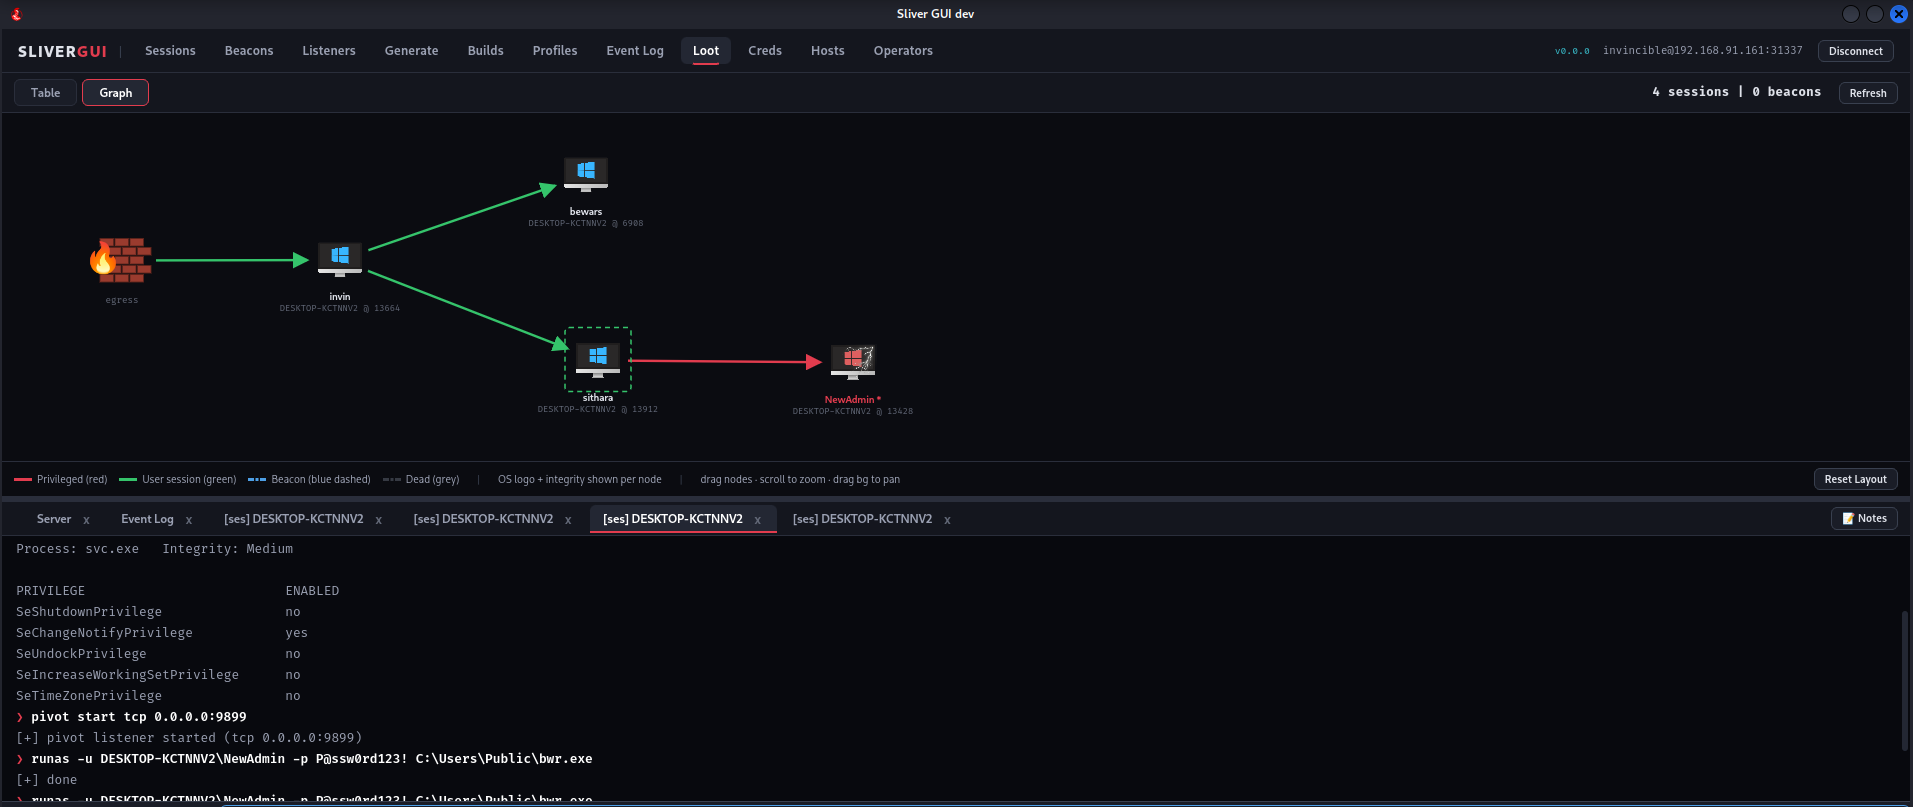
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…

command-and-controlexploitationlateral-movement+6
2311 month ago
Previous1234567Next