
 ghosttroops/top
TOP All bugbounty pentesting CVE-2023- POC Exp RCE example payload Things
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 shadow1ng/fscan
一款内网综合扫描工具,方便一键自动化、全方位漏扫扫描。(An intranet comprehensive scanning tool, enabling one-click automated, all-round vulnerability scanning)
 th3xace/sudo_killer
A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 safebuffer/pe-linux
Linux privilege escalation auditing tool that automates system enumeration, kernel vulnerability checks, password collection, log analysis, and cron…
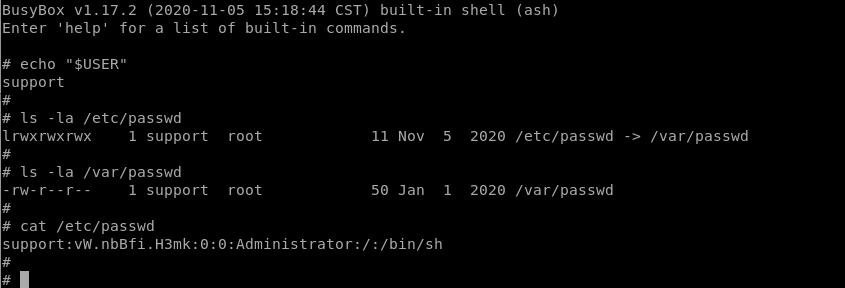 leoservalli/privilege-escalation-mitrastar
Privilege escalation vulnerability on MitraStar routers
 ari034/cve-2020-9758
Form submission for vulnerability in livezilla
 mrchucu1/cve-2022-0847-docker
Docker exploit
 orsuprasad/cve-2022-0847-dirtypipe-exploits
C exploit collection for Linux Dirty Pipe (CVE-2022-0847) local privilege escalation, including read-only file overwrite and SUID binary hijacking,…
 vig9610/exploiting-samba-on-metasploitable-2
Utilize metasploit from a Kali Linux machine to exploit a well-known samba vulnerability (CVE-2007-2447). This is done in order to infiltrate a…
 h3x0v3rl0rd/cve-2019-14287
Shell script to detect CVE-2019-14287 sudo privilege escalation vulnerability. Scans systems for the flaw and reports affected configurations.
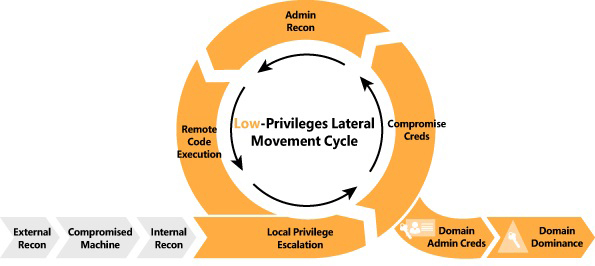 ihebski/a-red-teamer-diaries
RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.
 verrideo/cve-2024-23774
Repository dedicated to CVE-2024-23774, an unquoted Windows service path vulnerability, providing information and potential exploitation details.
 maxime288/fragnesia-cve-2026-46300
Educational repository detailing CVE-2026-46300 (Fragnesia), a Linux kernel local privilege escalation vulnerability. Provides technical analysis,…
 klynezyro/metasploitable2-vapt-report
Comprehensive Penetration Testing report and exploit chain for Metasploitable 2 focusing on CVE-2011-2523.
 gitchw/ghostlock-cve-2026-43499
CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)