Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
12 results
CVE-2024-44258 preview

CVE-2024-44258

GitHubifpdz/cve-2024-44258

CVE-2024-44258

exploitationios-securitymobile-security+3
911 year ago
CVE-2026-43499-pmg110-root preview

CVE-2026-43499-pmg110-root

GitHubsoralis0912/cve-2026-43499-pmg110-root

Android LPE exploit for CVE-2026-43499 targeting OPPO PMG110 (kernel 6.6). Uses futex PI UAF to gain root and install a su daemon via LD_PRELOAD.
android-securitybinary-exploitationexploitation+7
21 month ago
pack2theroot-lab preview

pack2theroot-lab

GitHubdinosn/pack2theroot-lab

CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation

container-securityctfdefensive-tools+7
84 months ago
launchd-portrep preview

launchd-portrep

GitHubbazad/launchd-portrep

CVE-2018-4280: Mach port replacement vulnerability in launchd on macOS 10.13.5 leading to local privilege escalation and SIP bypass.

binary-exploitationexploitationexploit-frameworks+3
597 years ago
Harmonic preview

Harmonic

GitLabrunik/harmonic

Suite for reverse shell handling geared toward working within the native shell

command-and-controlinformation-gatheringpayload-development+7
8 years ago
CVE-2026-41651 preview

CVE-2026-41651

GitHubvozec/cve-2026-41651

Exploits a TOCTOU race in PackageKit's transaction handler to install arbitrary packages as root, achieving local privilege escalation and a SUID…
exploitationprivilege-escalationvulnerability-analysis
1234 months ago
poc-cve-2024-0132 preview

poc-cve-2024-0132

GitHubssst0n3/poc-cve-2024-0132

Proof-of-concept exploit for CVE-2024-0132 enabling container escape via NVIDIA container toolkit, allowing host filesystem access and Docker daemon…
cloud-securitycontainer-escapecontainer-security+3
51 year ago
Document-Linux-Privilege-Escalation preview

Document-Linux-Privilege-Escalation

GitHubcoby-nguyen/document-linux-privilege-escalation

Exploiting the vulnerability called "Dirty_Sock" (CVE-2019-7304) in the REST API for Canonical's snapd daemon.
educationexploitationpenetration-testing+2
1 year ago
CVE-2026-41651 preview

CVE-2026-41651

GitHublutfifakee-project/cve-2026-41651

Local privilege escalation exploit targeting PackageKit's TOCTOU race condition (CVE-2026-41651). Escalates from unprivileged user to root via polkit…
binary-exploitationeducationexploitation+3
43 months ago
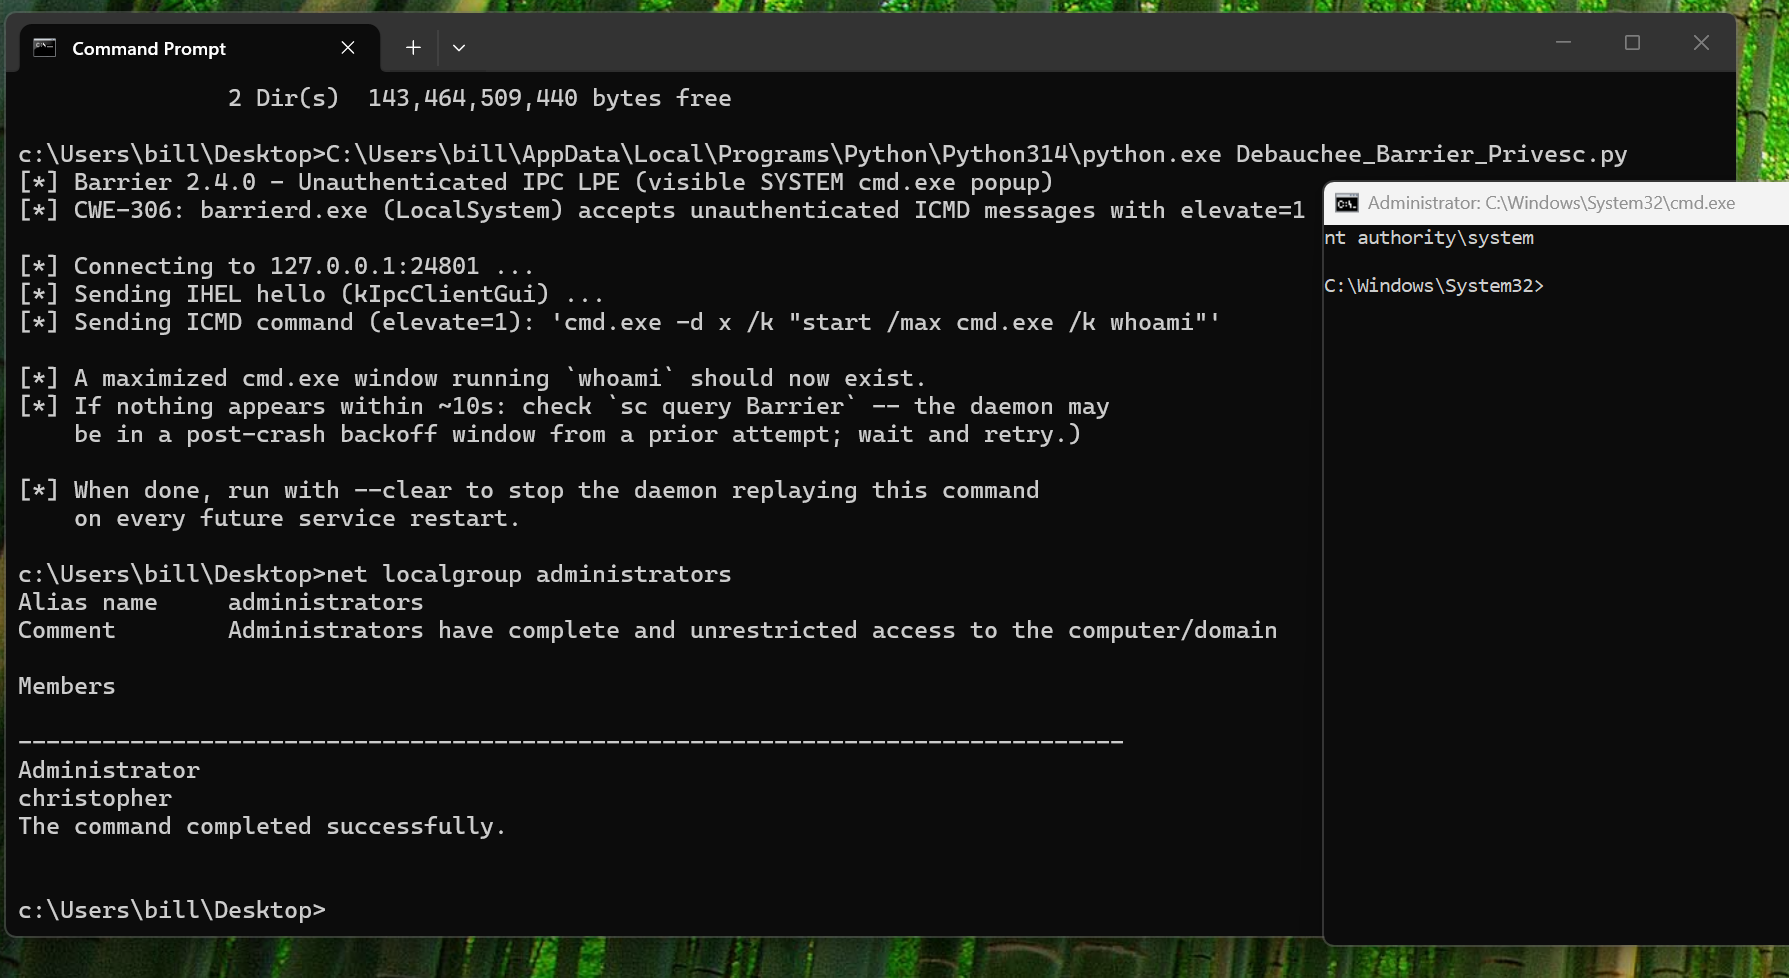
NotCVE-2026-0010 preview

NotCVE-2026-0010

GitHubcduram/notcve-2026-0010

Unauthenticated IPC Local Privilege Escalation to SYSTEM via Debauchee Barrier Daemon TCP Port 24801
exploitationpenetration-testingpost-exploitation+2
1 month ago
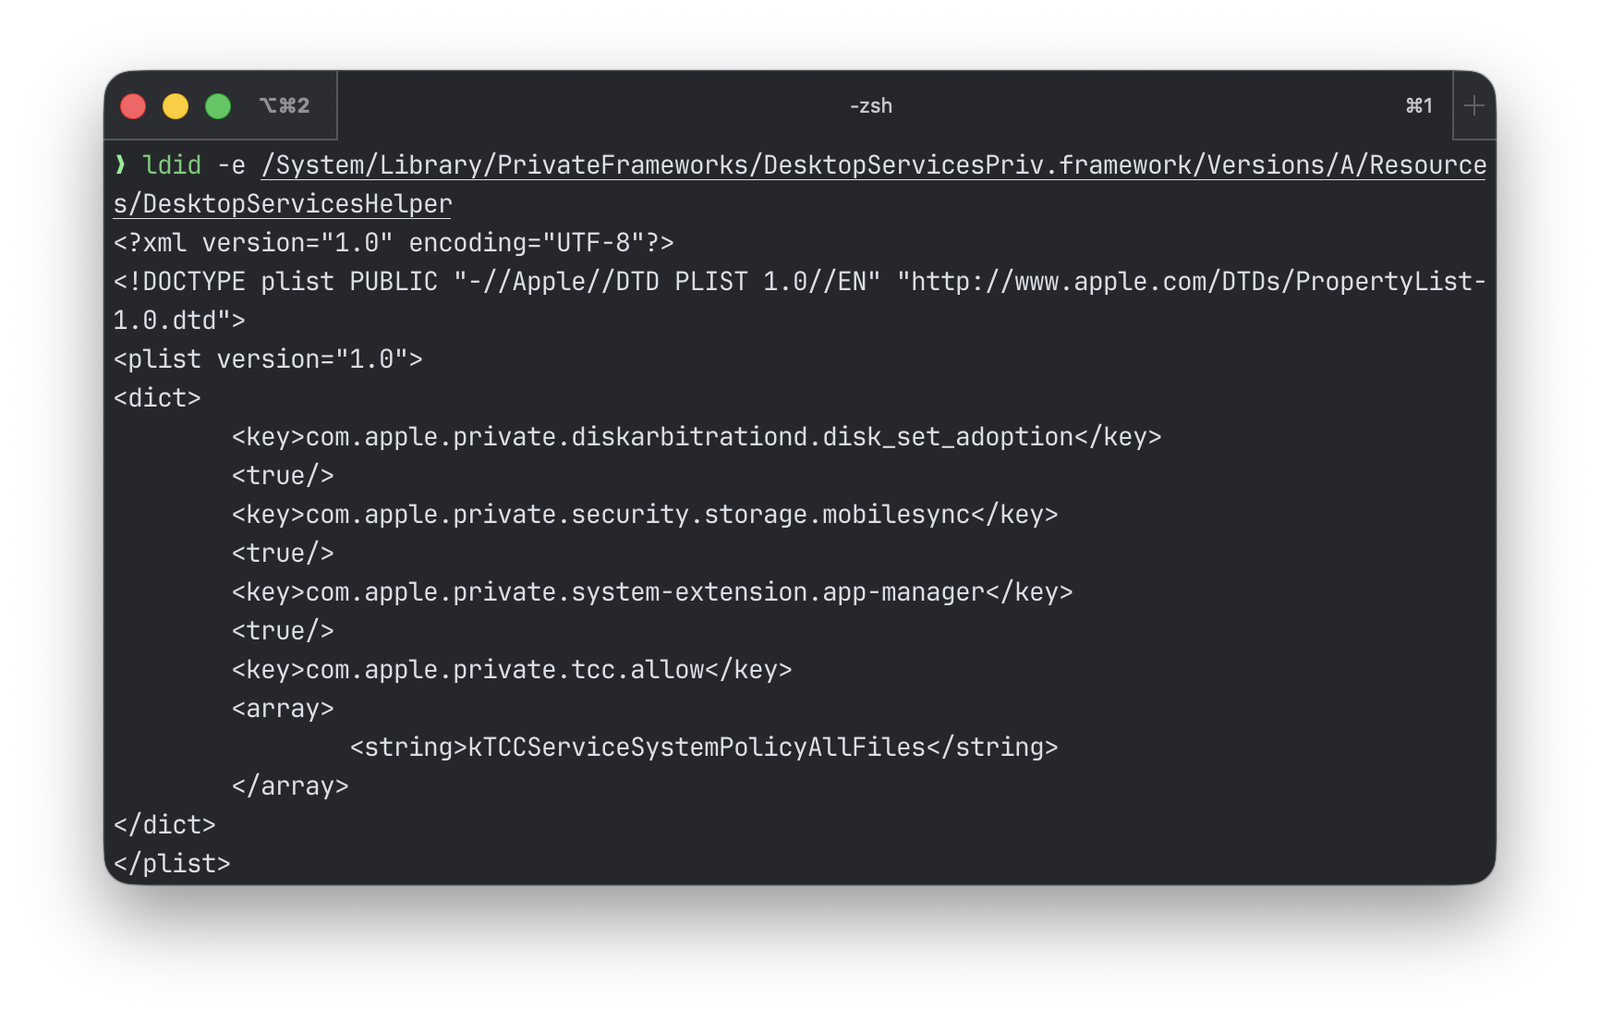
CVE-2026-43783 preview

CVE-2026-43783

GitHubandrd3v/cve-2026-43783

Proof-of-concept and technical writeup for CVE-2026-43783, a macOS local privilege escalation via DesktopServicesHelper XPC arbitrary chown to gain…

binary-analysisexploitationpapers-research+4
26 days ago
CVE-2026-52199 preview

CVE-2026-52199

GitHublamaper/cve-2026-52199

Proof-of-concept exploit for CVE-2026-52199: unauthenticated remote code execution via exposed ADB daemon on UZ801 4G LTE router. Includes…

educationexploitationlabs-practice+5
2 months ago