
adPEAS
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
authenticationexploitationinformation-gathering+6
1.4k5 days ago
61106960/adpeasPowershell tool to automate Active Directory enumeration.
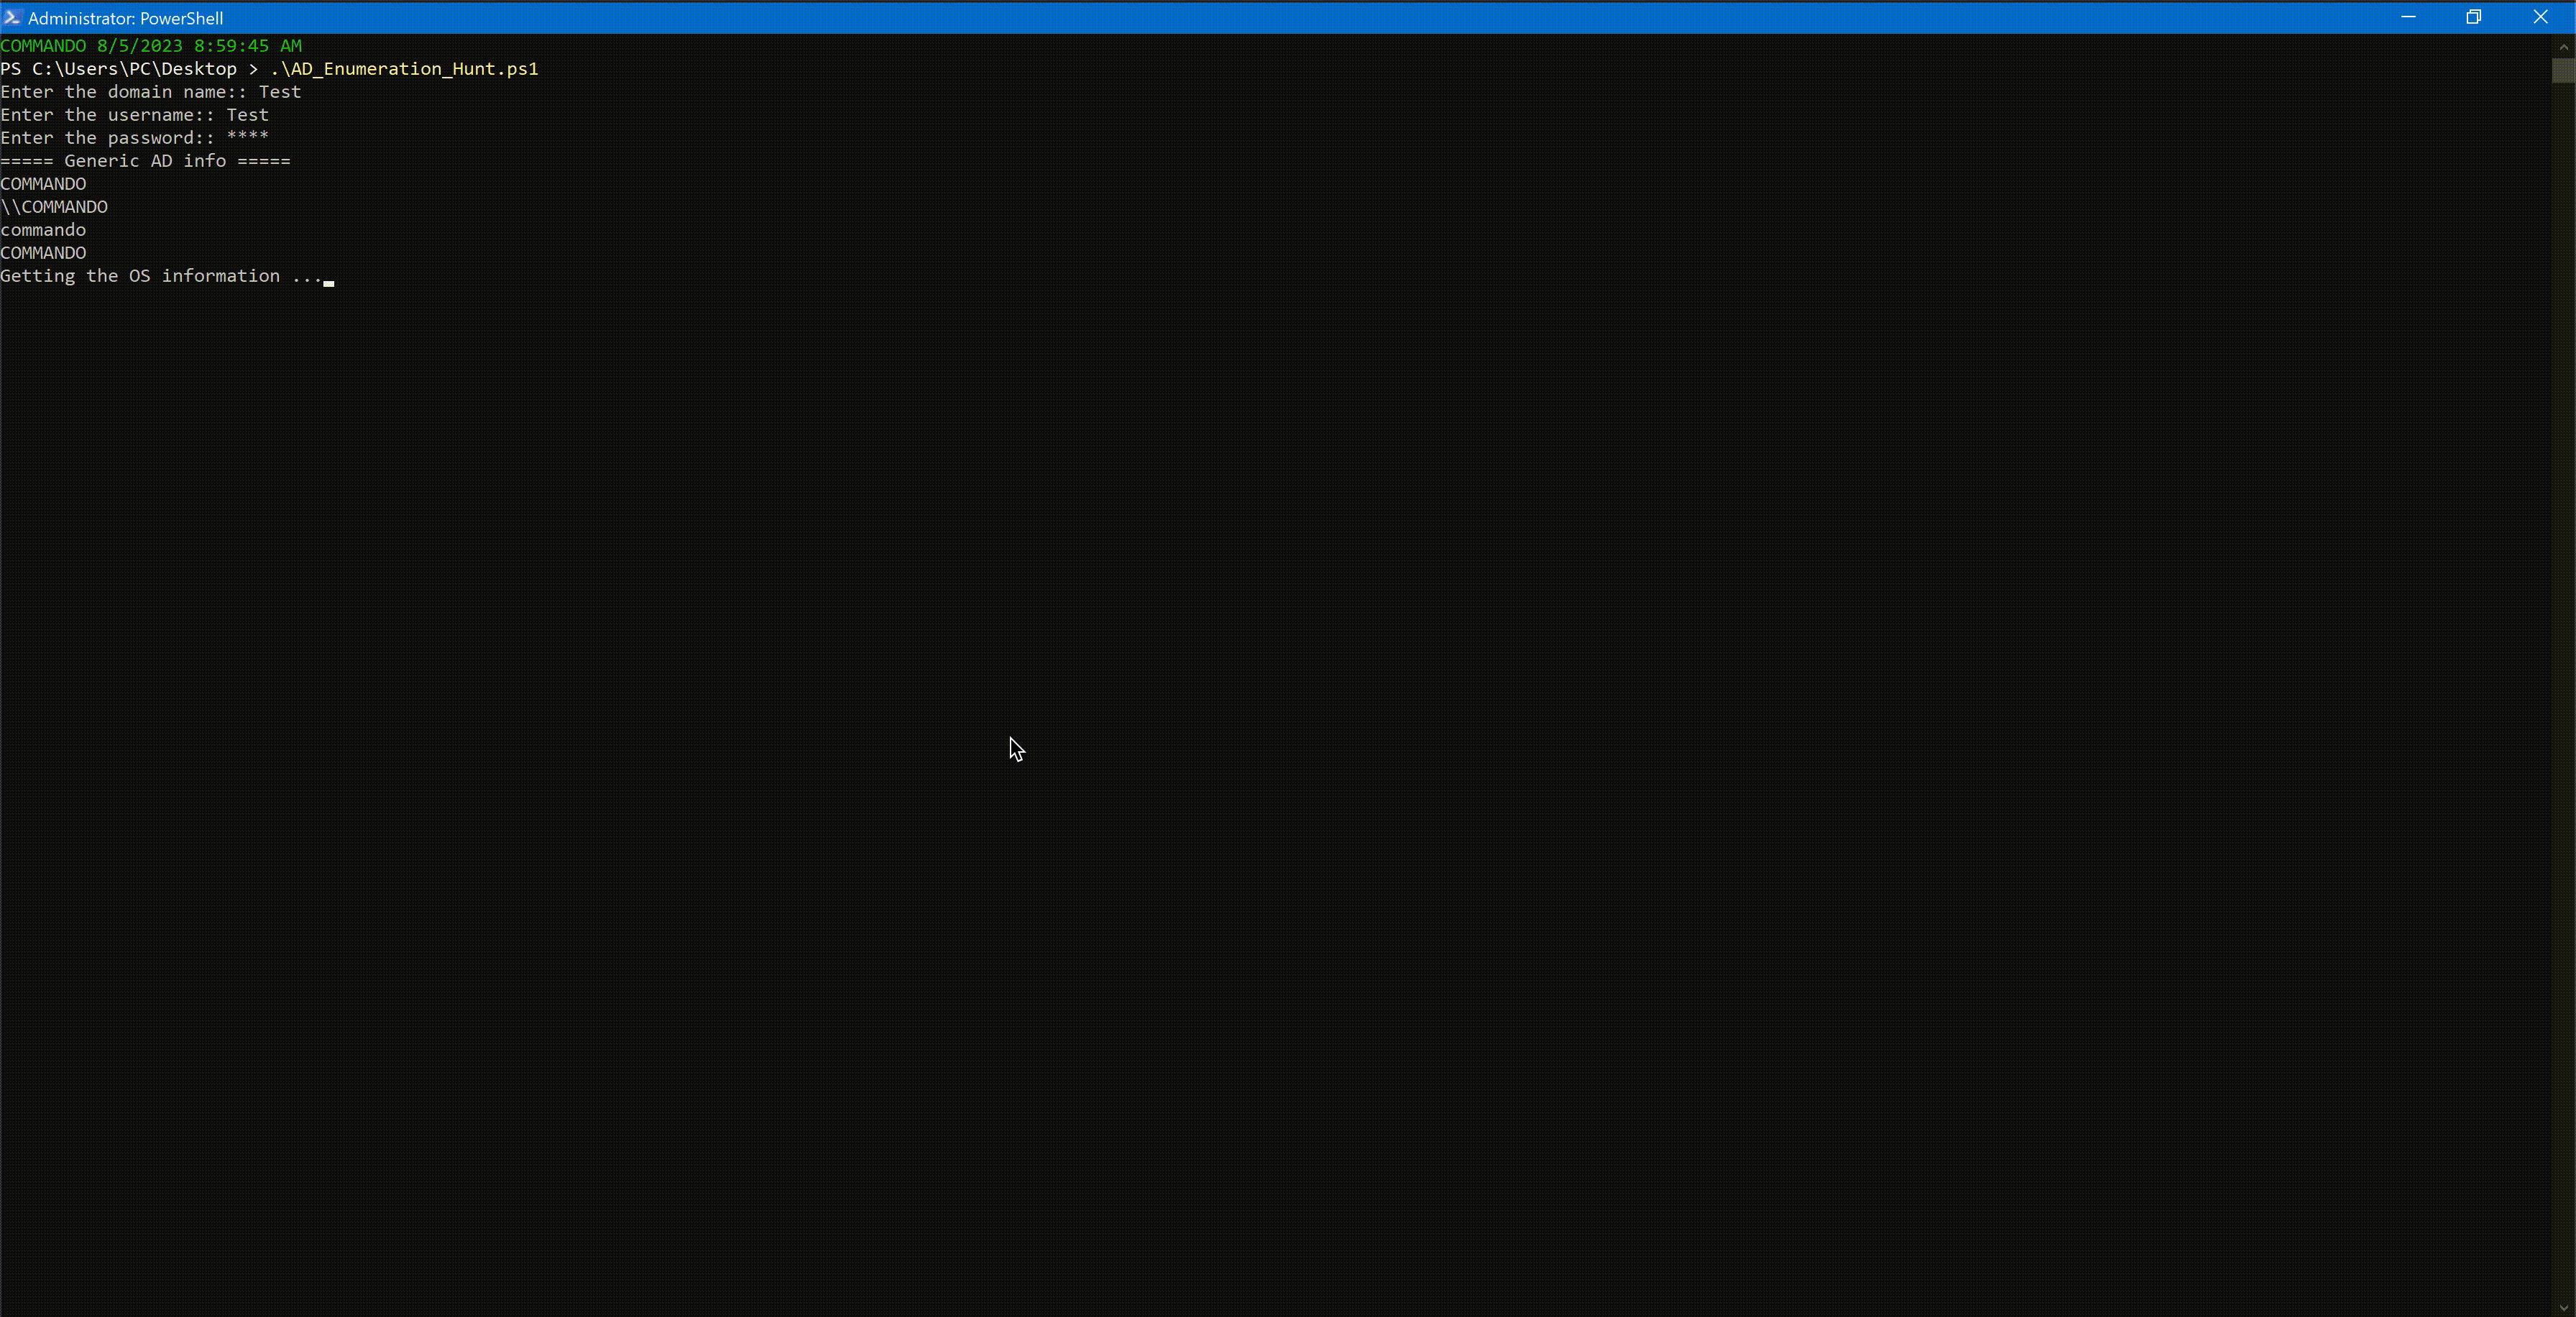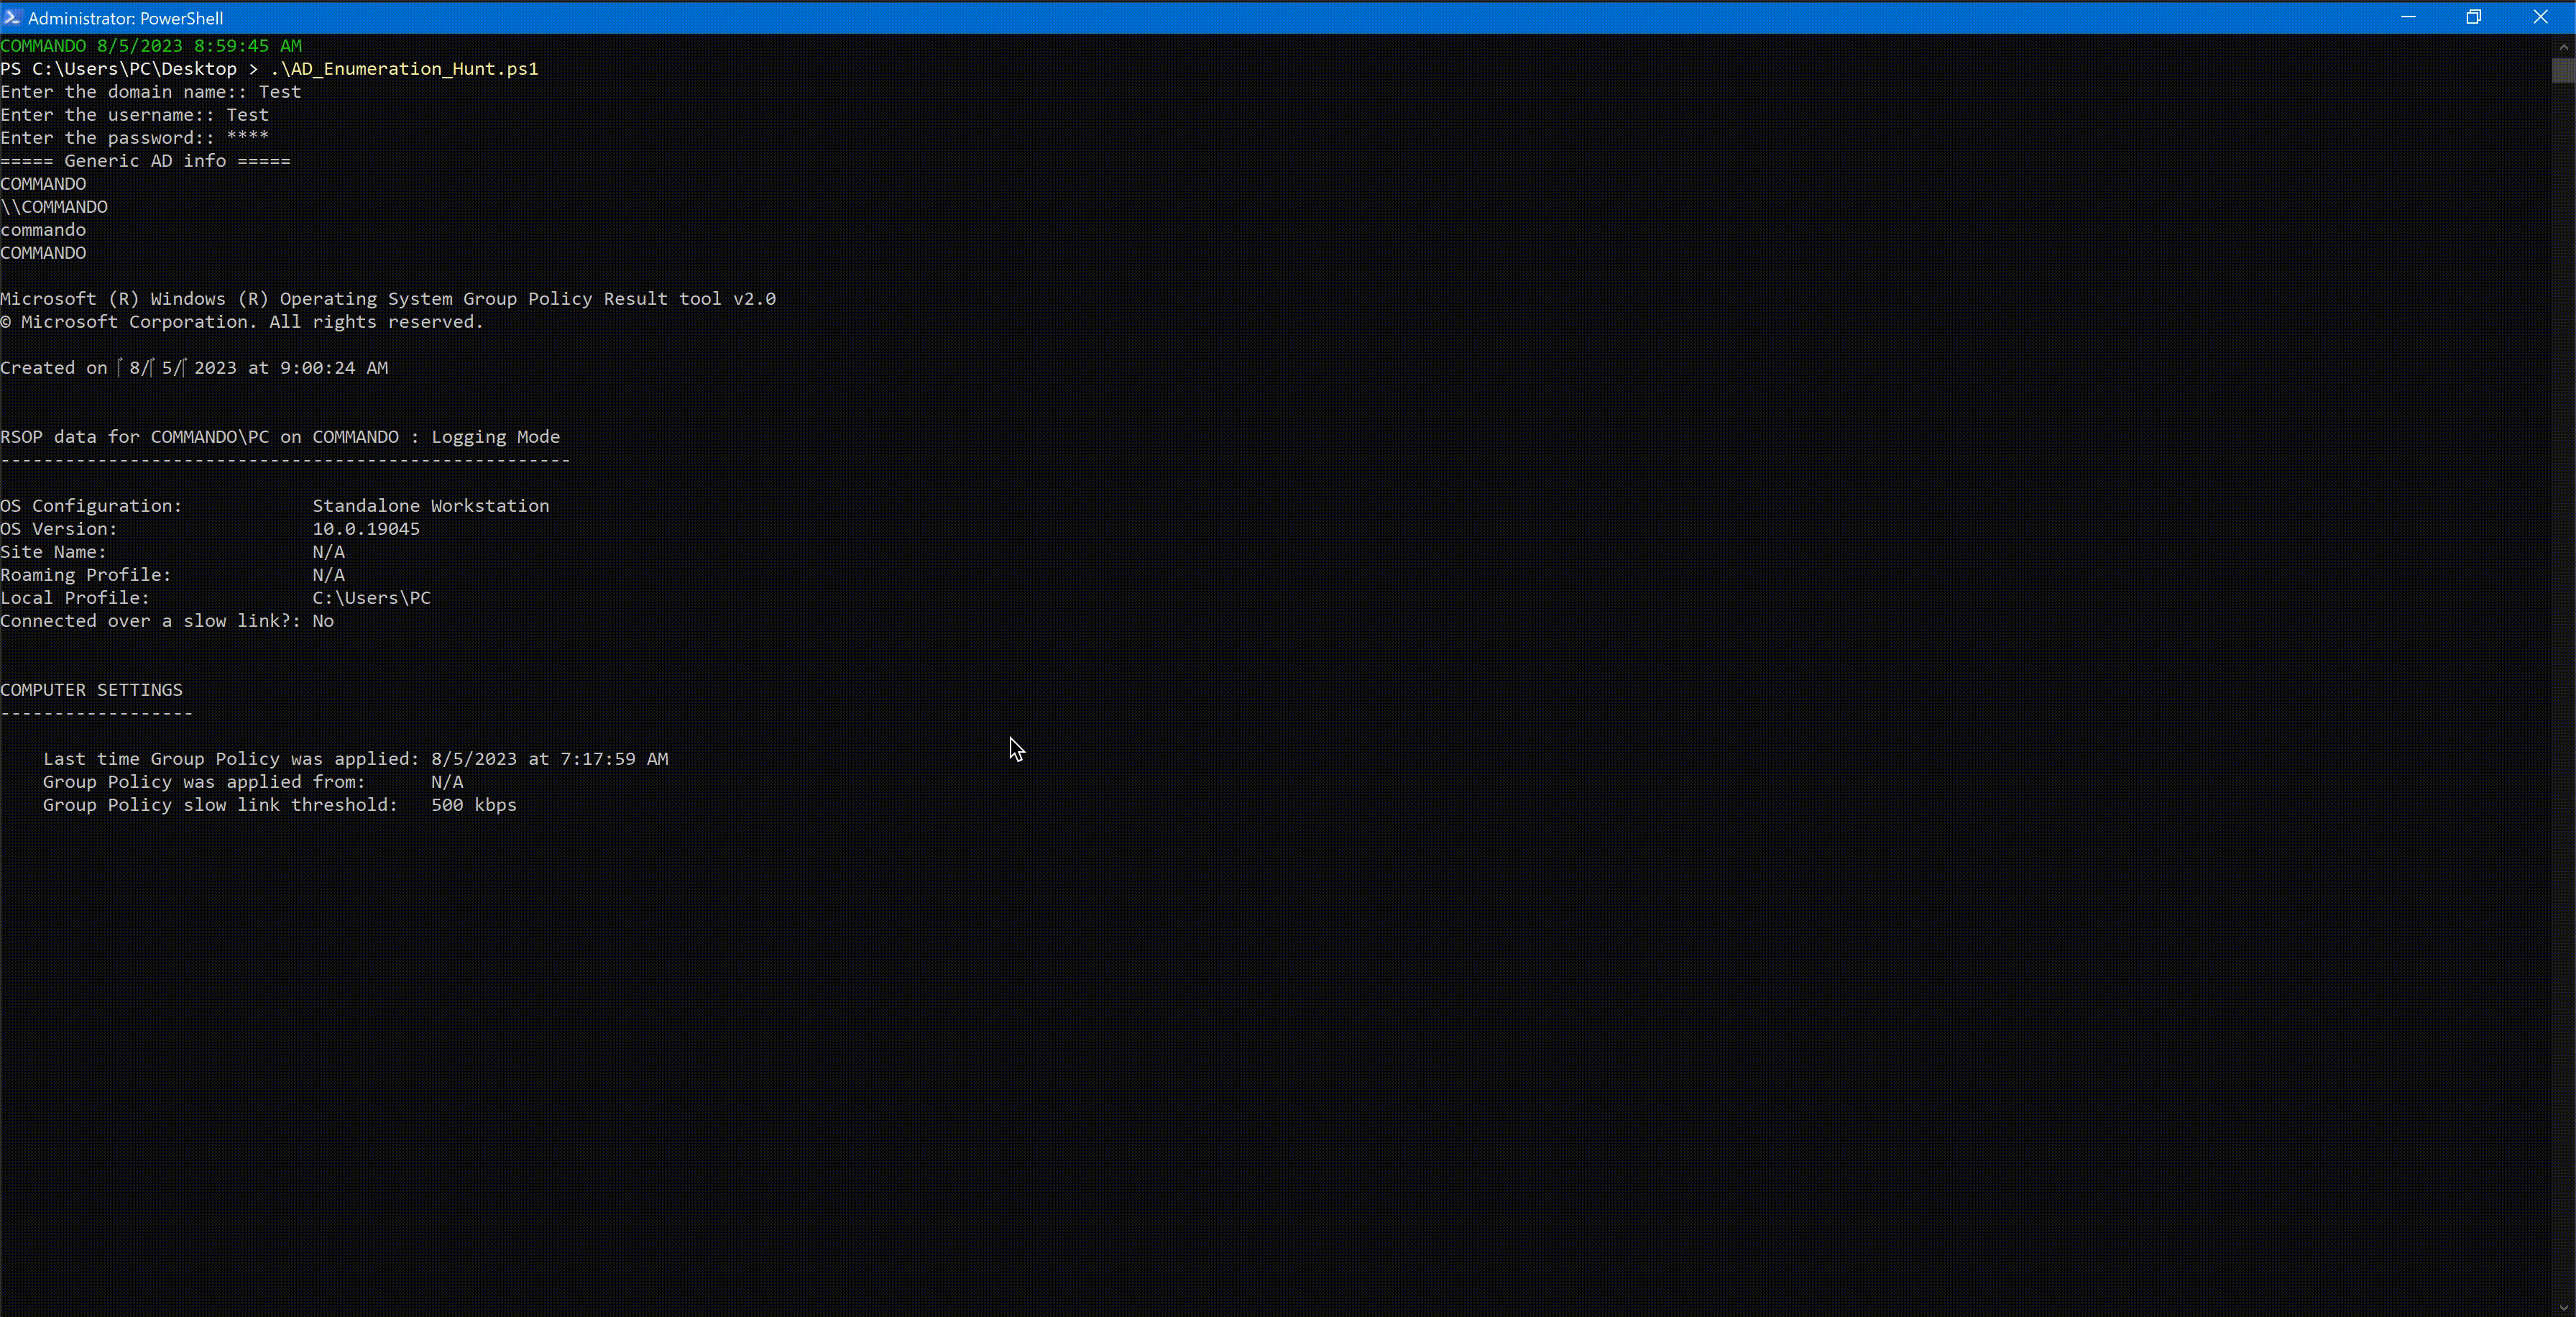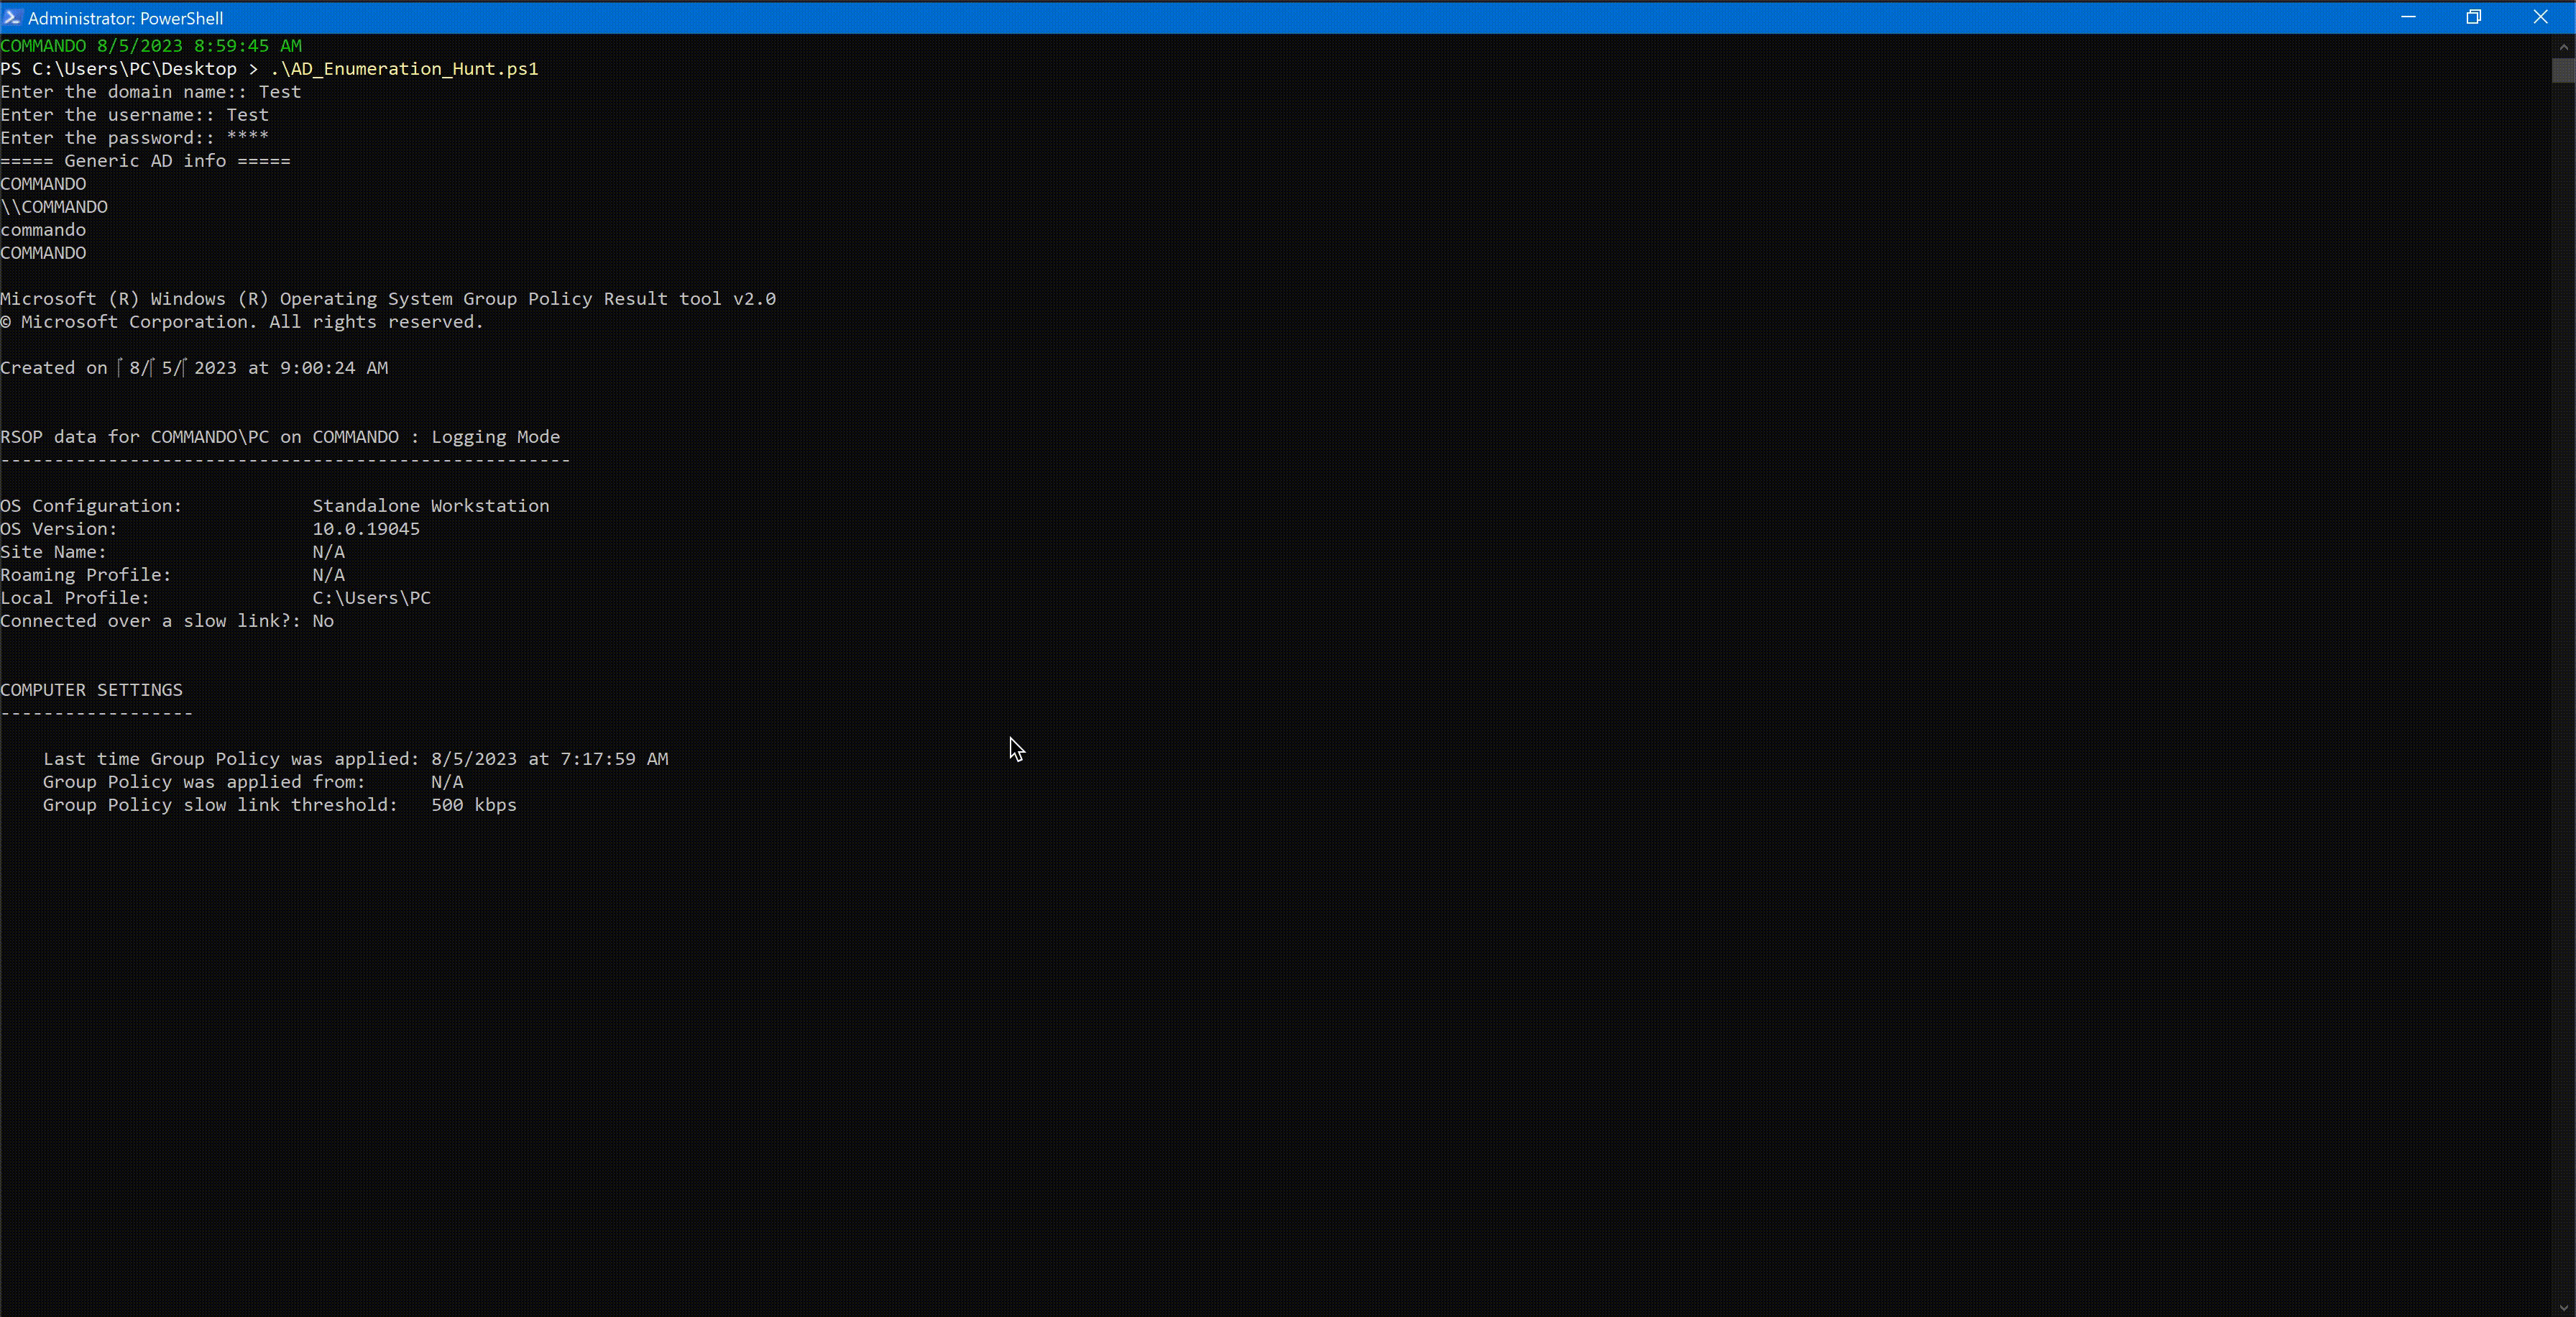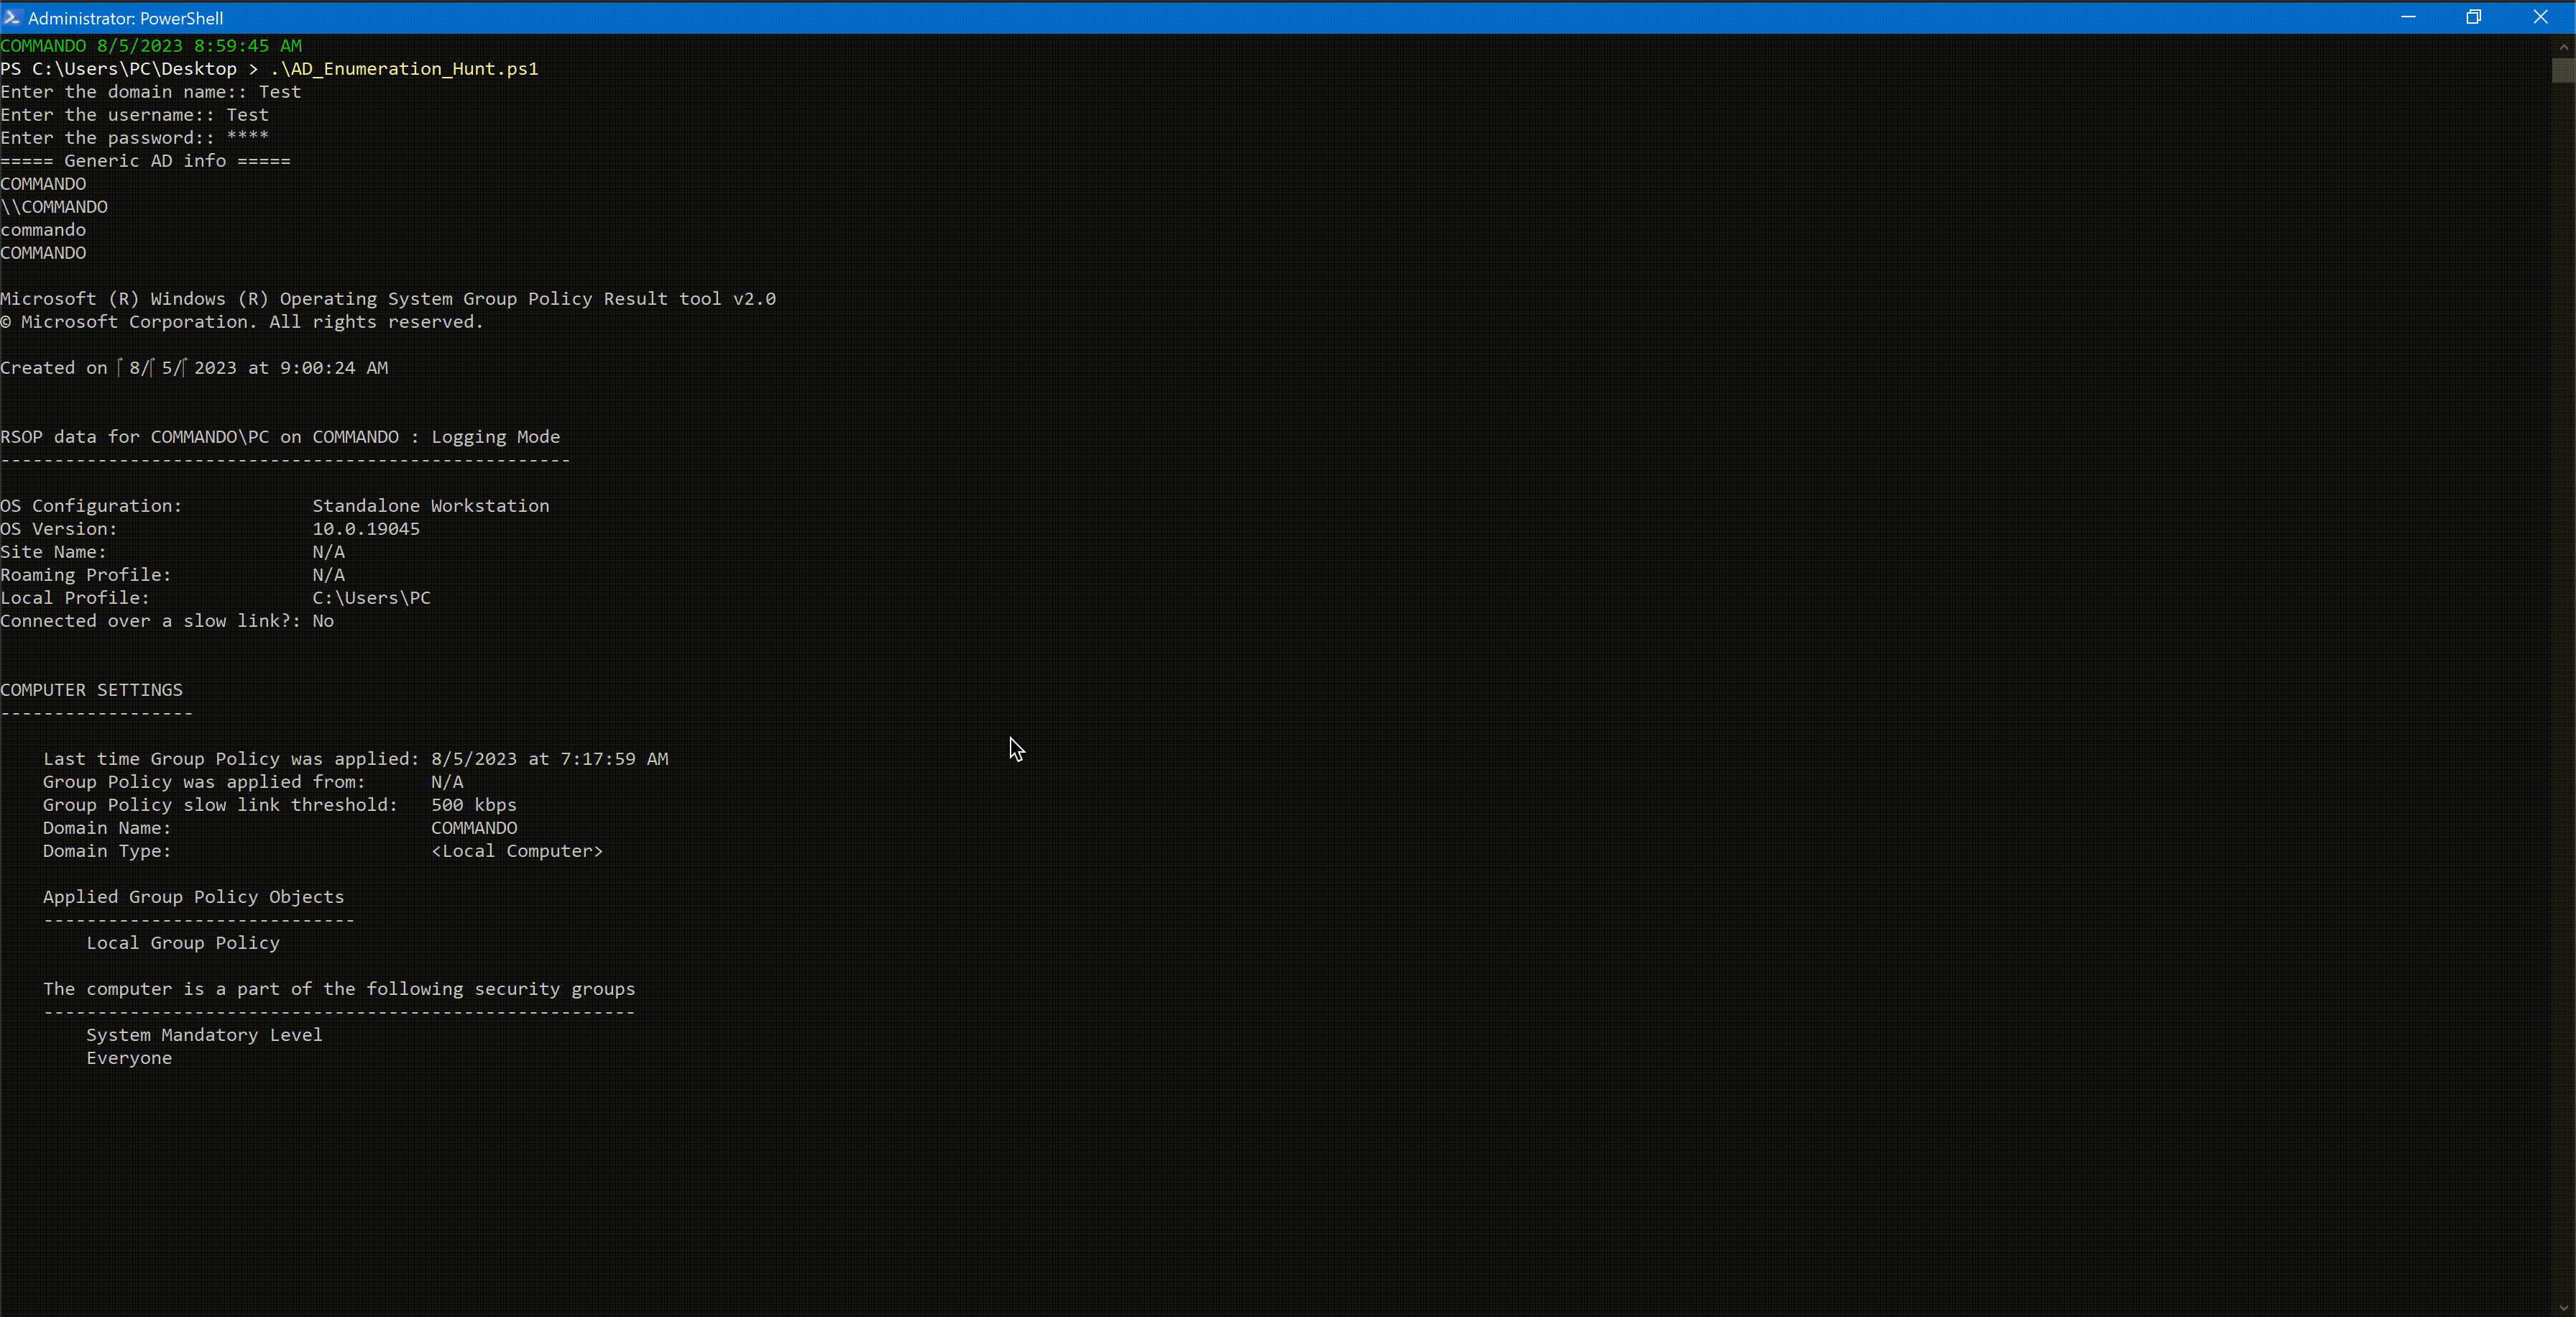 alperenugurlu/ad_enumeration_hunt
PowerShell toolkit for Active Directory penetration testing, featuring domain/user/group enumeration, trust relationship analysis, RDP configuration,…
 mwr-cybersec/pxethief
PXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 lucasjacks0n/eggshell
iOS/macOS/Linux Remote Administration Tool
 redsiege/edd
.NET-based Active Directory enumeration tool inspired by PowerView. Enumerates domains, users, computers, groups, shares, and sessions. Supports LDAP…
 hyd3sec/azur3alph4
PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
 ghostpack/seatbelt
Seatbelt is a C# project that performs a number of security oriented host-survey "safety checks" relevant from both offensive and defensive security…
 nccgroup/gtfoblookup
Offline command line lookup utility for GTFOBins (https://github.com/GTFOBins/GTFOBins.github.io), LOLBAS (https://github.com/LOLBAS-Project/LOLBAS),…
 safebuffer/pe-linux
Linux privilege escalation auditing tool that automates system enumeration, kernel vulnerability checks, password collection, log analysis, and cron…
 tobor88/powershell-red-team
Collection of PowerShell functions a Red Teamer may use in an engagement
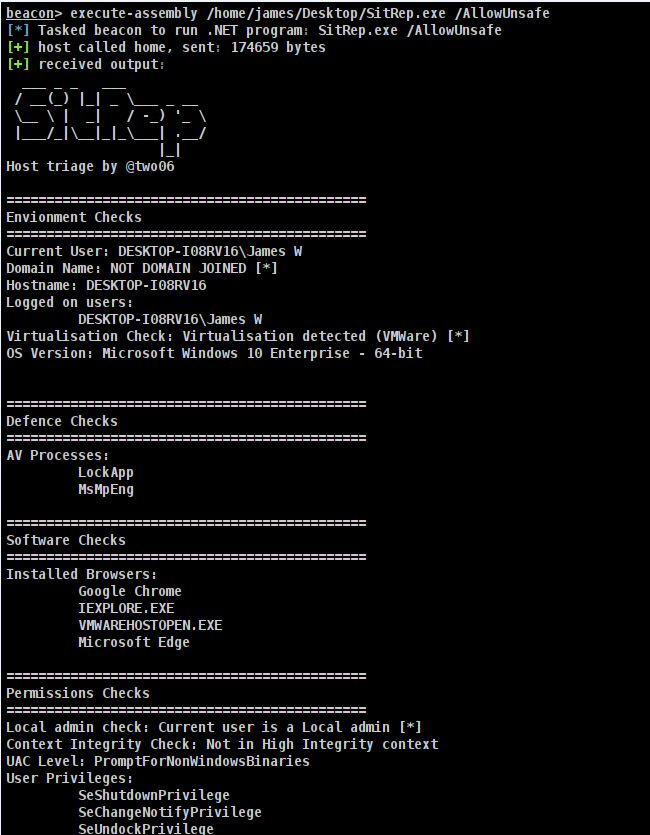 mdsecactivebreach/sitrep
Extensible host triage tool for red teams, dynamically loading OpSec-aware checks to gather user, domain, privilege, and credential information from…
 shac0x/wonka
Wonka is a sweet Windows tool that extracts Kerberos tickets from the Local Security Authority (LSA) cache. Like finding a ticket, but for security…
 twelvesec/rootend
A *nix Enumerator & Auto Privilege Escalation tool.
 ghostpels/cve-2026-18366
Unauthenticated privilege-escalation PoC for WordPress Events Manager < 7.4.1; discovers colliding post/user IDs and escalates targets to…
 ari034/cve-2020-9758
Form submission for vulnerability in livezilla
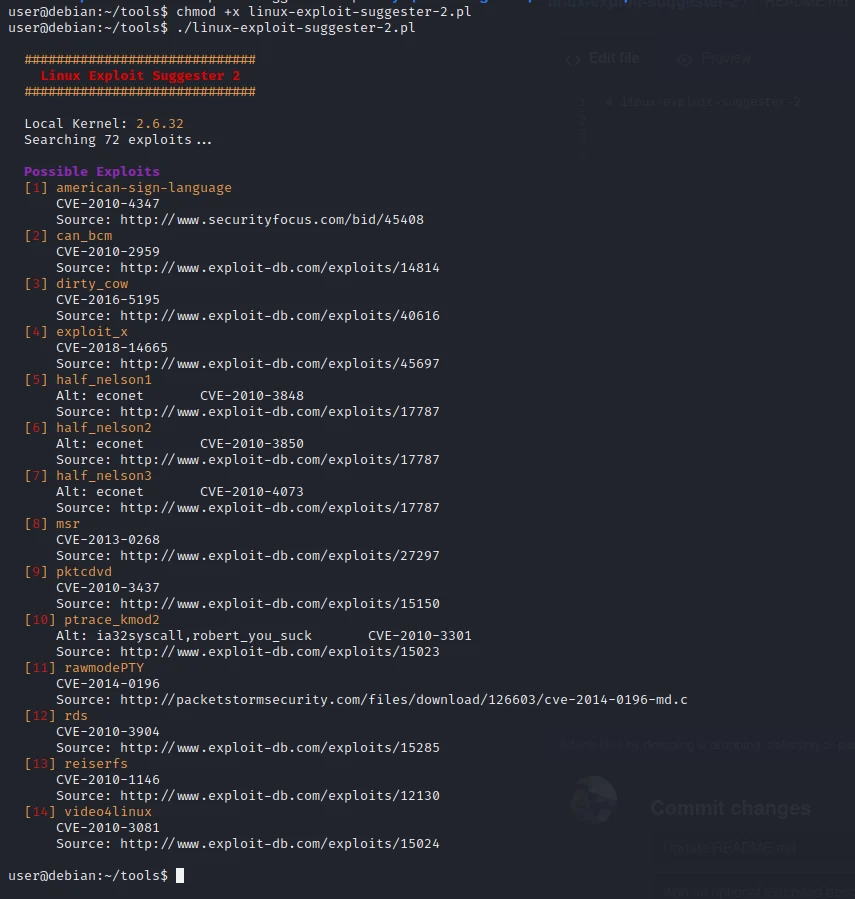 h3x0v3rl0rd/linux-exploit-suggester-2
Post-exploitation utility that scans kernel/OS version and configuration to suggest applicable local privilege escalation exploits.