
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems Security
General Purpose Utilities
Indicator of Compromise (IOC) Management
OSINT (Open Source Intelligence)
Packet Sniffing & Analysis
Password Cracking
Penetration Testing Frameworks
Phishing Tools
Privilege Escalation
Reconnaissance
Static Analysis
Vulnerability Scanners
Web Vulnerability Scanners
Wi-Fi Auditing
Bluetooth Security
Container Security
Dynamic Analysis (Sandboxing)
Encryption/Decryption Tools
Exploit Frameworks
Identity Management
iOS Security
IoT Security
Memory Forensics
Network Mapping
OSINT for Social Engineering
Password Attacks
Payload Generation
Persistence Mechanisms
Port Scanning
Static Code Analysis (SAST)
Threat Feeds & Aggregators
Vulnerability Analysis
Web Proxies & Interception
Code Analysis
DNS & Subdomain Enumeration
Dynamic Code Analysis (DAST)
Exploitation
Hash Analysis
IDS/IPS Evasion
Impersonation Tools
Lateral Movement
Mobile App Pentesting
Network Forensics
Reverse Engineering
RFID/NFC Tools
SCADA/ICS Security
Scripting & Automation
Serverless Security
Shellcode
Web Application Exploitation
API Security Testing
Configuration Auditing
Data Exfiltration
Debuggers
Forensics
Information Gathering
Mobile Forensics
Network Access Control
Post-Exploitation
Security Virtualization
Phishing
WAF Bypass
Web Security
Fuzzing
Network Security
Steganography
Wireless Security
Data Recovery
Malware Analysis
Digital Forensics
Hardware Hacking
Cryptography
CTF
Penetration Testing
Cloud Security
DevSecOps
Mobile Security
Privacy
Command and Control
Social Engineering
Hardware Security
Utilities & Frameworks
Hardware & IoT Security
Secret Detection
Binary Analysis
Threat Intelligence
Identity & Access Management (IAM)
Supply Chain Security
Authentication
Machine Learning
Intrusion Detection
Papers & Research
Misconfiguration
Subdomain Enumeration
Email Harvesting
Learning & Education
AI-Assisted Reversing
DNS Fuzzing
Red Teaming
Incident Response
Crawler
Curated Resources
Remote Access Tool
Shellcode Generation
Payload Development
Remote Access Trojan
API Security
Anti-Bot
Fingerprint Spoofing
CAPTCHA Bypass
Email Security
DNS Analysis
Chaos Engineering
Learning Paths & Courses
Container Escape
AI Security
Database Security
Firmware Analysis
Anomaly Detection
Log Analysis
Adversarial Attack
Binary Exploitation
Labs & Practice
NewestRelevanceMost popularRecently updated
120 results
WinFlesher preview

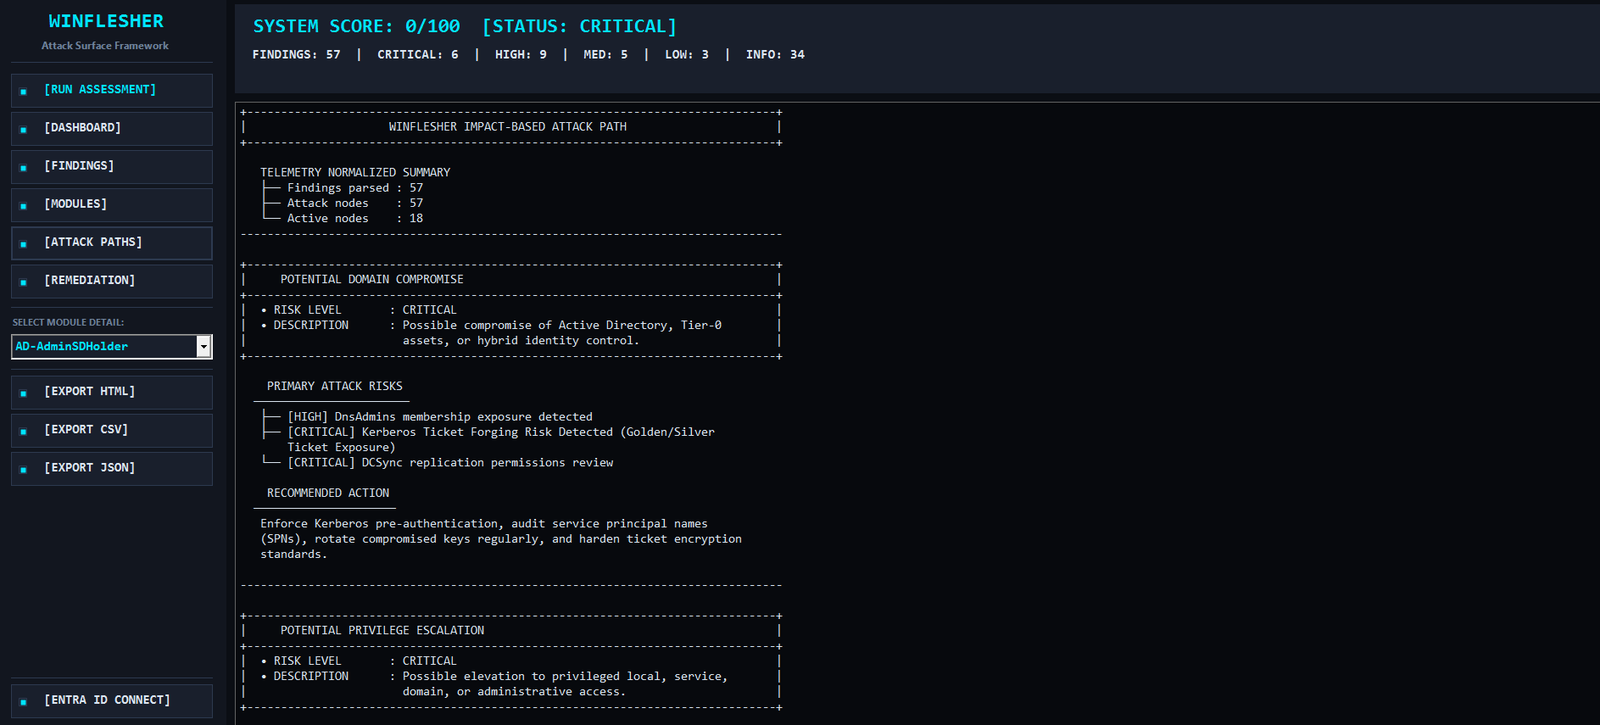
WinFlesher

GitHubmindsflee/winflesher

Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
configuration-auditinglateral-movementpenetration-testing+4
253 days ago
adPEAS preview

adPEAS

GitHub61106960/adpeas

Powershell tool to automate Active Directory enumeration.
authenticationexploitationinformation-gathering+6
1.4k7 days ago
Rubeus preview

Rubeus

GitHubghostpack/rubeus

Trying to tame the three-headed dog.

authenticationexploitationlateral-movement+6
5.2k10 months ago
redamon preview

redamon

GitHubsamugit83/redamon

An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…

ai-securityexploit-frameworkslateral-movement+8
2.6k3 days ago
wasmforge preview

wasmforge

GitHubpraetorian-inc/wasmforge

WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.

binary-analysiscommand-and-controlexploit-frameworks+9
1313 months ago
BloodHound preview

BloodHound

GitHubspecterops/bloodhound

Six Degrees of Domain Admin
defensive-toolsidentity-access-managementinformation-gathering+4
3.4k19h 40m ago
Seatbelt preview

Seatbelt

GitHubghostpack/seatbelt

Seatbelt is a C# project that performs a number of security oriented host-survey "safety checks" relevant from both offensive and defensive security…
defensive-toolsinformation-gatheringpenetration-testing+6
4.7k1 year ago
Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis preview

Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis

GitHubkaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

binary-analysiscommand-and-controldata-exfiltration+4
1023 days ago
Oihk-pentesting preview

Oihk-pentesting

GitHubbroskigx/oihk-pentesting

Autonomous multi-agent AI penetration-testing engine: a governed tool sandbox, an immutable evidence-and-validation gate, and a reproducible…
ai-securityeducationexploit-frameworks+7
44 days ago
EDD preview

EDD

GitHubredsiege/edd

.NET-based Active Directory enumeration tool inspired by PowerView. Enumerates domains, users, computers, groups, shares, and sessions. Supports LDAP…
information-gatheringlateral-movementpenetration-testing+2
3353 years ago
RelayKing-Depth preview

RelayKing-Depth

GitHubdepthsecurity/relayking-depth

Dominate the domain. Relay to royalty.
exploitationids-ips-evasioninformation-gathering+7
3535 months ago
sitrep preview

sitrep

GitHubmdsecactivebreach/sitrep

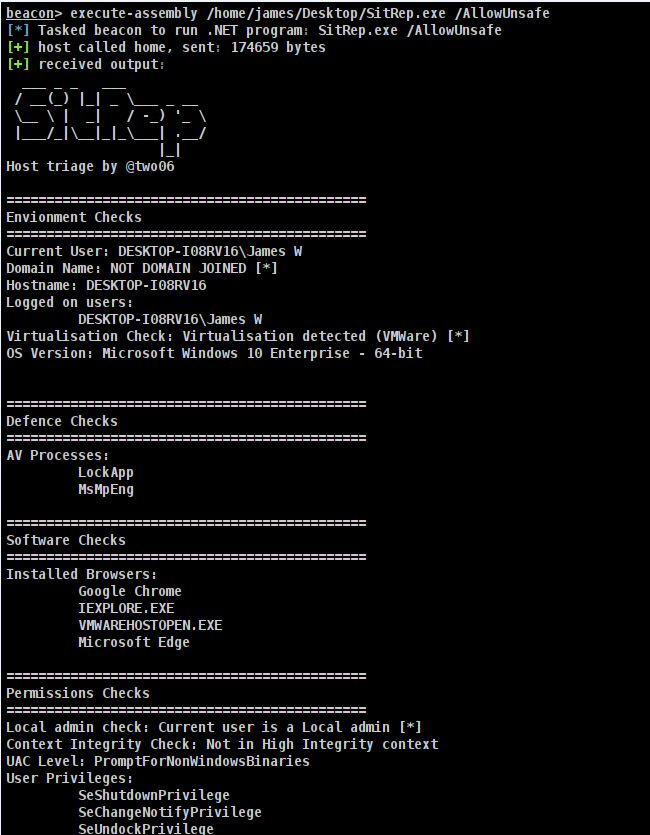
Extensible host triage tool for red teams, dynamically loading OpSec-aware checks to gather user, domain, privilege, and credential information from…

information-gatheringpost-exploitationprivilege-escalation+2
1276 years ago
LSTAR-EN preview

LSTAR-EN

GitHubmoscowchill/lstar-en

LSTAR - CobaltStrike Translated to EN
command-and-controlexploitationids-ips-evasion+9
233 years ago
GPOHound preview

GPOHound

GitHubcogiceo/gpohound

Offensive GPO dumping and analysis tool that leverages and enriches BloodHound data
configuration-auditinginformation-gatheringmisconfiguration+4
4292 months ago
C2-Tool-Collection preview

C2-Tool-Collection

GitHuboutflanknl/c2-tool-collection

A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
command-and-controlexploit-frameworksinformation-gathering+8
1.4k2 years ago
SockTail preview

SockTail

GitHubyeeb1/socktail

Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…
command-and-controllateral-movementnetwork-security+4
57111 months ago
backup_dc_registry preview

backup_dc_registry

GitHubhorizon3ai/backup_dc_registry

A simple POC that abuses Backup Operator privileges to remote dump SAM, SYSTEM, and SECURITY
exploitationlateral-movementmisconfiguration+3
964 years ago
Root-My-Galaxy-Payloads preview

Root-My-Galaxy-Payloads

GitHubnewazbenalam/root-my-galaxy-payloads

Device-specific CVE-2026-43499 root payloads and KernelSU artifacts for Samsung Galaxy models, with firmware profiles, exploit source, and a support…

android-securitybinary-exploitationexploitation+6
10 days ago
Previous1234567Next