
windows-kernel-exploits
 secwiki/windows-kernel-exploits
windows-kernel-exploits Windows平台提权漏洞集合
curated-resourcesexploitationpenetration-testing+2
8.8k
secwiki/windows-kernel-exploitswindows-kernel-exploits Windows平台提权漏洞集合
 k8gege/cve-2021-1675
Exploit for CVE-2021-1675 (PrintNightmare) enabling local and remote SYSTEM-level privilege escalation on Windows via the Print Spooler service.…
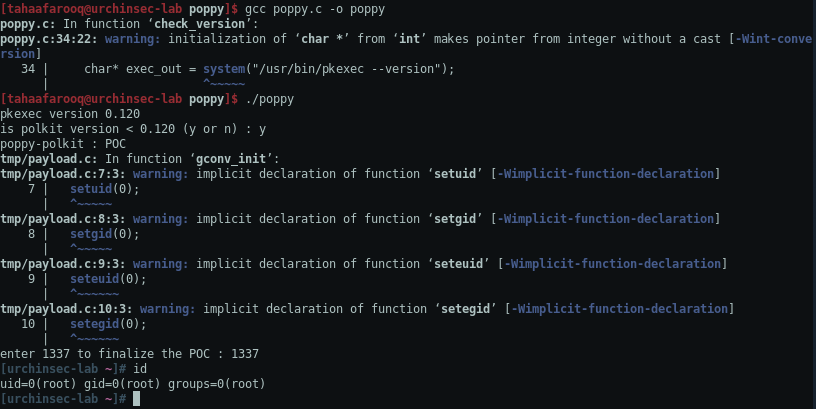 tahaafarooq/poppy
CVE-2021-4034 PoC , polkit < 0.131
 exploitblizzard/windowsmdm-lpe-0day
CVE-2021-24084 Windows Local Privilege Escalation Left officially unpatched since 2020. Hence, its still a zero day
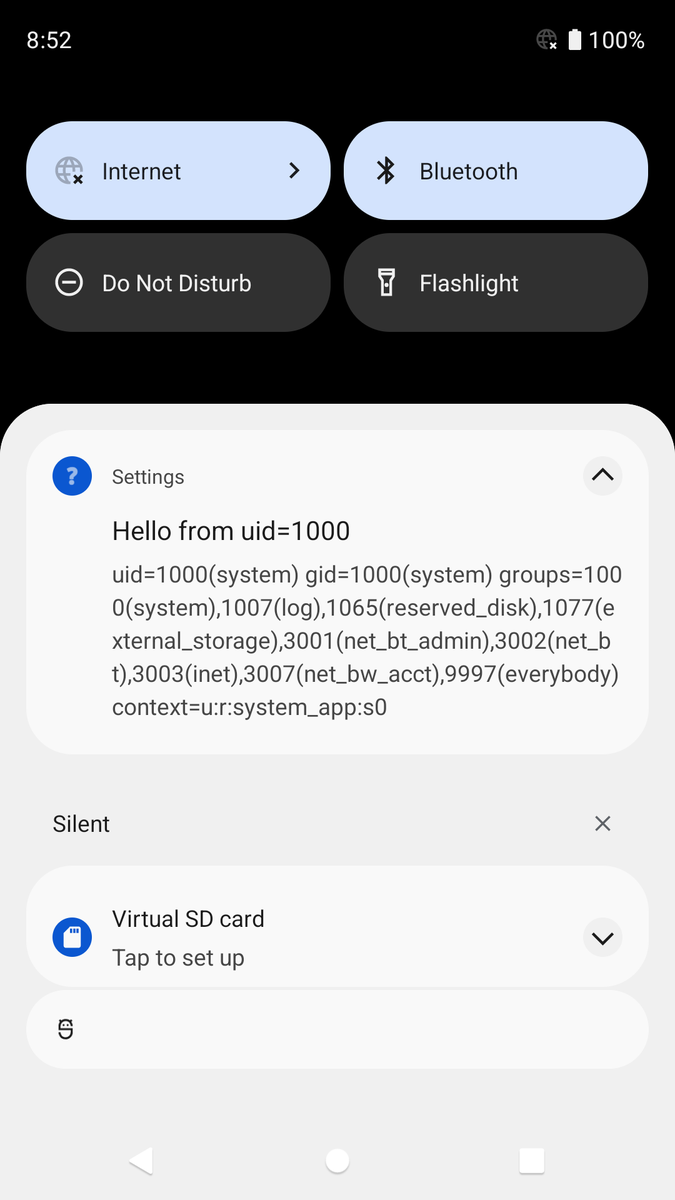 michalbednarski/reparcelbug2
Writeup and exploit for installed app to system privilege escalation on Android 12 Beta through CVE-2021-0928, a `writeToParcel`/`createFromParcel`…
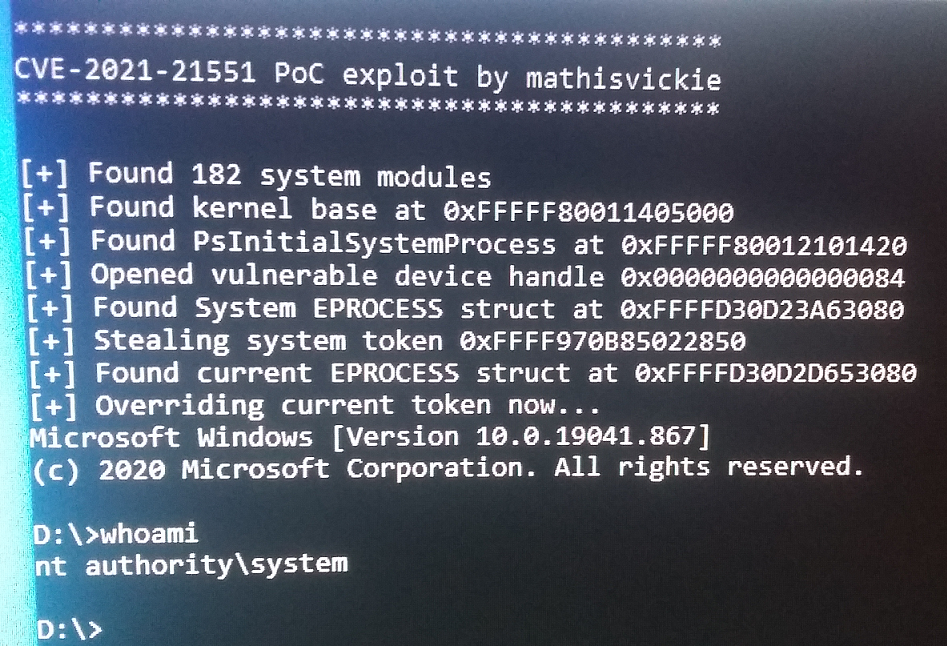 mathisvickie/cve-2021-21551
arbitrary kernel read/write in dbutil_2_3.sys, Proof of Concept Local Privilege Escalation to nt authority/system
 wh04m1001/vsscopy
Small and dirty PoC for CVE-2021-36934
 fathallah17/overlayfs-cve-2021-3493
Exploit a 2021 Kernel vulnerability in Ubuntu to become root almost instantly!
 khuntor/cve-2021-43858-minio
Go-based exploit for CVE-2021-43858 targeting MinIO privilege escalation vulnerability. Executes against a specified IP and port to demonstrate the…
 xmco/sdwan-cve-2021-1480
PoC materials to exploit the CVE-2021-1480 on Cico SD-WAN.
 ly4k/printnightmare
Python implementation for PrintNightmare (CVE-2021-1675 / CVE-2021-34527)
 0xdea/raptor_infiltrate20
#INFILTRATE20 raptor's party pack.
 usmansec/-cve-2021-4034
Controlled proof-of-concept assessment and exploitation report for CVE-2021-4034 (PwnKit) local privilege escalation in pkexec/polkit, with forensic…
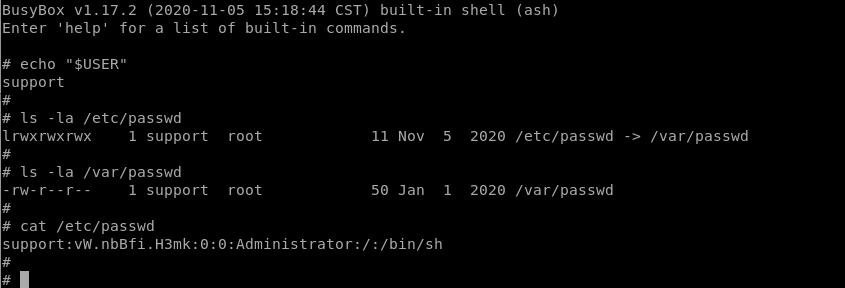 leoservalli/privilege-escalation-mitrastar
Privilege escalation vulnerability on MitraStar routers
 z3r0space/cve-2021-4034
This contains single-file exploit for cve-2021-4034 which is a Polkit Local Privilege Escalation. Use it wisely!
 tr3ee/cve-2021-4204
CVE-2021-4204: Linux Kernel eBPF Local Privilege Escalation
 flyinbedxyz/cve-2021-1732
Local privilege escalation exploit for CVE-2021-1732 targeting Windows 10 and Server versions, with PoC code and affected system enumeration.
 shams-ul-mehmood/cve-2021-3156-project
Educational lab environment for CVE-2021-3156 (Baron Samedit) with a Dockerized vulnerable sudo target, exploit scaffold, canary test, root-cause…