adversarial-robustness-toolbox

Python library for adversarial machine learning security, enabling red and blue teams to run evasion, poisoning, extraction, and inference attacks…

Python library for adversarial machine learning security, enabling red and blue teams to run evasion, poisoning, extraction, and inference attacks…

A privacy-first app that strips AI watermarks from content you own.

Evades LLM text watermarks by injecting Unicode variation selectors; includes the SynthID generator, mean-g detector, normalization defenses, and…

Research-only AI watermark robustness toolkit: local reverse proxy strips C2PA/EXIF/XMP, Unicode, image/audio stego, OOXML/PDF metadata, and scans…

A collection of awesome resources related AI security

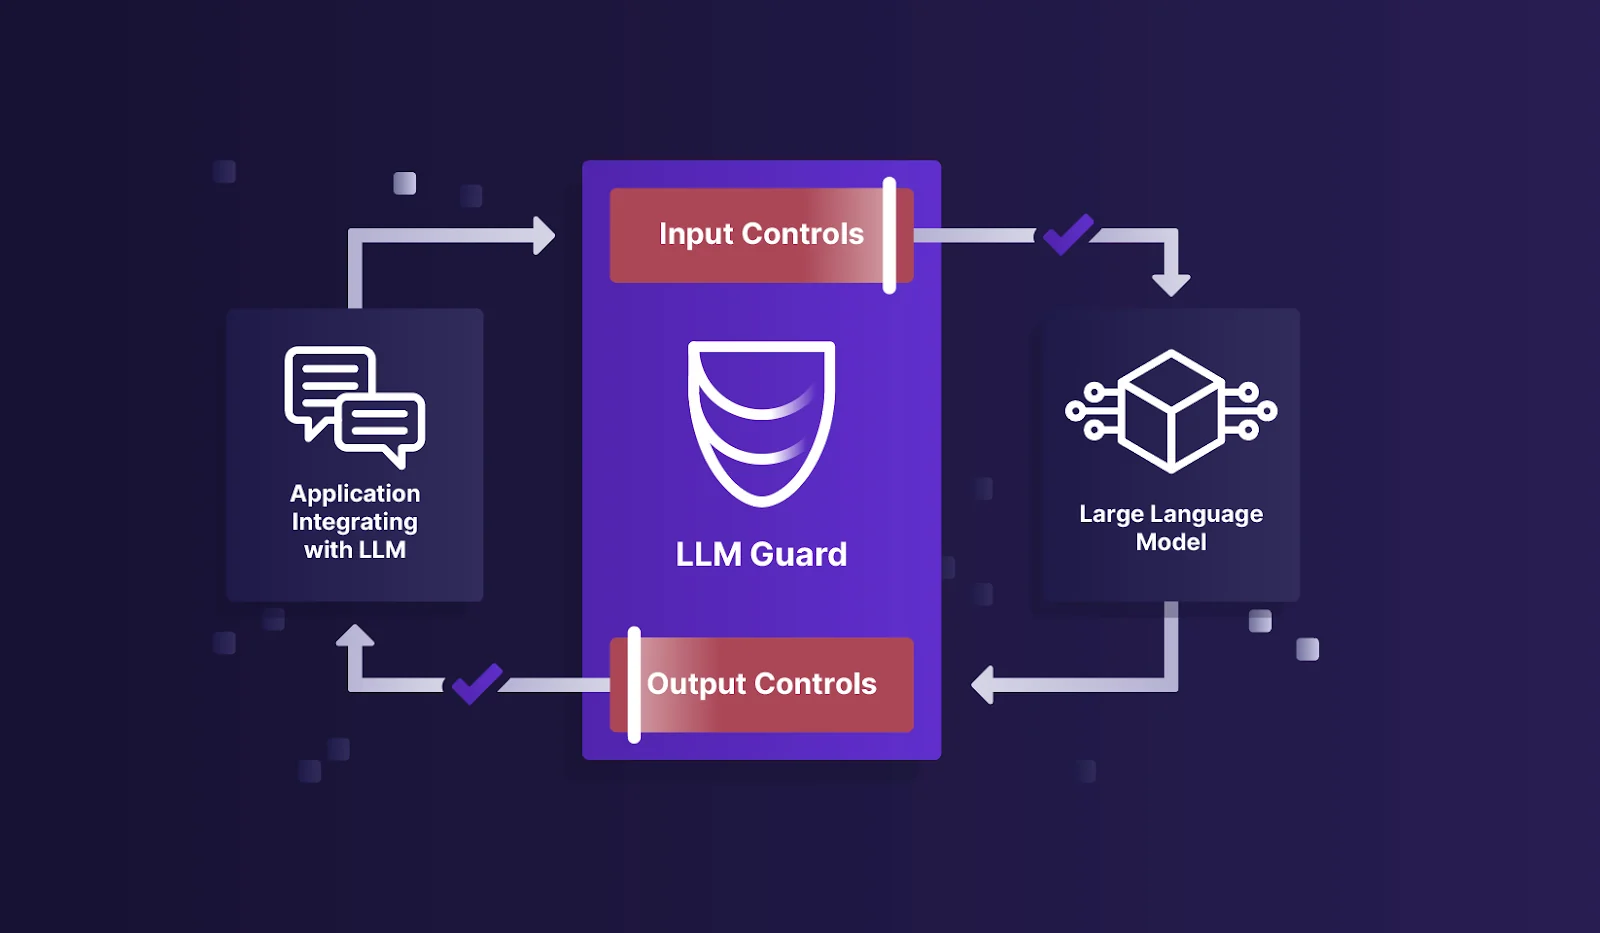
The Security Toolkit for LLM Interactions

Improve your security and privacy by blocking ads, tracking and malware domains.

The code for ACM MM2024 (Multimodal Unlearnable Examples: Protecting Data against Multimodal Contrastive Learning)

Privacy testing library for deep learning systems, enabling assessment of susceptibility to membership inference, model extraction, and model…

Privaxy is the next generation tracker and advertisement blocker. It blocks ads and trackers by MITMing HTTP(s) traffic. Also check out my new…

Never ever ever use pixelation as a redaction technique

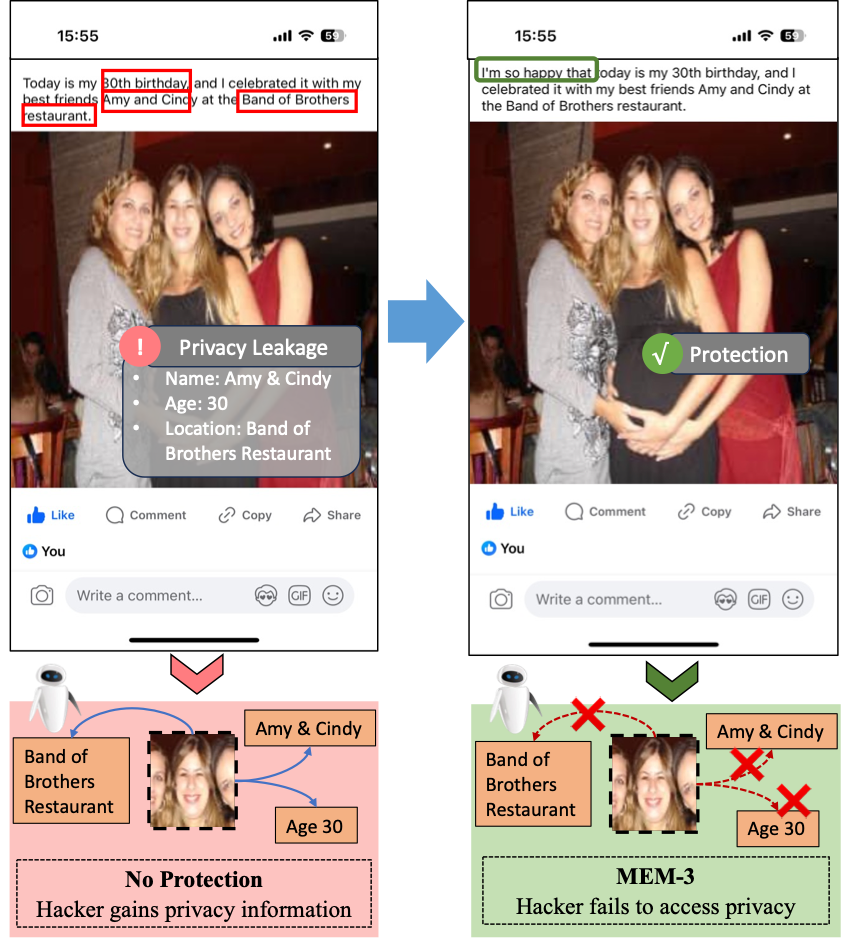
Mobile camera-based application that attempts to alter photos to preserve their utility to humans while making them unusable for facial recognition…

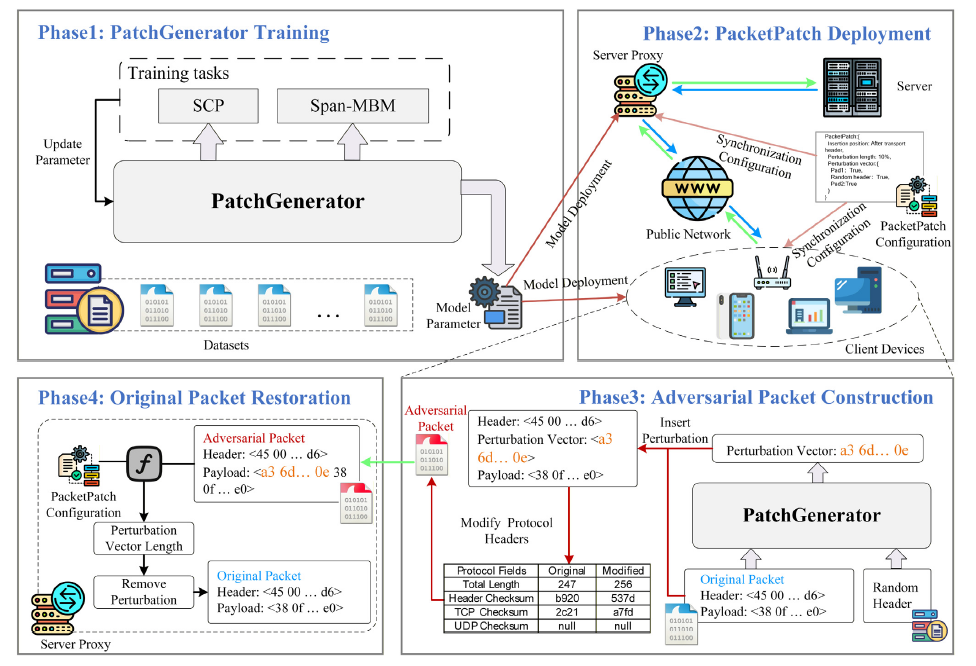
Practical black-box adversarial packet generation against encrypted traffic classification with minimal overhead and full packet recoverability.

This project (PoC for now, and part of Shit Bucket) involves face detection, face recognition and adversarial input to protect avatars

Browser PoC demonstrating CVE-2026-2828, a WebGPU timing side-channel that leaks cross-origin iframe pixel values by measuring GPU timestamp-query…

CVE-2026-6765, Test only FormAutofill handlers exposed in Firefox