

Comment2Shell
 deathshotxd/comment2shell
Zero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…
exploitationlabs-practicepayload-development+7
61
deathshotxd/comment2shellZero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…
 samratashok/nishang
Nishang - Offensive PowerShell for red team, penetration testing and offensive security.
 aktia1/megaquagga_pentesting_report
Web application penetration testing project targeting a WordPress environment. Includes exploitation of CVE-2019-9978, reverse shell execution,…
 justicerage/freedomfighting
A collection of scripts which may come in handy during your freedom fighting activities.
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
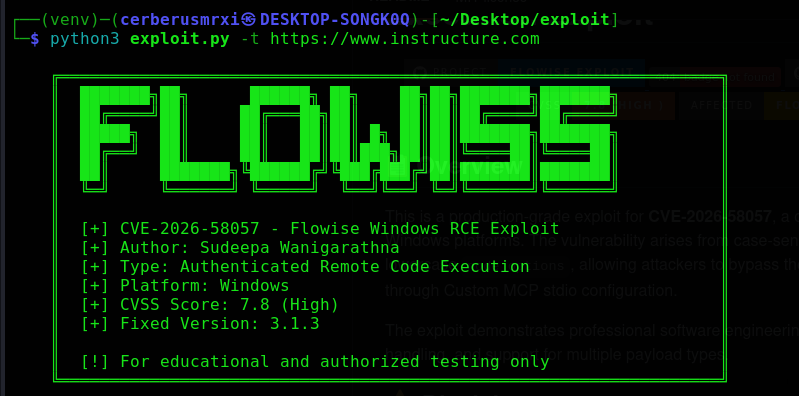 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
 hackhermind-pixel/vulnerable-lab-exploitation
A hands-on project demonstrating the setup of virtual security lab, network reconnaissance, and exploitation of CVE-2012-1823.
 zephrfish/azureattackkit
Collection of Azure Tools to Pull down for Attacking an Environment + quick tips and other useful information
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
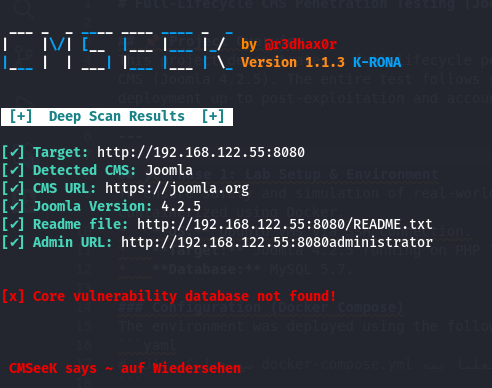 marwan651/joomla-cms-full-lifecycle-pentest
A comprehensive full-lifecycle penetration testing project on Joomla 4.2.5 exploiting CVE-2023-23752 inside a Dockerized lab environment
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
 alixiacf/hpim-training-lab
Trained to Escalate: Forensic Analysis and Local Replication of RLHF-Induced Privilege Escalation in AI Agents (CVE-2026-65616)
 rootsecnz/htb-ctf-walkthroughs
Walkthroughs for Capture the Flag challenges on the HTB Cybersecurity Platform.
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
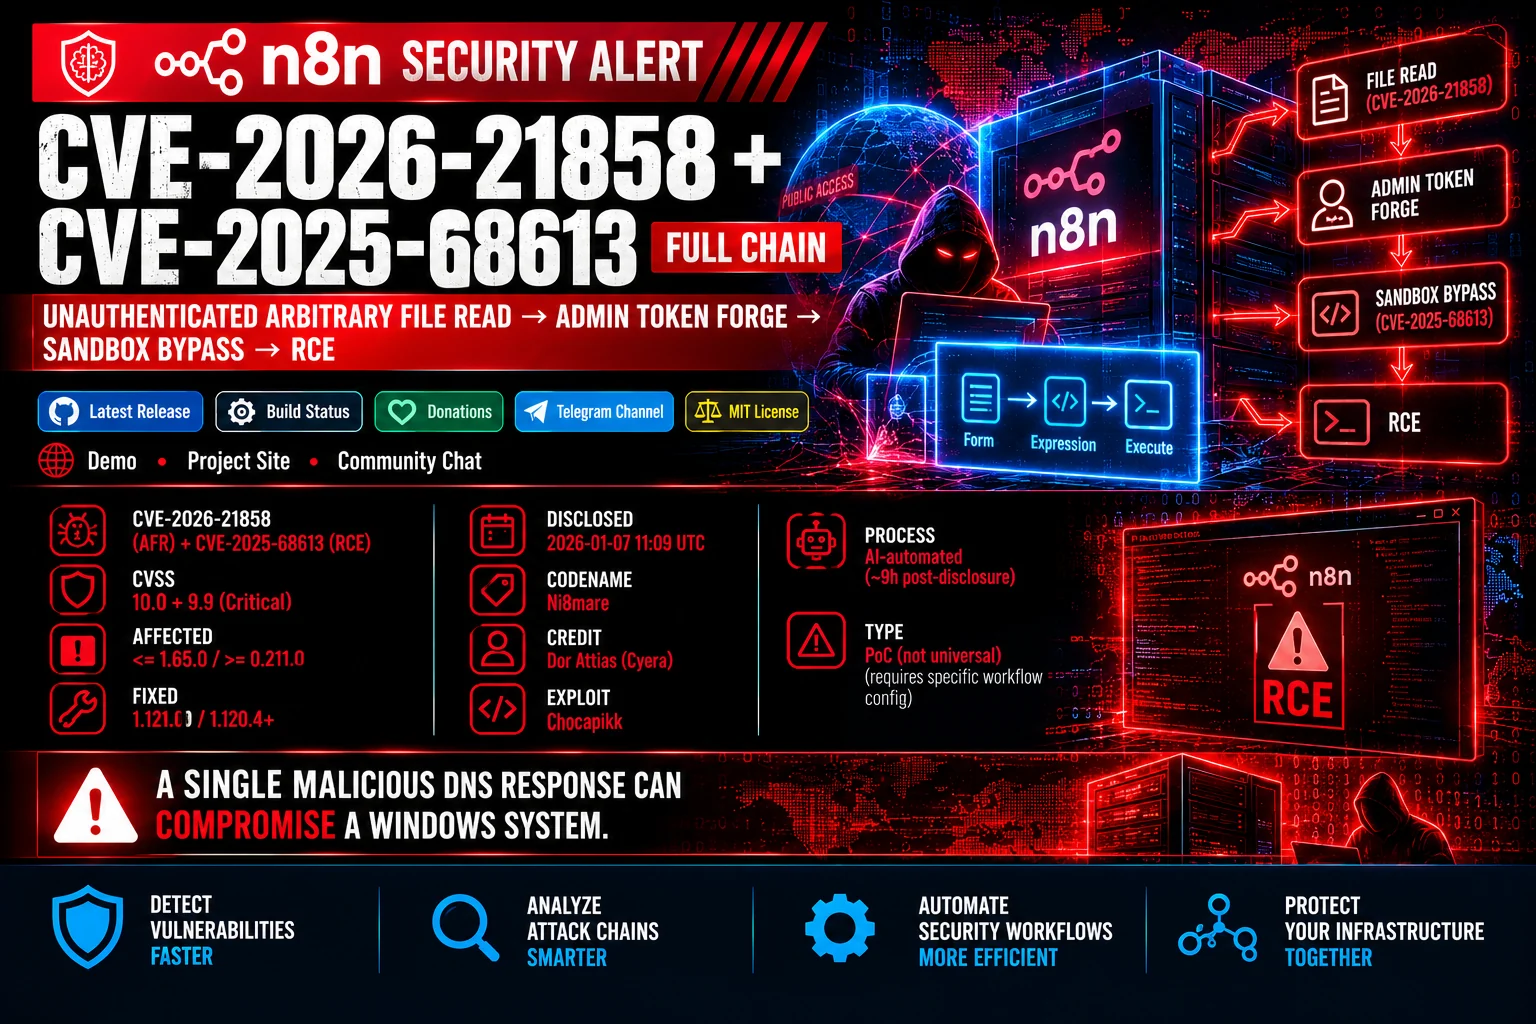 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 artemcyberlab/project-project-chimera-exploiting-a-modern-wordpress-xxe-to-pillage-secrets-
The objective is to conduct a full-scale security assessment of a WordPress-based web application, culminating in a complete server compromise. The…
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 z4nzu/hackingtool
All-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing,…