

honda
 nu11secur1ty/0
Exploit for a Windows Defender race condition that escalates to SYSTEM via use-after-free, crashes MsMpEng.exe, spawns a hidden shell, and persists…
binary-exploitationexploitationpayload-development+3
nu11secur1ty/0Exploit for a Windows Defender race condition that escalates to SYSTEM via use-after-free, crashes MsMpEng.exe, spawns a hidden shell, and persists…

 joelgmsec/autordpwn
The Shadow Attack Framework
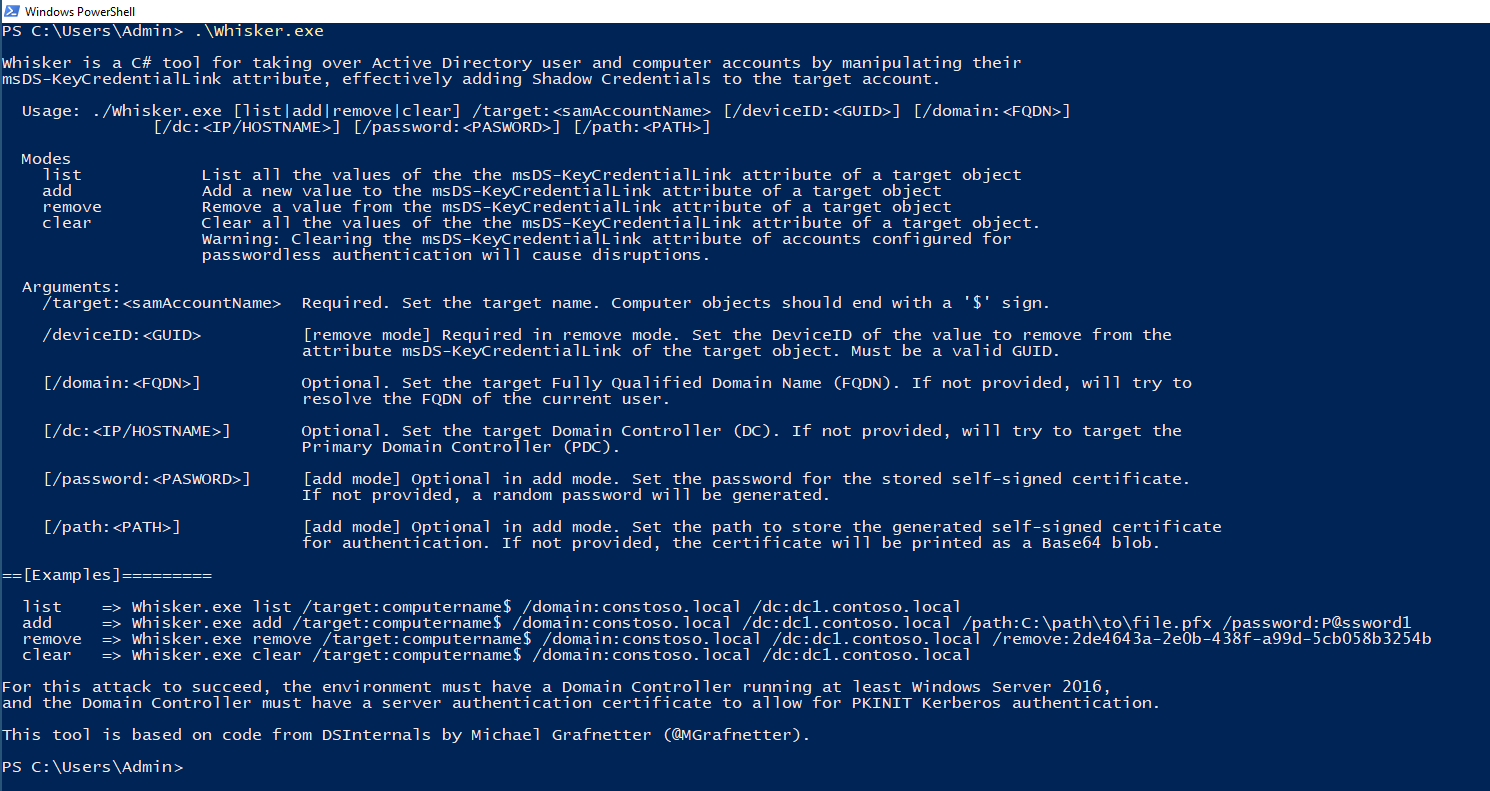 eladshamir/whisker
Whisker is a C# tool for taking over Active Directory user and computer accounts by manipulating their msDS-KeyCredentialLink attribute, effectively…
 ricardojoserf/samdump
Extract the SAM and SYSTEM hives using the Volume Shadow Copy (VSS) API. With exfiltration and XOR obfuscation options. In C#, C++, Crystal, Python,…
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 jenderal92/shadow-vault
Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.
 olivierlaflamme/cve-2021-36934-export-shadow-volume-poc
Proof-of-concept exploit for CVE-2021-36934, exporting Windows Volume Shadow Copy files to enable privilege escalation and hash-based credential…
 p1rat3r00t/why-so-serious-sam
PoC malware that uses exploit CVE-2021-36934 (improper ACLs on shadow copies) using a fileless red team method on Windows 10/11 with LOLBins,…
 ivancabrera02/srhollow
Extracts LSA secrets and DPAPI keys from Windows registry hives via existing or newly created VSS shadow copies, with an inline regf parser and…
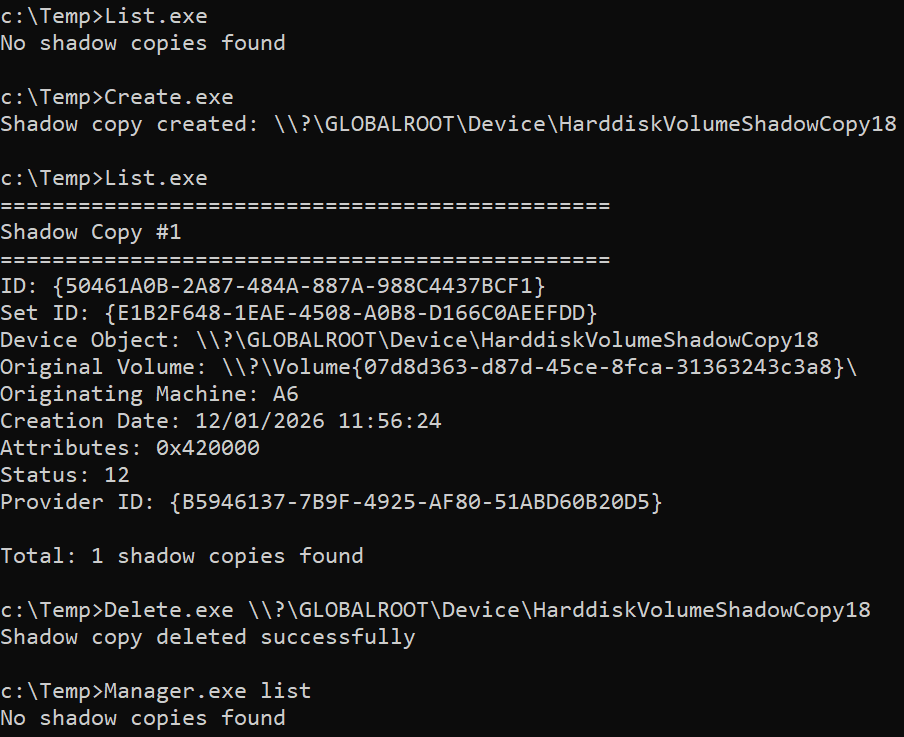 ricardojoserf/w11_shadow_copies
Manage Shadows Copies via the VSS API using C#, C++, Crystal or Python. Working on Windows 11