Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
21 results
PE-Obfuscator preview

PE-Obfuscator

GitHubsaadahla/pe-obfuscator

PE obfuscator with Evasion in mind

adversarial-attackexploitationpayload-development+2
2093 years ago
NimSyscallPacker preview

NimSyscallPacker

GitHubs3cur3th1ssh1t/nimsyscallpacker

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
binary-exploitationexploitationlateral-movement+7
22026 days ago
NyxInvoke preview

NyxInvoke

GitHubblacksnufkin/nyxinvoke

NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support

command-and-controlexploitationids-ips-evasion+6
2431 year ago
amber preview

amber

GitHubegebalci/amber

Reflective PE packer.

binary-exploitationencryption-decryption-toolsexploitation+6
1.4k2 years ago
PowerSploit preview
Archived

PowerSploit

GitHubpowershellmafia/powersploit

PowerSploit - A PowerShell Post-Exploitation Framework
lateral-movementpayload-generationpenetration-testing+5
13.1k6 years ago
the-backdoor-factory preview

the-backdoor-factory

GitHubsecretsquirrel/the-backdoor-factory

Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors

binary-exploitationexploitationmalware-analysis+6
3.4k2 years ago
donut preview

donut

GitHubthewover/donut

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

exploitationids-ips-evasionmemory-forensics+7
4.7k1 year ago
FilelessPELoader preview

FilelessPELoader

GitHubsaadahla/filelesspeloader

Loading Remote AES Encrypted PE in memory , Decrypted it and run it

adversarial-attackids-ips-evasionpayload-development+3
1.0k3 years ago
ExecuteAssembly preview

ExecuteAssembly

GitHubmed0x2e/executeassembly

Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
command-and-controlexploitationids-ips-evasion+8
5995 years ago
PELoader preview

PELoader

GitHubhagrid29/peloader

PE loader with various shellcode injection techniques

binary-analysisexploitationmalware-analysis+4
4603 years ago
BOF_RunPe preview

BOF_RunPe

GitHubntdallas/bof_runpe

BOF to run PE in Cobalt Strike Beacon without console creation
memory-forensicspost-exploitationred-teaming+1
19710 months ago
VectoredOverloading preview

VectoredOverloading

GitHubcheckpointsw/vectoredoverloading

Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…

binary-exploitationexploitationmalware-analysis+6
12610 months ago
ReflectivePluginLoader preview

ReflectivePluginLoader

GitHubracoten/reflectivepluginloader

A minimal PE mapper that loads DLLs straight from memory and calls into a clean plugin interface, no LoadLibrary needed.
binary-exploitationdefensive-toolseducation+7
4722 days ago
GhostlyHollowingViaTamperedSyscalls2 preview

GhostlyHollowingViaTamperedSyscalls2

GitHubmaldev-academy/ghostlyhollowingviatamperedsyscalls2

Implementing Ghostly-Hollowing using tampered syscalls for remote PE injection
educationids-ips-evasionpayload-development+2
769 months ago
zig-pe preview

zig-pe

GitHubthoxy67/zig-pe

Reflective PE loader written in Zig. Loads and executes native and .NET PE files directly from memory.
binary-exploitationexploitationpayload-development+3
657 months ago
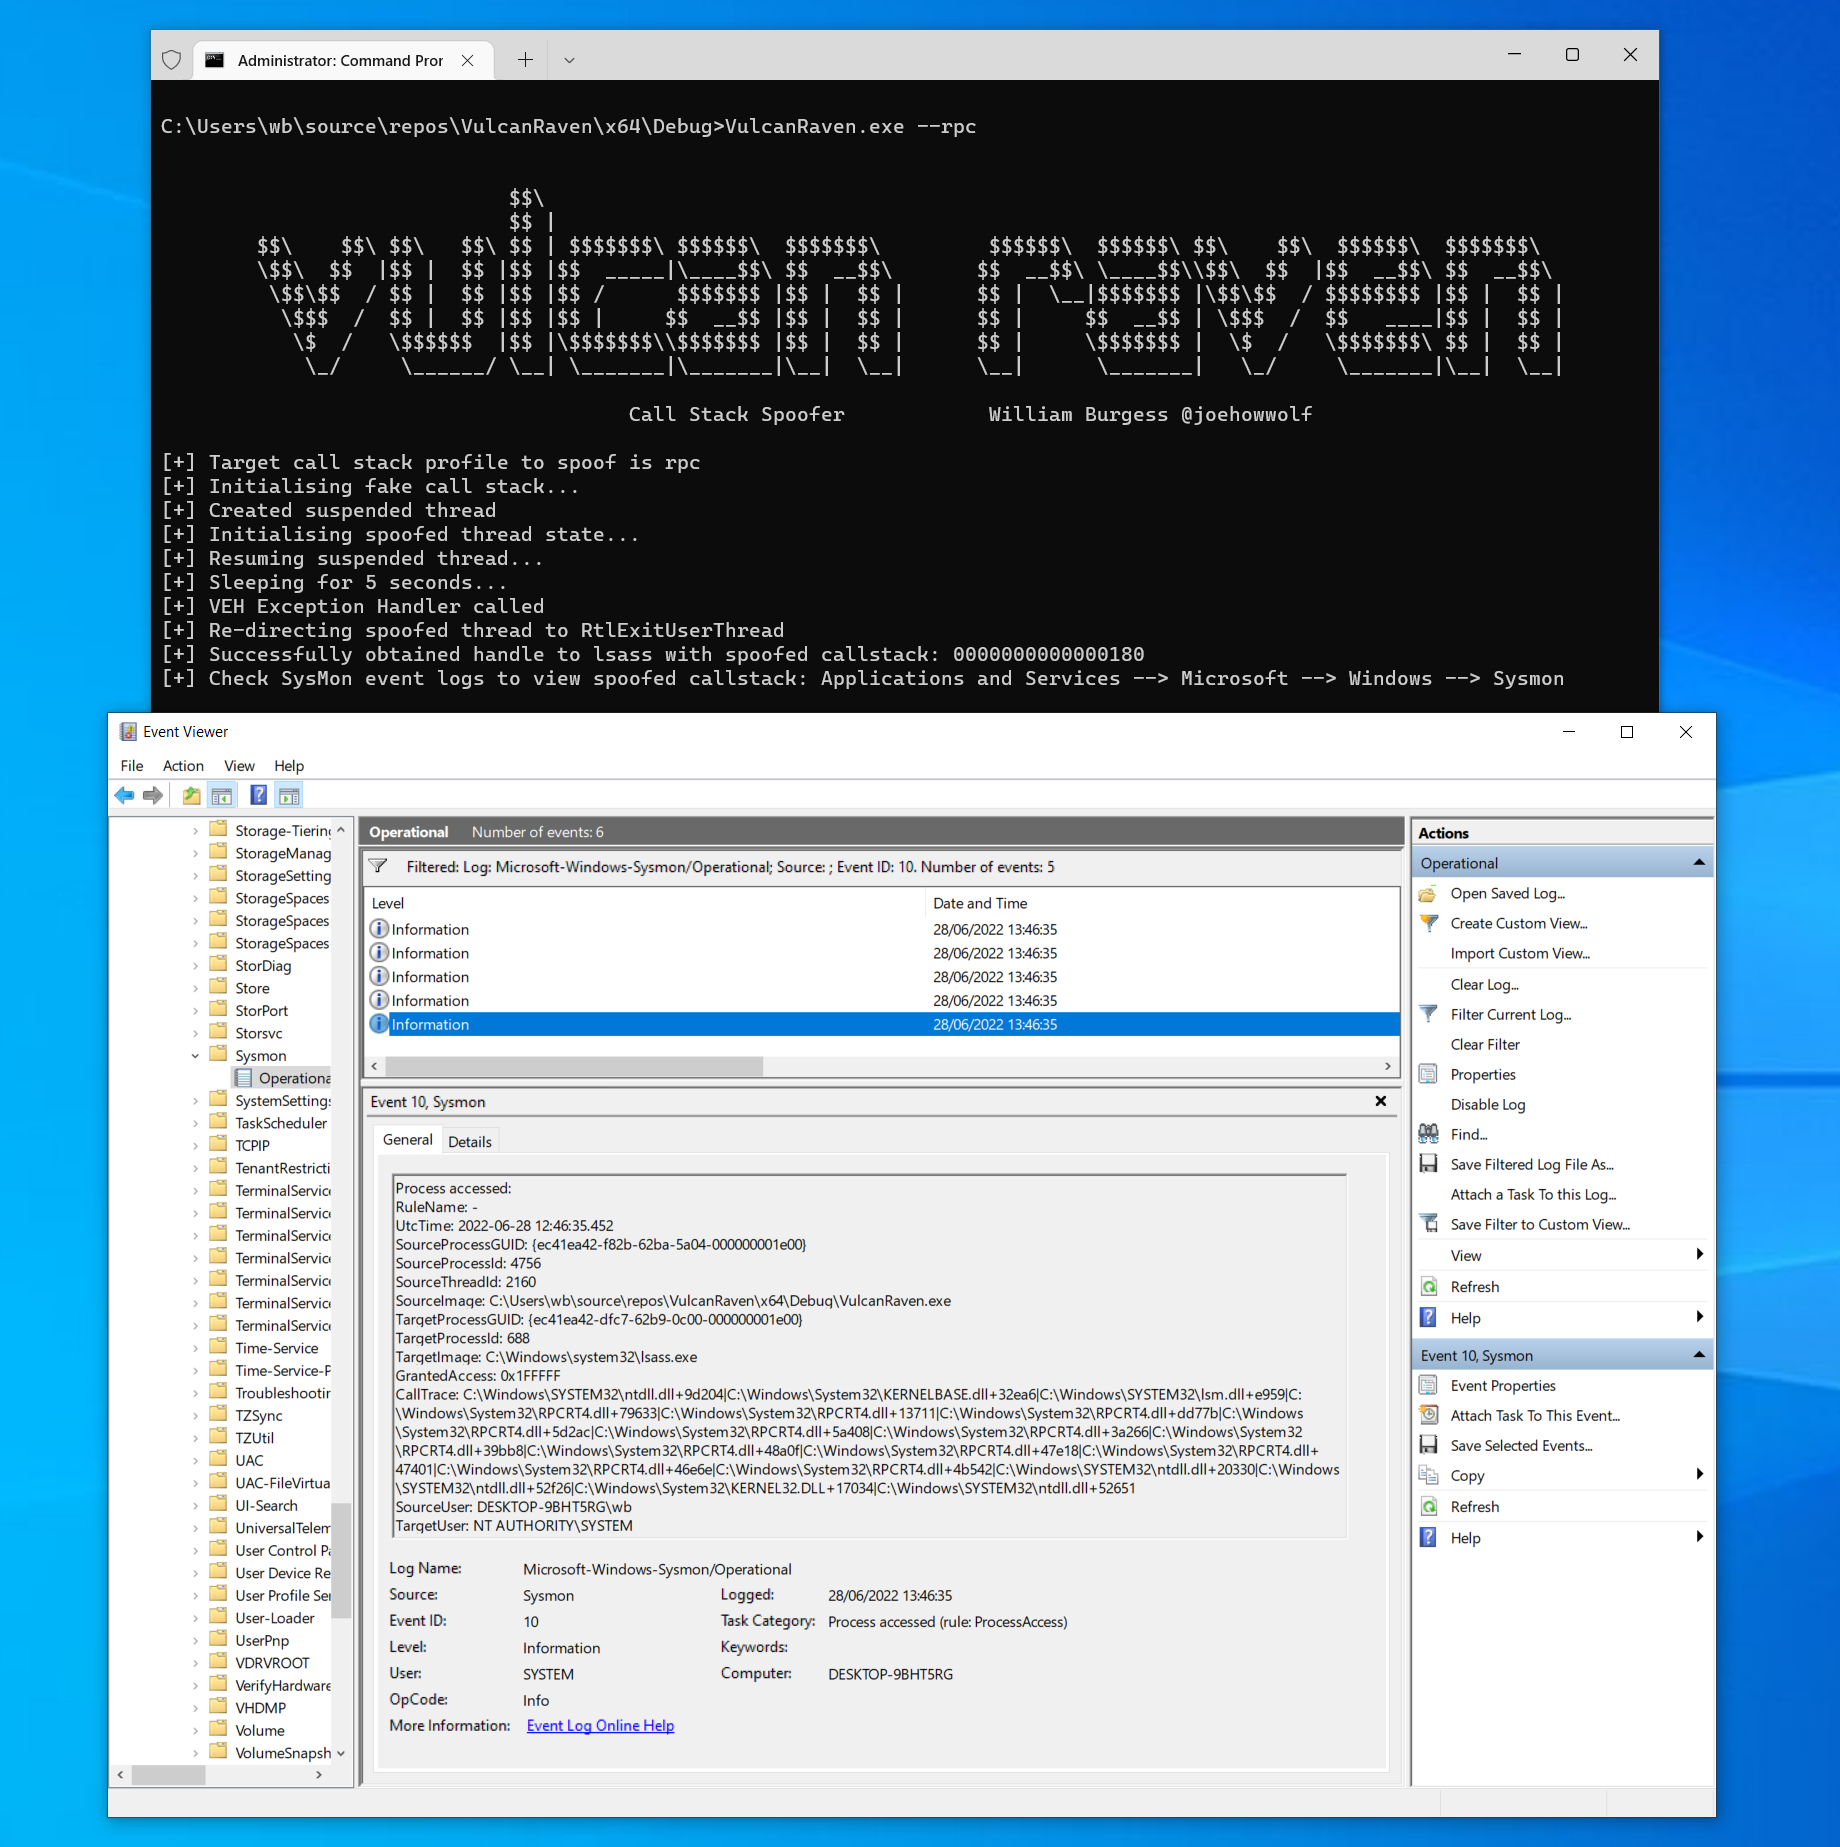
CallStackSpoofer preview

CallStackSpoofer

GitHubwithsecurelabs/callstackspoofer

A PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)
adversarial-attackids-ips-evasionpost-exploitation+1
5981 year ago
DInvoke_rs preview

DInvoke_rs

GitHubkudaes/dinvoke_rs

Dynamically invoke arbitrary unmanaged code
binary-analysisids-ips-evasionpayload-development+3
3673 months ago
BokuLoader preview

BokuLoader

GitHubxforcered/bokuloader

A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!

adversarial-attackcommand-and-controlids-ips-evasion+4
3322 years ago
Previous12Next