
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
80 results
donut preview

donut

GitHubthewover/donut

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

exploitationids-ips-evasionmemory-forensics+7
4.7k
1 year ago
r77-rootkit preview

r77-rootkit

GitHubbytecode77/r77-rootkit

Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
command-and-controldefensive-toolsids-ips-evasion+6
2.2k2 months ago
DonPAPI preview

DonPAPI

GitHublogin-securite/donpapi

Automated remote credential dumper for Windows environments, extracting DPAPI secrets, browser credentials, certificates, and configuration files…
authenticationinformation-gatheringpassword-cracking+3
1.4k12 days ago
COFFLoader preview

COFFLoader

GitHubtrustedsec/coffloader

Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
binary-analysispayload-developmentpenetration-testing+2
65511 days ago
CS-Remote-OPs-BOF preview

CS-Remote-OPs-BOF

GitHubtrustedsec/cs-remote-ops-bof

Remote operations commands implemented using Beacon Object Files
authenticationencryption-decryption-toolslateral-movement+6
1.2k2 months ago
NativeDump preview

NativeDump

GitHubricardojoserf/nativedump

Dump lsass using only NTAPI functions by hand-crafting Minidump files (without MiniDumpWriteDump!!!)
memory-forensicspost-exploitationred-teaming
7501 month ago
Nemesis preview

Nemesis

GitHubspecterops/nemesis

Centralized data enrichment platform for offensive security assessments that ingests, enriches, and enables collaborative analysis of collected files…
information-gatheringosintpenetration-testing+3
9971 month ago
scavenger preview

scavenger

GitHubspiderlabs/scavenger

scavenger : is a multi-threaded post-exploitation scanning tool for scavenging systems, finding most frequently used files and folders as well as…
data-exfiltrationinformation-gatheringpenetration-testing+2
3427 years ago
MemFiles preview

MemFiles

GitHuboctoberfest7/memfiles

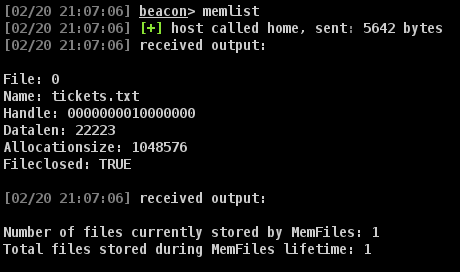
A CobaltStrike toolkit to write files produced by Beacon to memory instead of disk
command-and-controldata-exfiltrationpost-exploitation+1
4752 years ago
Volumiser preview

Volumiser

GitHubccob/volumiser

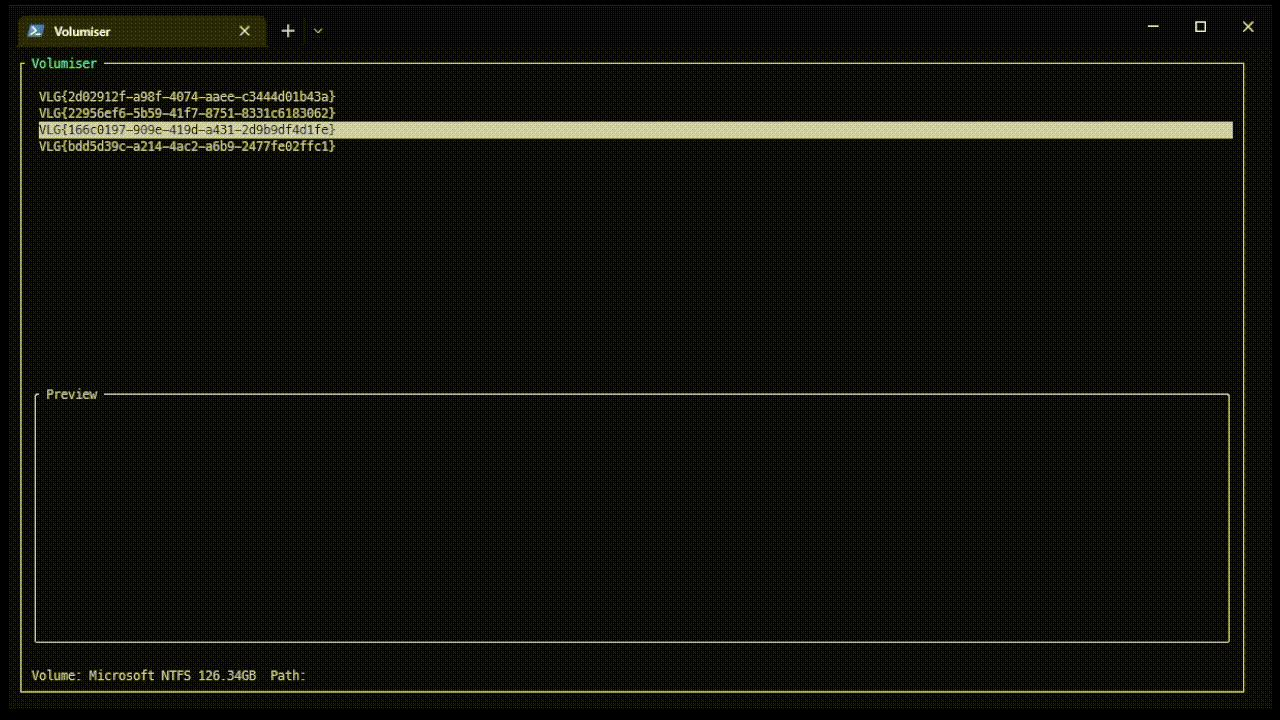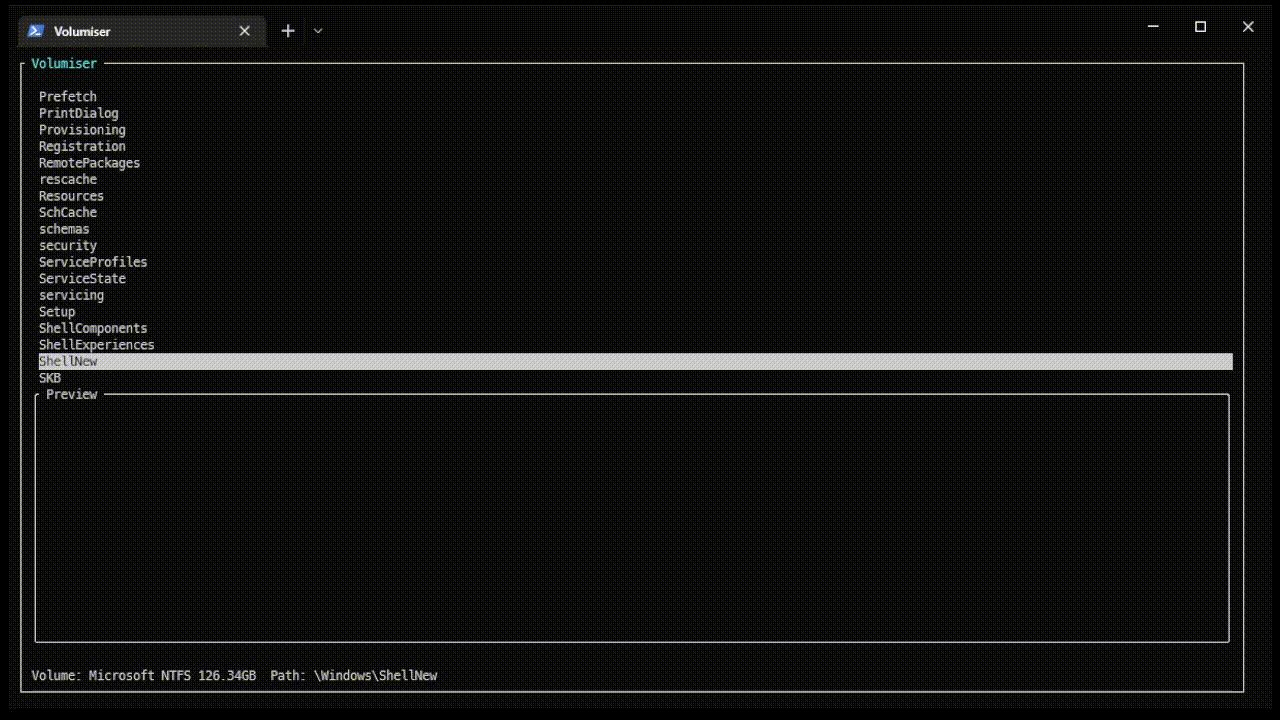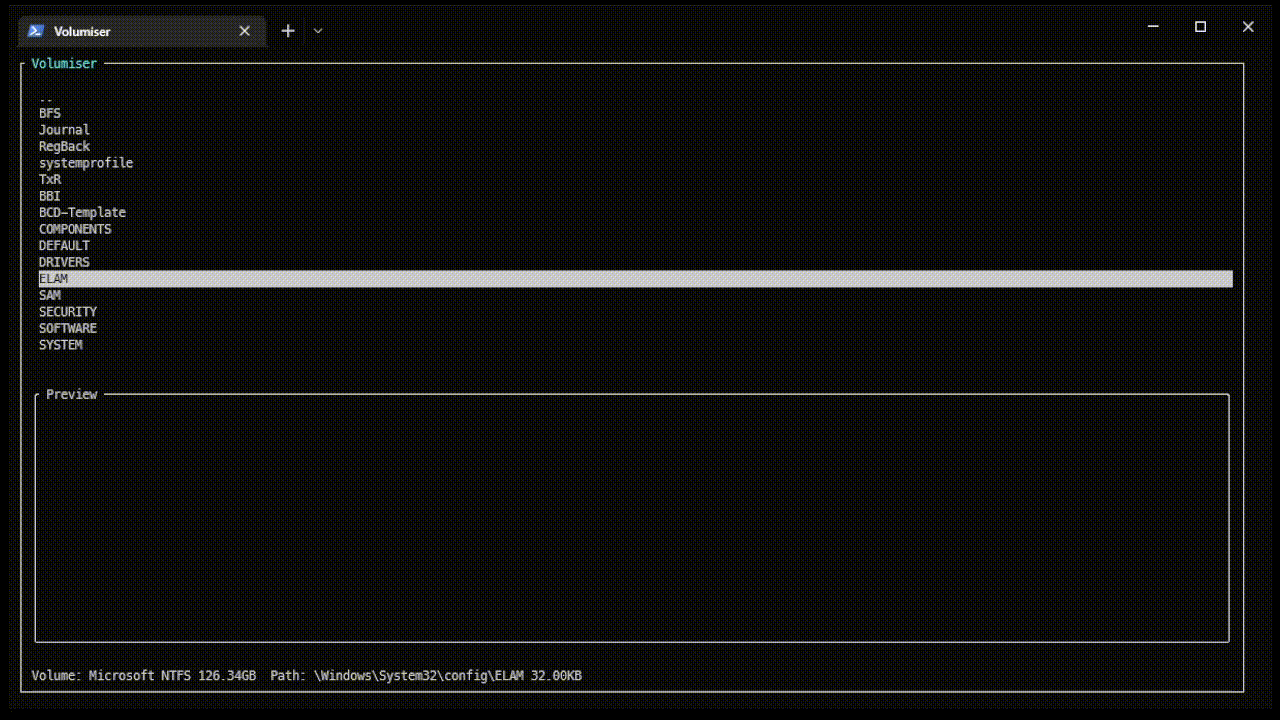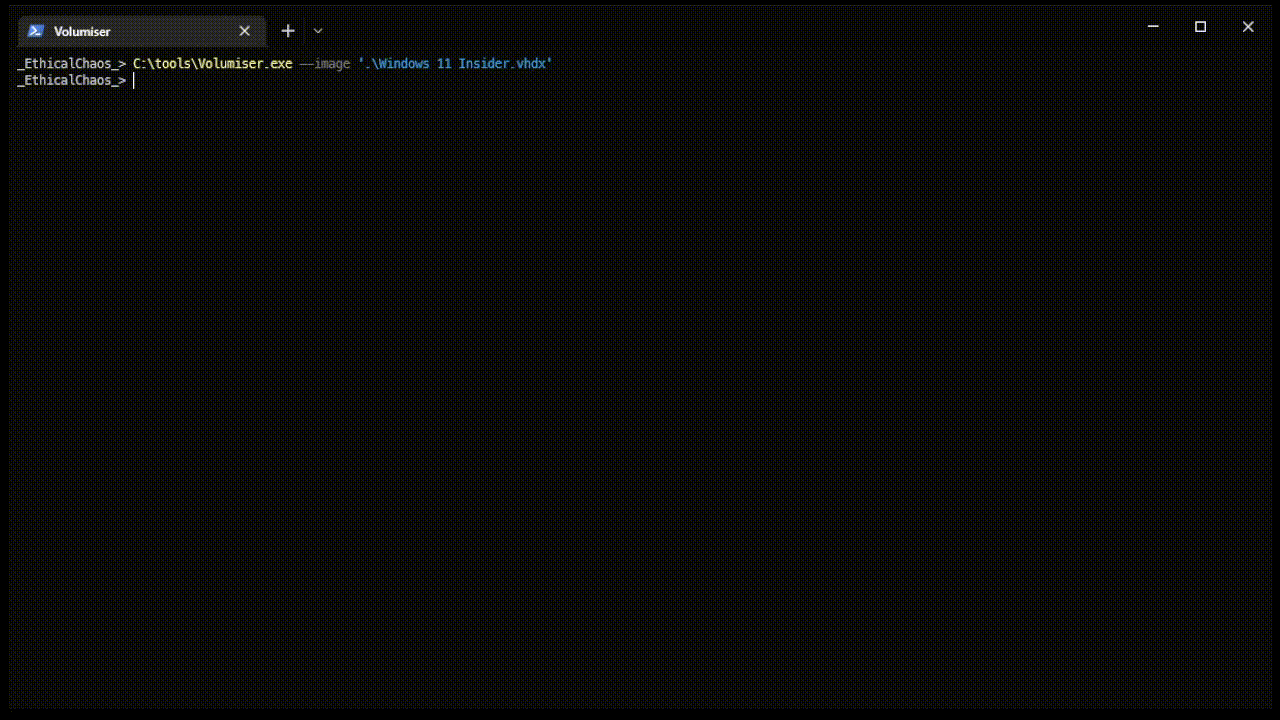
CLI and interactive console for listing, browsing, and extracting files from VM disk images (VHDX, VMDK, EBS snapshots, raw disks) for red-team…

command-and-controldata-exfiltrationdigital-forensics+3
4361 year ago
PPLBlade preview

PPLBlade

GitHubtastypepperoni/pplblade

Bypasses PPL protection to dump LSASS process memory, obfuscates dump files with XOR, and exfiltrates them remotely via RAW or SMB without writing to…
data-exfiltrationexploitationmemory-forensics+2
6013 years ago
EDRaser preview

EDRaser

GitHubsafebreach-labs/edraser

Remotely delete access logs, Windows event logs, databases, and files on target machines using automated scanning or manual attack selection for…

database-securitypost-exploitation
3742 years ago
NimSyscallPacker preview

NimSyscallPacker

GitHubs3cur3th1ssh1t/nimsyscallpacker

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

binary-exploitationexploitationlateral-movement+7
21710 days ago
eviltree preview

eviltree

GitHubt3l3machus/eviltree

A python3 remake of the classic "tree" command with the additional feature of searching for user provided keywords/regex in files, highlighting those…
information-gatheringpost-exploitationprivilege-escalation+3
4131 year ago
evilrdp preview

evilrdp

GitHubskelsec/evilrdp

RDP client with extended control for automated mouse, keyboard, and clipboard manipulation, file transfer, SOCKS proxy, and remote command execution…
command-and-controllateral-movementpenetration-testing+3
3091 year ago
UnderlayCopy preview

UnderlayCopy

GitHubkfallahi/underlaycopy

PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads
data-recoverydigital-forensicsdisk-forensics+3
25610 months ago
ExecIT preview

ExecIT

GitHubflorylsk/execit

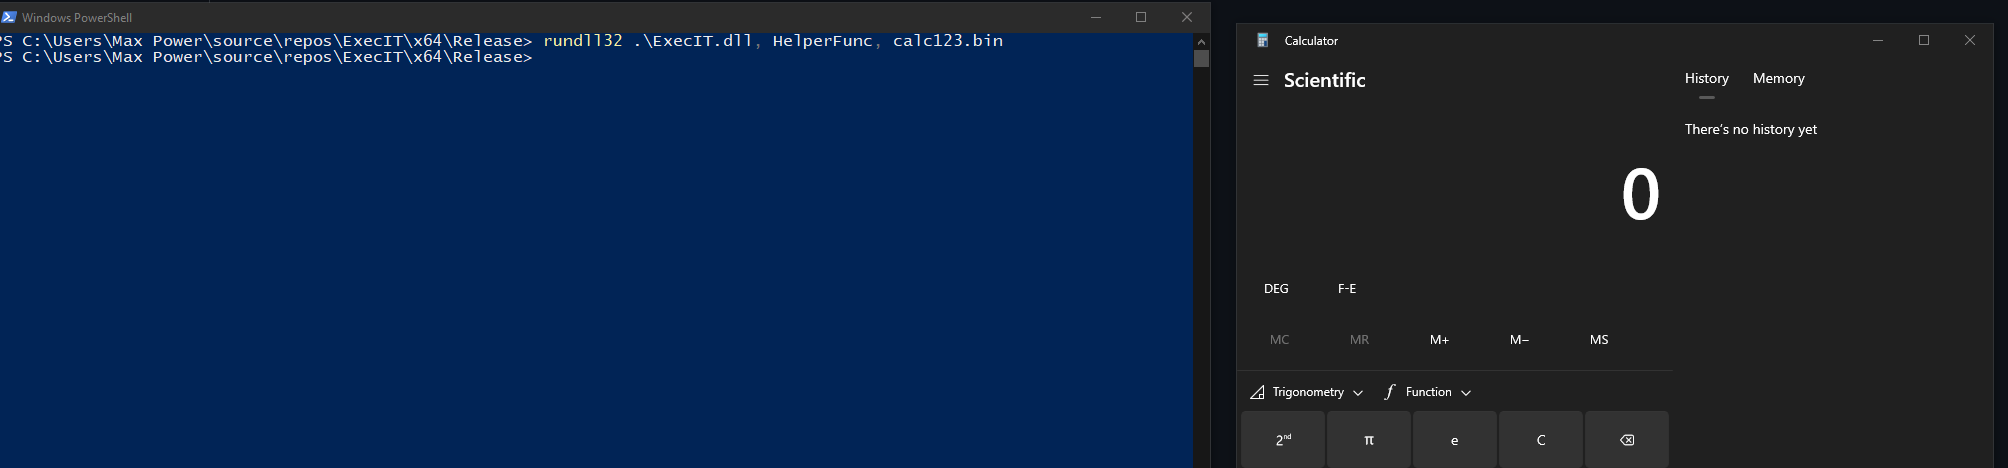
Execute shellcode files with rundll32
ids-ips-evasionmalware-analysispayload-development+4
2272 years ago
PixelCode-Attack preview

PixelCode-Attack

GitHubs3n4t0r-0x0/pixelcode-attack

Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…

command-and-controldata-exfiltrationeducation+8
1747 months ago
Previous12345Next