
pict
 thomasareed/pict
Modular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
digital-forensicsforensicsincident-response+2
95
thomasareed/pictModular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
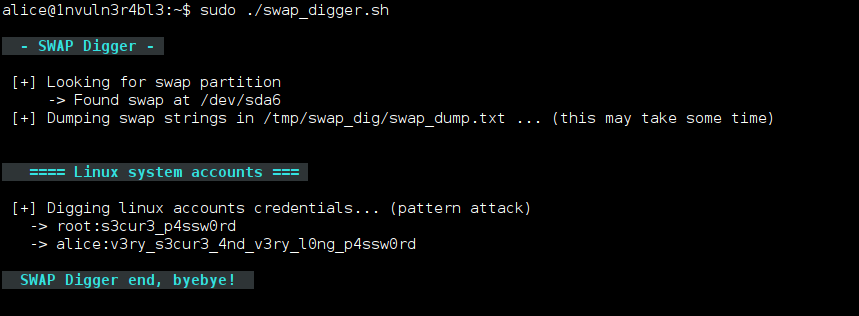 sevagas/swap_digger
Automates Linux swap analysis to extract user credentials, web form data, WiFi keys, and HTTP authentication during post-exploitation or forensic…