
SharpStay
 0xthirteen/sharpstay
.NET tool for installing Windows persistence via registry keys, scheduled tasks, services, WMI events, COM hijacks, and LNK backdoors, supporting…
penetration-testingpersistence-mechanismspost-exploitation+1
499
0xthirteen/sharpstay.NET tool for installing Windows persistence via registry keys, scheduled tasks, services, WMI events, COM hijacks, and LNK backdoors, supporting…
 0xthirteen/sharpmove
.NET Project for performing Authenticated Remote Execution
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 saadahla/docplz
Documents Exfiltration project for fun and educational purposes
 starseed12345/queststack
Unlock the Meta Quest 1 bootloader and gain root access using GhostLock + CVE-2021-1931.
 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
 threatexpress/malleable-c2
Cobalt Strike Malleable C2 Design and Reference Guide
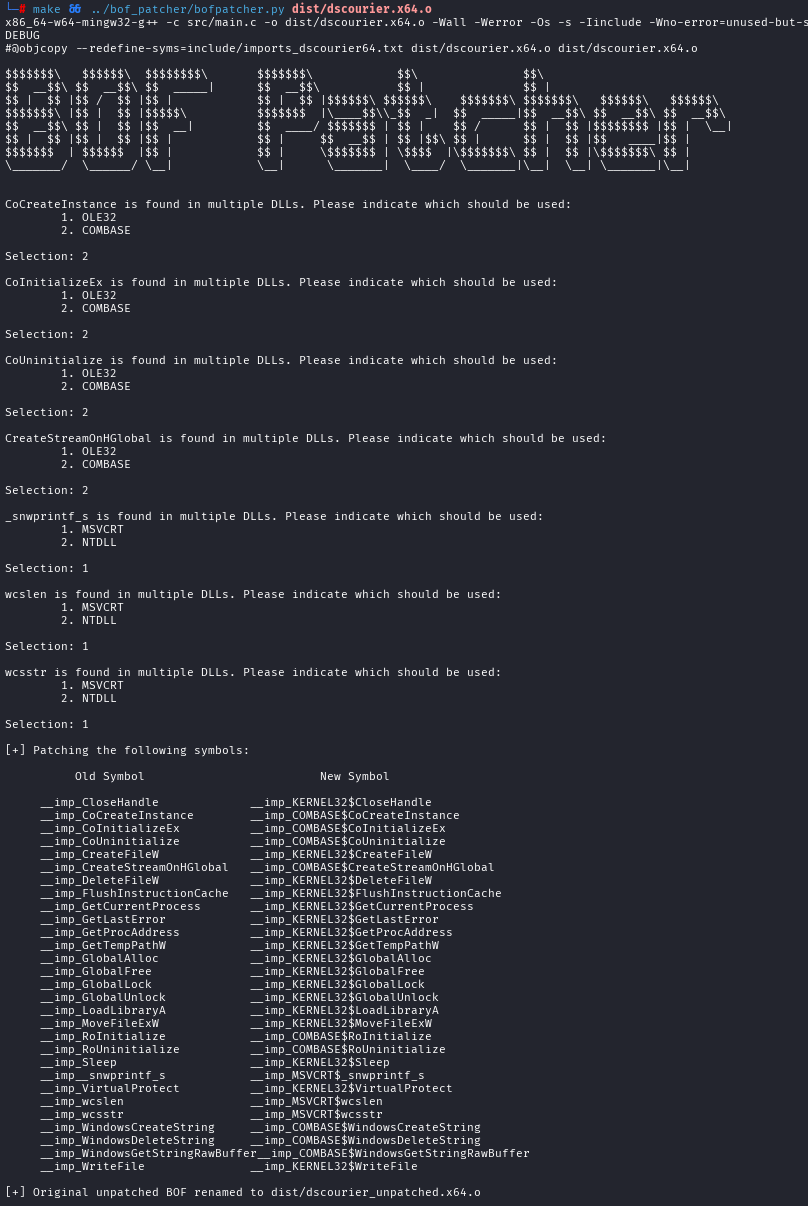 octoberfest7/dscourier_bof
BOF POC of the DSCourier project / invoking WinGet via COM
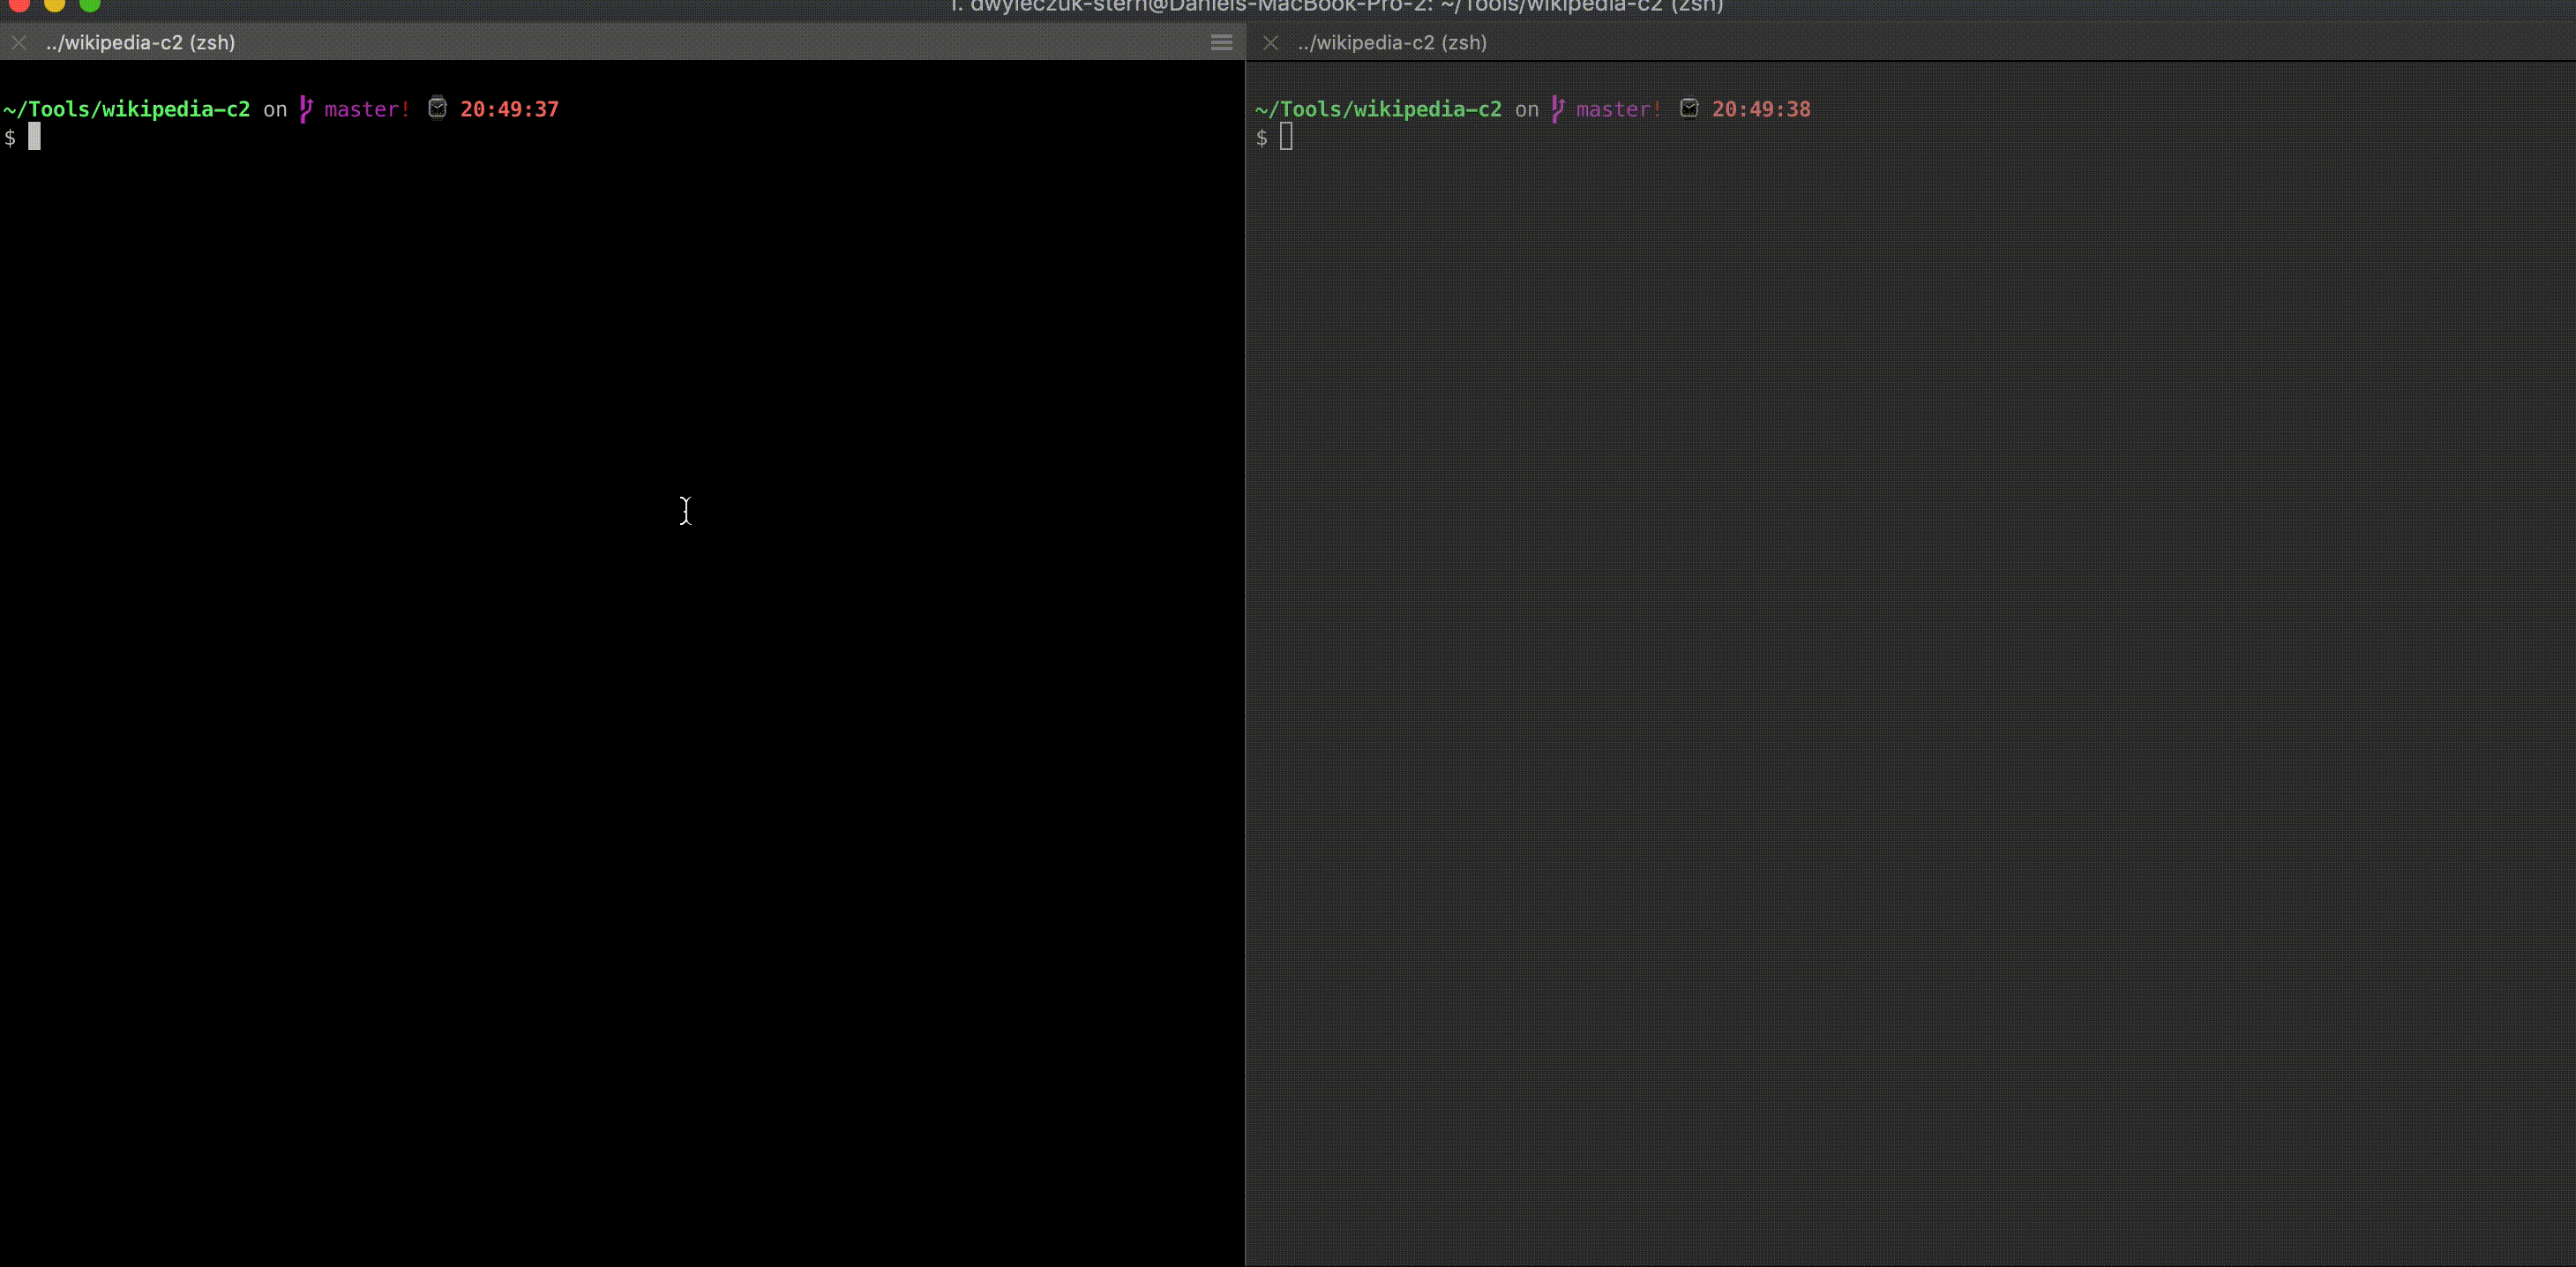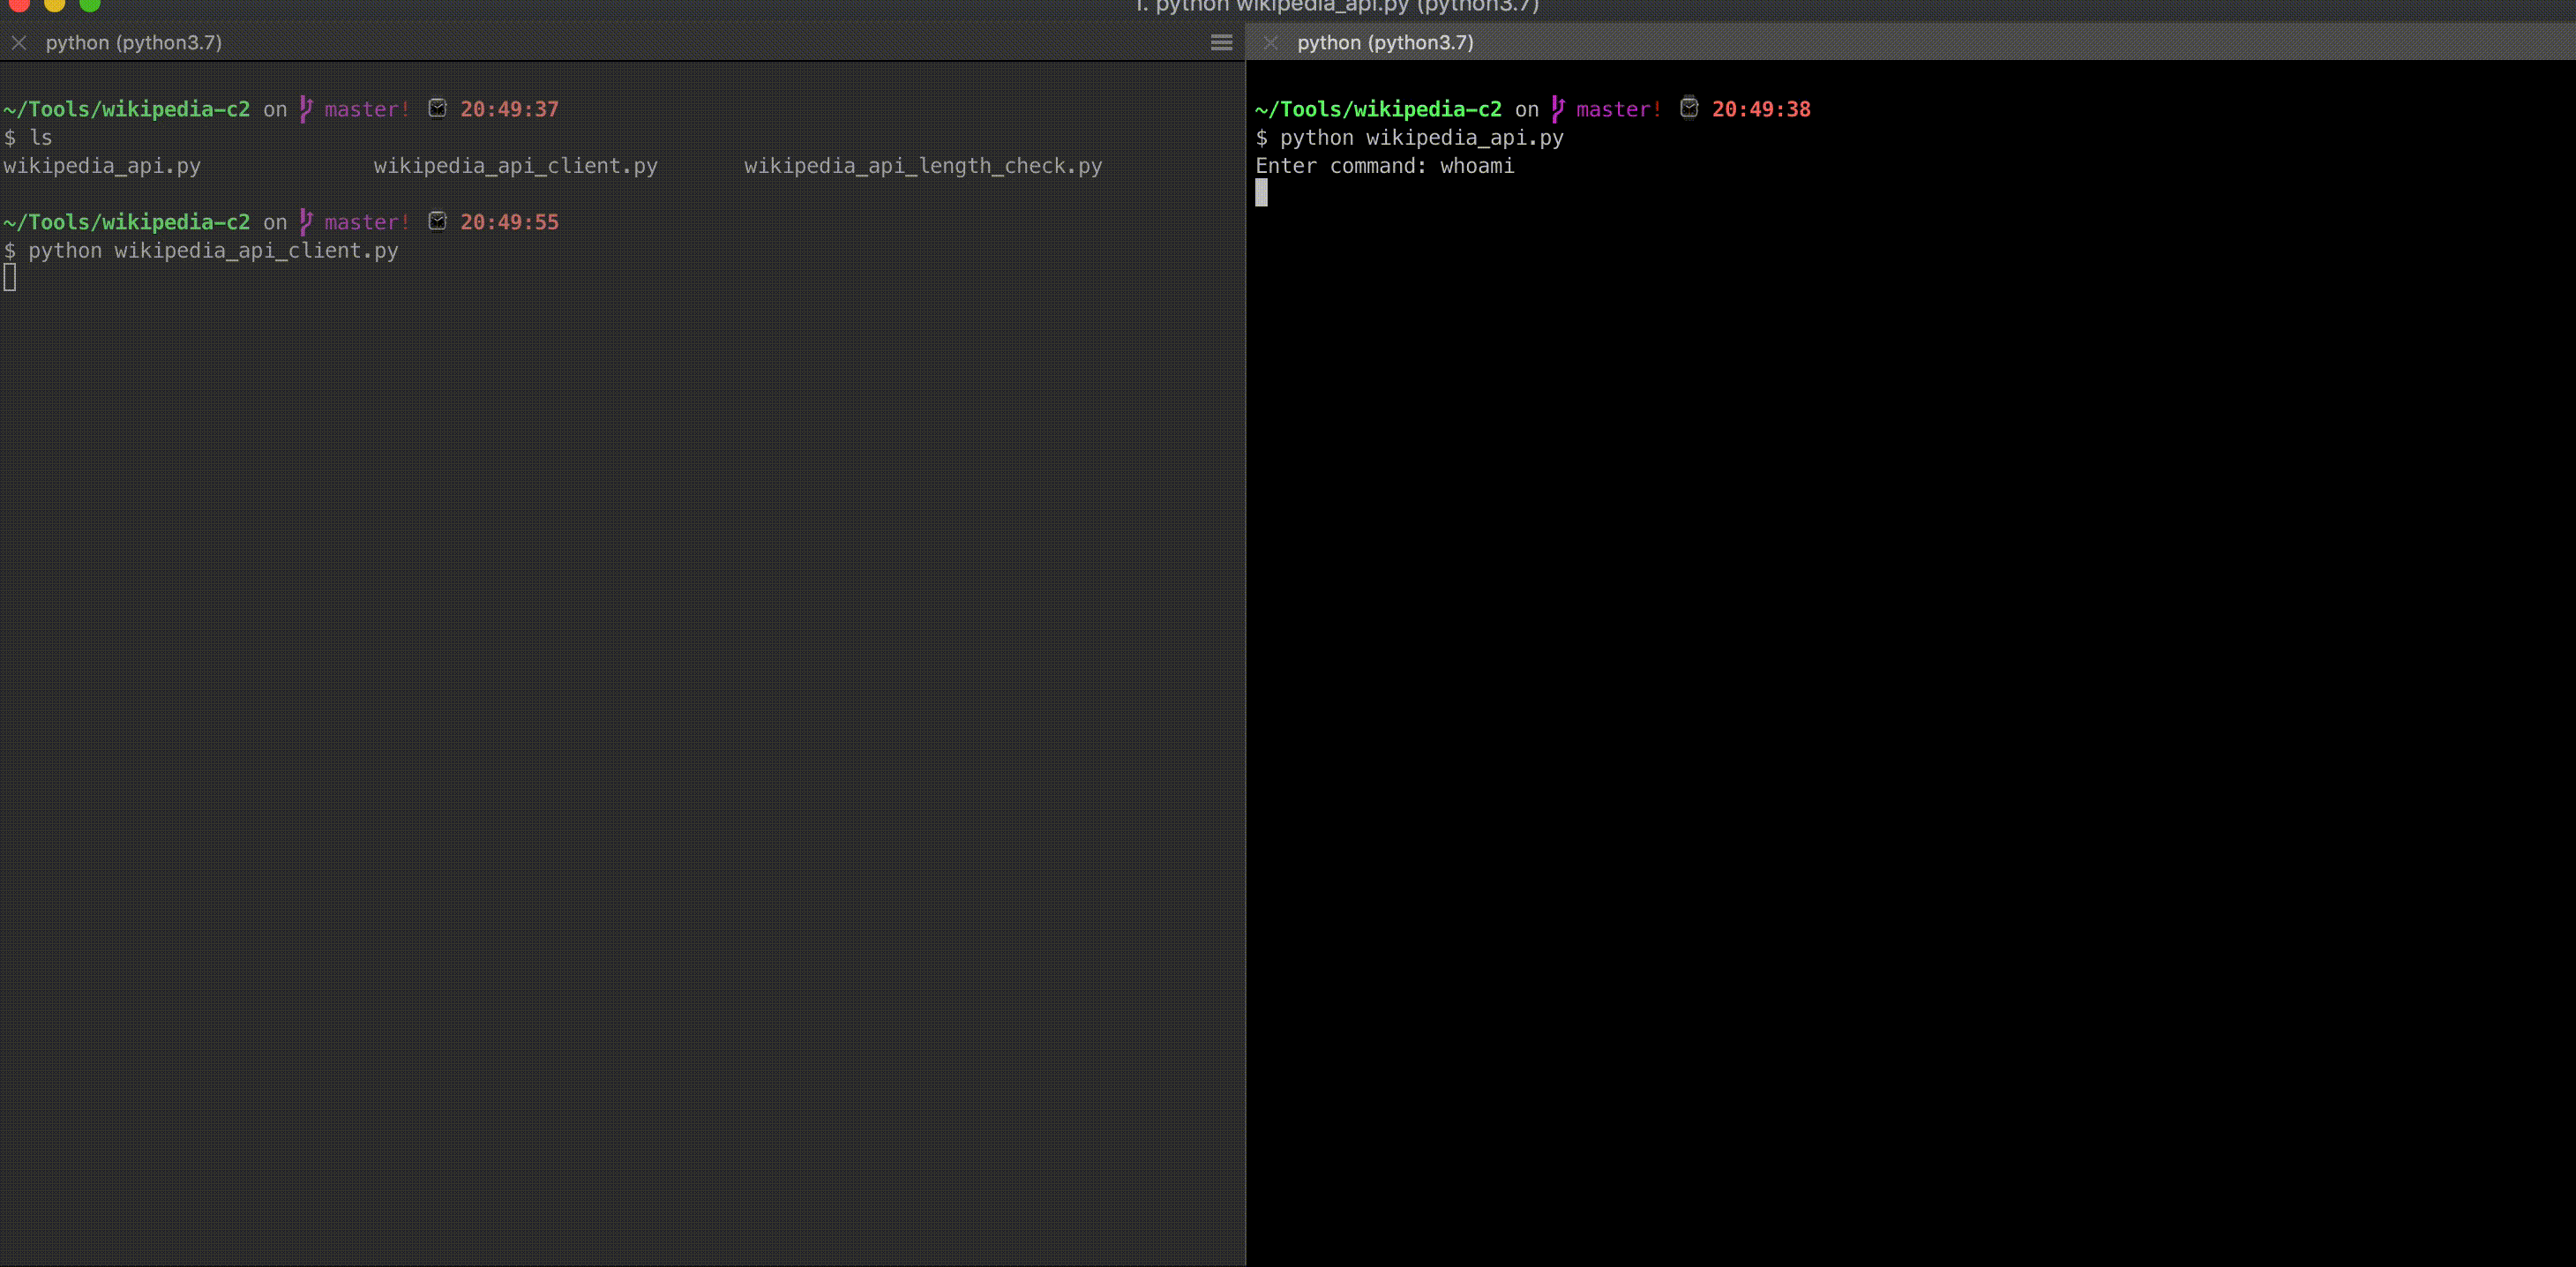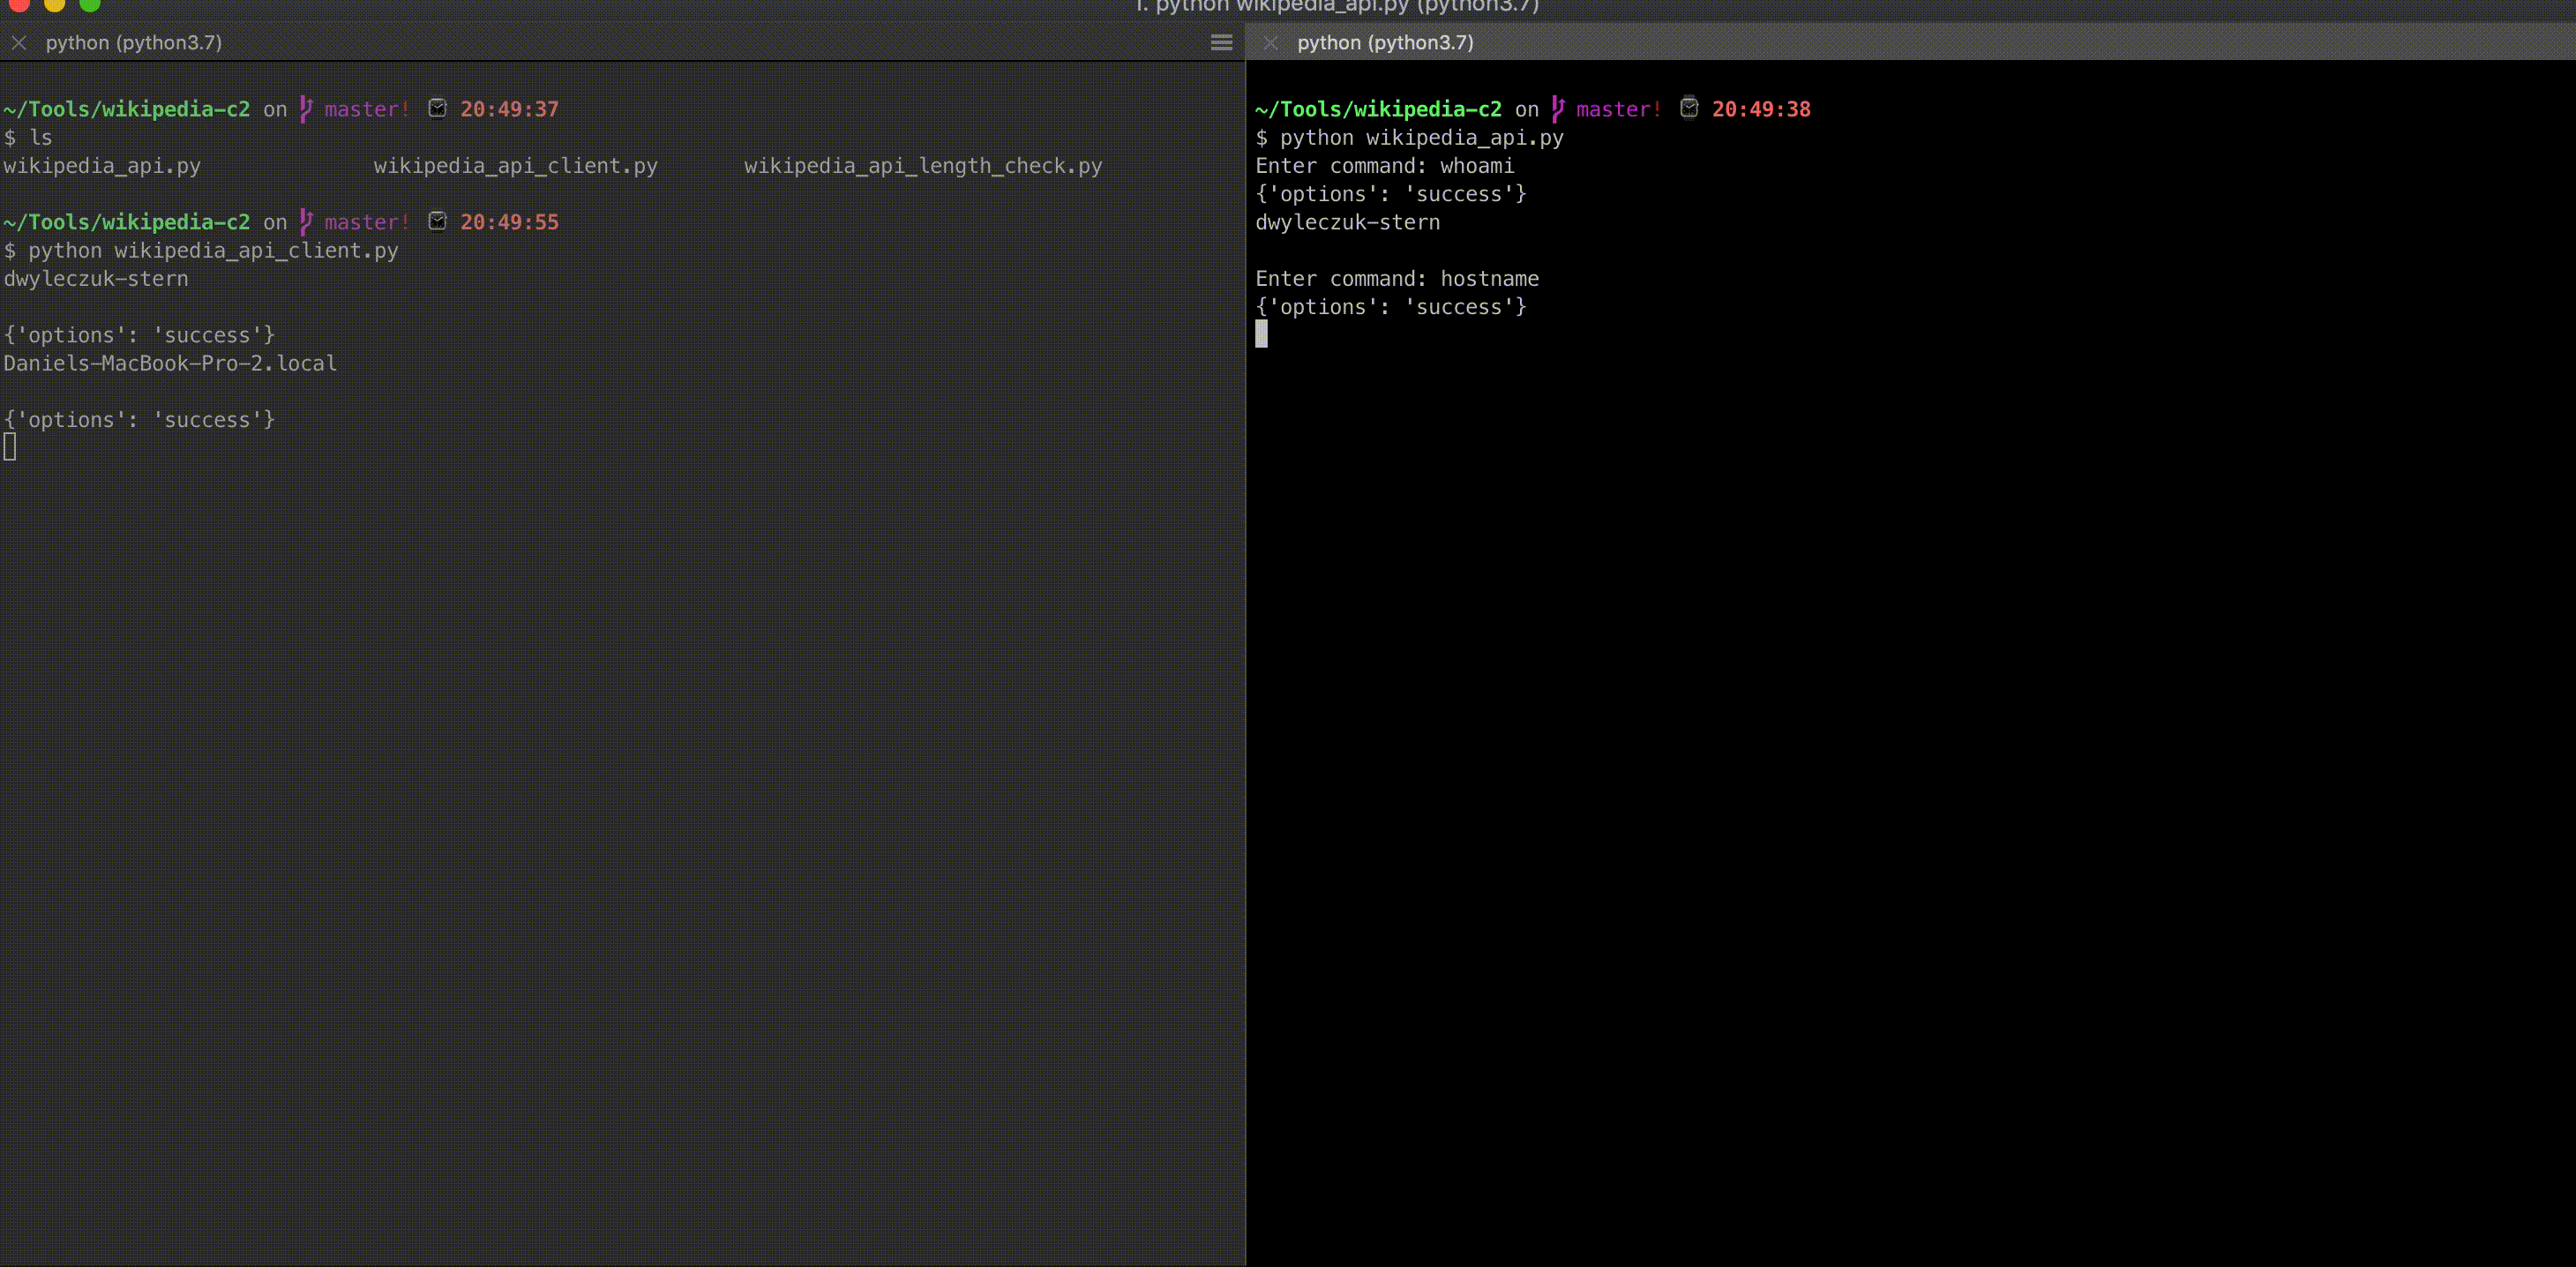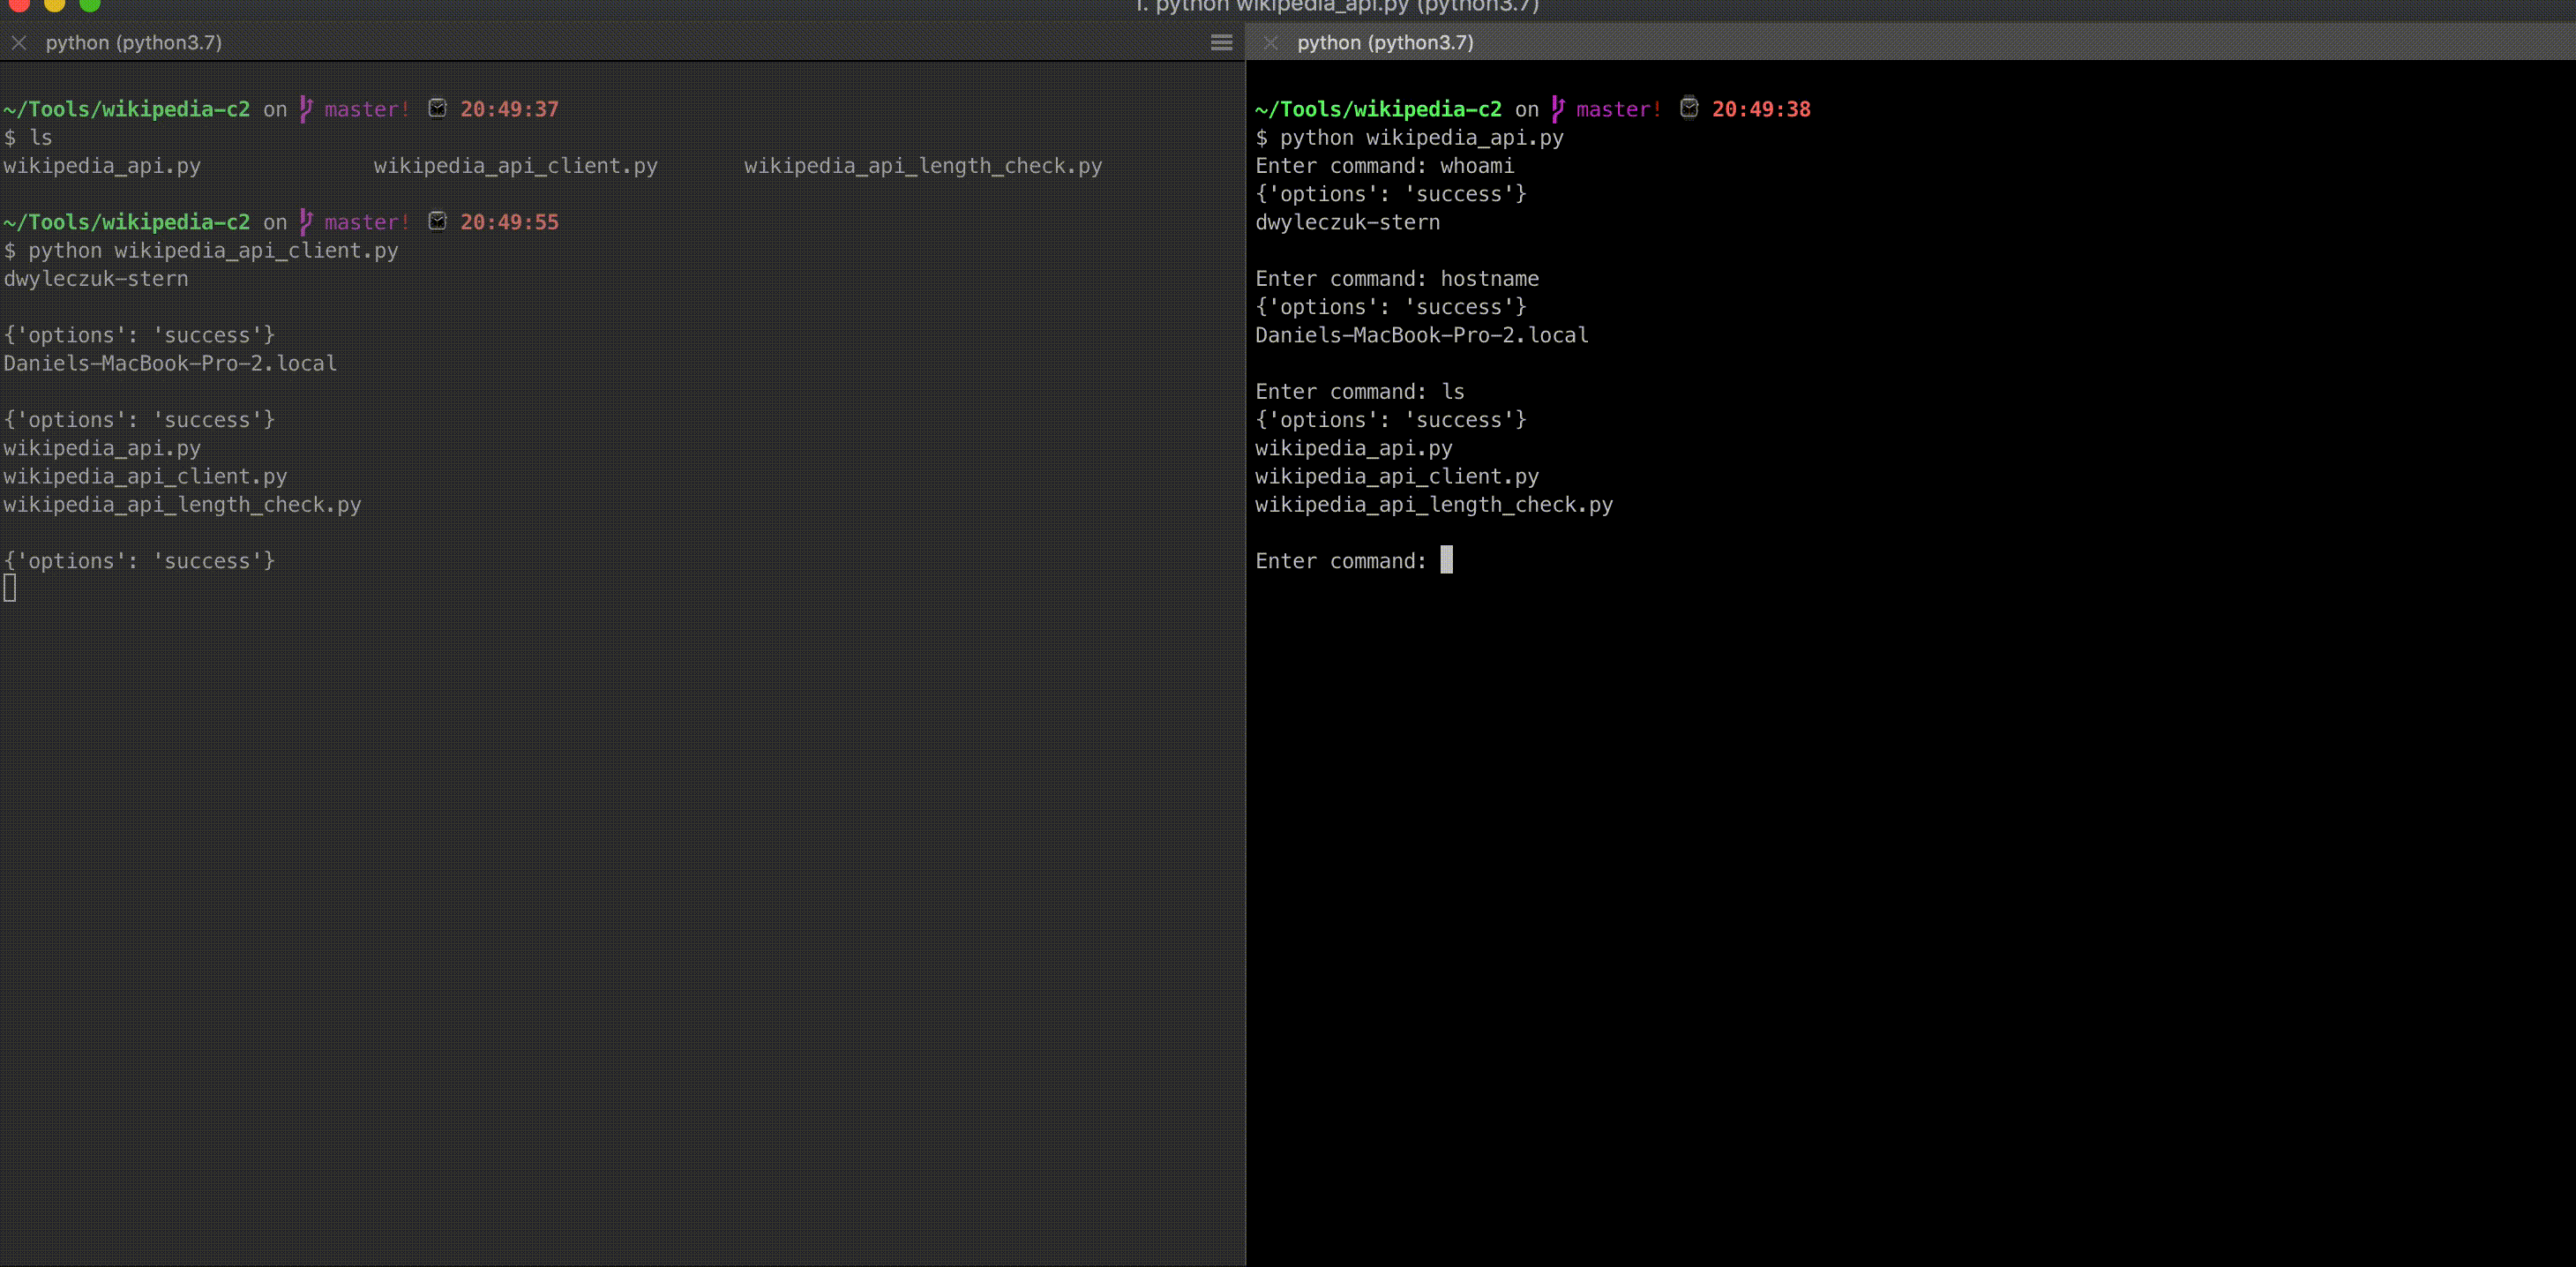 daniel-infosec/wikipedia-c2
POC for utilizing wikipedia API for Command and Control
 admin2099/penetration-testing-assessment-23-04-2026
Penetration testing assessment of a vulnerable IIS 6.0 WebDAV server, demonstrating reconnaissance, enumeration, exploitation (CVE-2017-7269), and…
 samugit83/redamon
An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
 paulsec/twittor
A fully featured backdoor that uses Twitter as a C&C server
 maldevel/gdog
A fully featured Windows backdoor that uses Gmail as a C&C server
 ilikenwf/darkagent
DarkAgent Remote Administration Tool RAT by DragonHunter
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 erarnitox/malvexc2
A simple C2 Framework written in modern C++
 byt3bl33d3r/gcat
A PoC backdoor that uses Gmail as a C&C server
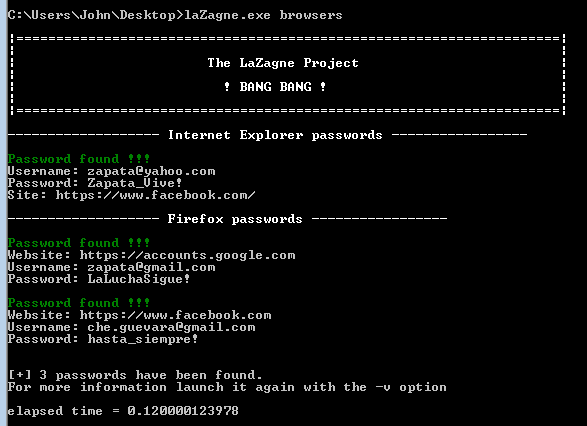 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…