
Priv2Admin
 gtworek/priv2admin
Exploitation paths allowing you to (mis)use the Windows Privileges to elevate your rights within the OS.
exploitationpenetration-testingpost-exploitation+1
2.5k
gtworek/priv2adminExploitation paths allowing you to (mis)use the Windows Privileges to elevate your rights within the OS.
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
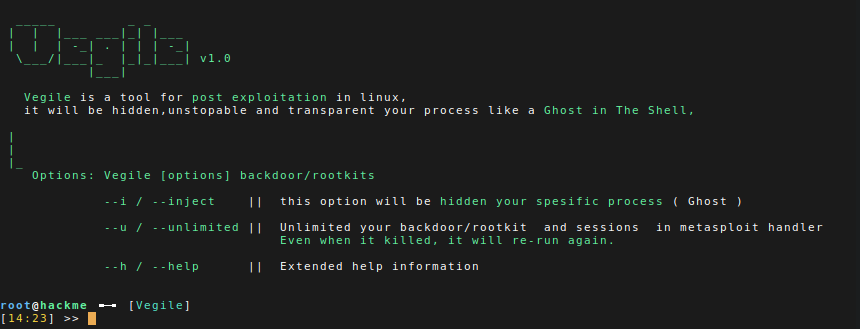 screetsec/vegile
This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…
 mufeedvh/moonwalk
Cover your tracks during Linux Exploitation by leaving zero traces on system logs and filesystem timestamps.
 gellin/teamviewer_permissions_hook_v1
A proof of concept injectable C++ dll, that uses naked inline hooking and direct memory modification to change your TeamViewer permissions.
 justicerage/freedomfighting
A collection of scripts which may come in handy during your freedom fighting activities.
 tuhinshubhra/shellstack
A PHP Based Tool That Helps You To Manage All Your Backdoored Websites Efficiently.
 gmh5225/callmewin32kdriver
Load your driver like win32k.sys
 hazcod/ransomwhere
A PoC ransomware sample to test out your ransomware response strategy.
 xaitax/totalrecall
This tool extracts and displays data from the Recall feature in Windows 11, providing an easy way to access information about your PC's activity…
 smokeme/airstrike
Customizable Stage0 C2 framework with C and Rust agent templates, a Flask backend, and a React dashboard for building and operating your own C2…
 warpedatom/noisehound
Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
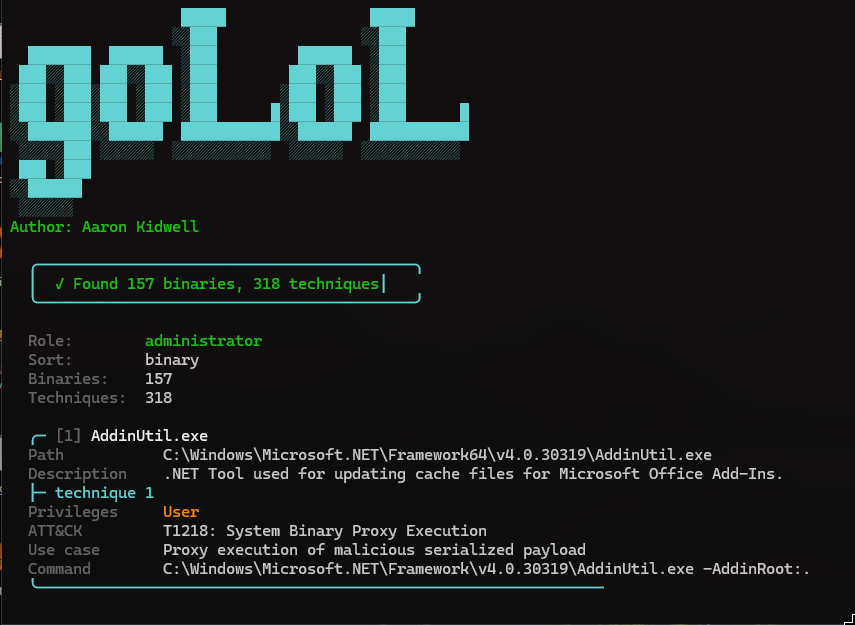 aaron-kidwell/golol
goLoL is a Windows host scanner with dual support for LOLBAS binaries and LOLDrivers. It lists LOLBAS techniques runnable at your current privilege…
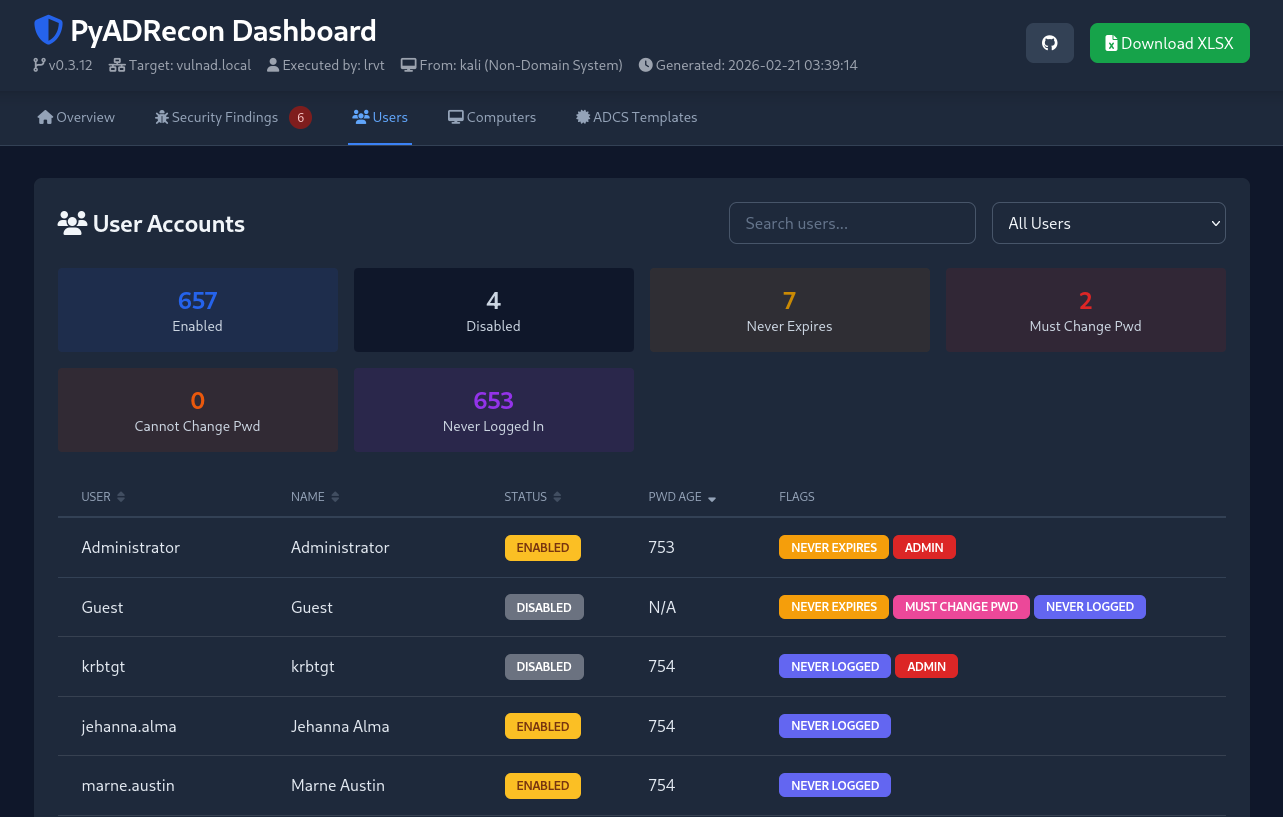 l4rm4nd/pyadrecon
Python3 implementation of ADRecon with support for NTLM and Kerberos authentication querying LDAP. Generates individual CSV files and a single XSLX +…
 woj-ciech/social-media-c2
Script is a proof of concept how to control your machine by using social media sites.
 sethwhy/bluedoor
Can you exploit the EternalBlue vulnerability (CVE-2017-0144) on a Windows 7 system and retrieve the hidden flag? Your goal is to gain administrative…
 hrmtz/snet
AI-guided CTF - Break into a real server with Claude Code as your trainer
