ZerologonWithImpacket-CVE2020-1472

A practical proof-of-concept for CVE-2020-1472 (Zerologon) using the Impacket library to exploit Netlogon vulnerability and perform unauthorized…

A practical proof-of-concept for CVE-2020-1472 (Zerologon) using the Impacket library to exploit Netlogon vulnerability and perform unauthorized…

Exploit for CVE-2024-32002, a Git RCE vulnerability that uses recursive submodule cloning and symlinks to execute arbitrary commands on Windows and…

An exploit proof of concept for ConnectWise SecureConnect authentication bypass vulnerability.

Can you exploit the EternalBlue vulnerability (CVE-2017-0144) on a Windows 7 system and retrieve the hidden flag? Your goal is to gain administrative…

CVE-2026-31431-killed page-cache exploit — code exec into containers sharing the same image layer

Redis RCE through Lua Sandbox Escape vulnerability

Winrar CVE exploitation before 7.13 using multiple ADS streams on a single file (Custom PDF implementation)

HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)

This is a PoC exploit for CVE-2020-8559 Kubernetes Vulnerability

Utilize metasploit from a Kali Linux machine to exploit a well-known samba vulnerability (CVE-2007-2447). This is done in order to infiltrate a…

Exploit for CVE-2021-36934

Authenticated command injection exploit for QuickBox Pro v2.1.8, providing remote code execution as www-data and privilege escalation to root via…

Craft CMS RCE via relational conditionals in the control panel

Exploit for elevation of privilege vulnerability in QuickHeal's Seqrite EPS (CVE-2023-31497).

Proof-of-concept exploit for CVE-2026-0828, a BYOVD vulnerability in Safetica ProcessMonitorDriver.sys allowing unprivileged termination of…

Exploit for CVE-2019-14287, a sudo vulnerability allowing privilege escalation to root via crafted user ID specification. Provides a proof-of-concept…

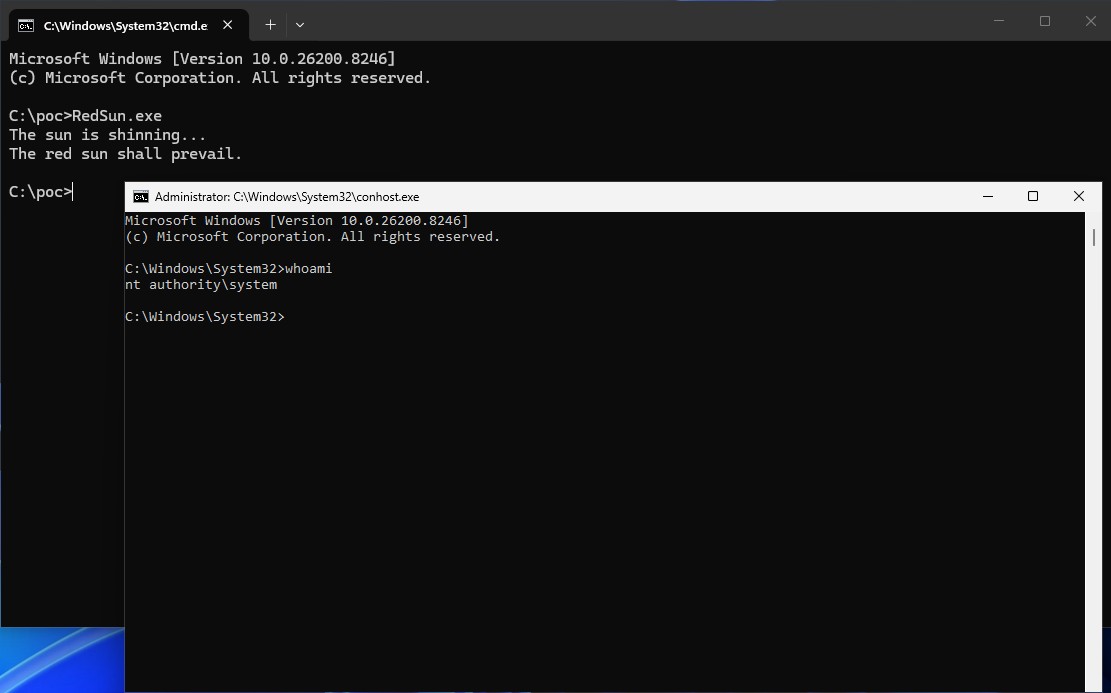
Windwos Zero Day Local PrivESc Exploit (CVE-2026-41091)

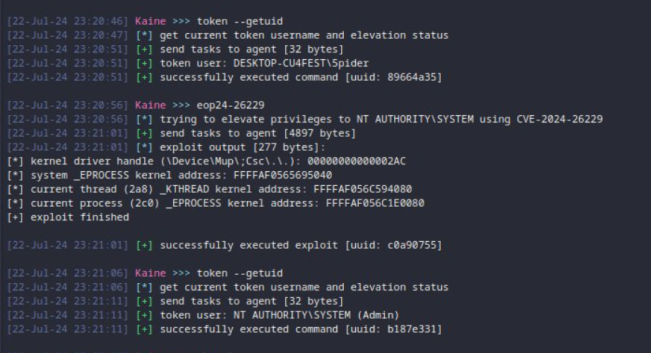
A firebeam plugin that exploits the CVE-2024-26229 vulnerability to perform elevation of privilege from a unprivileged user