
Aether-C2-Framework
 gmh5225/aether-c2-framework
🛠️ Explore custom C2 TTPs with Aether-C2-Framework, focusing on lightweight Rust implants and stealthy transport stacks to reduce forensic…
command-and-controleducationpayload-development+2
gmh5225/aether-c2-framework🛠️ Explore custom C2 TTPs with Aether-C2-Framework, focusing on lightweight Rust implants and stealthy transport stacks to reduce forensic…
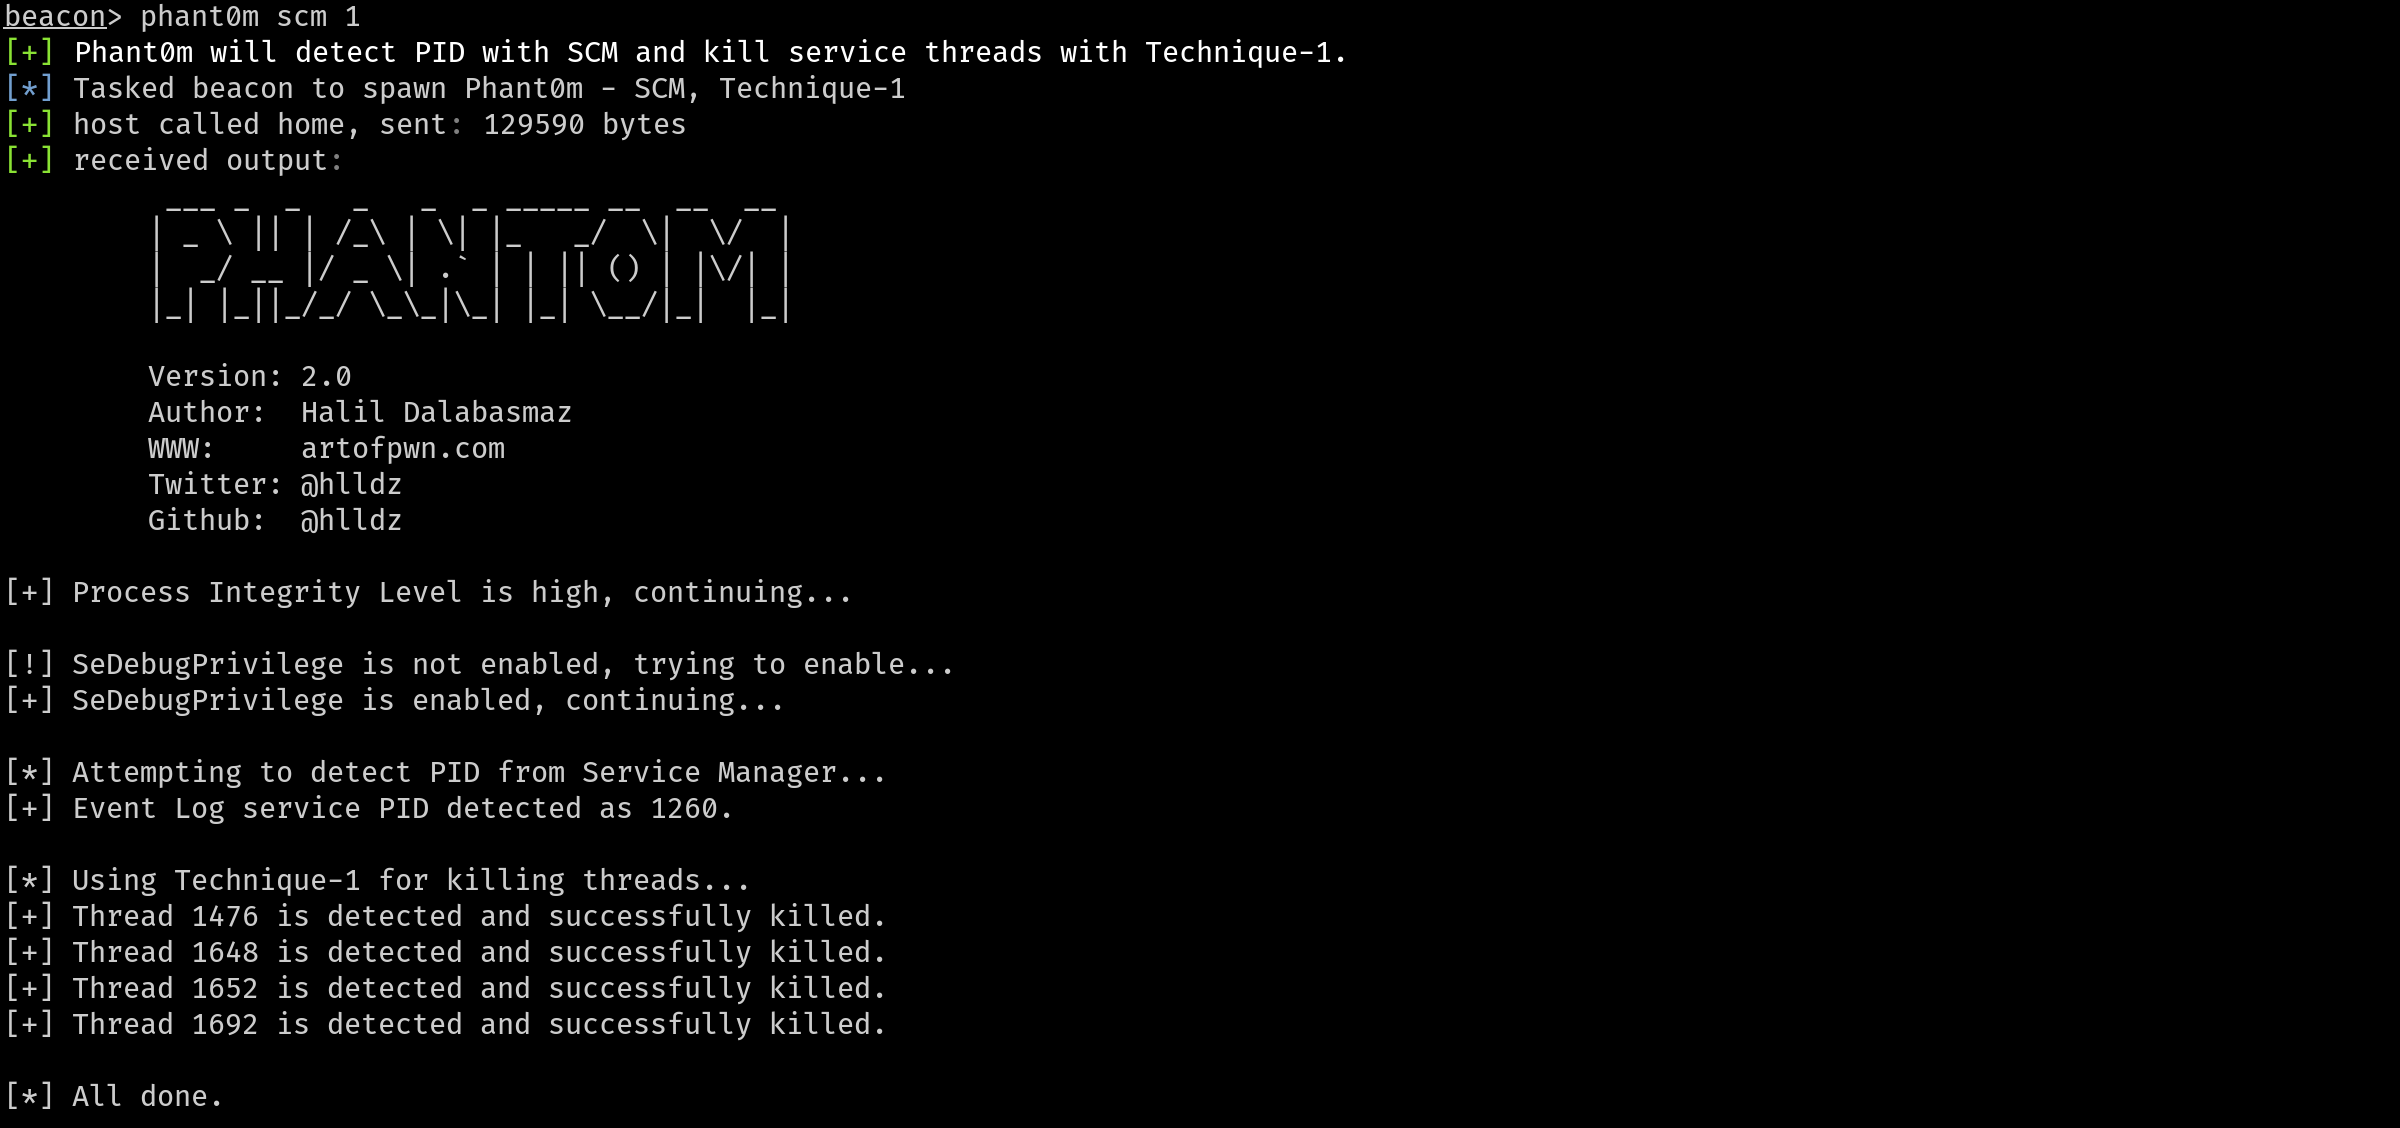 hlldz/phant0m
Windows Event Log Killer

 wattocyber/oscp-notes-2026
OSCP notes vault + exam cockpit dashboard: merged technique notes, variable-filled command decks, machines, creds, and runbook for exam day. MIT.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 infosecn1nja/red-teaming-toolkit
This repository contains cutting-edge open-source security tools (OST) for a red teamer and threat hunter.
 hacktricks-wiki/hacktricks
Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 snailsploit/claude-red
Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…
 s1ckb0y1337/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
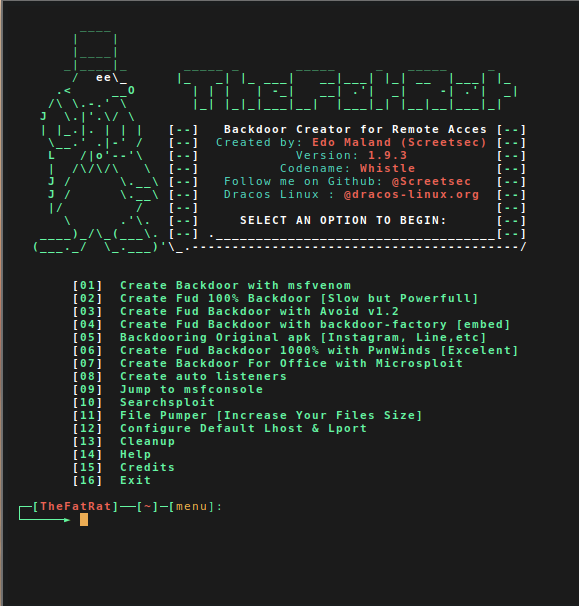 screetsec/thefatrat
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…
 samyk/poisontap
Exploits locked/password protected computers over USB, drops persistent WebSocket-based backdoor, exposes internal router, and siphons cookies using…
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
 mantvydasb/redteaming-tactics-and-techniques
Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…