
LSPromise
 lsposed/lspromise
Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
android-securityexploitationexploit-frameworks+4
489
lsposed/lspromiseAndroid complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
 alessandroz/pupy
Pupy is an opensource, multi-platform (Windows, Linux, OSX, Android), multi function RAT (Remote Administration Tool) mainly written in python. It…
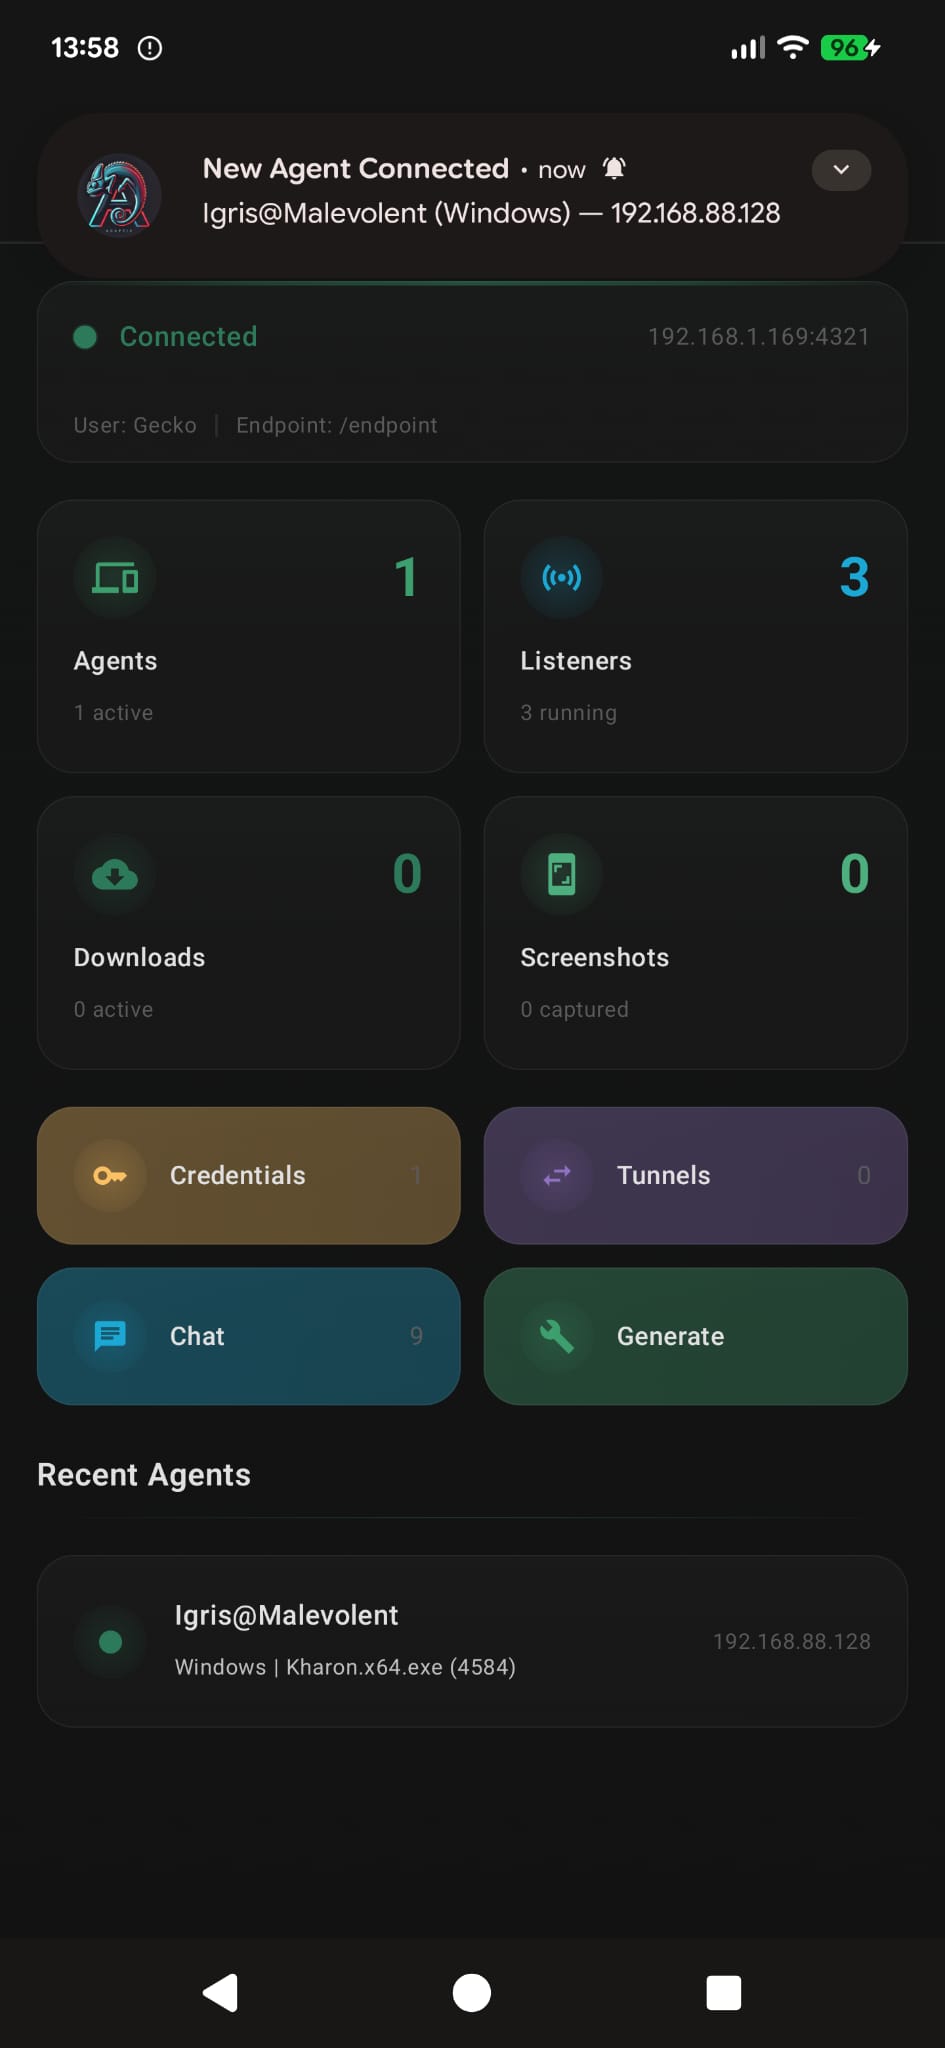 blacksnufkin/geckodroid
Android client for Adaptix C2 framework enabling remote agent management, interactive command shells, listener control, payload generation, and…
 kanpol/pocforcve-2015-1528
Proof-of-concept exploit for CVE-2015-1528 demonstrating privilege escalation on Android 5.0 via binder call fuzzing, with staged code injection into…
 spiralbl0ck/mallicious-ios-shortcut-keylogger-
iOS Shortcut-based keylogger designed to capture keystrokes and exfiltrate data from compromised devices.
 c0ntextomy/c0ntextomy
CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…
 5ky9uy/glass-cage-i18-2025-24085-and-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, exploiting WebKit (CVE-2025-24201) and Core Media (CVE-2025-24085) to achieve sandbox…
 persistent-security/smshell
PoC for a SMS-based shell. Send commands and receive responses over SMS from mobile broadband capable computers
 josephshenton/triple_fetch-kernel-creds
Attempt to steal kernelcredentials from launchd + task_t pointer (Based on: CVE-2017-7047)
 jingmatrix/pixel-ksu-root
CVE research and exploits to help gaining roots for Pixel devices
 secmob/pocforcve-2015-1528
I'll submit the poc after blackhat
 r0rt1z2/ghostlock
Kernel root exploit (CVE-2026-43499) for some Amazon devices
 mtjailed/unjailme
A sandbox escape based on the proof-of-concept (CVE-2018-4087) by Rani Idan (Zimperium)
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…