Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
71 results
PowerSploit preview
Archived

PowerSploit

GitHubpowershellmafia/powersploit

PowerSploit - A PowerShell Post-Exploitation Framework
lateral-movementpayload-generationpenetration-testing+5
13.1k
6 years ago
nosferatu preview

nosferatu

GitHubkindtime/nosferatu

DLL that hooks NTLM and Kerberos authentication in lsass.exe to inject a backdoor hash, enabling persistent authenticated access on Windows systems.
authenticationlateral-movementpenetration-testing+2
2421 year ago
PrintSpoofer-ReflectiveDLL preview

PrintSpoofer-ReflectiveDLL

GitHubjonyfilc/printspoofer-reflectivedll

The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…

exploitationlateral-movementpayload-development+4
22 months ago
RemoteDLLInjector preview

RemoteDLLInjector

GitHubal1ex/remotedllinjector

RemoteDLLInjector
exploitationpayload-developmentpenetration-testing+3
96 years ago
CVE-2026-66804 preview

CVE-2026-66804

GitHubcypherhippie/cve-2026-66804

Local Windows privilege escalation PoC for CVE-2026-66804: plants a COM DLL in a missing path to abuse Camera FrameServer and impersonate SYSTEM.
exploitationpenetration-testingpost-exploitation+1
12 months ago
Kernel_VADInjector preview

Kernel_VADInjector

GitHublleon1435/kernel_vadinjector

Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
adversarial-attackids-ips-evasionpayload-development+3
543 years ago
VectoredOverloading preview

VectoredOverloading

GitHubcheckpointsw/vectoredoverloading

Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
binary-exploitationexploitationmalware-analysis+6
12710 months ago
Mangle preview
Archived

Mangle

GitHuboptiv/mangle

Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
binary-analysisdefensive-toolsexploitation+6
1.2k3 years ago
winsos-poc preview

winsos-poc

GitHubthiagopeixoto/winsos-poc

A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.
adversarial-attackexploitationpayload-development+2
1122 years ago
CVE-2021-1366 preview

CVE-2021-1366

GitHubkoztkozt/cve-2021-1366

Proof-of-concept for Cisco AnyConnect HostScan local privilege escalation via DLL hijacking and IPC command injection, demonstrating DLL proxying to…
binary-exploitationexploitationpayload-development+2
3 years ago
venom-rs preview
Archived

venom-rs

GitHubmemn0ps/venom-rs

Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)
payload-developmentpost-exploitationred-teaming+2
3702 years ago
CLR-Unhook preview

CLR-Unhook

GitHubhwbp/clr-unhook

Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…
defensive-toolsexploitationpayload-development+3
21710 months ago
RdpThief preview

RdpThief

GitHub0x09al/rdpthief

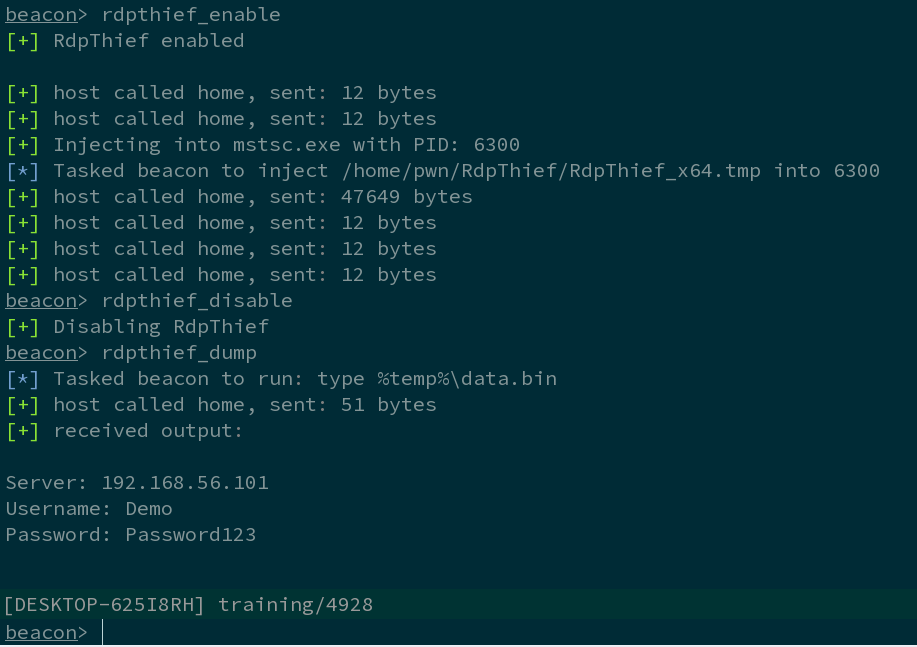
Extracting Clear Text Passwords from mstsc.exe using API Hooking.
penetration-testingpost-exploitationred-teaming
1.5k6 years ago
doublepulsar-usermode-injector preview

doublepulsar-usermode-injector

GitHubwithsecurelabs/doublepulsar-usermode-injector

A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…
exploitationmalware-analysispayload-development+2
1249 years ago
NoFaxGiven preview

NoFaxGiven

GitHubhackerhouse-opensource/nofaxgiven

Code Execution & Persistence in NETWORK SERVICE FAX Service
exploitationpayload-developmentpersistence-mechanisms+3
379 months ago
CVE-2024-50986 preview

CVE-2024-50986

GitHubriftsandroses/cve-2024-50986

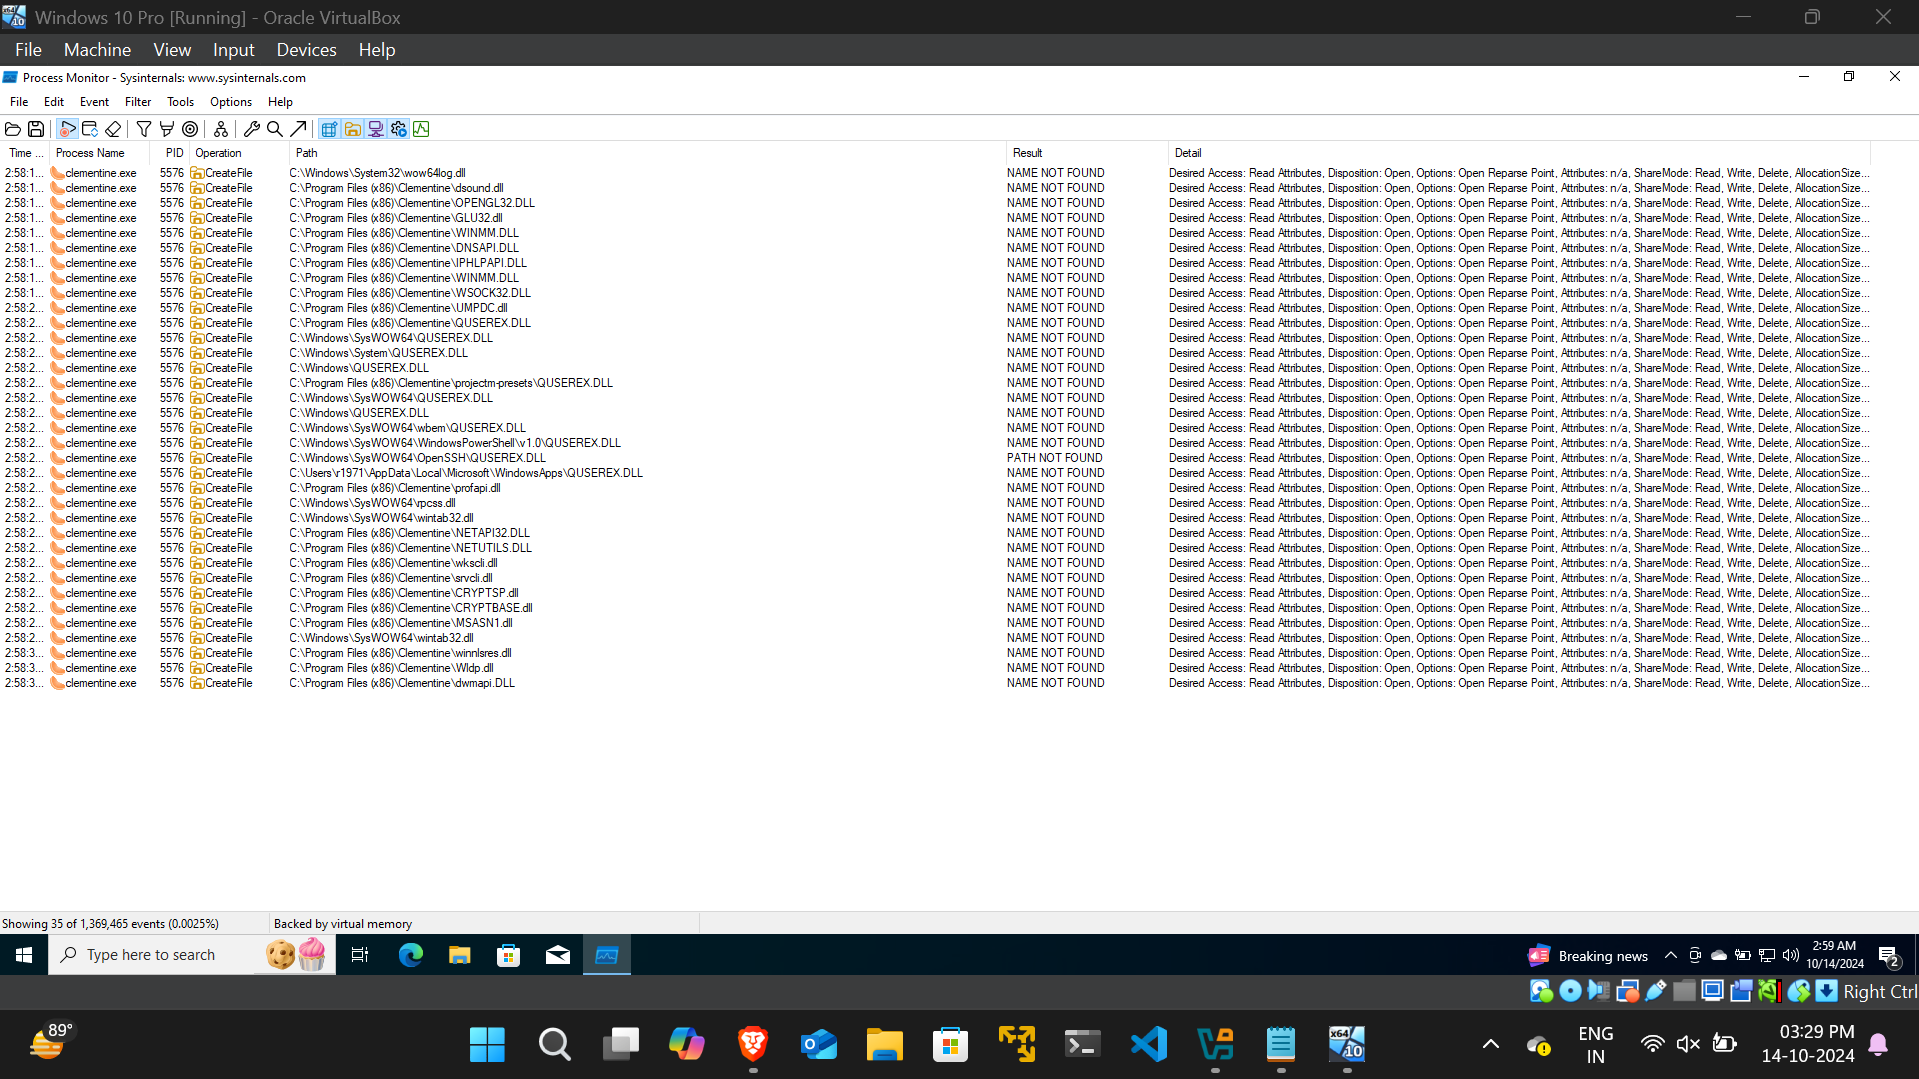
An issue in Clementine v.1.3.1 allows a local attacker to execute arbitrary code via a crafted DLL file (DLL Hijacking)
binary-exploitationexploitationpayload-generation+4
1 year ago
RDPCredentialStealer preview

RDPCredentialStealer

GitHubs12cybersecurity/rdpcredentialstealer

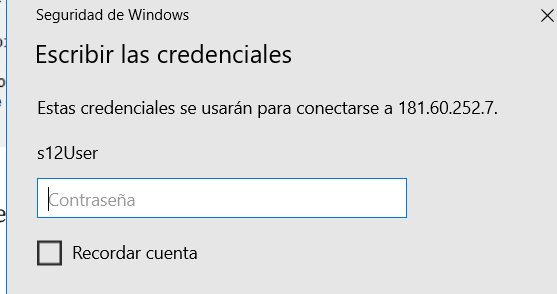
Windows implant that steals RDP credentials via API hooking (Detours) and DLL injection, capturing usernames and passwords to a file for red-team…
post-exploitationred-teaming
2667 months ago
ReflectiveDLLInjection preview

ReflectiveDLLInjection

GitHubstephenfewer/reflectivedllinjection

Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…

exploitationmemory-forensicspayload-development+2
3.4k13 years ago
Previous1234Next