

JavaPayload
 schierlm/javapayload
JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
exploitationmisconfigurationpayload-development+3
128
schierlm/javapayloadJavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
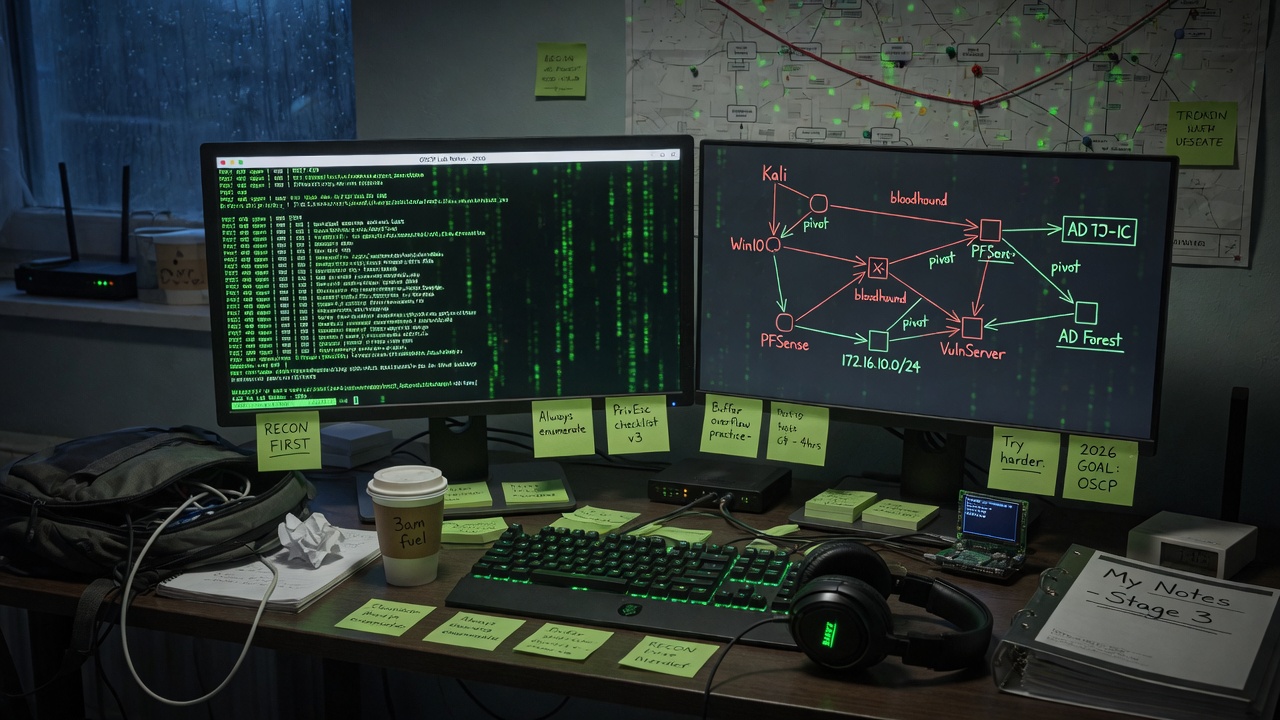
 wattocyber/oscp-notes-2026
OSCP notes vault + exam cockpit dashboard: merged technique notes, variable-filled command decks, machines, creds, and runbook for exam day. MIT.
 etahen/etahen
PS5 homebrew enabler payload offering post-exploitation features: custom plugin/payload loading, unsigned fself/fpkg support, debug settings, FTP…
 johnhammond/cve-2021-34527
PowerShell script for local privilege escalation via PrintNightmare (CVE-2021-34527). Injects a custom DLL payload to add a local admin user,…
 syss-research/outis
outis is a custom Remote Administration Tool (RAT) or something like that. It was build to support various transport methods (like DNS) and platforms…
 nccgroup/async-pico-hub
Async PICO Hub is a work-in-progress framework to extend Cobalt Strike with custom event monitoring and in-process Asynchronous BOFs
 pentestfunctions/best-cve-2025-8088
Winrar CVE exploitation before 7.13 using multiple ADS streams on a single file (Custom PDF implementation)
 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
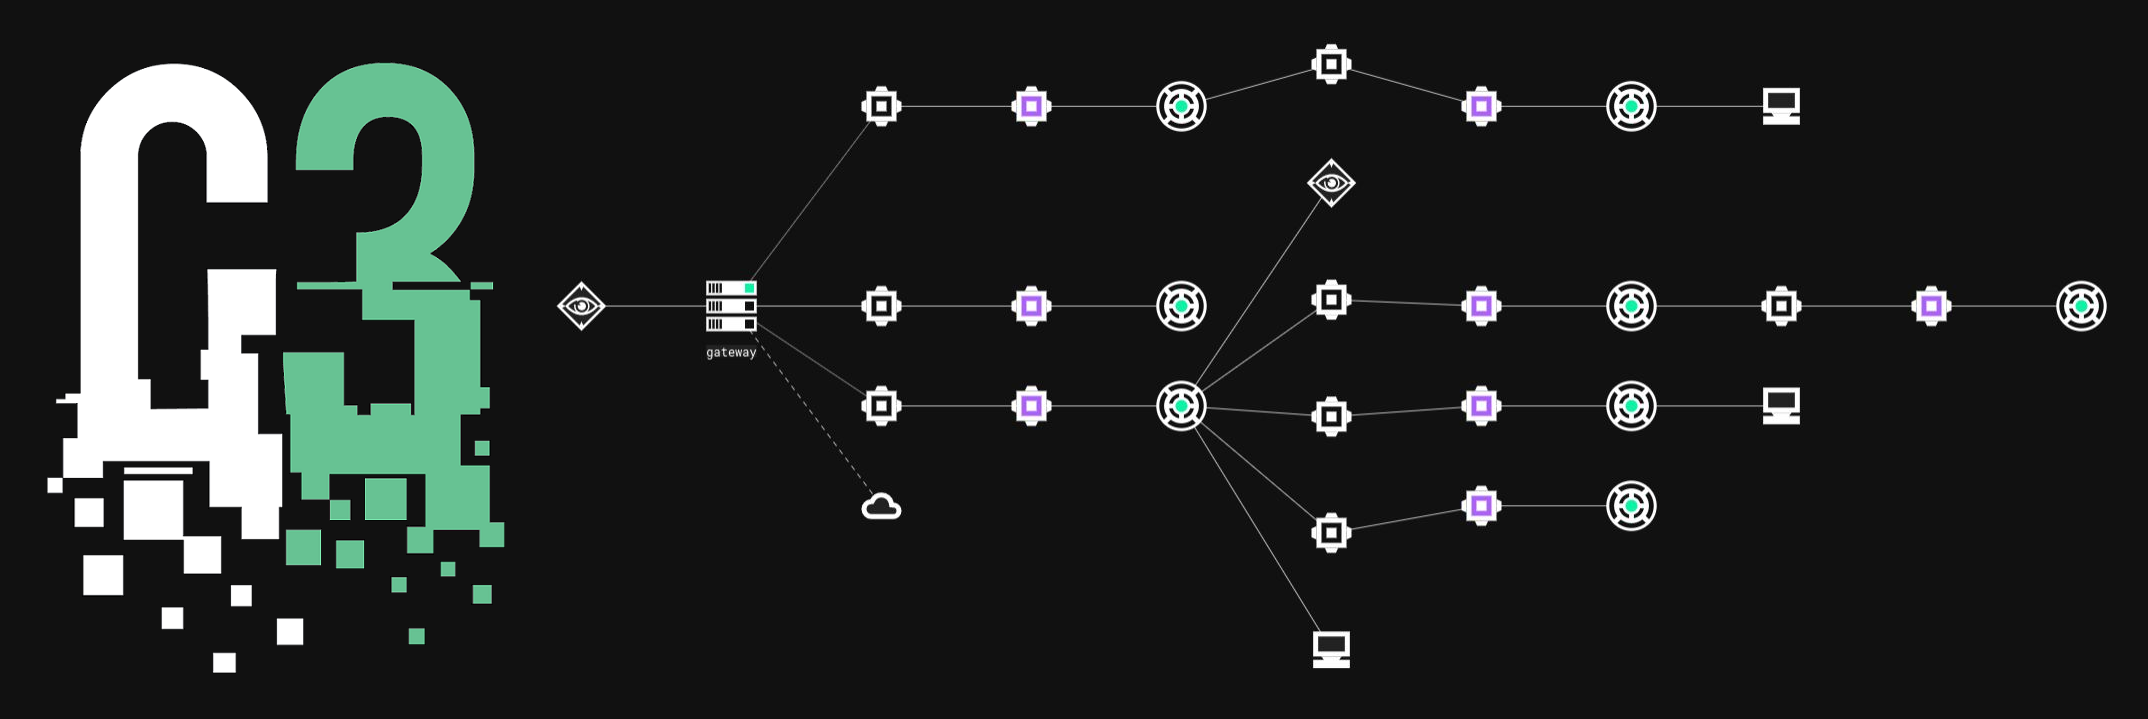 reverseclabs/c3
Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…
 anthemtotheego/inlineexecute-assembly
Cobalt Strike BOF for in-process .NET assembly execution with AMSI/ETW bypass, custom AppDomain, and named pipe/mailslot output redirection.
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
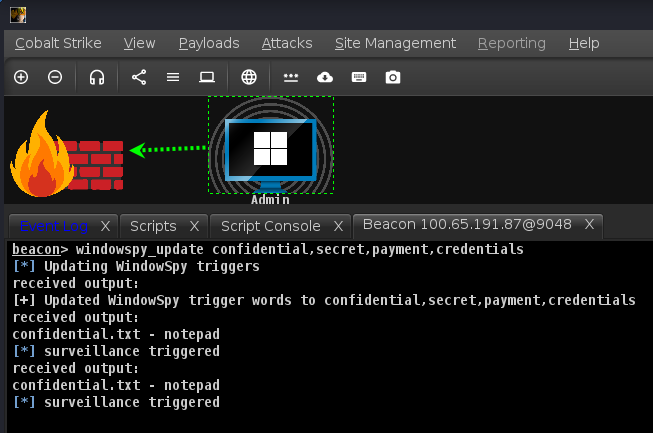 codextf2/windowspy
Cobalt Strike Beacon Object File for automated, targeted user surveillance. Triggers screenshots or custom actions when specific window titles (e.g.,…
 hagrid29/duplicatedump
Dumping LSASS with a duplicated handle from custom LSA plugin
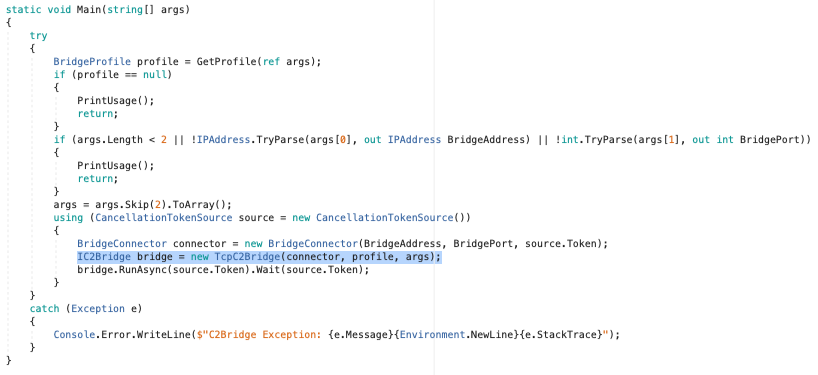 cobbr/c2bridge
C2Bridges allow developers to create new custom communication protocols and quickly utilize them within Covenant.
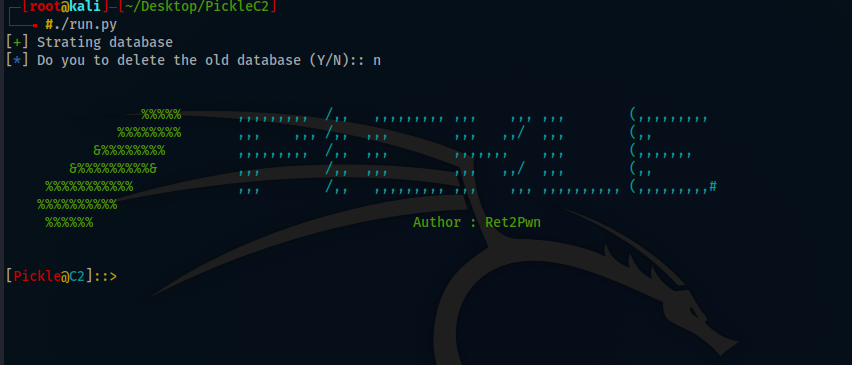 xret2pwn/picklec2
Encrypted C2 framework for post-exploitation and lateral movement, supporting PowerShell implants and custom modules for red team engagements.
 illegal-instruction-co/processhacker-mcp
Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…
 decoder-it/newmachineaccount
Creates Active Directory machine accounts with custom passwords, supporting optional OU placement, explicit credentials, and UAC flag configuration.
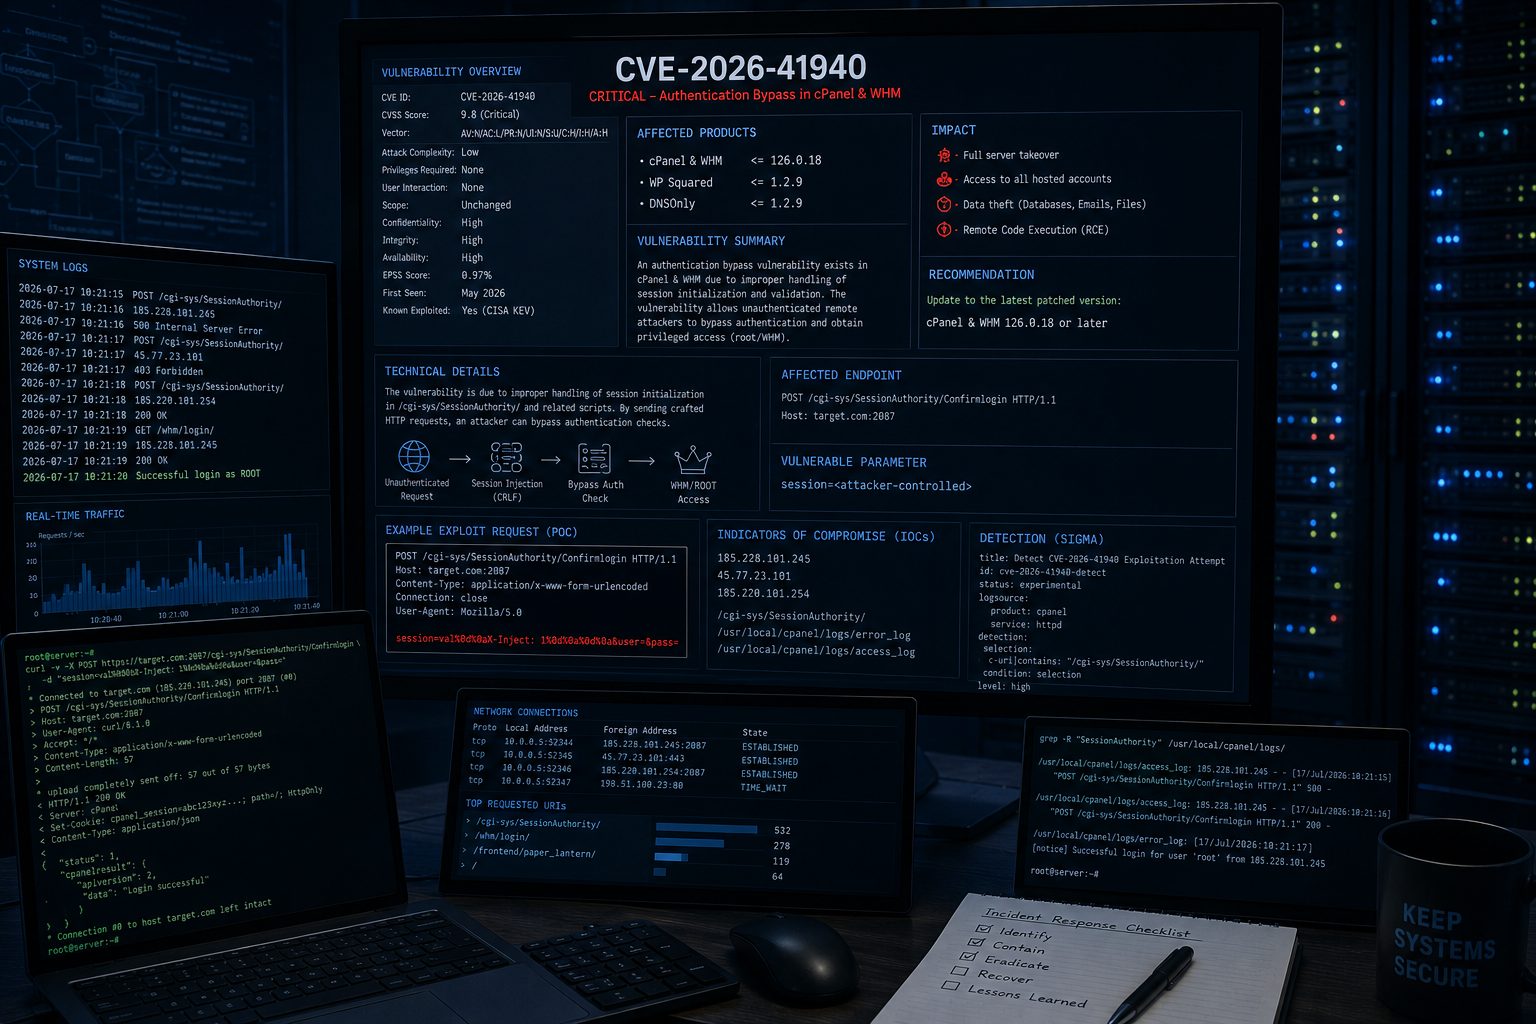 tc4dy/cve-2026-41940-poc-exploit
🚀 CVE-2026-41940 cPanel/WHM Auth Bypass Exploit - Best Flow 💥 CRLF injection leads to auth bypass, session hijacking & account leak. ✅ Proxy,…