
ranger
 funkandwagnalls/ranger
A tool for security professionals to access and interact with remote Microsoft Windows based systems.
command-and-controlexploitationlateral-movement+3
431
funkandwagnalls/rangerA tool for security professionals to access and interact with remote Microsoft Windows based systems.
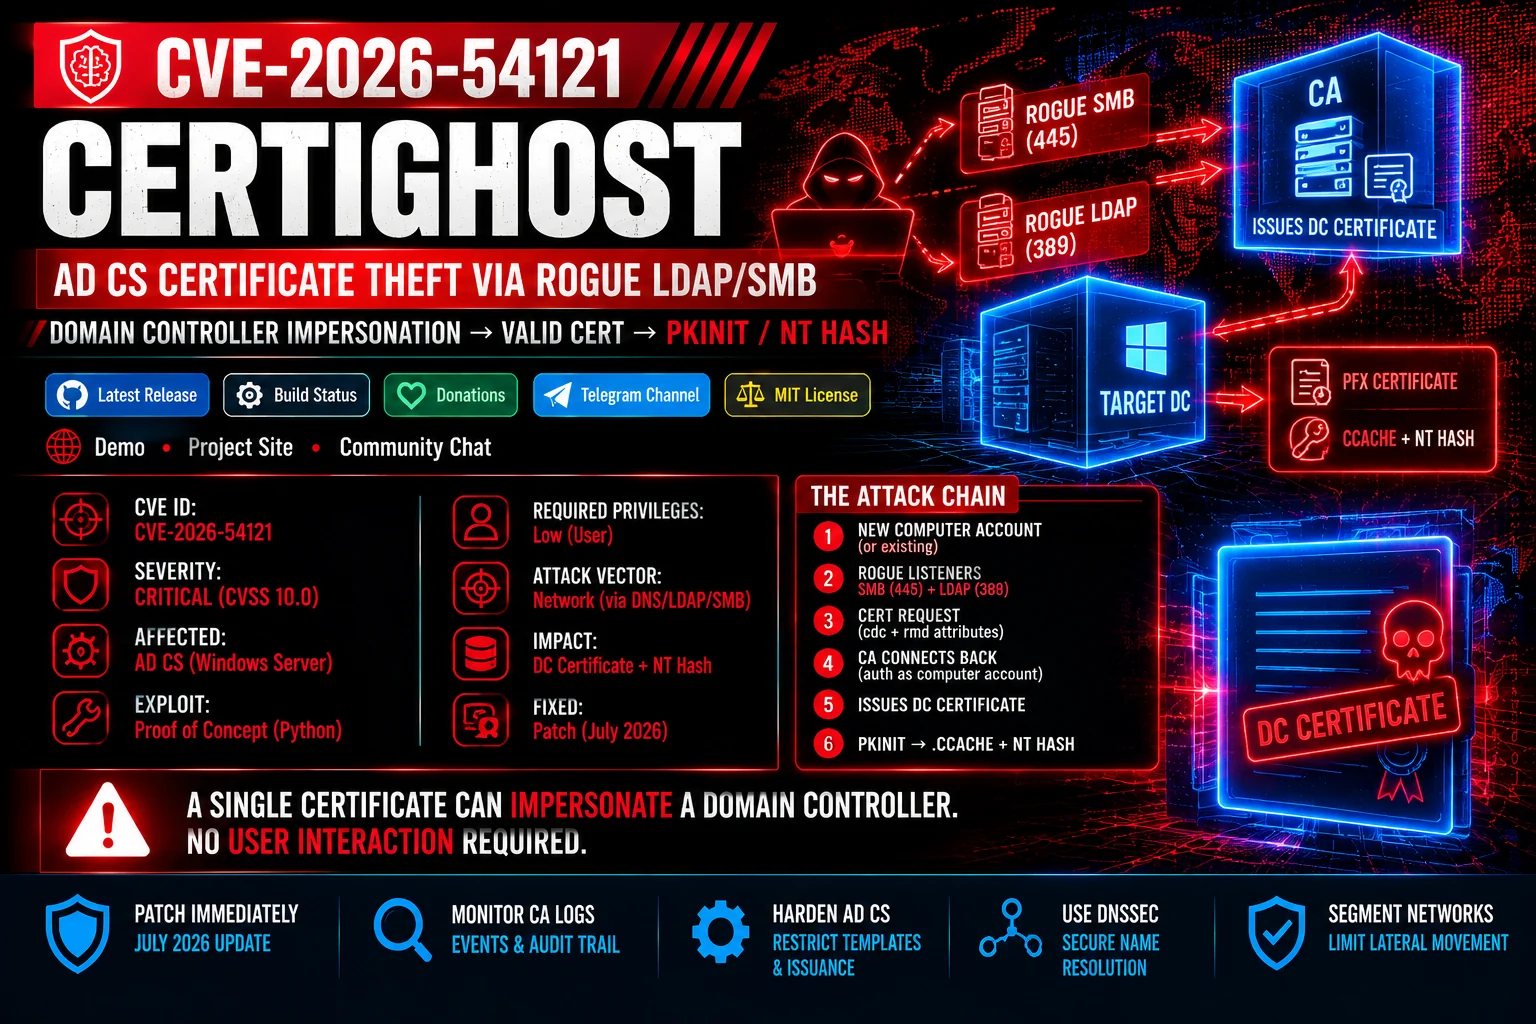 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 viralmaniar/hivejack
This tool can be used during internal penetration testing to dump Windows credentials from an already-compromised host. It allows one to dump SYSTEM,…
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it
 nccgroup/chuckle
An automated SMB relay exploitation script.
 chron1k/oxide_hive
Exploit for CVE-2021-36934
 tc4dy/cve-2026-6875-poc-exploit
CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…
 portbuster1337/atlas
Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#
 antoniococo/malseclogon
A little tool to play with the Seclogon service
 jarnovandenbrink/getspnless
Python tool to automatically perform SPN-less RBCD attacks.
 rweijnen/createdump
Leverage WindowsApp createdump tool to obtain an lsass dump
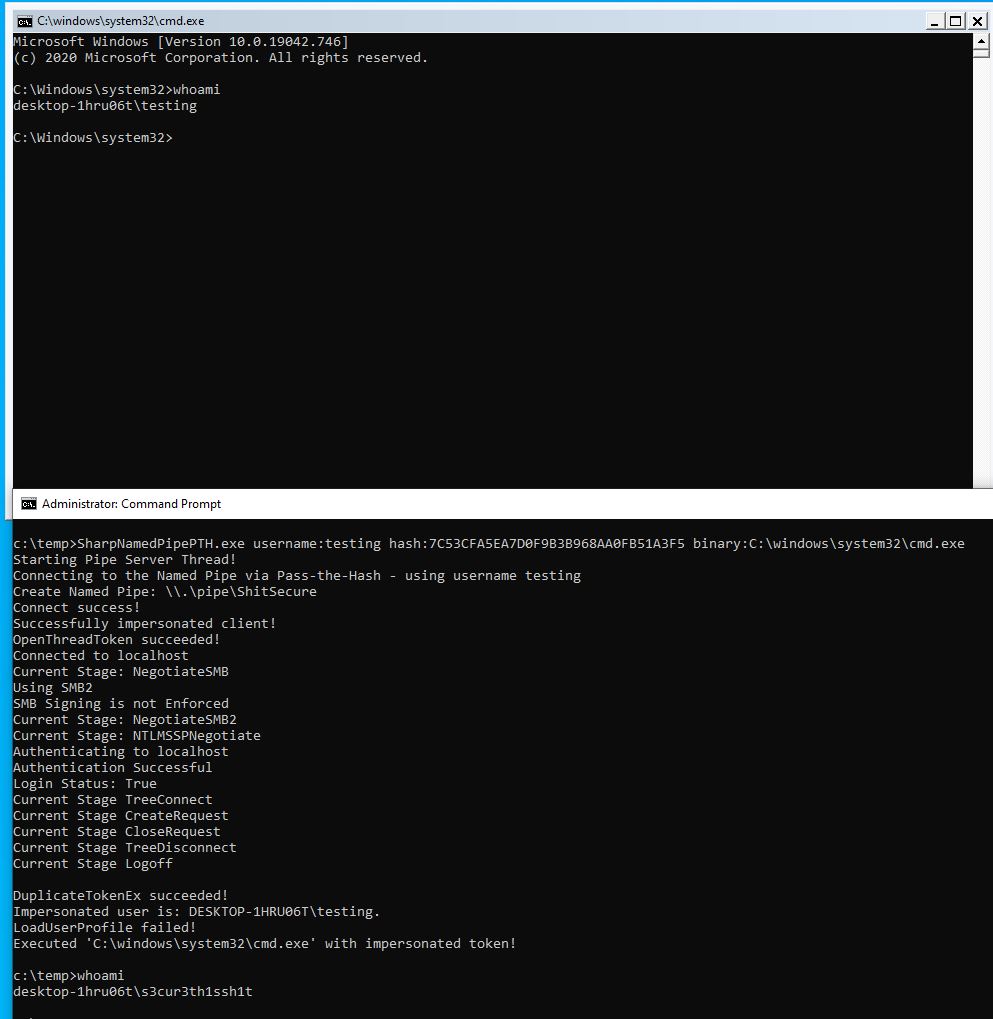 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
 n00py/hwacha
Deploy payloads to *Nix systems en masse
 mayyhem/sharpsccm
C# post-exploitation tool for abusing Microsoft Configuration Manager (SCCM) to perform lateral movement, credential gathering, and NTLM…
 byt3bl33d3r/pth-toolkit
Modified version of the passing-the-hash tool collection made to work straight out of the box
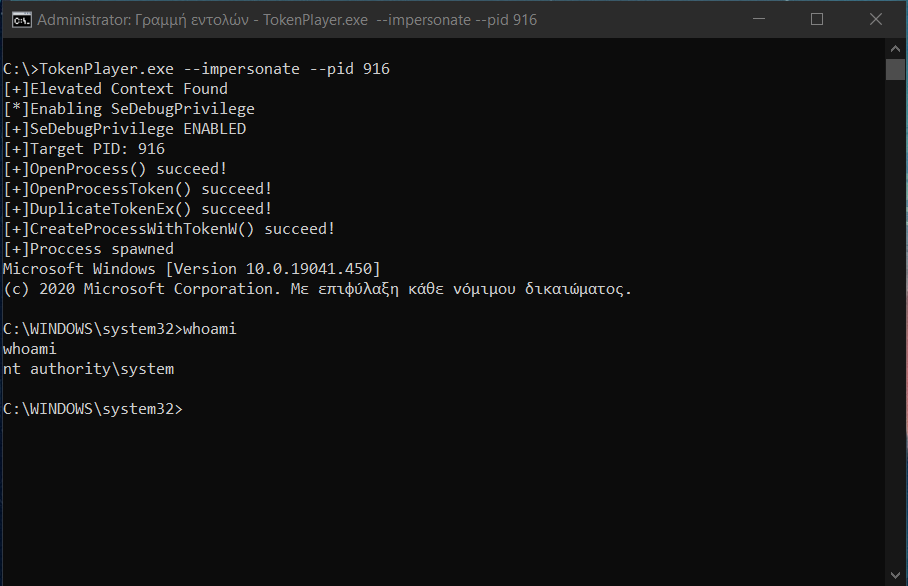 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 bishopfox/firecat
Firecat is a penetration testing tool that allows you to punch reverse TCP tunnels out of a compromised network.