

best-CVE-2025-8088
 pentestfunctions/best-cve-2025-8088
Winrar CVE exploitation before 7.13 using multiple ADS streams on a single file (Custom PDF implementation)
binary-exploitationexploitationpayload-development+4
10
pentestfunctions/best-cve-2025-8088Winrar CVE exploitation before 7.13 using multiple ADS streams on a single file (Custom PDF implementation)
 mbanyamer/msc-eviltwin-local-privilege-escalation
CVE-2025-26633 (CVSS 7.8) – Zero-day MMC .msc EvilTwin LPE actively exploited by Water Gamayun APT. PoC creates local admin via malicious MSC file on…
 5ky9uy/glass-cage-i18-2025-24085-and-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, exploiting WebKit (CVE-2025-24201) and Core Media (CVE-2025-24085) to achieve sandbox…
 manhndd/cve-2019-6329
Local Privilege Escalation in HP Support Assistant
 redtimmy/perf-exploiter
CVE-2014-2630 exploit for xglance-bin
 muhammad-ali007/localpotato_cve-2023-21746
Proof-of-concept exploit for Windows local privilege escalation (CVE-2023-21746) abusing NTLM local authentication to gain SYSTEM privileges via SMB…
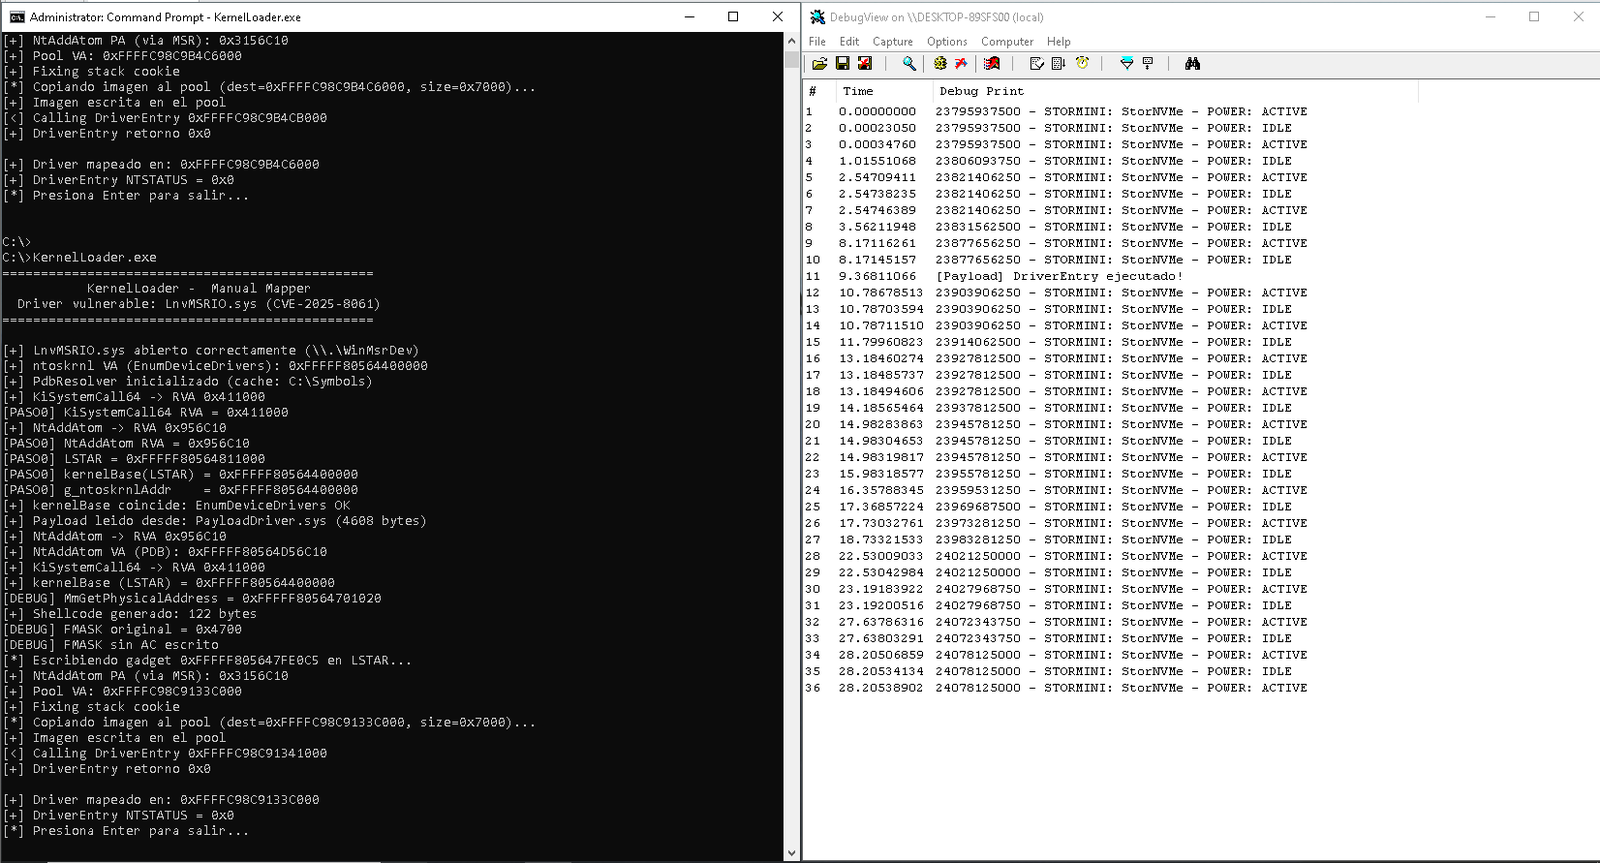 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
 davidcarliez/cve-2019-9702_symantec_encryption_desktop_lpe_poc
Local Privilege Escalation PoC to pop a SYSTEM shell for CVE-2019-9702 in Symantec Encryption Desktop.
 open-flaw/cve-2026-2005
PostgreSQL pgcrypto heap buffer overflow PoC demonstrating CVE-2026-2005: low-privileged RCE and privilege escalation to superuser via crafted…
 tomadimitrie/cve-2026-54424
Exploiting Parsec for Windows to gain SYSTEM privileges
 vulnquest58/vq-refluxcore
is an advanced security research framework designed to model, analyze, and demonstrate Local Privilege Escalation (LPE) mechanics associated with…
 r2qa/cve-2026-17544
Exploit for CVE-2026-17544: PHP bcmath OOB write converted into memory-only RCE, bypassing disable_functions and open_basedir with a runtime…
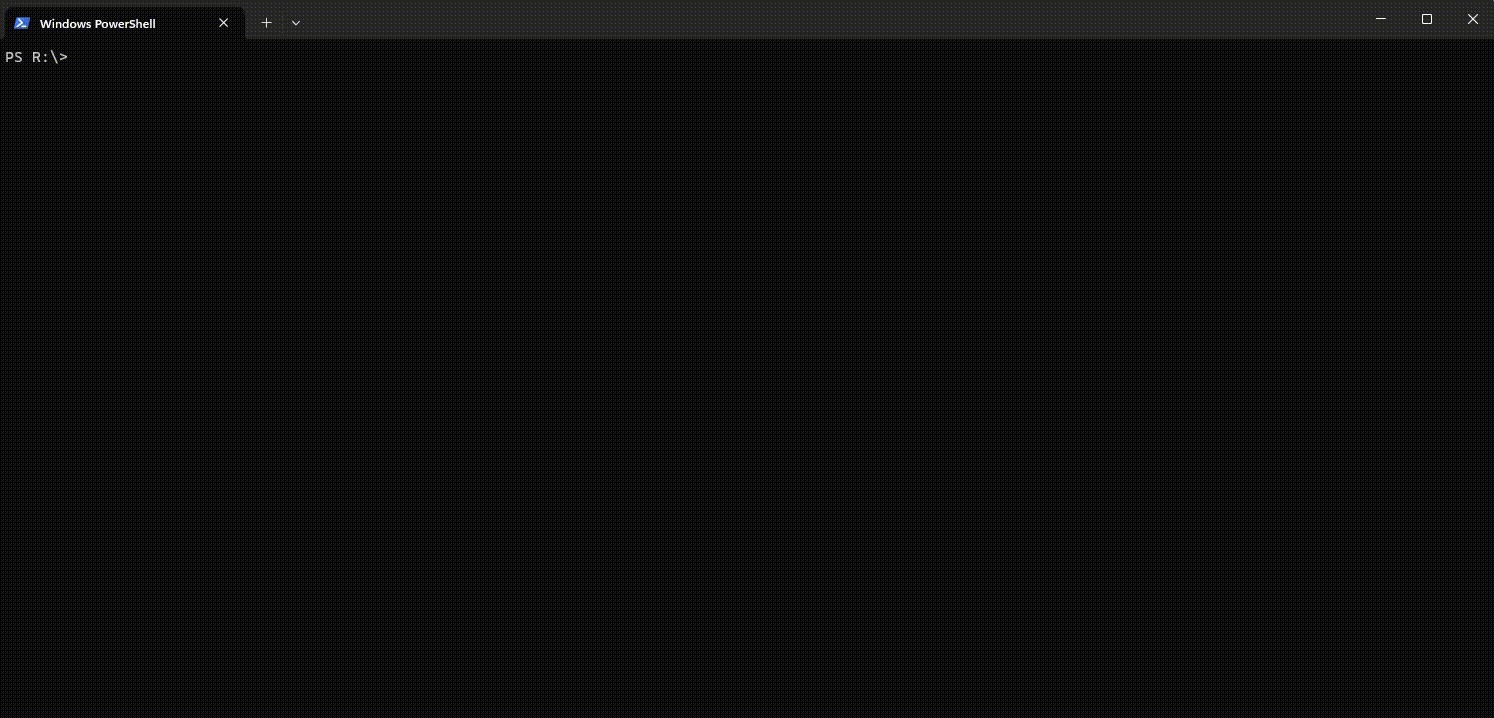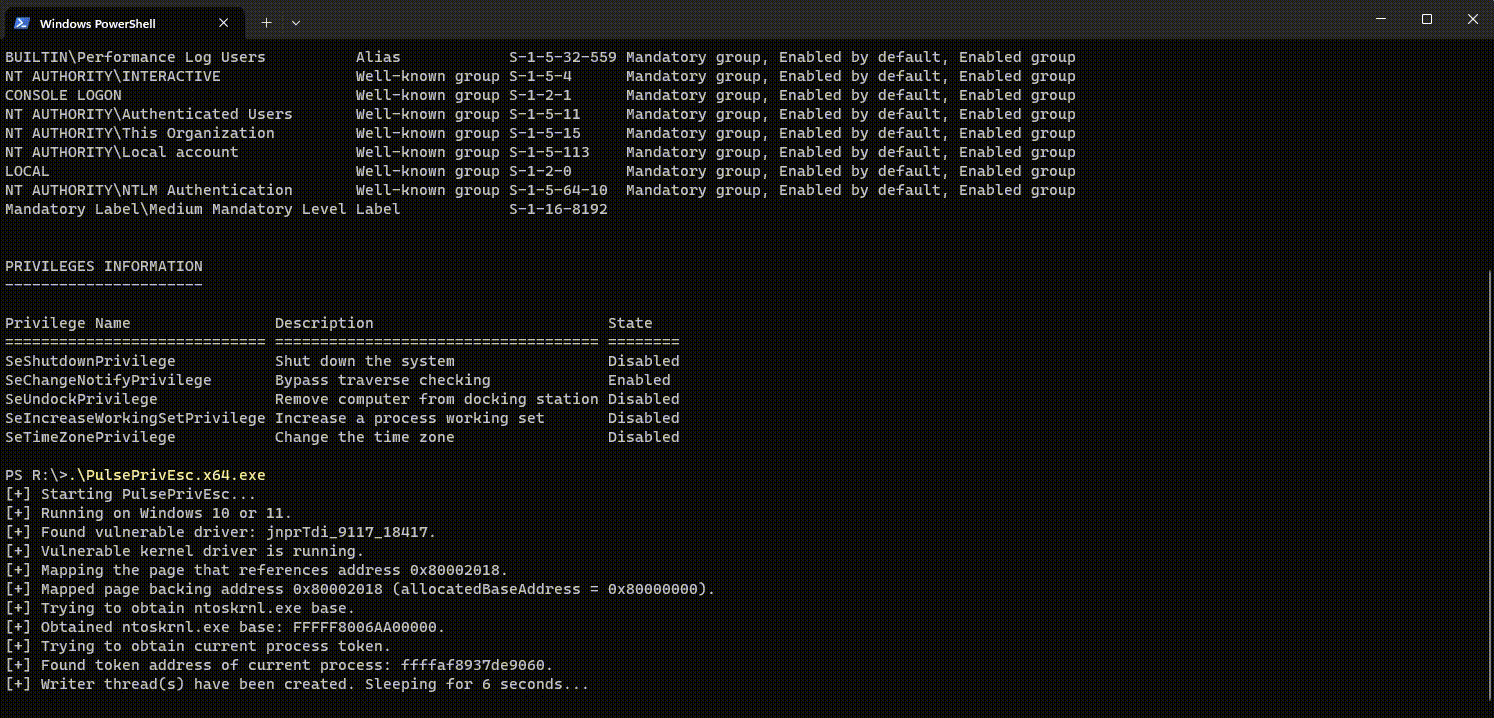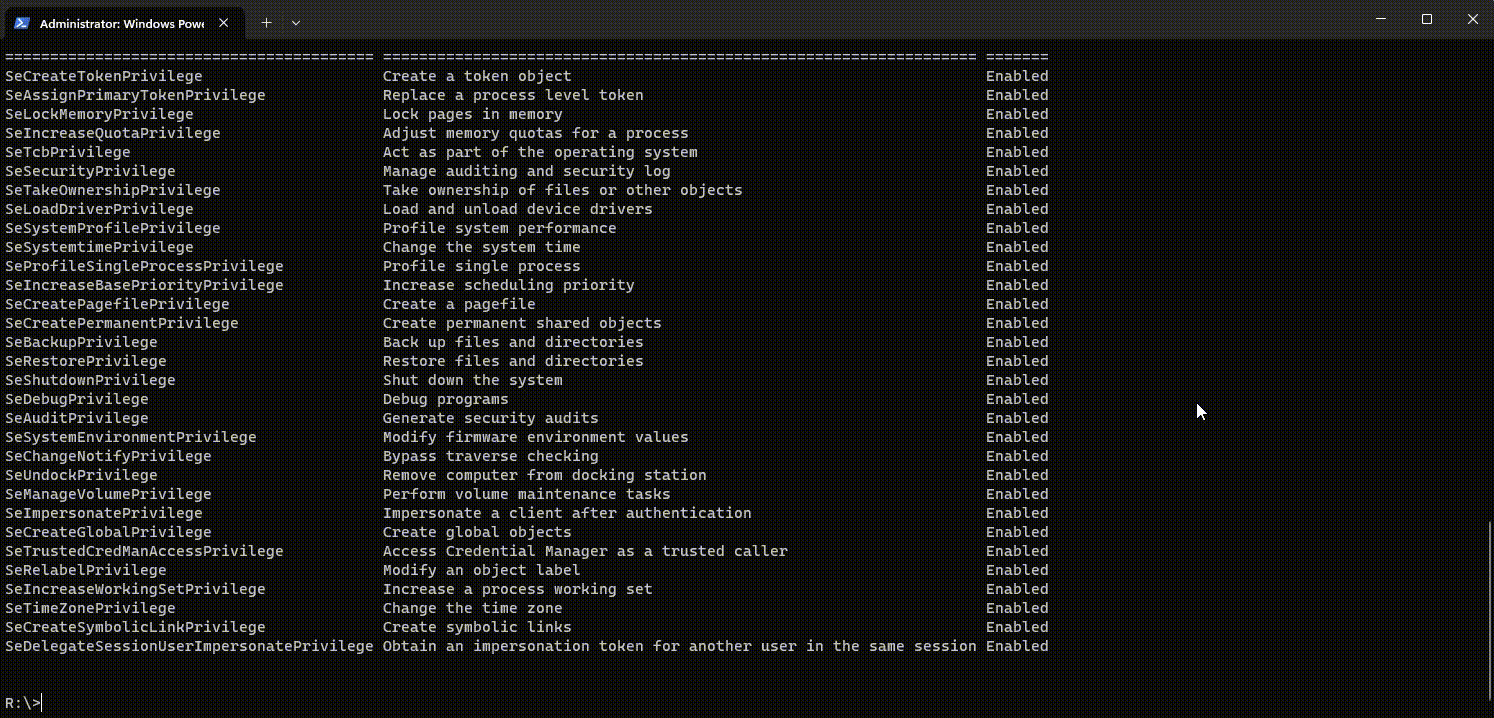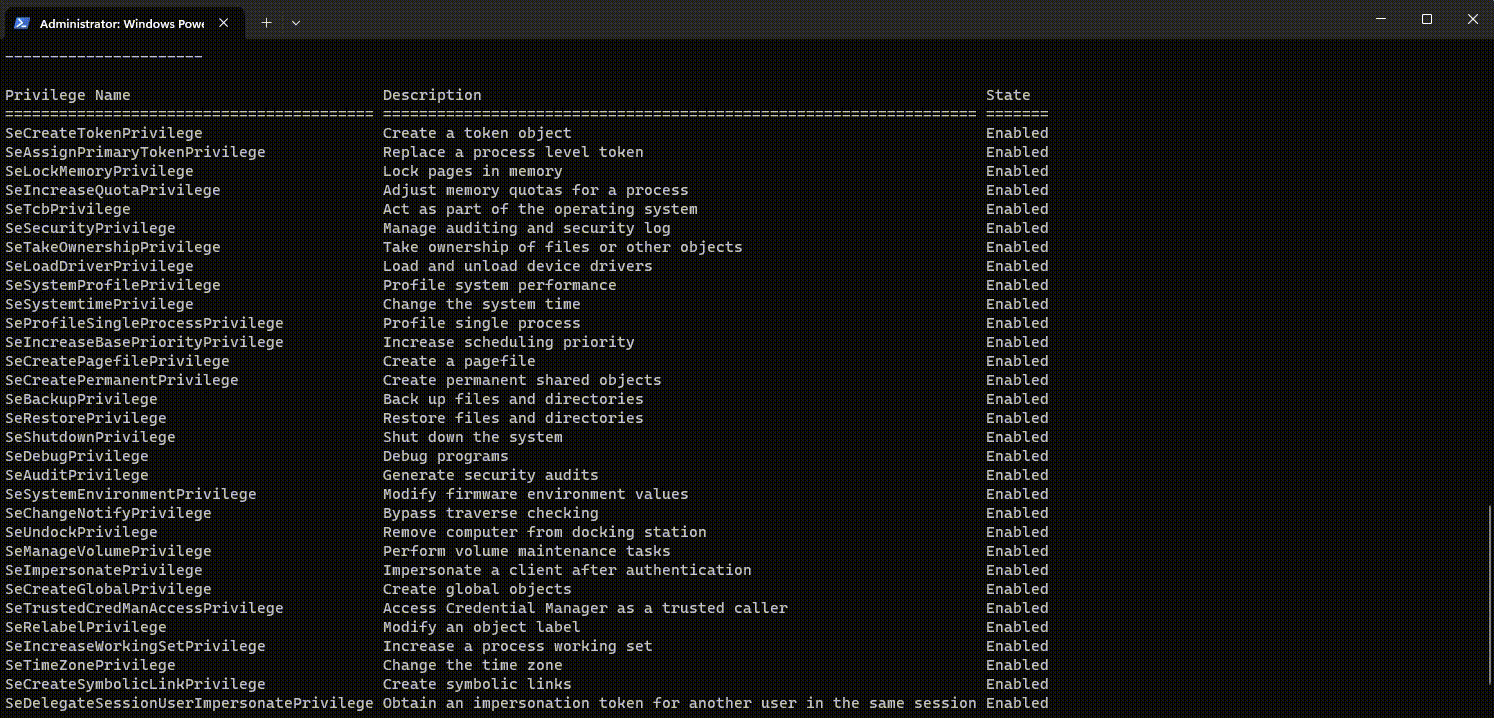 tijme/ivanti-cve-2023-35080-privilege-escalation-bof
Ivanti Secure Access (previously Pulse Secure) privilege escalation Cobalt Strike BOF (CVE-2023-35080).
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…
 captain-woof/cve-2026-25243
Stable POC for CVE-2026-25243 (Redis RESTORE double-free -> remote code execution)
 heegong/cve-2022-24924
An improper access control in LiveWallpaperService prior to versions 3.0.9.0 allows to create a specific named system directory without a proper…
 rat5ak/cve-2026-31413-bpf-container-escape
CVE-2026-31413: BPF verifier soundness bug - container escape

 nu11secur1ty/0
Exploit for a Windows Defender race condition that escalates to SYSTEM via use-after-free, crashes MsMpEng.exe, spawns a hidden shell, and persists…