
pivotool
 artusec/pivotool
Bash-based post-exploitation tool for semi-automated network pivoting, enabling lateral movement through compromised systems during penetration tests.
lateral-movementpenetration-testingpost-exploitation+1
9
artusec/pivotoolBash-based post-exploitation tool for semi-automated network pivoting, enabling lateral movement through compromised systems during penetration tests.
 synacktiv/gpblib
Common library for tools implementing GPO attack vectors
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
 tc4dy/cve-2026-6875-poc-exploit
CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…
 martinsohn/active-directory-trust-attacks
 chron1k/oxide_hive
Exploit for CVE-2021-36934

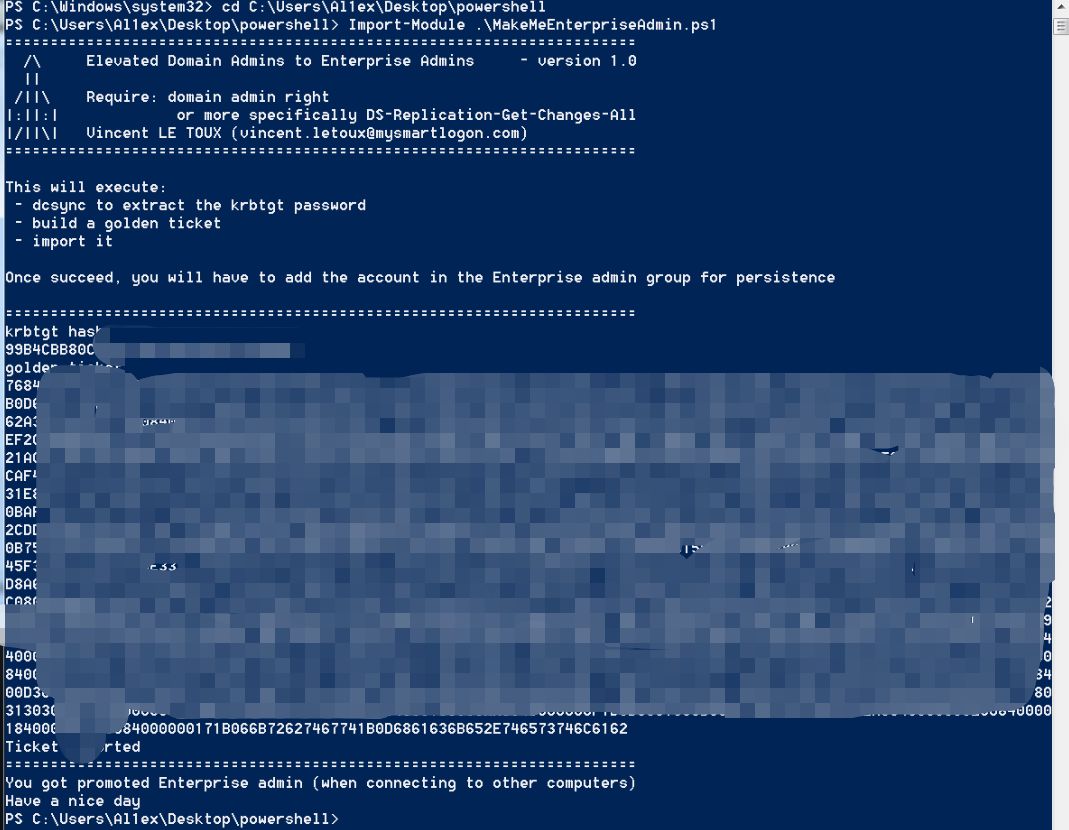 al1ex/makemeenterpriseadmin
MakeMeEnterpriseAdmin
 al1ex/hook-passwordchangenotify
Hook PasswordChangeNotify
 gunzf0x/cve-2020-0665
Proof of Concept for CVE-2020-0665, a.k.a. SID Filter Bypass.
 dll00p/cve-2021-1675
Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…
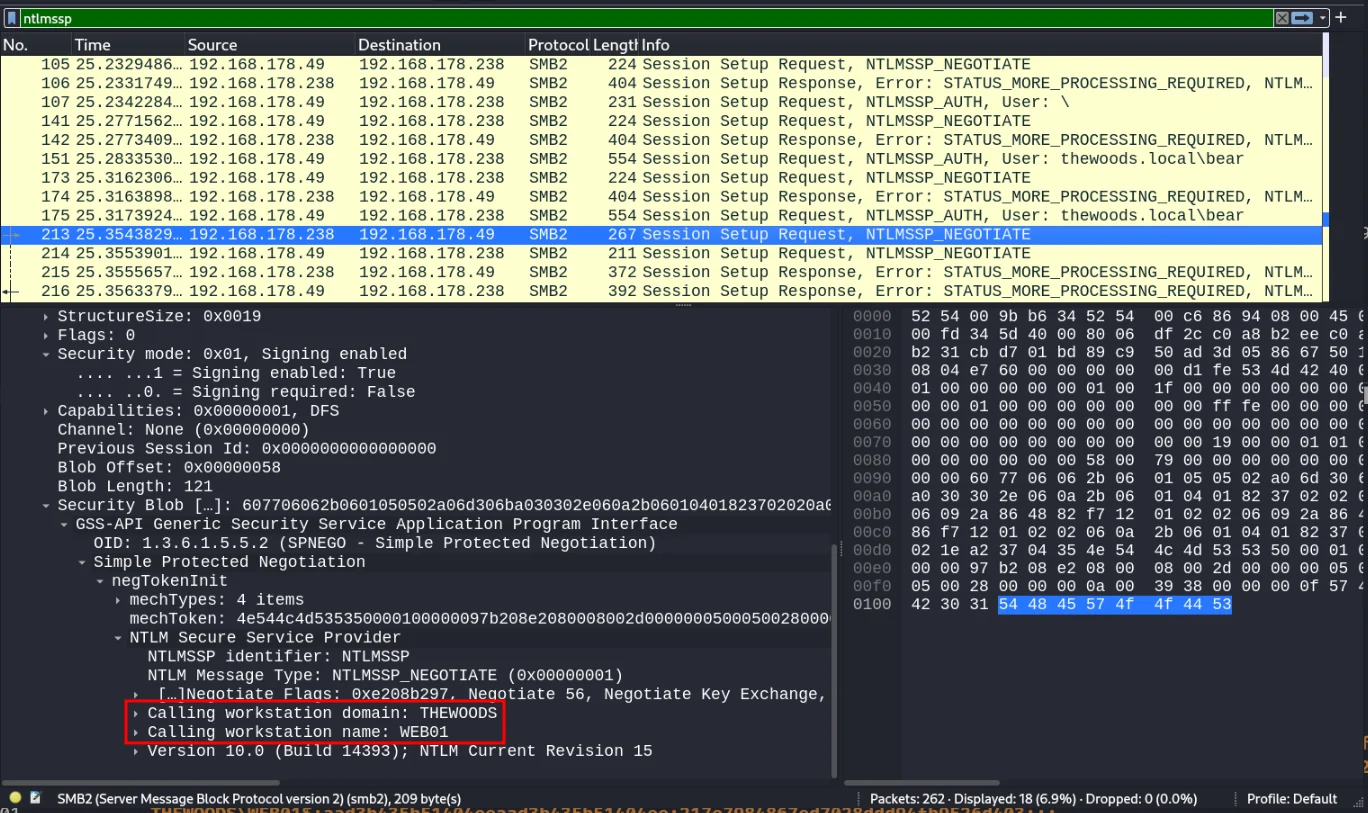 starscow/cve-2025-33073
PoC Exploit for the NTLM reflection SMB flaw.
 ianxtianxt/ssocks-0.0.14
SOCKS proxy for port forwarding and RDP tunneling, enabling lateral movement and remote access in penetration testing scenarios.
 dr4g0n23/cve-2020-1472
Exploit script for CVE-2020-1472 (ZeroLogon) with automated privilege escalation, credential dumping via secretsdump, and lateral movement using…
 coldzer0/reversesock5proxy
A tiny Reverse Sock5 Proxy written in C :V
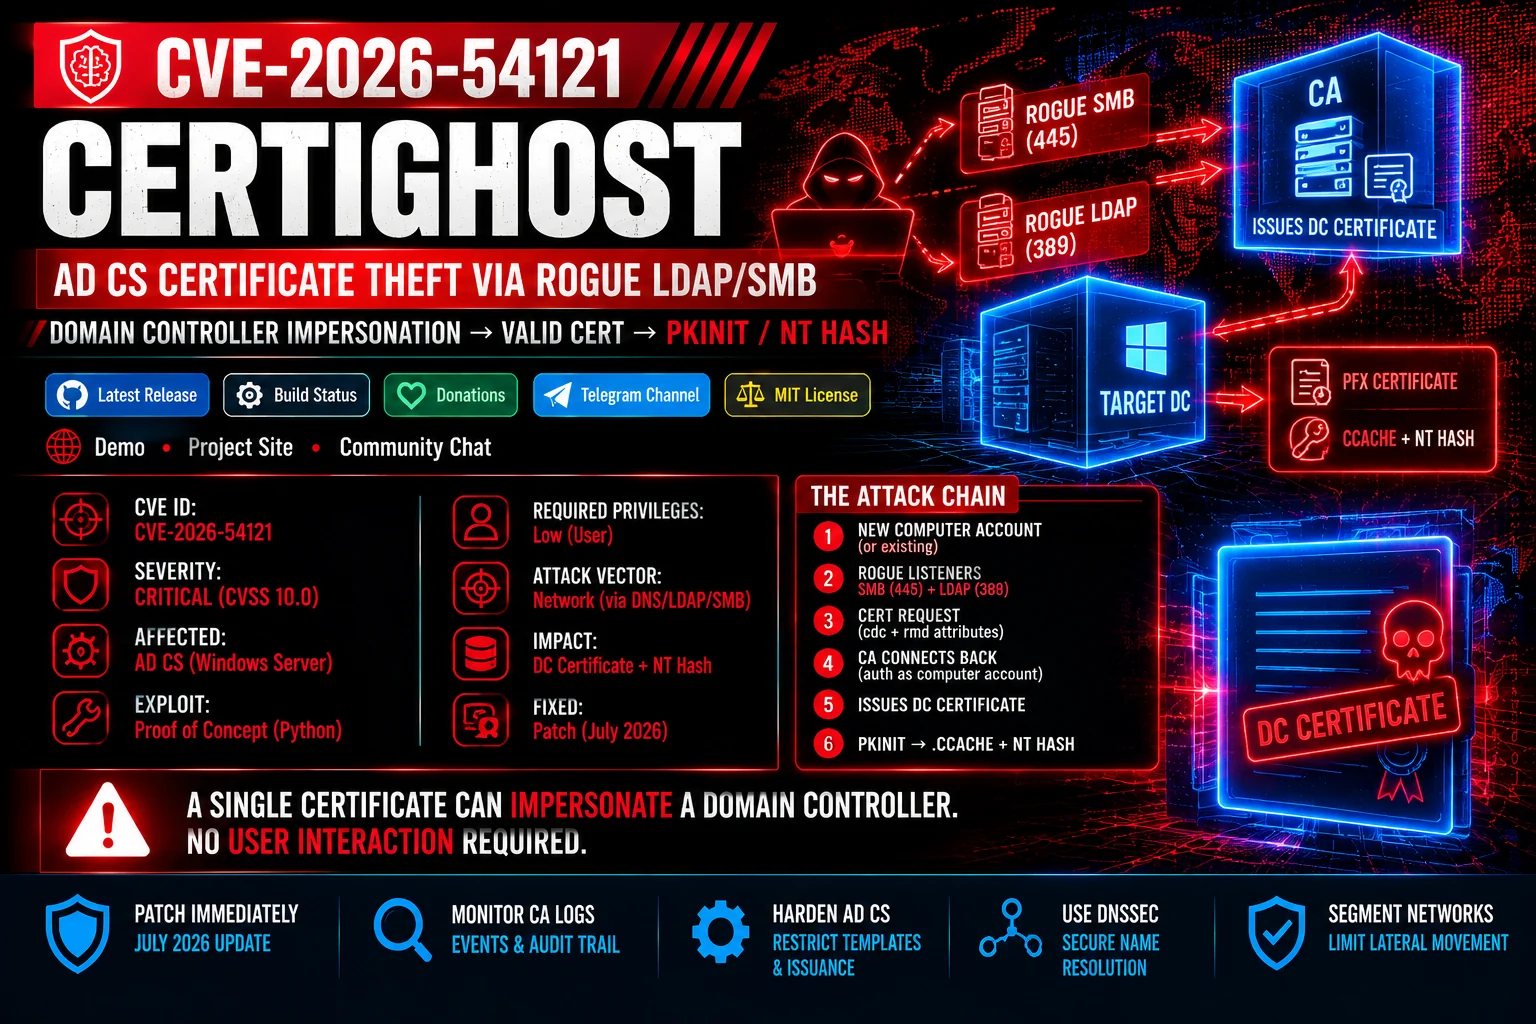 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 foxglovesec/potato
Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.