

TokenStealer
 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
impersonation-toolspost-exploitationprivilege-escalation+1
165
decoder-it/tokenstealerWindows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
 bishopfox/firecat
Firecat is a penetration testing tool that allows you to punch reverse TCP tunnels out of a compromised network.
 xret2pwn/picklec2
Encrypted C2 framework for post-exploitation and lateral movement, supporting PowerShell implants and custom modules for red team engagements.
 zblurx/acltoolkit
Active Directory ACL abuse toolkit for privilege escalation, DCSync, object ownership modification, and lateral movement via logon script…
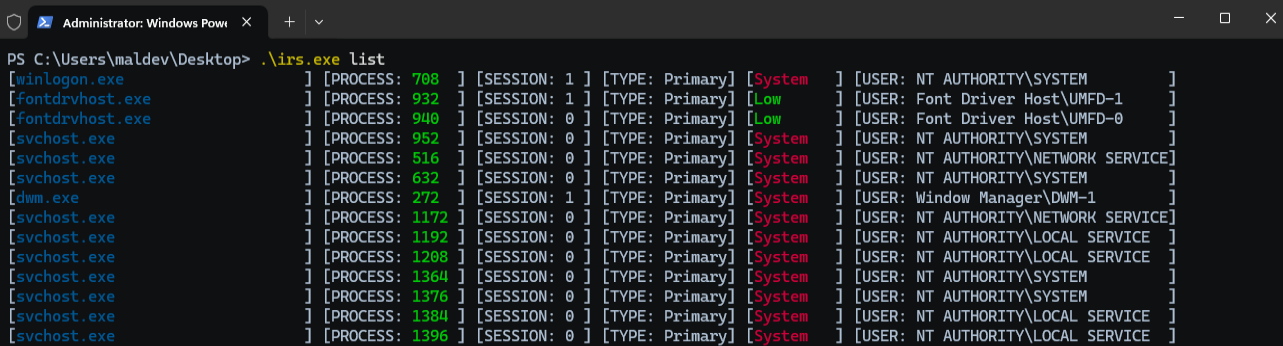 zblurx/impersonate-rs
Rusty Impersonate
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
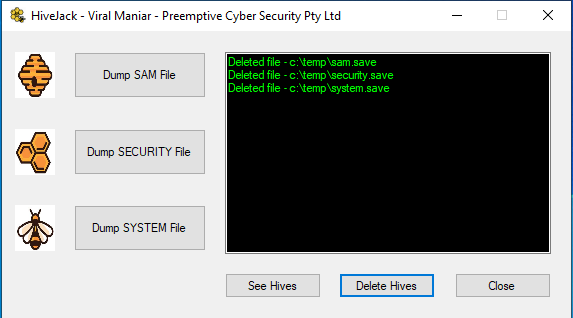 viralmaniar/hivejack
This tool can be used during internal penetration testing to dump Windows credentials from an already-compromised host. It allows one to dump SYSTEM,…
 rweijnen/createdump
Leverage WindowsApp createdump tool to obtain an lsass dump
 morrubin/negoexrelay
Relays NegoEx/PKU2U Kerberos authentication to arbitrary targets, enabling credentialless authentication, command execution, SMB hash dumping, and…
 synacktiv/ica2tcp
A SOCKS proxy for Citrix.
 portbuster1337/atlas
Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#
 eversinc33/sharpstartwebclient
Programmatically start WebClient from an unprivileged session to enable that juicy privesc.
 nccgroup/fenrir
PoC to tunnel the Meterpreter reverse HTTP shell over RDP Virtual Channels
 leftp/backupcreds
A C# implementation of dumping credentials from Windows Credential Manager
 synacktiv/kcmdump
Dump Kerberos tickets from the KCM database of SSSD
 u53rw4r3/remotekeystrokes
A script to automate keystrokes through a graphical desktop program.
 nccgroup/whowasi
Impersonate Logged In Accounts & Execute Commands
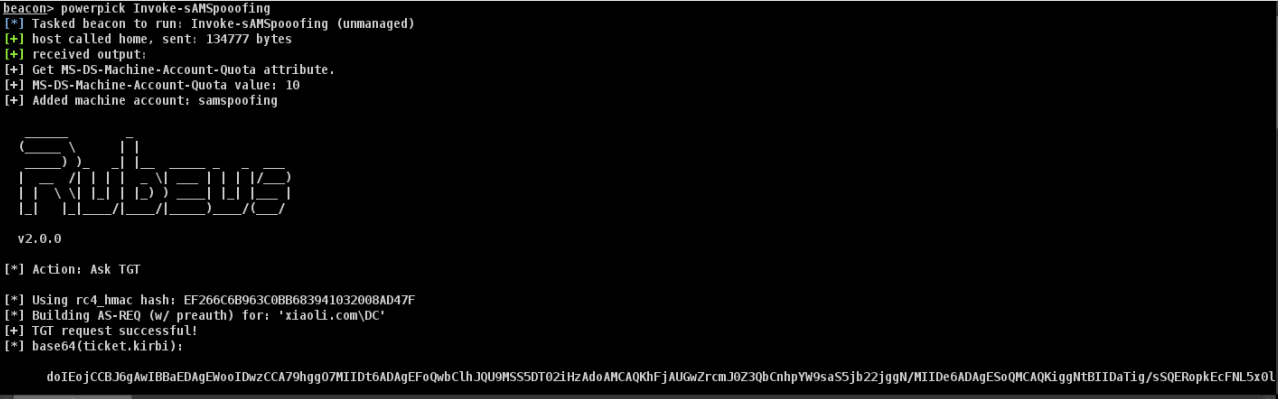 xiaolichan/invoke-samspoofing
CVE-2021-42287/CVE-2021-42278 exploits in powershell