Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
306 results
ShellcodeFluctuation preview

ShellcodeFluctuation

GitHubmgeeky/shellcodefluctuation

An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents

adversarial-attackpayload-developmentpayload-generation+4
1.1k
4 years ago
xc preview

xc

GitHubxct/xc

A small reverse shell for Linux & Windows

command-and-controlpayload-generationpenetration-testing+3
6474 years ago
backdoorme preview

backdoorme

GitHubkkevsterrr/backdoorme

powerful auto-backdooring utility

command-and-controlpayload-generationpenetration-testing+5
7478 years ago
Lilith preview

Lilith

GitHubwerkamsus/lilith

Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++

command-and-controlpayload-generationpenetration-testing+4
7477 years ago
ChromeAlone preview

ChromeAlone

GitHubpraetorian-inc/chromealone

A tool to transform Chromium browsers into a C2 Implant

command-and-controlpayload-developmentpersistence-mechanisms+6
60411 months ago
NimPlant preview

NimPlant

GitHubchvancooten/nimplant

A light-weight first-stage C2 implant written in Nim (and Rust).

command-and-controlpayload-generationpenetration-testing-frameworks+2
9541 year ago
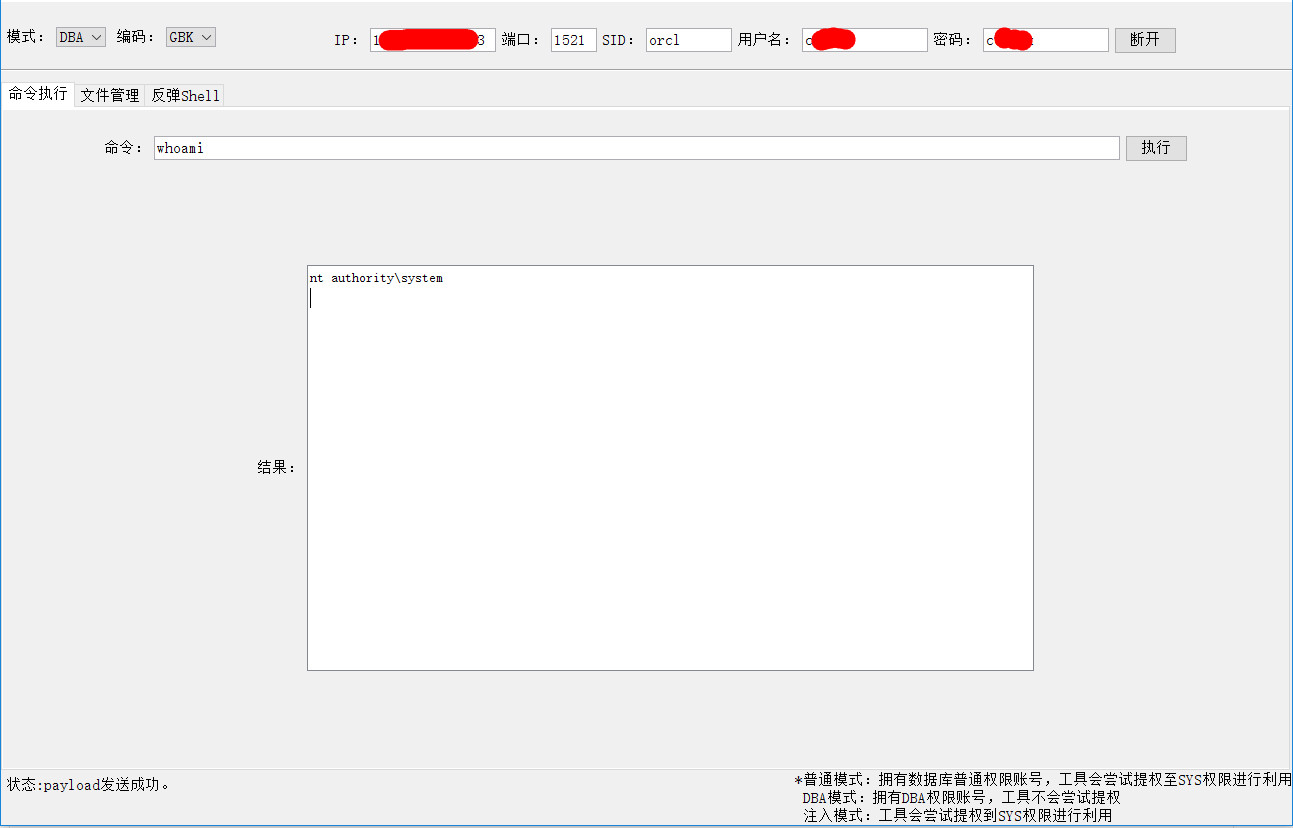
oracleShell preview

oracleShell

GitHubjas502n/oracleshell

oracle 数据库命令执行

database-securityexploitationpayload-development+2
5855 years ago
Dirty-Vanity preview

Dirty-Vanity

GitHubdeepinstinct/dirty-vanity

A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…

adversarial-attackexploitationpayload-development+4
6763 years ago
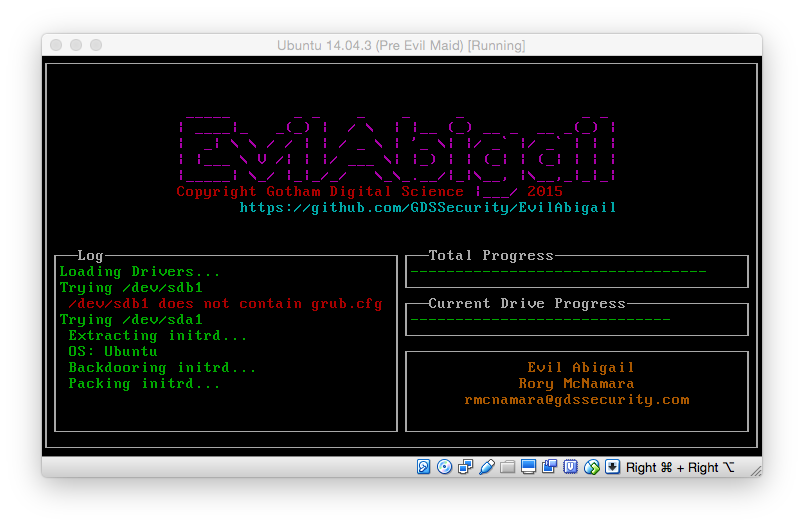
EvilAbigail preview

EvilAbigail

GitHubstrozfriedberg/evilabigail

Automated Linux evil maid attack

exploitationpassword-attackspayload-development+3
43710 years ago
hershell preview

hershell

GitHubsysdream/hershell

Hershell is a simple TCP reverse shell written in Go.

command-and-controlexploitationpayload-generation+5
5307 years ago
PR0CESS preview

PR0CESS

GitHubaaaddress1/pr0cess

some gadgets about windows process and ready to use :)

exploitationmalware-analysispayload-development+3
6152 years ago
DInvoke preview

DInvoke

GitHubthewover/dinvoke

Dynamically invoke arbitrary unmanaged code from managed code without PInvoke.

adversarial-attackpayload-developmentpost-exploitation+1
7923 years ago
CallbackHell preview

CallbackHell

GitHubly4k/callbackhell

Exploit for CVE-2021-40449 - Win32k Elevation of Privilege Vulnerability (LPE)

binary-exploitationexploitationpayload-development+4
4844 years ago
ScreenshotBOF preview

ScreenshotBOF

GitHubcodextf2/screenshotbof

An alternative screenshot capability for Cobalt Strike that uses WinAPI and does not perform a fork & run. Screenshot downloaded in memory.

command-and-controlpayload-developmentpenetration-testing+2
5082 months ago
FlavorTown preview

FlavorTown

GitHubwra7h/flavortown

Various ways to execute shellcode

payload-developmentpost-exploitationred-teaming+1
5122 years ago
PELoader preview

PELoader

GitHubhagrid29/peloader

PE loader with various shellcode injection techniques

binary-analysisexploitationmalware-analysis+4
4573 years ago
spawn preview

spawn

GitHubboku7/spawn

Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…

command-and-controlexploitationpayload-development+5
4643 years ago
gdog preview

gdog

GitHubmaldevel/gdog

A fully featured Windows backdoor that uses Gmail as a C&C server

command-and-controlpayload-generationpost-exploitation+2
5089 years ago
Previous1…345…17Next