

exploitation-course
 ashemery/exploitation-course
Offensive Software Exploitation Course
binary-exploitationeducationexploitation+7
2.5k3 years ago
ashemery/exploitation-courseOffensive Software Exploitation Course
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 fortra/nanodump
The swiss army knife of LSASS dumping
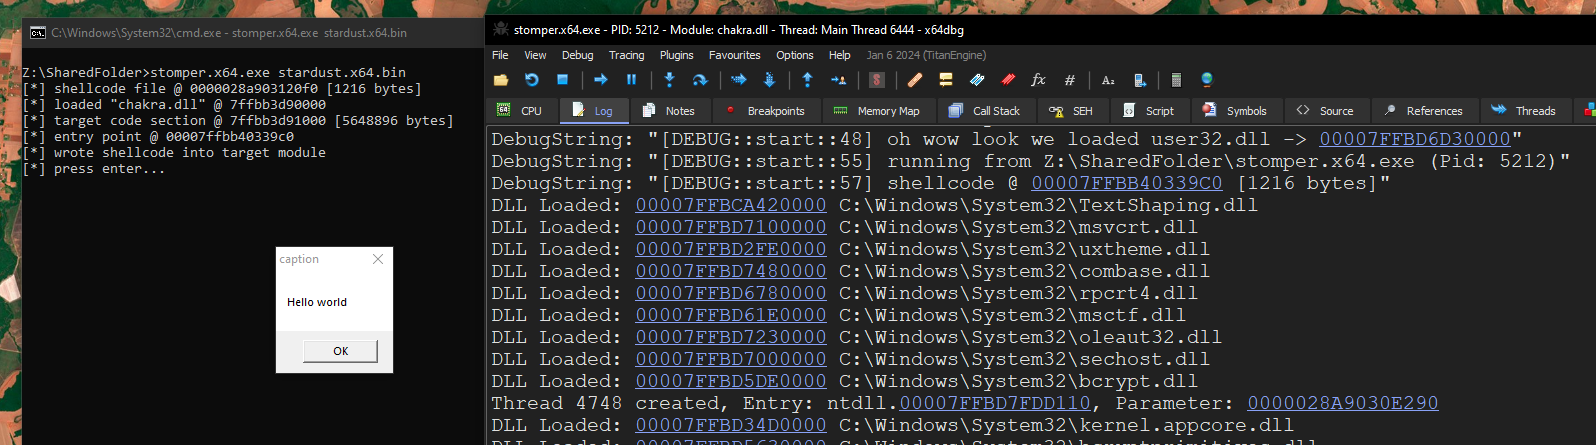 cracked5pider/stardust
A modern 32/64-bit position independent implant template
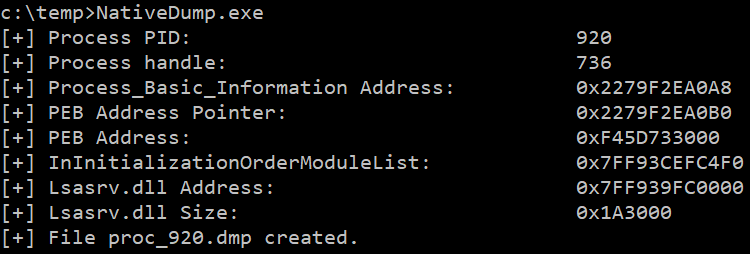 ricardojoserf/nativedump
Dump lsass using only NTAPI functions by hand-crafting Minidump files (without MiniDumpWriteDump!!!)
 sailay1996/awesome_windows_logical_bugs
collect for learning cases
 arget13/ddexec
A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.
 secretsquirrel/bdfproxy
Patch Binaries via MITM: BackdoorFactory + mitmProxy.
 cryptogenic/ps5-ipv6-kernel-exploit
An experimental webkit-based kernel exploit (Arb. R/W) for the PS5 on <= 4.51FW
 netspi/sshkey-grab
Grab ssh keys from ssh-agent
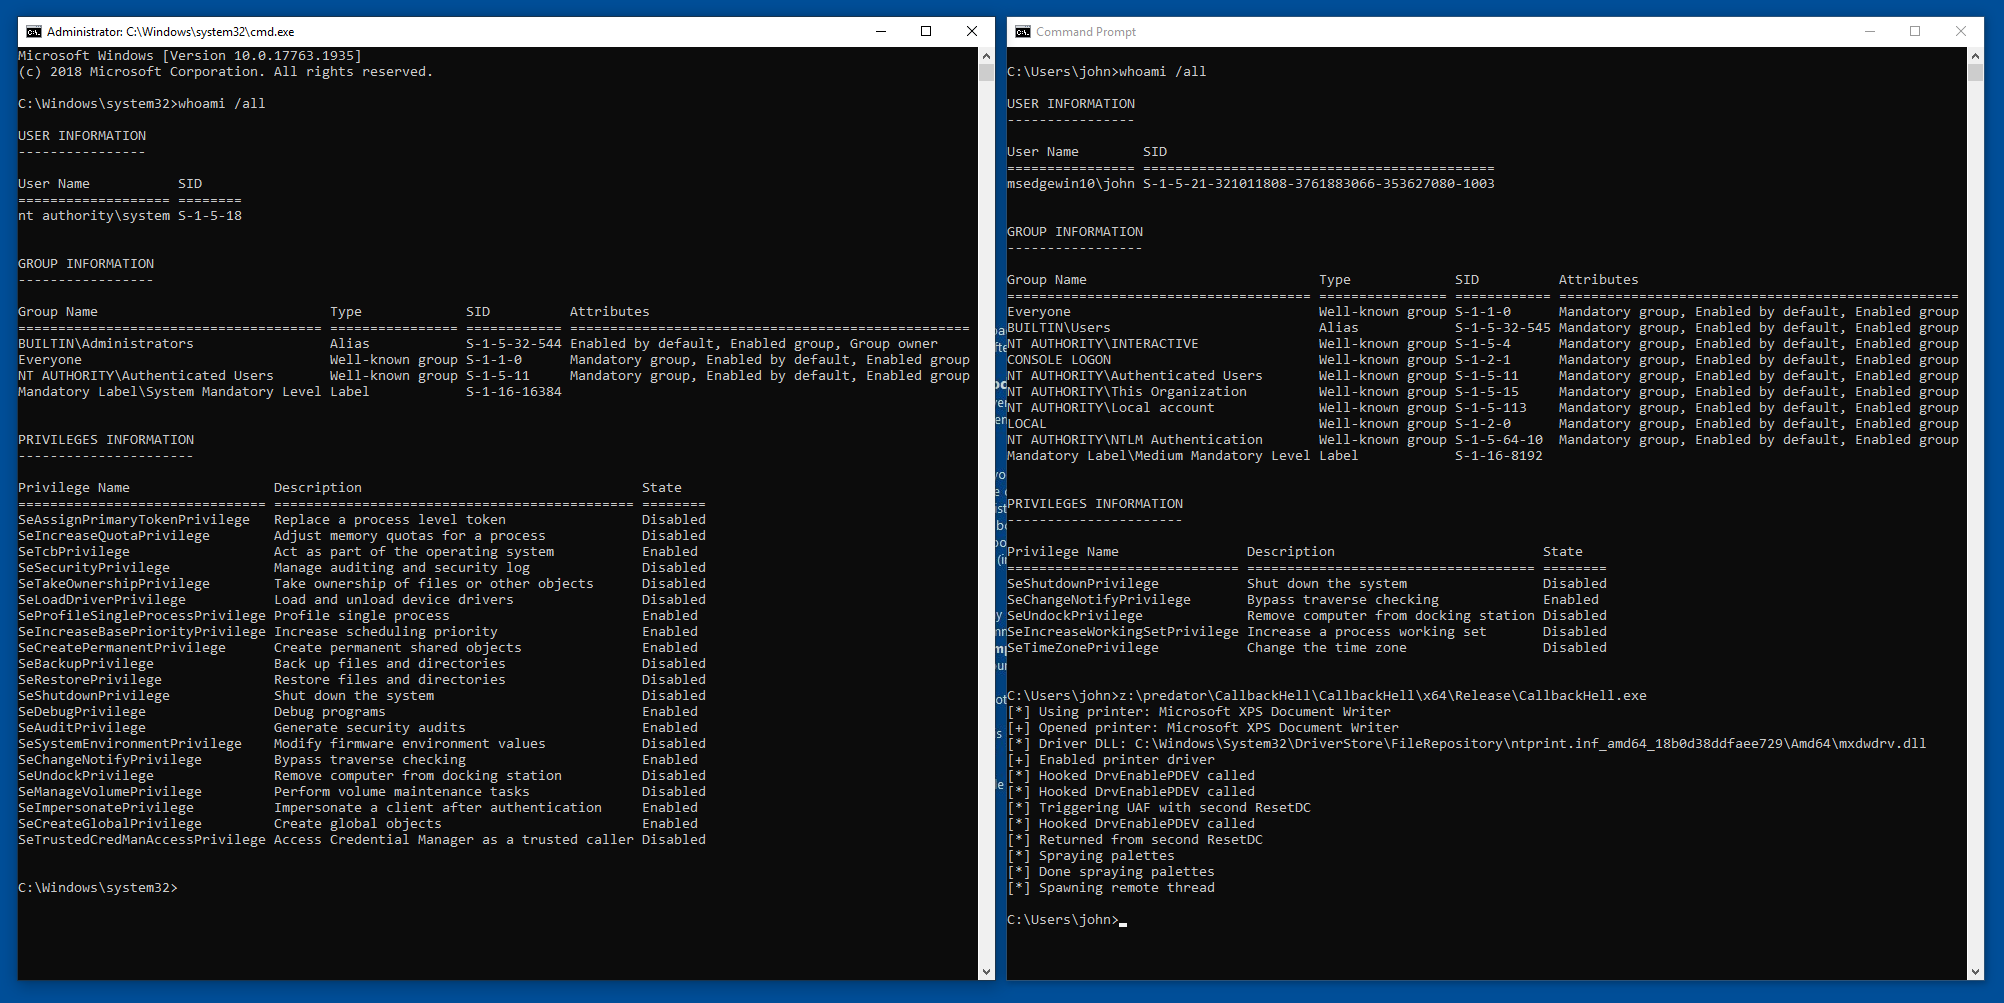 ly4k/callbackhell
Exploit for CVE-2021-40449 - Win32k Elevation of Privilege Vulnerability (LPE)
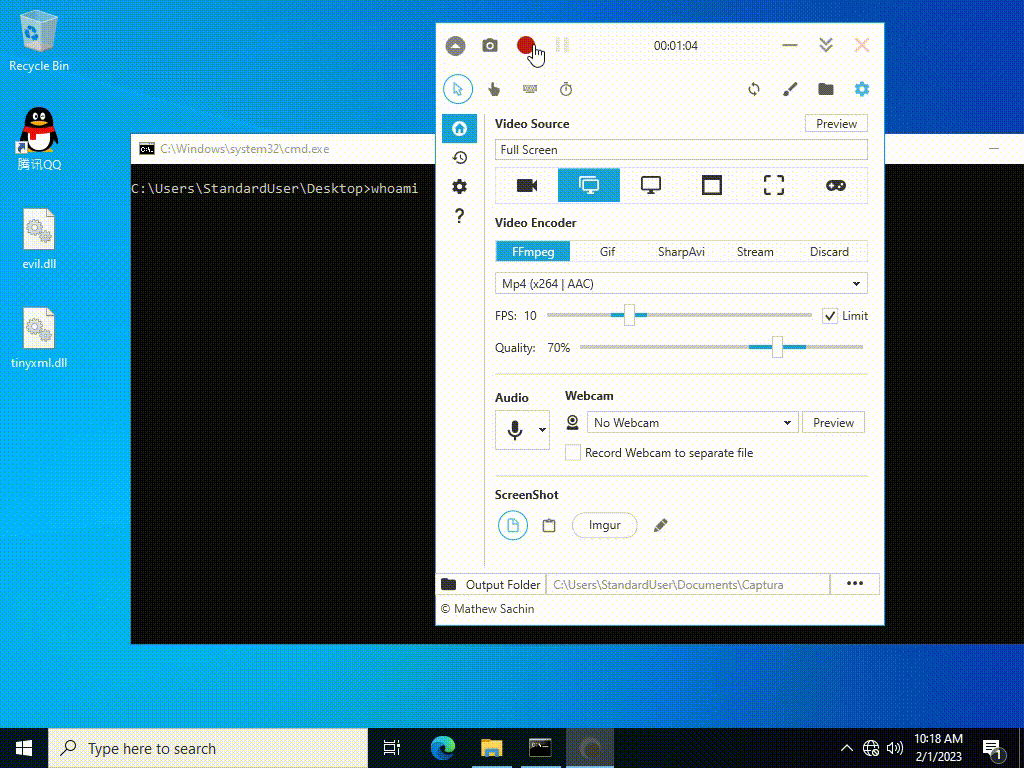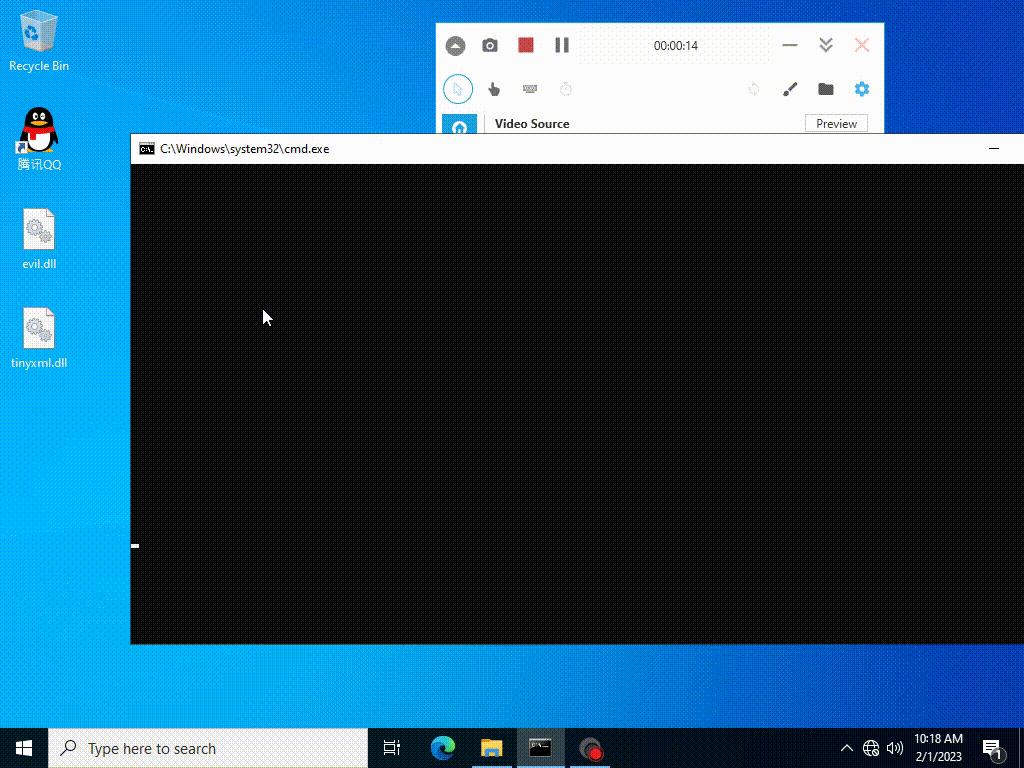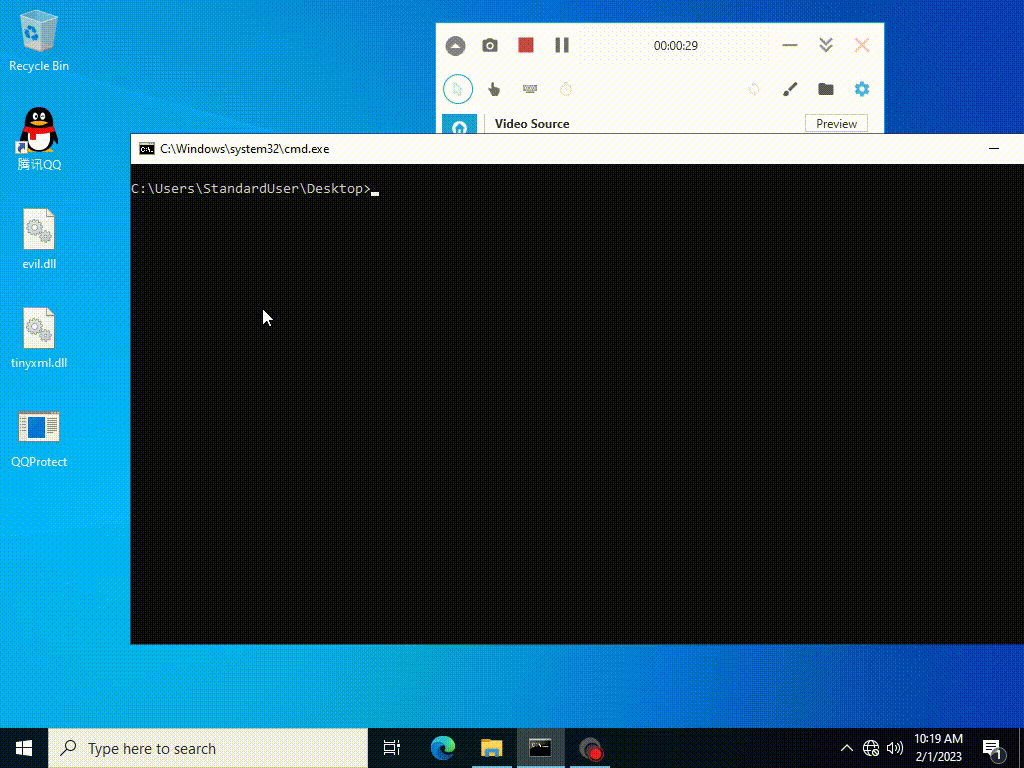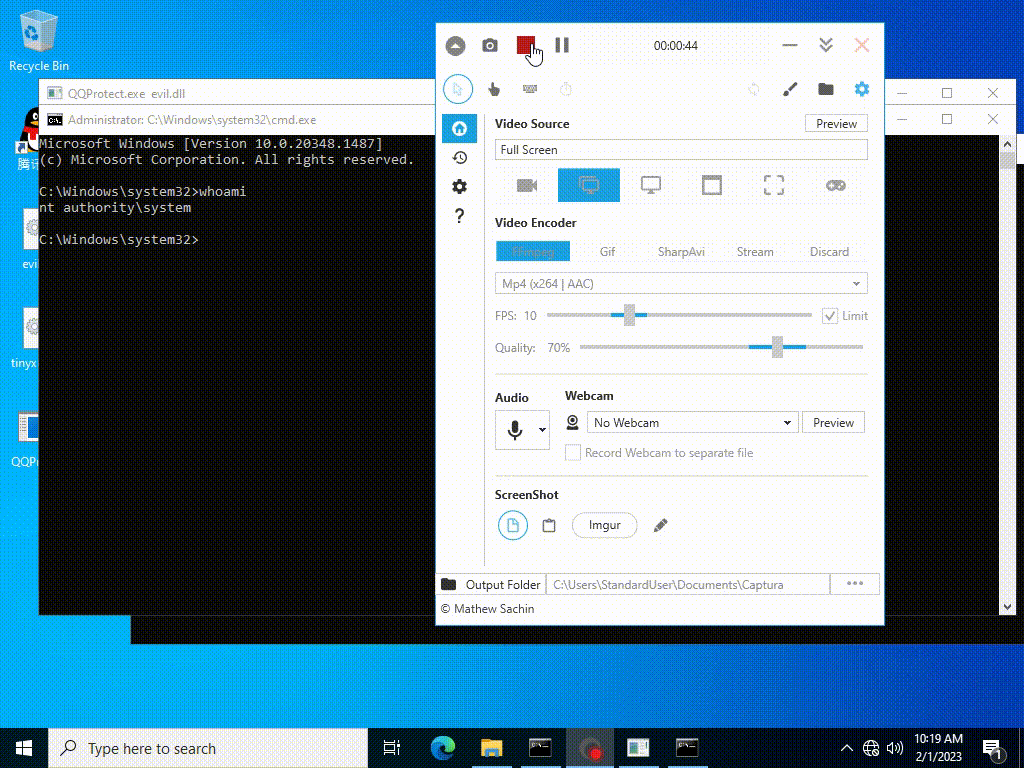 vi3t1/qq-tim-elevation
CVE-2023-34312
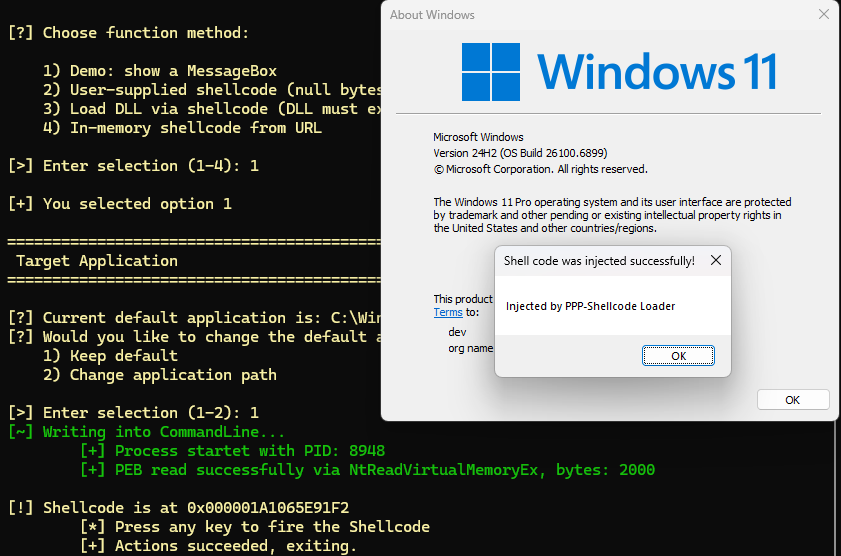 orange-cyberdefense/p3-loader
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
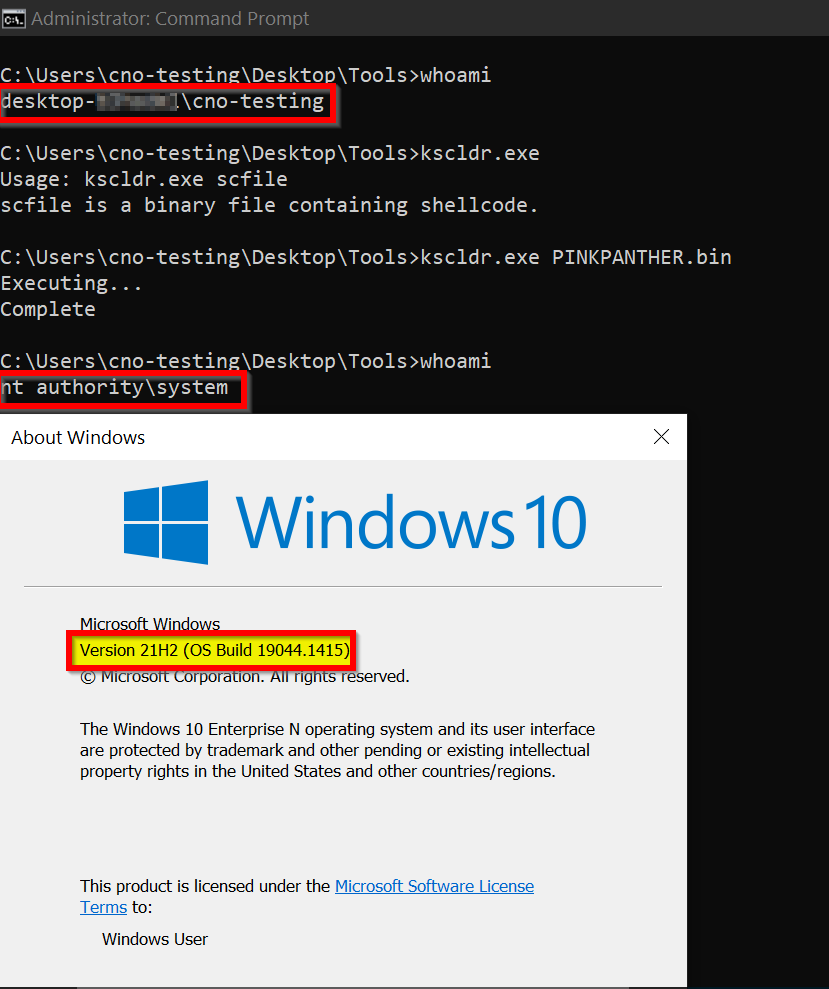 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 bazad/blanket
CVE-2018-4280: Mach port replacement vulnerability in launchd on iOS 11.2.6 leading to sandbox escape, privilege escalation, and codesigning bypass.
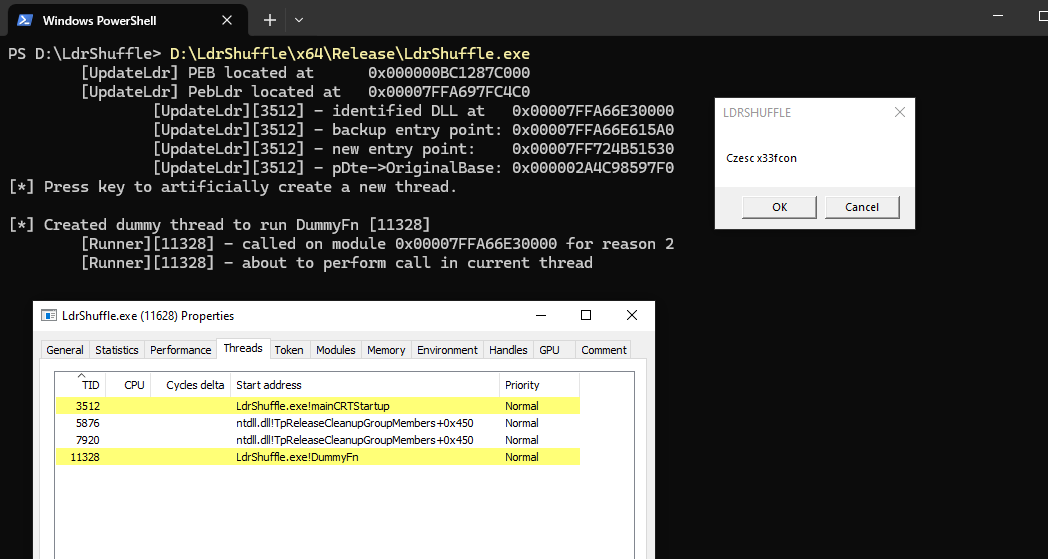 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 jgoyd/ios-attack-chain-cve-2025-31200-cve-2025-31201
CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s AudioConverterService, triggered by a malicious audio file via iMessage/SMS.…