
PoisonApple
 cyborgsecurity/poisonapple
CLI tool for applying and removing macOS persistence mechanisms, designed for threat emulation and red team operations. Supports 17 techniques…
persistence-mechanismspost-exploitationred-teaming
cyborgsecurity/poisonappleCLI tool for applying and removing macOS persistence mechanisms, designed for threat emulation and red team operations. Supports 17 techniques…
 cedowens/macshellswift
Proof of concept MacOS post exploitation tool written in Swift. Designed as a POC for blue teams to build macOS detections. Author: Cedric Owens
 trevohack/dynastypersist
Linux persistence toolkit with 11 modules for SSH key backdoors, cronjobs, systemd services, LKM rootkits, and LD_PRELOAD privilege escalation.…
 ivanitlearning/juicy-potato-x86
Windows privilege escalation exploit that abuses service token impersonation to execute arbitrary commands with SYSTEM privileges, designed for x86…
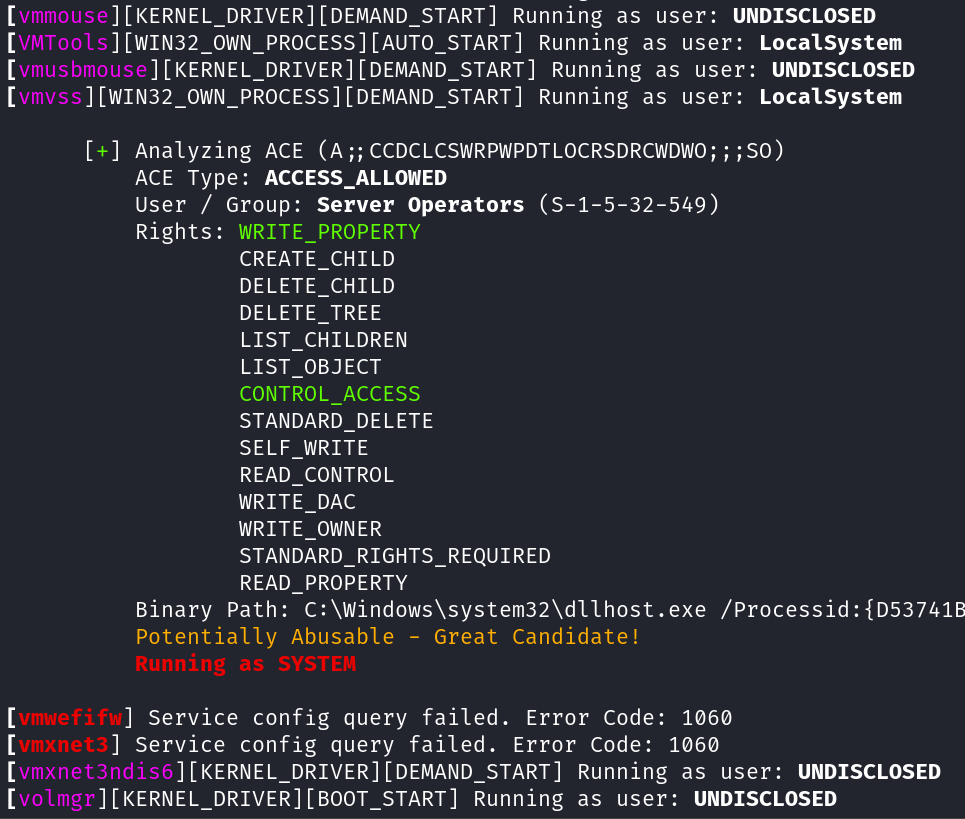 t3l3machus/aceshark
ACEshark is a utility designed for rapid extraction and analysis of Windows service configurations and Access Control Entries, eliminating the need…
 correcthorsebatterystaple-sudo/orwell-rat-and-botnet
Orwell is a RAT and Botnet designed as a trio of programs.
 prodefense/hawk
Golang tool designed to exfiltrate passwords found via the sshd and su services
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses
 vulnquest58/vq-refluxcore
is an advanced security research framework designed to model, analyze, and demonstrate Local Privilege Escalation (LPE) mechanics associated with…
 nikopmpm/fsociety-cve-2024-0670-checkmk-lpe
🔍 Exploit CVE-2024-0670 in CheckMK agents for local privilege escalation using a robust C++ tool designed for security professionals.
 spiralbl0ck/mallicious-ios-shortcut-keylogger-
iOS Shortcut-based keylogger designed to capture keystrokes and exfiltrate data from compromised devices.
 foxyproxys/cve-2023-52654
Automated privilege escalation script exploiting misconfigured setuid/sgid binaries, sudo, cron, and LD_PRELOAD on Unix systems. Designed for CTF and…
 0x4d31/honeybits
A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…
 hlldz/reflexxion
RefleXXion is a utility designed to aid in bypassing user-mode hooks utilised by AV/EPP/EDR etc. In order to bypass the user-mode hooks, it first…
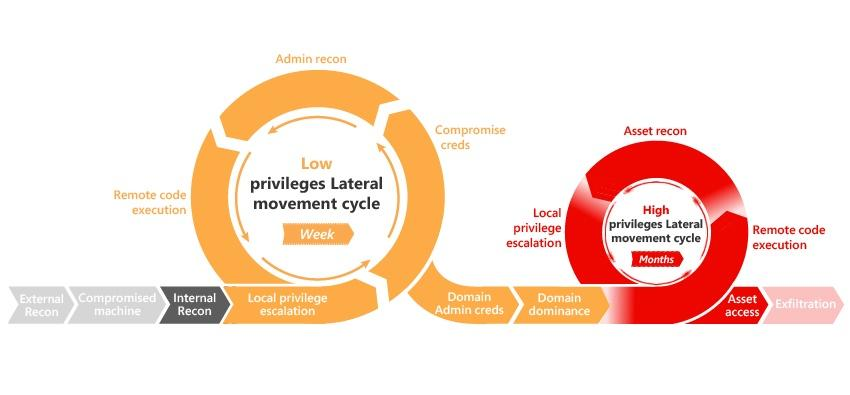 infosecn1nja/ad-attack-defense
Attack and defend active directory using modern post exploitation adversary tradecraft activity
 ignitetechnologies/privilege-escalation
This cheasheet is aimed at the CTF Players and Beginners to help them understand the fundamentals of Privilege Escalation with examples.
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 nyan-x-cat/asyncrat-c-sharp
Open-Source Remote Administration Tool For Windows C# (RAT)